
#databreach
databreach
107,441 views
199 Discussing
Hot
Latest
·
--
Article
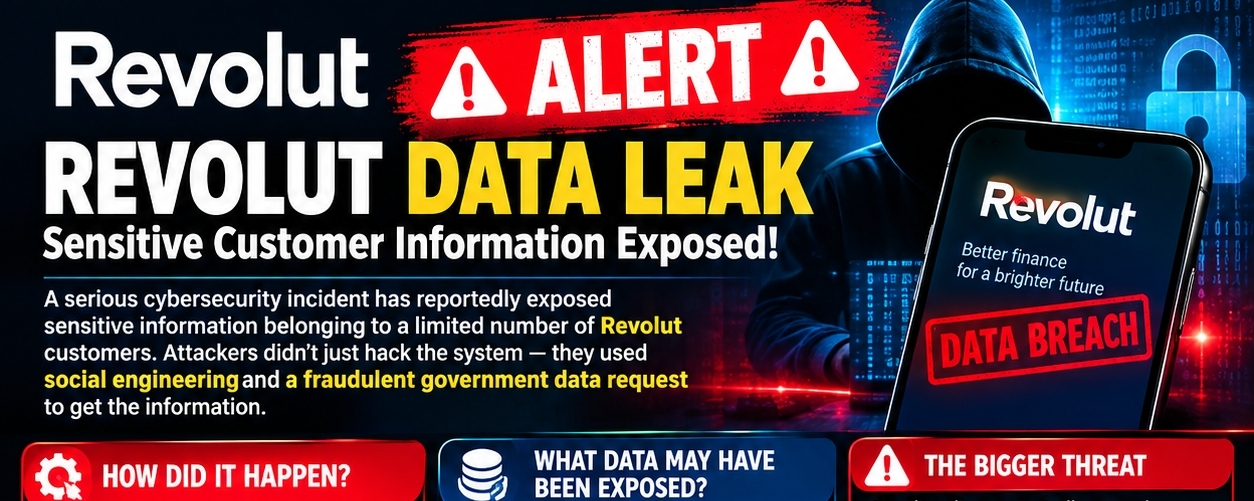
ALERT ALERT: REVOLUT DATA LEAK 🚨🚨🚨🚨 ALERT ALERT: REVOLUT DATA LEAK 🚨🚨
⚠️ Millions of crypto and fintech users should pay attention!
A serious cybersecurity incident has reportedly exposed sensitive information belonging to a limited number of Revolut customers. The alarming part? Attackers reportedly used social engineering and a fraudulent government data request instead of directly hacking Revolut’s systems.
🔴 HOW DID IT HAPPEN?
Attackers reportedly sent a fake request that appeared to come from a legitimate government email domain. Because the request looked authentic, Revolut reportedly provided certain customer information before discovering that the request was fraudulent.
🔓 WHAT DATA MAY HAVE BEEN EXPOSED?
⚠️ Customer names and personal details
⚠️ Email addresses and phone numbers
⚠️ Identity-document information
⚠️ Passport/ID details
⚠️ Verification selfies
⚠️ Financial and account information
⚠️ Withdrawal records
⚠️ Transaction history
⚠️ In some cases, Bitcoin transaction history
🚨 THE BIGGER THREAT
Reports say attackers have started publishing some customer information online and are threatening to release more data every day.
This could increase the risk of:
🔴 Identity theft
🔴 Phishing attacks
🔴 Account impersonation
🔴 Financial scams
🔴 Targeted crypto scams
💰 WERE FUNDS STOLEN?
So far, this has primarily been reported as a customer-data exposure, not a direct theft of customer funds. However, leaked KYC and financial information can still create serious security risks.
🛡️ HOW TO PROTECT YOURSELF
✅ Never share OTPs, passwords, PINs or 2FA codes.
✅ Do NOT click suspicious Revolut links sent through email, SMS or social media.
✅ Verify any “urgent” request through the official Revolut app.
✅ Enable strong 2FA/security protection.
✅ Watch your accounts for unusual activity.
✅ If Revolut confirms that your identity documents were exposed, take immediate steps to protect your identity.
🚨 IMPORTANT LESSON:
An email coming from an official-looking government domain does NOT automatically mean the request is genuine.
Cybercriminals are increasingly using social engineering to trick employees and obtain sensitive information.
🔴 STAY ALERT. STAY SECURE. PROTECT YOUR DATA. 🚨
#Revolut #RevolutDataLeak #ALERT #DataBreach #CyberSecurity #KYC #Bitcoin #Crypto #Privacy #CyberAttack
ALERT ALERT: REVOLUT DATA LEAK 🚨🚨
🚨🚨 ALERT ALERT: REVOLUT DATA LEAK 🚨🚨
⚠️ Millions of crypto and fintech users should pay attention!
A serious cybersecurity incident has reportedly exposed sensitive information belonging to a limited number of Revolut customers. The alarming part? Attackers reportedly used social engineering and a fraudulent government data request instead of directly hacking Revolut’s systems.
🔴 HOW DID IT HAPPEN?
Attackers reportedly sent a fake request that appeared to come from a legitimate government email domain. Because the request looked authentic, Revolut reportedly provided certain customer information before discovering that the request was fraudulent.
🔓 WHAT DATA MAY HAVE BEEN EXPOSED?
⚠️ Customer names and personal details
⚠️ Email addresses and phone numbers
⚠️ Identity-document information
⚠️ Passport/ID details
⚠️ Verification selfies
⚠️ Financial and account information
⚠️ Withdrawal records
⚠️ Transaction history
⚠️ In some cases, Bitcoin transaction history
🚨 THE BIGGER THREAT
Reports say attackers have started publishing some customer information online and are threatening to release more data every day.
This could increase the risk of:
🔴 Identity theft
🔴 Phishing attacks
🔴 Account impersonation
🔴 Financial scams
🔴 Targeted crypto scams
💰 WERE FUNDS STOLEN?
So far, this has primarily been reported as a customer-data exposure, not a direct theft of customer funds. However, leaked KYC and financial information can still create serious security risks.
🛡️ HOW TO PROTECT YOURSELF
✅ Never share OTPs, passwords, PINs or 2FA codes.
✅ Do NOT click suspicious Revolut links sent through email, SMS or social media.
✅ Verify any “urgent” request through the official Revolut app.
✅ Enable strong 2FA/security protection.
✅ Watch your accounts for unusual activity.
✅ If Revolut confirms that your identity documents were exposed, take immediate steps to protect your identity.
🚨 IMPORTANT LESSON:
An email coming from an official-looking government domain does NOT automatically mean the request is genuine.
Cybercriminals are increasingly using social engineering to trick employees and obtain sensitive information.
🔴 STAY ALERT. STAY SECURE. PROTECT YOUR DATA. 🚨
#Revolut #RevolutDataLeak #ALERT #DataBreach #CyberSecurity #KYC #Bitcoin #Crypto #Privacy #CyberAttack
⚠️ Millions of crypto and fintech users should pay attention!
A serious cybersecurity incident has reportedly exposed sensitive information belonging to a limited number of Revolut customers. The alarming part? Attackers reportedly used social engineering and a fraudulent government data request instead of directly hacking Revolut’s systems.
🔴 HOW DID IT HAPPEN?
Attackers reportedly sent a fake request that appeared to come from a legitimate government email domain. Because the request looked authentic, Revolut reportedly provided certain customer information before discovering that the request was fraudulent.
🔓 WHAT DATA MAY HAVE BEEN EXPOSED?
⚠️ Customer names and personal details
⚠️ Email addresses and phone numbers
⚠️ Identity-document information
⚠️ Passport/ID details
⚠️ Verification selfies
⚠️ Financial and account information
⚠️ Withdrawal records
⚠️ Transaction history
⚠️ In some cases, Bitcoin transaction history
🚨 THE BIGGER THREAT
Reports say attackers have started publishing some customer information online and are threatening to release more data every day.
This could increase the risk of:
🔴 Identity theft
🔴 Phishing attacks
🔴 Account impersonation
🔴 Financial scams
🔴 Targeted crypto scams
💰 WERE FUNDS STOLEN?
So far, this has primarily been reported as a customer-data exposure, not a direct theft of customer funds. However, leaked KYC and financial information can still create serious security risks.
🛡️ HOW TO PROTECT YOURSELF
✅ Never share OTPs, passwords, PINs or 2FA codes.
✅ Do NOT click suspicious Revolut links sent through email, SMS or social media.
✅ Verify any “urgent” request through the official Revolut app.
✅ Enable strong 2FA/security protection.
✅ Watch your accounts for unusual activity.
✅ If Revolut confirms that your identity documents were exposed, take immediate steps to protect your identity.
🚨 IMPORTANT LESSON:
An email coming from an official-looking government domain does NOT automatically mean the request is genuine.
Cybercriminals are increasingly using social engineering to trick employees and obtain sensitive information.
🔴 STAY ALERT. STAY SECURE. PROTECT YOUR DATA. 🚨
#Revolut #RevolutDataLeak #ALERT #DataBreach #CyberSecurity #KYC #Bitcoin #Crypto #Privacy #CyberAttack
1
71

Why is nobody talking about fintechs leaking complete Bitcoin transaction records to the world?
Most crypto traders face the constant risk of getting phished after a leak. Watching their funds disappear because hackers knew exactly when they bought $BTC is a nightmare many have lived.
Revolut has confirmed that customer data was exposed including identity documents, account details and full transaction histories with Bitcoin activity. This kind of leak gives attackers a detailed map of your financial life. They know your patterns and can strike when it hurts most.
People treat these incidents as just another Tuesday in tech. That attitude ignores how crypto data turns a simple breach into a hunting ground for your assets.
Start by auditing all your logins and enabling the strongest authentication available. Shift larger $ETH positions off connected services and scan recent $USDT activity for anything off.
Anyone else seeing this as a wake-up call for where we store our crypto details?
#DataBreach #Bitcoin #CryptoSecurity
Why is nobody talking about fintechs leaking complete Bitcoin transaction records to the world?
Most crypto traders face the constant risk of getting phished after a leak. Watching their funds disappear because hackers knew exactly when they bought $BTC is a nightmare many have lived.
Revolut has confirmed that customer data was exposed including identity documents, account details and full transaction histories with Bitcoin activity. This kind of leak gives attackers a detailed map of your financial life. They know your patterns and can strike when it hurts most.
People treat these incidents as just another Tuesday in tech. That attitude ignores how crypto data turns a simple breach into a hunting ground for your assets.
Start by auditing all your logins and enabling the strongest authentication available. Shift larger $ETH positions off connected services and scan recent $USDT activity for anything off.
Anyone else seeing this as a wake-up call for where we store our crypto details?
#DataBreach #Bitcoin #CryptoSecurity
Most crypto traders face the constant risk of getting phished after a leak. Watching their funds disappear because hackers knew exactly when they bought $BTC is a nightmare many have lived.
Revolut has confirmed that customer data was exposed including identity documents, account details and full transaction histories with Bitcoin activity. This kind of leak gives attackers a detailed map of your financial life. They know your patterns and can strike when it hurts most.
People treat these incidents as just another Tuesday in tech. That attitude ignores how crypto data turns a simple breach into a hunting ground for your assets.
Start by auditing all your logins and enabling the strongest authentication available. Shift larger $ETH positions off connected services and scan recent $USDT activity for anything off.
Anyone else seeing this as a wake-up call for where we store our crypto details?
#DataBreach #Bitcoin #CryptoSecurity
13

·
--
Everyone thinks their personal information is locked away safely with major fintech platforms, but actually a clever fake request can get it all handed over.
Crypto traders face the risk of identity theft that turns into stolen funds, especially when leaked details help scammers target $BTC purchases or $ETH wallets. That's a common way people get rugged without a single on-chain hack.
Attackers allegedly tricked Revolut by sending a fraudulent request from an unauthorized account operating inside a legitimate government agency’s domain. The company handed over sensitive customer information as a result.
This kind of attack works because it looks official, much like receiving a letter that appears to come from the tax authorities. You have to verify independently every time, particularly if you use these apps for $USDT conversions.
Where do you think this goes from here?
#CryptoSafety #DataBreach #FintechWarning
Everyone thinks their personal information is locked away safely with major fintech platforms, but actually a clever fake request can get it all handed over.
Crypto traders face the risk of identity theft that turns into stolen funds, especially when leaked details help scammers target $BTC purchases or $ETH wallets. That's a common way people get rugged without a single on-chain hack.
Attackers allegedly tricked Revolut by sending a fraudulent request from an unauthorized account operating inside a legitimate government agency’s domain. The company handed over sensitive customer information as a result.
This kind of attack works because it looks official, much like receiving a letter that appears to come from the tax authorities. You have to verify independently every time, particularly if you use these apps for $USDT conversions.
Where do you think this goes from here?
#CryptoSafety #DataBreach #FintechWarning
Crypto traders face the risk of identity theft that turns into stolen funds, especially when leaked details help scammers target $BTC purchases or $ETH wallets. That's a common way people get rugged without a single on-chain hack.
Attackers allegedly tricked Revolut by sending a fraudulent request from an unauthorized account operating inside a legitimate government agency’s domain. The company handed over sensitive customer information as a result.
This kind of attack works because it looks official, much like receiving a letter that appears to come from the tax authorities. You have to verify independently every time, particularly if you use these apps for $USDT conversions.
Where do you think this goes from here?
#CryptoSafety #DataBreach #FintechWarning
11

·
--
If you're still trusting every fintech app with your KYC and crypto, stop now.
These data breaches turn your personal details into ammunition for phishing attacks that empty wallets before you even notice. There is no clean exit once your info is out there.
Revolut is reportedly facing a 10,000 $BTC ransom demand following a customer data breach. Some will say just pay it to lock down the remaining data and move forward. Others insist that paying only guarantees the next group will come knocking with a bigger ask.
I land firmly in the never-pay camp. A 10,000 $BTC transfer would fund more of these operations and put every platform holding $ETH or $USDT in the crosshairs. Self-custody is the only setup that actually removes this risk.
Would you pay if you ran Revolut, or is this proof we need to get off these apps?
#Bitcoin #CryptoSecurity #DataBreach
If you're still trusting every fintech app with your KYC and crypto, stop now.
These data breaches turn your personal details into ammunition for phishing attacks that empty wallets before you even notice. There is no clean exit once your info is out there.
Revolut is reportedly facing a 10,000 $BTC ransom demand following a customer data breach. Some will say just pay it to lock down the remaining data and move forward. Others insist that paying only guarantees the next group will come knocking with a bigger ask.
I land firmly in the never-pay camp. A 10,000 $BTC transfer would fund more of these operations and put every platform holding $ETH or $USDT in the crosshairs. Self-custody is the only setup that actually removes this risk.
Would you pay if you ran Revolut, or is this proof we need to get off these apps?
#Bitcoin #CryptoSecurity #DataBreach
These data breaches turn your personal details into ammunition for phishing attacks that empty wallets before you even notice. There is no clean exit once your info is out there.
Revolut is reportedly facing a 10,000 $BTC ransom demand following a customer data breach. Some will say just pay it to lock down the remaining data and move forward. Others insist that paying only guarantees the next group will come knocking with a bigger ask.
I land firmly in the never-pay camp. A 10,000 $BTC transfer would fund more of these operations and put every platform holding $ETH or $USDT in the crosshairs. Self-custody is the only setup that actually removes this risk.
Would you pay if you ran Revolut, or is this proof we need to get off these apps?
#Bitcoin #CryptoSecurity #DataBreach
7
·
--
🚨🔐 Revolut Confirms Fake Government Email Data Breach 🔐🚨
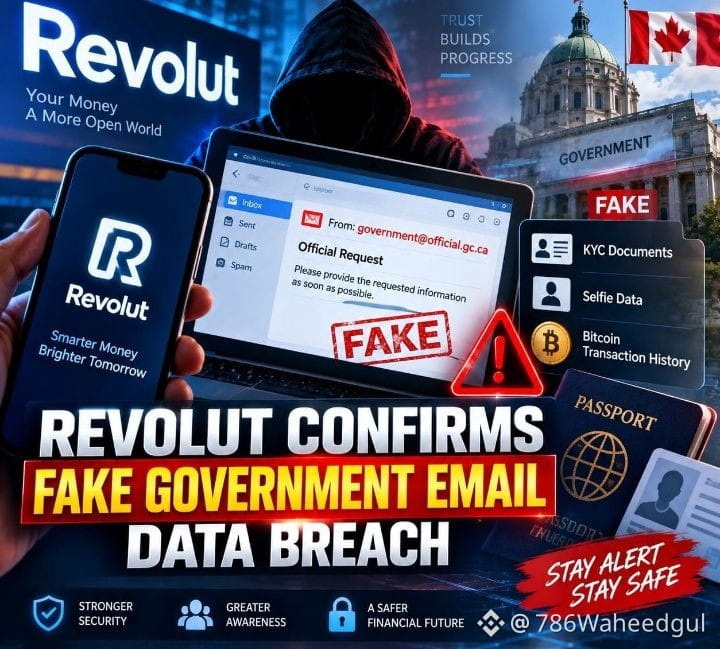
A legitimate-looking government email can still be fraudulent—and that’s the key lesson from Revolut’s latest security incident.
Revolut reportedly informed a subset of customers that personal and financial information was disclosed after the company received a fraudulent information request that appeared to originate from a government agency.
What makes this especially concerning? The email reportedly passed SPF, DKIM and DMARC authentication, showing that technical email verification alone cannot confirm whether the sender is actually authorized.
Reportedly exposed information included KYC images, selfie data and Bitcoin transaction histories. Revolut later confirmed the mailbox was unauthorized, blocked it and notified regulators.
🔐 The takeaway: authenticated doesn’t always mean authorized. Sensitive requests need layered, independent verification.
Should financial institutions add another verification step for government data requests?
Educational purposes only. Not financial advice.
$BTC
{spot}(BTCUSDT)
#CyberSecurity #Crypto #Revolut #BTC #DataBreach
🚨🔐 Revolut Confirms Fake Government Email Data Breach 🔐🚨
A legitimate-looking government email can still be fraudulent—and that’s the key lesson from Revolut’s latest security incident.
Revolut reportedly informed a subset of customers that personal and financial information was disclosed after the company received a fraudulent information request that appeared to originate from a government agency.
What makes this especially concerning? The email reportedly passed SPF, DKIM and DMARC authentication, showing that technical email verification alone cannot confirm whether the sender is actually authorized.
Reportedly exposed information included KYC images, selfie data and Bitcoin transaction histories. Revolut later confirmed the mailbox was unauthorized, blocked it and notified regulators.
🔐 The takeaway: authenticated doesn’t always mean authorized. Sensitive requests need layered, independent verification.
Should financial institutions add another verification step for government data requests?
Educational purposes only. Not financial advice.
$BTC
#CyberSecurity #Crypto #Revolut #BTC #DataBreach
A legitimate-looking government email can still be fraudulent—and that’s the key lesson from Revolut’s latest security incident.
Revolut reportedly informed a subset of customers that personal and financial information was disclosed after the company received a fraudulent information request that appeared to originate from a government agency.
What makes this especially concerning? The email reportedly passed SPF, DKIM and DMARC authentication, showing that technical email verification alone cannot confirm whether the sender is actually authorized.
Reportedly exposed information included KYC images, selfie data and Bitcoin transaction histories. Revolut later confirmed the mailbox was unauthorized, blocked it and notified regulators.
🔐 The takeaway: authenticated doesn’t always mean authorized. Sensitive requests need layered, independent verification.
Should financial institutions add another verification step for government data requests?
Educational purposes only. Not financial advice.
$BTC
#CyberSecurity #Crypto #Revolut #BTC #DataBreach
1
·
--
🚨 Revolut & Fake Government Email: A Serious Data Security Warning
A new cybersecurity controversy involving Revolut is raising questions about how financial institutions verify sensitive government requests.
Reports circulating online suggest that a fake government email/request may have been used to obtain or expose sensitive customer information. While the full scope and details still need to be independently verified, the situation highlights a major cybersecurity lesson:
🔐 Never trust an email simply because it looks official.
For financial platforms, even a convincing government-style request can become dangerous if identity and authorization checks aren't strong enough.
Why this matters 👇
💳 Financial platforms hold highly sensitive customer data.
📧 Email impersonation can make fraudulent requests look legitimate.
🏦 KYC information can become extremely valuable to attackers.
🎣 Leaked information can potentially fuel targeted phishing and social-engineering attacks.
Revolut itself advises users to check suspicious sender addresses and contact support through the app rather than trusting unexpected communications. �
Revolut
⚠️ The bigger question:
Should banks and fintech companies require multiple independent verification steps before releasing customer information in response to government requests?
🟢 YES — verification should be mandatory
🔴 Current systems are already sufficient
What do you think? 👇
#Revolut #CyberSecurity #DataBreach #Crypto_Jobs🎯 #Fintech #Privacy #Phishing #ScamAlert #Blockchain
*This post discusses reported allegations and does not establish that every claim circulating online has been independently confirmed. Always verify information through official sources.*
🚨 Revolut & Fake Government Email: A Serious Data Security Warning
A new cybersecurity controversy involving Revolut is raising questions about how financial institutions verify sensitive government requests.
Reports circulating online suggest that a fake government email/request may have been used to obtain or expose sensitive customer information. While the full scope and details still need to be independently verified, the situation highlights a major cybersecurity lesson:
🔐 Never trust an email simply because it looks official.
For financial platforms, even a convincing government-style request can become dangerous if identity and authorization checks aren't strong enough.
Why this matters 👇
💳 Financial platforms hold highly sensitive customer data.
📧 Email impersonation can make fraudulent requests look legitimate.
🏦 KYC information can become extremely valuable to attackers.
🎣 Leaked information can potentially fuel targeted phishing and social-engineering attacks.
Revolut itself advises users to check suspicious sender addresses and contact support through the app rather than trusting unexpected communications. �
Revolut
⚠️ The bigger question:
Should banks and fintech companies require multiple independent verification steps before releasing customer information in response to government requests?
🟢 YES — verification should be mandatory
🔴 Current systems are already sufficient
What do you think? 👇
#Revolut #CyberSecurity #DataBreach #Crypto_Jobs🎯 #Fintech #Privacy #Phishing #ScamAlert #Blockchain
*This post discusses reported allegations and does not establish that every claim circulating online has been independently confirmed. Always verify information through official sources.*
A new cybersecurity controversy involving Revolut is raising questions about how financial institutions verify sensitive government requests.
Reports circulating online suggest that a fake government email/request may have been used to obtain or expose sensitive customer information. While the full scope and details still need to be independently verified, the situation highlights a major cybersecurity lesson:
🔐 Never trust an email simply because it looks official.
For financial platforms, even a convincing government-style request can become dangerous if identity and authorization checks aren't strong enough.
Why this matters 👇
💳 Financial platforms hold highly sensitive customer data.
📧 Email impersonation can make fraudulent requests look legitimate.
🏦 KYC information can become extremely valuable to attackers.
🎣 Leaked information can potentially fuel targeted phishing and social-engineering attacks.
Revolut itself advises users to check suspicious sender addresses and contact support through the app rather than trusting unexpected communications. �
Revolut
⚠️ The bigger question:
Should banks and fintech companies require multiple independent verification steps before releasing customer information in response to government requests?
🟢 YES — verification should be mandatory
🔴 Current systems are already sufficient
What do you think? 👇
#Revolut #CyberSecurity #DataBreach #Crypto_Jobs🎯 #Fintech #Privacy #Phishing #ScamAlert #Blockchain
*This post discusses reported allegations and does not establish that every claim circulating online has been independently confirmed. Always verify information through official sources.*
43

·
--
Revolut messed up! A fintech company was actually tricked by a fake government request, exposing users' passport information and their complete Bitcoin transaction history. Although they claim only "limited" users were affected, this is absolutely outrageous!
With data security issues, people are once again debating the importance of decentralized wallets. In the short term, you may see some users starting to move their assets out of Revolut; in the long run, it could even spur a broader push toward self-custody awareness.
#DataBreach #CryptoSecurity $BTC
Revolut messed up! A fintech company was actually tricked by a fake government request, exposing users' passport information and their complete Bitcoin transaction history. Although they claim only "limited" users were affected, this is absolutely outrageous!
With data security issues, people are once again debating the importance of decentralized wallets. In the short term, you may see some users starting to move their assets out of Revolut; in the long run, it could even spur a broader push toward self-custody awareness.
#DataBreach #CryptoSecurity $BTC
With data security issues, people are once again debating the importance of decentralized wallets. In the short term, you may see some users starting to move their assets out of Revolut; in the long run, it could even spur a broader push toward self-custody awareness.
#DataBreach #CryptoSecurity $BTC
75

🚨 Massive data leak reveals 153 million driver’s licenses offered for sale
A recent report uncovered an alleged leak of 153 million driver’s licenses, believed to have been stolen from an identity verification company. This incident highlights the growing security risks associated with storing sensitive information with third parties, making it an attractive target for malicious actors.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#DataBreach #CyberSecurity #Privacy #IdentityTheft #DataProtection
📰 Source: gizmodo.com
🚨 Massive data leak reveals 153 million driver’s licenses offered for sale
A recent report uncovered an alleged leak of 153 million driver’s licenses, believed to have been stolen from an identity verification company. This incident highlights the growing security risks associated with storing sensitive information with third parties, making it an attractive target for malicious actors.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#DataBreach #CyberSecurity #Privacy #IdentityTheft #DataProtection
📰 Source: gizmodo.com
A recent report uncovered an alleged leak of 153 million driver’s licenses, believed to have been stolen from an identity verification company. This incident highlights the growing security risks associated with storing sensitive information with third parties, making it an attractive target for malicious actors.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#DataBreach #CyberSecurity #Privacy #IdentityTheft #DataProtection
📰 Source: gizmodo.com
12

According to decrypt-sourced news, users on the X platform are repeatedly encountering unsolicited password-reset emails in succession. While sector analysts are closely monitoring the situation, X engineers have acknowledged the issue but have not yet confirmed an official data breach. In particular, it would be beneficial for social media users managing $BTC or other assets to pay attention to account security. #CryptoSecurity #X #DataBreach
According to decrypt-sourced news, users on the X platform are repeatedly encountering unsolicited password-reset emails in succession. While sector analysts are closely monitoring the situation, X engineers have acknowledged the issue but have not yet confirmed an official data breach. In particular, it would be beneficial for social media users managing $BTC or other assets to pay attention to account security. #CryptoSecurity #X #DataBreach
30
According to Decrypt, attackers registered Lenovo IDs with victims' email addresses and accessed their Dropbox accounts (including the one with the code $BTC ) and other assets without prompting for a password. This security vulnerability has caused users to question the security of their cloud storage once again. We reiterate the importance of two-factor authentication for digital asset security. #CyberSecurity #DataBreach #CryptoSafety
According to Decrypt, attackers registered Lenovo IDs with victims' email addresses and accessed their Dropbox accounts (including the one with the code $BTC ) and other assets without prompting for a password. This security vulnerability has caused users to question the security of their cloud storage once again. We reiterate the importance of two-factor authentication for digital asset security. #CyberSecurity #DataBreach #CryptoSafety
25
·
--
Something big might be going on! A large number of users are being bombarded with mysteriously password-reset emails they never requested. Official engineers admit there’s a problem, but they still won’t say it’s been hacked.
For the crypto world, this is definitely not a small issue. X is the crypto hub—KOL calls, project announcements, and airdrop information are all there. If the email database really leaked, targeted phishing will come right away. Fake accounts and fake links could wipe out a batch of people.
Do these three things to stay safe: enable two-factor authentication, don’t click random links, and move large assets to a hardware wallet.
In terms of the market, this kind of security panic will likely weigh on sentiment in the short term—people will trade more cautiously and watch out for a surge in phishing scams. But on the flip side, the security narrative could also be used as an excuse for funds to stir up a rally.
Keep your money tightly guarded—don’t be that fish that gets hooked.
#Security #DataBreach $BTC
Something big might be going on! A large number of users are being bombarded with mysteriously password-reset emails they never requested. Official engineers admit there’s a problem, but they still won’t say it’s been hacked.
For the crypto world, this is definitely not a small issue. X is the crypto hub—KOL calls, project announcements, and airdrop information are all there. If the email database really leaked, targeted phishing will come right away. Fake accounts and fake links could wipe out a batch of people.
Do these three things to stay safe: enable two-factor authentication, don’t click random links, and move large assets to a hardware wallet.
In terms of the market, this kind of security panic will likely weigh on sentiment in the short term—people will trade more cautiously and watch out for a surge in phishing scams. But on the flip side, the security narrative could also be used as an excuse for funds to stir up a rally.
Keep your money tightly guarded—don’t be that fish that gets hooked.
#Security #DataBreach $BTC
For the crypto world, this is definitely not a small issue. X is the crypto hub—KOL calls, project announcements, and airdrop information are all there. If the email database really leaked, targeted phishing will come right away. Fake accounts and fake links could wipe out a batch of people.
Do these three things to stay safe: enable two-factor authentication, don’t click random links, and move large assets to a hardware wallet.
In terms of the market, this kind of security panic will likely weigh on sentiment in the short term—people will trade more cautiously and watch out for a surge in phishing scams. But on the flip side, the security narrative could also be used as an excuse for funds to stir up a rally.
Keep your money tightly guarded—don’t be that fish that gets hooked.
#Security #DataBreach $BTC
105
🚨 Data breach settlement worth $5.5 million for a financial software company
Doxim Inc., a financial software provider based in Michigan, reached a class-action settlement of $5.5 million following a data breach incident in 2023. During that event, users’ personal information was compromised. Affected individuals in the United States may claim compensation of up to $5,000 for documented losses, a proportional cash payment, or credit monitoring.
━━━━━━━━━━━━━━
📊 Impact: 📊 Medium
🏷️ OTHER
#DataBreach #CyberSecurity #LegalSettlement #FinancialSoftware
📰 Source: dailyhodl.com
🚨 Data breach settlement worth $5.5 million for a financial software company
Doxim Inc., a financial software provider based in Michigan, reached a class-action settlement of $5.5 million following a data breach incident in 2023. During that event, users’ personal information was compromised. Affected individuals in the United States may claim compensation of up to $5,000 for documented losses, a proportional cash payment, or credit monitoring.
━━━━━━━━━━━━━━
📊 Impact: 📊 Medium
🏷️ OTHER
#DataBreach #CyberSecurity #LegalSettlement #FinancialSoftware
📰 Source: dailyhodl.com
Doxim Inc., a financial software provider based in Michigan, reached a class-action settlement of $5.5 million following a data breach incident in 2023. During that event, users’ personal information was compromised. Affected individuals in the United States may claim compensation of up to $5,000 for documented losses, a proportional cash payment, or credit monitoring.
━━━━━━━━━━━━━━
📊 Impact: 📊 Medium
🏷️ OTHER
#DataBreach #CyberSecurity #LegalSettlement #FinancialSoftware
📰 Source: dailyhodl.com
1
58
·
--
A data breach at Israel’s biggest crypto broker, Bits of Gold, exposed personal details of about 200,000 users.🔐 Names, bank accounts and national IDs were leaked, though funds and digital assets remained untouched. The incident highlights a persistent vulnerability: even centralized platforms can become entry points for attackers, pushing many participants to reconsider self‑custody options.
On Binance, $BTC is trading around $64,336 and $ETH near $1,903, showing the market’s resilience amid security headlines. Still, the breach may spur increased demand for hardware wallets and non‑custodial solutions, as traders look to isolate private keys from third‑party services. It also reminds compliance teams to audit data handling procedures more rigorously.
What steps are you taking to protect your crypto holdings after this kind of breach? #CryptoSecurity #DataBreach #GAMERXERO #Binance
A data breach at Israel’s biggest crypto broker, Bits of Gold, exposed personal details of about 200,000 users.🔐 Names, bank accounts and national IDs were leaked, though funds and digital assets remained untouched. The incident highlights a persistent vulnerability: even centralized platforms can become entry points for attackers, pushing many participants to reconsider self‑custody options.
On Binance, $BTC is trading around $64,336 and $ETH near $1,903, showing the market’s resilience amid security headlines. Still, the breach may spur increased demand for hardware wallets and non‑custodial solutions, as traders look to isolate private keys from third‑party services. It also reminds compliance teams to audit data handling procedures more rigorously.
What steps are you taking to protect your crypto holdings after this kind of breach? #CryptoSecurity #DataBreach #GAMERXERO #Binance
On Binance, $BTC is trading around $64,336 and $ETH near $1,903, showing the market’s resilience amid security headlines. Still, the breach may spur increased demand for hardware wallets and non‑custodial solutions, as traders look to isolate private keys from third‑party services. It also reminds compliance teams to audit data handling procedures more rigorously.
What steps are you taking to protect your crypto holdings after this kind of breach? #CryptoSecurity #DataBreach #GAMERXERO #Binance
28

·
--
Israel’s largest crypto broker Bits of Gold confirms a data breach affecting around 200k customers. Funds and digital assets were not touched, but names, bank details, and national IDs may have been exposed in what the company calls a wider global attack. If you’re a Bits of Gold user, monitor your accounts, beware phishing, and enable 2FA. Stay vigilant in crypto security. $BTC #CryptoNews #DataBreach #BitsOfGold
Israel’s largest crypto broker Bits of Gold confirms a data breach affecting around 200k customers. Funds and digital assets were not touched, but names, bank details, and national IDs may have been exposed in what the company calls a wider global attack. If you’re a Bits of Gold user, monitor your accounts, beware phishing, and enable 2FA. Stay vigilant in crypto security. $BTC #CryptoNews #DataBreach #BitsOfGold
11

·
--
3 wallet and exchange vendors disclosed data breaches in one week — and not one of them lost a single coin or private key.
What happened: SafePal confirmed August 16 that a third-party order-tracking plug-in exposed names, emails, and purchase details for roughly 39,798 customers. The same day, Bits of Gold, Israel's largest regulated crypto broker, disclosed a separate vendor breach reportedly affecting around 200,000 customers. Both land three days after Trezor disclosed its fulfillment partner ShipMonk exposed roughly 14,000 customers.
Why it matters: no seed phrases, private keys, or funds were touched in any of the three. But leaked names, emails, and proof of which hardware wallet you own is exactly the targeting data used for convincing "fake support" phishing later — the same playbook that followed Ledger's 2020 breach for years. None of these three companies were breached directly; their vendors were.
The nuance: Bits of Gold hasn't officially confirmed the 200,000 figure yet — that number is reported, not company-stated. And this is a phishing-setup story, not a theft story, so don't read it as "funds at risk today." The real risk shows up weeks or months later, in a targeted email that already knows your name and your wallet brand.
If you've ever bought a hardware wallet, would you know if your shipping data leaked?
Not financial advice. DYOR.
$BTC #CryptoSecurity #DataBreach #SelfCustody #Phishing
3 wallet and exchange vendors disclosed data breaches in one week — and not one of them lost a single coin or private key.
What happened: SafePal confirmed August 16 that a third-party order-tracking plug-in exposed names, emails, and purchase details for roughly 39,798 customers. The same day, Bits of Gold, Israel's largest regulated crypto broker, disclosed a separate vendor breach reportedly affecting around 200,000 customers. Both land three days after Trezor disclosed its fulfillment partner ShipMonk exposed roughly 14,000 customers.
Why it matters: no seed phrases, private keys, or funds were touched in any of the three. But leaked names, emails, and proof of which hardware wallet you own is exactly the targeting data used for convincing "fake support" phishing later — the same playbook that followed Ledger's 2020 breach for years. None of these three companies were breached directly; their vendors were.
The nuance: Bits of Gold hasn't officially confirmed the 200,000 figure yet — that number is reported, not company-stated. And this is a phishing-setup story, not a theft story, so don't read it as "funds at risk today." The real risk shows up weeks or months later, in a targeted email that already knows your name and your wallet brand.
If you've ever bought a hardware wallet, would you know if your shipping data leaked?
Not financial advice. DYOR.
$BTC #CryptoSecurity #DataBreach #SelfCustody #Phishing
What happened: SafePal confirmed August 16 that a third-party order-tracking plug-in exposed names, emails, and purchase details for roughly 39,798 customers. The same day, Bits of Gold, Israel's largest regulated crypto broker, disclosed a separate vendor breach reportedly affecting around 200,000 customers. Both land three days after Trezor disclosed its fulfillment partner ShipMonk exposed roughly 14,000 customers.
Why it matters: no seed phrases, private keys, or funds were touched in any of the three. But leaked names, emails, and proof of which hardware wallet you own is exactly the targeting data used for convincing "fake support" phishing later — the same playbook that followed Ledger's 2020 breach for years. None of these three companies were breached directly; their vendors were.
The nuance: Bits of Gold hasn't officially confirmed the 200,000 figure yet — that number is reported, not company-stated. And this is a phishing-setup story, not a theft story, so don't read it as "funds at risk today." The real risk shows up weeks or months later, in a targeted email that already knows your name and your wallet brand.
If you've ever bought a hardware wallet, would you know if your shipping data leaked?
Not financial advice. DYOR.
$BTC #CryptoSecurity #DataBreach #SelfCustody #Phishing
49

·
--
🚨 $SFP BREACH EXPOSES 40K USERS — TRUST LINES CRACKING? 🛑
🛡️ SafePal just disclosed a data breach leaking names, home addresses, and phone numbers of nearly 40,000 customers. The flaw sat in an order tracking plugin for over a year, granting unauthorized access to sensitive order details. 🔍 With 30+ phishing sites tied to the stolen data, this isn't a small leak — it's a targeted harvest of wallet-holder identity.
📉 For the token, sentiment is the real casualty here. Hardware wallet brands sell on one thing: impenetrable custody. When that narrative cracks, capital flows shift fast, and $SFP will likely feel the friction long after the headlines fade. ⚠️ This raises a sharper question about third-party plugins in the custody stack — where does your trust actually live?
💬 Are you re-auditing your security setup after this, or does a breach like this change nothing about your hardware wallet conviction? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SFP #DataBreach #SecurityAlert #CryptoRisk
🛡️ ⚠️
🚨 $SFP BREACH EXPOSES 40K USERS — TRUST LINES CRACKING? 🛑
🛡️ SafePal just disclosed a data breach leaking names, home addresses, and phone numbers of nearly 40,000 customers. The flaw sat in an order tracking plugin for over a year, granting unauthorized access to sensitive order details. 🔍 With 30+ phishing sites tied to the stolen data, this isn't a small leak — it's a targeted harvest of wallet-holder identity.
📉 For the token, sentiment is the real casualty here. Hardware wallet brands sell on one thing: impenetrable custody. When that narrative cracks, capital flows shift fast, and $SFP will likely feel the friction long after the headlines fade. ⚠️ This raises a sharper question about third-party plugins in the custody stack — where does your trust actually live?
💬 Are you re-auditing your security setup after this, or does a breach like this change nothing about your hardware wallet conviction? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SFP #DataBreach #SecurityAlert #CryptoRisk
🛡️ ⚠️
🛡️ SafePal just disclosed a data breach leaking names, home addresses, and phone numbers of nearly 40,000 customers. The flaw sat in an order tracking plugin for over a year, granting unauthorized access to sensitive order details. 🔍 With 30+ phishing sites tied to the stolen data, this isn't a small leak — it's a targeted harvest of wallet-holder identity.
📉 For the token, sentiment is the real casualty here. Hardware wallet brands sell on one thing: impenetrable custody. When that narrative cracks, capital flows shift fast, and $SFP will likely feel the friction long after the headlines fade. ⚠️ This raises a sharper question about third-party plugins in the custody stack — where does your trust actually live?
💬 Are you re-auditing your security setup after this, or does a breach like this change nothing about your hardware wallet conviction? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SFP #DataBreach #SecurityAlert #CryptoRisk
🛡️ ⚠️
72

·
--
DATA BREACH HITS 13K WALLETS 🚨 $COTI $AVNT $AKE ON EDGE 📉
The flow just got a fresh layer of turbulence. Trezor's shipping vector breach surfaces 13,689 user records—names, emails, phones, addresses. This isn't a core protocol attack, but it's a classic liquidity squeeze on sentiment. Smart money reads this as a short-term volatility spike, not a structural invalidation.
Devices remain secure, but the market reprices trust instantaneously. Expect a cautious bid under $COTI , $AVNT , and $AKE as traders digest the noise. The real play is watching for the inevitable inefficiency fill—a sweep of low liquidity before any meaningful reclaim.
How are you positioning your risk around this data event? Is this a dip-buying opportunity or a reason to step aside until structure confirms direction? 🧐
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #COTI #AVNT #AKE #DataBreach #CryptoNews
🧠📊
DATA BREACH HITS 13K WALLETS 🚨 $COTI $AVNT $AKE ON EDGE 📉
The flow just got a fresh layer of turbulence. Trezor's shipping vector breach surfaces 13,689 user records—names, emails, phones, addresses. This isn't a core protocol attack, but it's a classic liquidity squeeze on sentiment. Smart money reads this as a short-term volatility spike, not a structural invalidation.
Devices remain secure, but the market reprices trust instantaneously. Expect a cautious bid under $COTI , $AVNT , and $AKE as traders digest the noise. The real play is watching for the inevitable inefficiency fill—a sweep of low liquidity before any meaningful reclaim.
How are you positioning your risk around this data event? Is this a dip-buying opportunity or a reason to step aside until structure confirms direction? 🧐
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #COTI #AVNT #AKE #DataBreach #CryptoNews
🧠📊
The flow just got a fresh layer of turbulence. Trezor's shipping vector breach surfaces 13,689 user records—names, emails, phones, addresses. This isn't a core protocol attack, but it's a classic liquidity squeeze on sentiment. Smart money reads this as a short-term volatility spike, not a structural invalidation.
Devices remain secure, but the market reprices trust instantaneously. Expect a cautious bid under $COTI , $AVNT , and $AKE as traders digest the noise. The real play is watching for the inevitable inefficiency fill—a sweep of low liquidity before any meaningful reclaim.
How are you positioning your risk around this data event? Is this a dip-buying opportunity or a reason to step aside until structure confirms direction? 🧐
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #COTI #AVNT #AKE #DataBreach #CryptoNews
🧠📊
179

SOUTH KOREA FINES BITHUMB FOR USER DATA LEAK $USDT 🔒
The Personal Information Protection Commission slapped Bithumb with a 210 million won penalty for sharing user names, wallet addresses, and birth dates with overseas platforms during USDT order book data transfers. This happened between September and November 2025 without proper consent.
Regulatory scrutiny on exchange data handling is tightening globally. When a top-tier exchange fails basic consent protocols, it creates uncertainty about user privacy standards industry-wide. Are you verifying where your personal information ends up when you trade?
Not financial advice. Always manage your risk.
#USDT #Privacy #DataBreach #CryptoRegulation
🔒
SOUTH KOREA FINES BITHUMB FOR USER DATA LEAK $USDT 🔒
The Personal Information Protection Commission slapped Bithumb with a 210 million won penalty for sharing user names, wallet addresses, and birth dates with overseas platforms during USDT order book data transfers. This happened between September and November 2025 without proper consent.
Regulatory scrutiny on exchange data handling is tightening globally. When a top-tier exchange fails basic consent protocols, it creates uncertainty about user privacy standards industry-wide. Are you verifying where your personal information ends up when you trade?
Not financial advice. Always manage your risk.
#USDT #Privacy #DataBreach #CryptoRegulation
🔒
The Personal Information Protection Commission slapped Bithumb with a 210 million won penalty for sharing user names, wallet addresses, and birth dates with overseas platforms during USDT order book data transfers. This happened between September and November 2025 without proper consent.
Regulatory scrutiny on exchange data handling is tightening globally. When a top-tier exchange fails basic consent protocols, it creates uncertainty about user privacy standards industry-wide. Are you verifying where your personal information ends up when you trade?
Not financial advice. Always manage your risk.
#USDT #Privacy #DataBreach #CryptoRegulation
🔒
13
🚨 Developers are freaking out after reports of a massive GitHub breach started spreading online.
A hacker group called “TeamPCP” claims it broke into GitHub’s internal systems and accessed data connected to nearly 4,000 private repositories. The leaked information allegedly includes internal company files and even parts of GitHub’s proprietary source code. 😳💻
And it gets worse.
The group is reportedly trying to sell the stolen data on underground cybercrime forums for more than $50,000. That alone has sparked major concern across the tech world. 🔥
GitHub says it’s investigating the unauthorized access, but developers aren’t waiting around. Many are already rushing to change API keys, secure repositories, and remove sensitive credentials before things spiral further. ⚠️🔐
If these claims are confirmed, this could turn into one of the biggest security scares the developer community has seen in years. One exposed token or private key can open the door to much larger attacks, which is why cybersecurity experts are telling users to act fast and stay alert.
#GitHub #CyberSecurity #DataBreach
$GTC
{future}(GTCUSDT)
$PHB
{spot}(PHBUSDT)
$EDEN
{future}(EDENUSDT)
🚨 Developers are freaking out after reports of a massive GitHub breach started spreading online.
A hacker group called “TeamPCP” claims it broke into GitHub’s internal systems and accessed data connected to nearly 4,000 private repositories. The leaked information allegedly includes internal company files and even parts of GitHub’s proprietary source code. 😳💻
And it gets worse.
The group is reportedly trying to sell the stolen data on underground cybercrime forums for more than $50,000. That alone has sparked major concern across the tech world. 🔥
GitHub says it’s investigating the unauthorized access, but developers aren’t waiting around. Many are already rushing to change API keys, secure repositories, and remove sensitive credentials before things spiral further. ⚠️🔐
If these claims are confirmed, this could turn into one of the biggest security scares the developer community has seen in years. One exposed token or private key can open the door to much larger attacks, which is why cybersecurity experts are telling users to act fast and stay alert.
#GitHub #CyberSecurity #DataBreach
$GTC
$PHB
$EDEN
A hacker group called “TeamPCP” claims it broke into GitHub’s internal systems and accessed data connected to nearly 4,000 private repositories. The leaked information allegedly includes internal company files and even parts of GitHub’s proprietary source code. 😳💻
And it gets worse.
The group is reportedly trying to sell the stolen data on underground cybercrime forums for more than $50,000. That alone has sparked major concern across the tech world. 🔥
GitHub says it’s investigating the unauthorized access, but developers aren’t waiting around. Many are already rushing to change API keys, secure repositories, and remove sensitive credentials before things spiral further. ⚠️🔐
If these claims are confirmed, this could turn into one of the biggest security scares the developer community has seen in years. One exposed token or private key can open the door to much larger attacks, which is why cybersecurity experts are telling users to act fast and stay alert.
#GitHub #CyberSecurity #DataBreach
$GTC
$PHB
$EDEN
48

$ONG BREAKS ON APPLE SUPPLIER DATA BREACH NEWS 🔥
The leak at Tata Electronics involves unreleased iPhone 18 Pro files and supplier data. This kind of security event often triggers volatility in correlated assets — and $ONG is reacting with increased volume on top-tier exchange order books.
Speculation is already running hot on whether this will drive a dip for accumulation or a breakout. The data point to watch is whether accumulation continues at current levels.
Do you see this as a buying opportunity or a risk to avoid?
Not financial advice. Always manage your risk.
#ONG #News #DataBreach #Crypto
🔥
$ONG BREAKS ON APPLE SUPPLIER DATA BREACH NEWS 🔥
The leak at Tata Electronics involves unreleased iPhone 18 Pro files and supplier data. This kind of security event often triggers volatility in correlated assets — and $ONG is reacting with increased volume on top-tier exchange order books.
Speculation is already running hot on whether this will drive a dip for accumulation or a breakout. The data point to watch is whether accumulation continues at current levels.
Do you see this as a buying opportunity or a risk to avoid?
Not financial advice. Always manage your risk.
#ONG #News #DataBreach #Crypto
🔥
The leak at Tata Electronics involves unreleased iPhone 18 Pro files and supplier data. This kind of security event often triggers volatility in correlated assets — and $ONG is reacting with increased volume on top-tier exchange order books.
Speculation is already running hot on whether this will drive a dip for accumulation or a breakout. The data point to watch is whether accumulation continues at current levels.
Do you see this as a buying opportunity or a risk to avoid?
Not financial advice. Always manage your risk.
#ONG #News #DataBreach #Crypto
🔥
78
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BitcoinReboundsTo$79K
9,066 views
93 Discussing
2
#GrayscalePutsXRPAt26.11%InAdvisorPortfolio
422 views
41 Discussing
3
#PhiladelphiaSemiconductorIndexFalls5.9%
578 views
29 Discussing
4
#SECChairUrgesCongressToAdvanceClarityAct
693 views
30 Discussing
5
#FedHikeOddsRiseTo89%
75,058 views
1,017 Discussing
6
#RLUSDSupplyHitsRecord$2.442B
5,298 views
62 Discussing
7
#AvalancheIntegratesIntoUAEPassDigitalVault
71,972 views
986 Discussing
8
#UKSeeksViewsOnTokenizingGold
58,917 views
749 Discussing
9
#AnthropicCEOCallsForAISlowdown
232,688 views
3,269 Discussing
10
#RevolutDataLeakReportedlyPostedAttackersThreatenDailyReleases
4,335 views
87 Discussing