

#security
security
1.9M views
5,233 Discussing
Hot
Latest

🚨 $BTC ALERT: CA KEY FLOOD THREATENING HTTPS TRUST CHAIN! 💥
The eMudhra CA blunder exposed eight intermediate certificates with private keys reduced to tiny integers—think 4 or 56—making them crackable in a heartbeat. 🦈 This collapse of the HTTPS trust anchor sends shockwaves through any service that leans on TLS, including crypto wallets and exchange APIs.
Top‑tier browsers and language runtimes have already blacklisted the compromised certs, but legacy IoT nodes and outdated clients remain exposed. 📊 If the gap isn’t sealed fast, malicious actors could hijack traffic to siphon credentials or inject false price feeds, rattling market confidence.
💬 Are you certain your node’s trust store is up to date, or could a hidden cert be the next flash‑crash vector? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #Crypto #RiskManagement #Update
🚀 🔥
4

·
--
🚨 $BTC USERS ALERT: Coldcard Flaw Could Expose Your Keys 🛑
The recent Ontario class‑action filing reveals that Coldcard’s firmware has been running a predictable PRNG since March 2021, turning what should be a one‑time seed into a replayable script. 🦈 Smart money already sniffing the leak is shifting to hardware that guarantees true entropy.
For Bitcoin holders, the breach translates into a silent liquidity sweep—if a malicious actor ever extracts the mnemonic, they can front‑run your stash. 📊 Keep an eye on any unusual outbound transactions and consider migrating to a wallet with a hardware‑based RNG. 💡
💬 Are you planning a wallet migration this week or waiting for a patch? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Coldcard #Security #Crypto
🔥 💎
6

Heads up, DeFi: a security researcher just flagged what could be a live attack in progress on Swell.
Spreek — a known on-chain investigator — reports that the keys behind Swell DAO's swETH and rswETH appear compromised. The attacker has been inflating the tokens' net asset value by up to 1% per hour with no real backing, and four malicious upgrade contracts are already deployed. If those clear the multisig, roughly 2,500 ETH (~$6M) in Swell's withdrawal and deposit contracts could be drained.
Two caveats: nothing has been stolen yet — the contracts are deployed but not queued for execution — and the compromise is a suspicion, not a confirmed breach. Spreek's own write-up flags the possible link to the Railway cloud platform as pure timing correlation, and Swell has not issued an official statement.
If you hold swETH or rswETH, this is a sit-tight-and-watch-for-official-word moment. And it raises an uncomfortable question: how many protocols are one compromised key away from a $6M hole?
When the alarm goes off — withdraw first and ask later, or wait for confirmation?
#DeFi #Security #Ethereum #SwellAlert

🚨 $BTC LIGHTNING NETWORK PATCH ALERT: UPDATE OR RISK COMPROMISE! 💥
📊 The newly disclosed CVE‑2026‑111943 cracks the certificate authority chain, putting every Lightning node—lnd, btcd, tapd, litd—in the crosshairs. ⚡ Attackers could hijack channel negotiations, turning the network into a playground for front‑run sweeps.
🦈 Top‑tier operators are already rebuilding with Go 1.27.3 and pushing fresh binaries. If you’re still on legacy builds, you’re handing liquidity hunters a free ticket. 📌 Snap the update now or brace for a cascade of forced closures.
💬 Are you pulling the trigger on the patch or watching the risk snowball?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Lightning #Security #Update
🔥 💎
5

·
--
🚨 $ALT $BMT $IRYS EXPOSED TO UNPATCHED VULNS – VOLATILITY AHEAD 📉
📊 CZ’s advisory flags two active PHP exploits that could siphon credentials from exchange users. 🦈 Smart‑money operators are already scanning order flow for liquidity drains as traders scramble to patch defenses. 📌 The immediate risk is a short‑term sell‑off triggered by heightened caution, not a systemic collapse.
⚡ Expect a brief dip in risk‑off assets while security‑focused positions re‑price. Tighten multi‑factor authentication and monitor on‑chain inflows for any abnormal outflows. 💬 How are you adjusting your exposure in response to the security shock? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ALT #Security #Vulnerability #Crypto
🔥 🦈
3

🚨 $PHP PATCH ALERT: CRITICAL VULNERABILITIES STALLING SERVER STABILITY 🛑
📊 The PHP Foundation admits a structural failure—hesitant decisions and scarce resources have kept remediation on a perpetual loop. 🦈 This delay creates a massive liquidity vacuum for attackers, letting unauthenticated code execution slip through unchecked. ⚡
💡 Emergency patches dropped for two linked exploits, forcing government sites across Europe and Australia offline to scramble for fixes. Developers must act now or watch their services get swept by the next wave. 💬 How quickly will you harden your stack before the next breach surfaces? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #PHP #Security #Patch #Crypto
🔥 💎
3
🚨 $ETH INFRASTRUCTURE PATCH RUSH UNVEILS CRITICAL VULNERABILITIES 🛡️
📊 The latest security blitz across PHP, Node.js and Go closes remote code execution holes that power many DeFi back‑ends. 📈 With TLS validation bypasses and certificate trust flaws fixed, smart‑money bots are re‑evaluating risk on $ETH bridges that rely on these stacks. 💡 Expect a brief shake‑out as liquidity sweeps prune exposed positions, then a steadier climb as confidence restores.
💬 How are you adjusting your exposure to $ETH after these infra updates? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Security #Update #Crypto
🔥 💎
1
⚠️ $AI SUPPLY CHAIN BREACH IN LITELLM V1.107.0 – WATCH THE BACKDOOR! 🚨
📊 The latest 1.107.0 release was silently seeded with three hidden Python files that spring to life as soon as the environment starts, even if LiteLLM isn’t called. 🦈 Hackers are siphoning browser passwords, SSH keys, cloud creds and even model API tokens, then exfiltrating them to a spoofed domain. 📈 This covert pivot follows a March poisoning, showing a pattern of relentless supply‑chain infiltration.
💡 PyPI has pulled the tainted wheels and Docker Hub removed the images, but the damage may already be baked in. Rotate every credential, rebuild your stacks, and fallback to the clean 1.106.2 version. 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AI #SupplyChain #Security #Crypto
🦈 💎
11

·
--
🚨 $BTC ALERT: WHITE HOUSE MONITORS PHP VULNERABILITY IMPACT ON INFRASTRUCTURE 🟢
Federal eyes on a PHP flaw echo through the crypto corridor; any breach on critical web layers can cascade into exchange APIs, wallet gateways, and on‑ramp services 📊. Smart‑money operators are already tightening liquidity buffers, re‑routing order flow through hardened nodes, and scouting for a potential short‑term dip as risk‑off sentiment spikes 🦈. Watch volume contraction on the 4H chart—an abrupt pullback may signal the market pricing in mitigation delays 📈.
💬 How are you adjusting your exposure to $BTC amid the emerging security uncertainty? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #RiskManagement #Security #CryptoNews
🚀 ⚡
4

·
--
🚨 $PHP VULNERABILITY ALERT: GOVERNMENT SITES SHUTDOWN, PATCH RUSH 🔴
🦈 Smart money is already re‑positioning as the PHP flaw ripples through the backbone of 75% of the web. The sudden offline of European government portals creates a liquidity vacuum that could shift demand toward hardened infrastructure tokens. ⚡
📊 Patch deployment on $PHP ‑linked platforms is accelerating, spurring a spike in upgrade‑related transaction volume on a major exchange. Order‑block formations around the new release may act as a short‑term catalyst for re‑entry. 💬 How are you adjusting exposure to web‑infrastructure assets amid this scramble? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #PHP #Security #WebRisk #Crypto
🔥 💎
6
Less than 1% of stolen crypto ever comes back — and the kill switch everyone assumed exists was never pressed.
Blockaid examined 60 major onchain exploits from January to August 2026: $1.18 billion stolen. Just $9.8 million — 0.8% — was returned to victims as of September 2; $81.4 million frozen but unreturned. Only 5 of 60 incidents saw anything frozen or recovered.
Zero came back through issuer blacklists or exchange deposit interception: 16 incidents were eligible, zero actions taken.
$287.1 million sits in known wallets investigators can watch but cannot freeze — mostly ETH, BTC and liquid staking tokens with no central kill switch. ~$229 million traces to April's Drift exploit (107,165 ETH). Median hack-to-movement: 17 minutes; 22% within 60 seconds.
Of the $91.2 million frozen or returned, 99.1% came from protocol governance or validator controls — led by Arbitrum, Syscoin and Stellar.
The safety net is the protocol layer, and it caught 5 of 60. If recovery is a lottery, what makes you trust the protocols you touch? $BTC $ETH NFA. DYOR.
#CryptoNews #DeFi #Security #Blockaid
1
15
·
--
⚠️ $BGB SECURITY UPDATE: PUBLIC LOG EXFILTRATION CONFIRMED 🛡️
📊 The recent breach of PingCAP’s TiDB Cloud exposed only public transaction logs that a top-tier exchange had stored, with no user passwords or private data involved. 🔍 a top-tier exchange ceased using the service over two months ago, limiting exposure to on‑chain data anyone could already view.
🦈 Smart‑money operators treat such data leaks as a reminder to audit every third‑party feed. Maintaining clean pipelines and monitoring for abnormal flow can preserve liquidity integrity. 💡 How are you tightening your risk protocols after this exposure? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BGB #Security #RiskManagement #Crypto
🔥 💎
3

·
--
🚨 $BTC ALERT: PUBLIC TRANSACTION LOGS EXPOSED IN CLOUD BREACH! 💥
📊 A major exchange’s public transaction feed was pulled from TiDB Cloud, a data‑service used for on‑chain analytics. 🦈 The breach stripped only openly viewable logs—no private keys, passwords, or user balances were touched. ⚡ Still, the snapshot gives smart money a glimpse into order flow that was meant to stay opaque, opening a short window for liquidity sweeps. 📌 Traders should watch the next volume spike; any sudden sell‑off could be a reaction to the leaked data.
💬 How will you adjust your position now that the public ledger is temporarily transparent? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #DataBreach #Crypto
🔥 💎
3
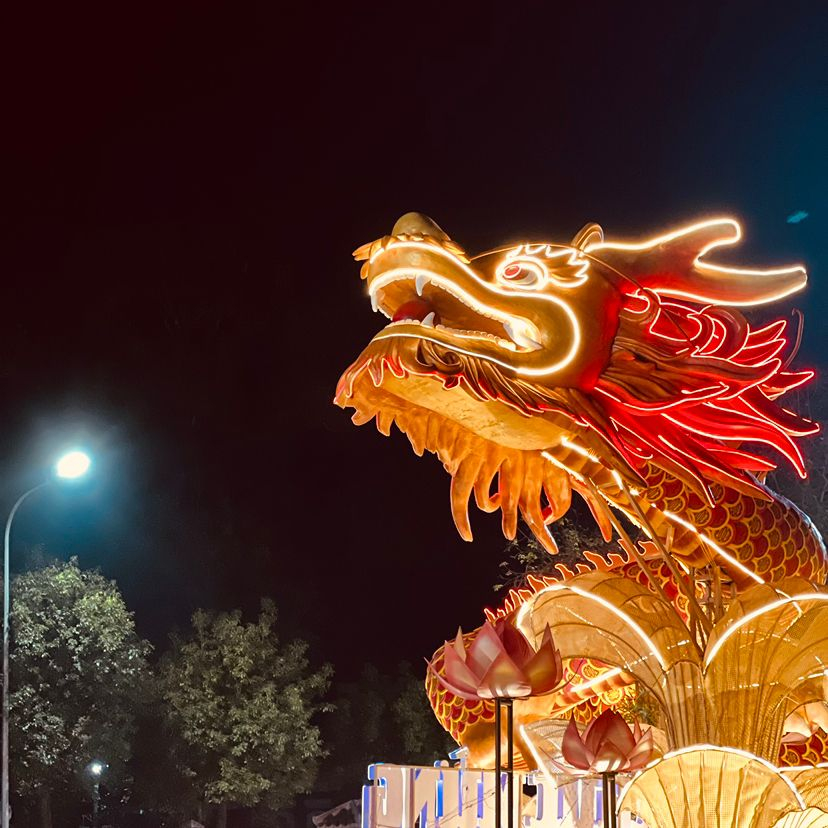
🔍 Analysis: A serious PHP security vulnerability shocks governments worldwide
The PHP Foundation has just admitted to a systemic failure that caused lengthy delays in patching critical security vulnerabilities. This gave attackers an opportunity to execute malicious code remotely without logging in, with widespread impact.
Here are the details:
📍 Impact: Numerous government websites in the Netherlands, Finland, France, Germany, and Australia had to temporarily shut down for updates.
📍 Cause: Delayed decisions and insufficient resources on the part of the PHP Foundation.
📍 Status: Emergency patches have now been released.
A closer look:
Although this is news about a programming language, those of us in crypto should take note because many early Web3 projects and payment gateways still run on PHP. A vulnerability at the infrastructure level like this could become a “gateway” for phishing attacks or wallet takeovers if a project's administration system isn't updated in time.
Looking at the bigger picture, this shows the danger of a technology becoming extremely widespread while still lacking.
👉 Stay the course — Follow [Channel](https://app.binance.com/uni-qr/cpro/Square-Creator-4a0f2008149d?l=en\u0026r=BOZMO8A1)
#AI #AIAgent #Crypto #Security #Hack $BTC
220
·
--
🚨 $BTC USERS ALERT: DARKSWORD iOS TROJAN TARGETING WALLET KEYS 🦈
📊 SlowMist’s deep dive shows DarkSword‑PROV2 surfacing on GitHub in July, then going live by late September. The kit stitches a fully automated pipeline—vulnerability delivery, data exfiltration, and crypto fund consolidation—focused on iOS 18.6‑18.7.2 and 26.0‑26.1, effectively weaponizing public exploits.
⚡ The threat lowers the entry barrier for sophisticated iOS attacks, meaning a single malicious Safari page can compromise mnemonic phrases. Immediate actions: update iOS, avoid untrusted links, treat any visited page as compromised, and revoke all token approvals across chains. 📌
💬 Are you auditing your device’s exposure and revoking stale approvals now? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #ThreatIntel #CryptoSafety
🔥 🦈
8
South Korea's biggest exchange just pulled the plug on one of crypto's oldest layer-1s.
ICX/KRW trading ended today at 15:00 KST — unfilled orders canceled, withdrawals open until November 18. The trigger wasn't volume. The exchange flagged ICX back on August 28, and after review said the security concerns were never resolved.
The incident behind it: on August 27, a replay attack reused two signed withdrawal messages 1,492 times, releasing roughly 120 million ICX and 531,600 bnUSD. The network went dark for about 25 hours.
The part that stings: this was telegraphed for seven weeks. Anyone watching the warning list saw it coming — delistings like this punish inattention, not just the chain.
Now watch the pattern: when one major exchange cites unresolved security, the others rarely wait around. Does a 2017-era chain coasting on reputation change how you judge "established" networks? NFA. DYOR.
$ICX #Delisting #Security
11

CertiK warns: eMudhra certificate flaw still threatens crypto trading bots
- CertiK warns that trading bots and exchange apps may still be exposed to the eMudhra certificate vulnerability
- A browser fix may not protect all software
- Investors and developers need to recheck their automated systems
#BinanceSquare #CryptoNews #Security #CertiK
$btc $eth
#vlikevn Titanbot
Source: CoinTelegraph
225
An attacker minted 10 million $CYS out of thin air on Saturday — and sold 7.2 million of them before anyone could stop it.
At 12:31 UTC on October 17, a forged mint message hit Cysic's cross-chain bridge. The blacklist came 76 minutes later. By then the attacker had dumped 5.65 million CYS in five minutes (~$0.10 each) and moved roughly $727,000 worth of ETH to Ethereum through Mayan, deBridge and SWFT.
The foundation is cautious about the final dollar figure: the mint size alone doesn't set the loss. The bridge stays offline until the security review is done. Consensus and the mainnet were never touched — and the team says no user funds were stolen.
The uncomfortable part: the chain held. The off-chain database feeding the bridge didn't. Bridges keep dying in the plumbing, not the protocol.
Which bridge do you still actually trust with your money?
NFA. DYOR.
$CYS #Crypto #Security #DeFi
479
1,404 wallets drained — not by a smart-contract bug, but by wallet seeds that weren't random enough.
On October 18, Qubic halted its chain at tick 85,371,949 after an attacker exploited weak seed generation: ~2.94 trillion $QU stolen (~$1.4M) from 1,404 wallets. The vulnerable wallets were created on iPhones, iPads and Macs (Safari) before October 18 — or the Qubic iOS app before July 2025.
The response was sharp: 87.1% of the stolen funds got frozen on-chain, and one exchange locked down the other 12.9%. The fix (wallet v4.26.4) swaps a weak pseudorandom generator for a cryptographically secure one. The network's Computors still have to vote on what happens to the frozen funds.
The uncomfortable part: no protocol flaw, no bridge — the most boring layer of the stack did the damage.
When did you last check how your own wallet makes its seed phrase?
NFA. DYOR.
$QU #Crypto #Security #DeFi
6
Big Tech rushes to lock down 8 dangerous eMudhra certificates
* **Private key generation flaw:** A vulnerability in the private key generation process allows anyone to predict the keys.
* **Enables HTTPS certificate spoofing:** Exploiting this flaw, malicious actors can create fake HTTPS certificates for any website.
* **Emergency action by tech giants:** Major companies are rushing to block and revoke 8 eMudhra certificates to prevent the creation of fake websites.
#BinanceSquare #CryptoNews #Web3 #Security #TechNews
$btc $eth
vlikevn Titanbot
Source: CoinTelegraph
137
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BinancePick
310,996 views
48,113 Discussing
2
#TeslaSlides5%PreMarket
98,243 views
1,041 Discussing
3
#KOSPISinks3.52%ToLowestCloseSinceApril
26,446 views
656 Discussing
4
#TeslaAndNvidiaToInvest$2.8BInSamsungElectroMechanics
2,823 views
71 Discussing
5
#ChinaSeeksToSeize61800BTC
59,413 views
769 Discussing
6
#BitcoinETFsPullIn$1.08BInThreeDays
5,519 views
66 Discussing
7
#EarningsSeason
2.7M views
12,889 Discussing
8
#EthereumSurpasses$2500
46,731 views
266 Discussing
9
#BitcoinDropsBelow$84K
24,567 views
108 Discussing
10
#FirstUNIBlockTradeViaRegulatedTradFiChannelCompleted
3,084 views
80 Discussing