

#phishing
phishing
232,327 views
432 Discussing
Hot
Latest

·
--
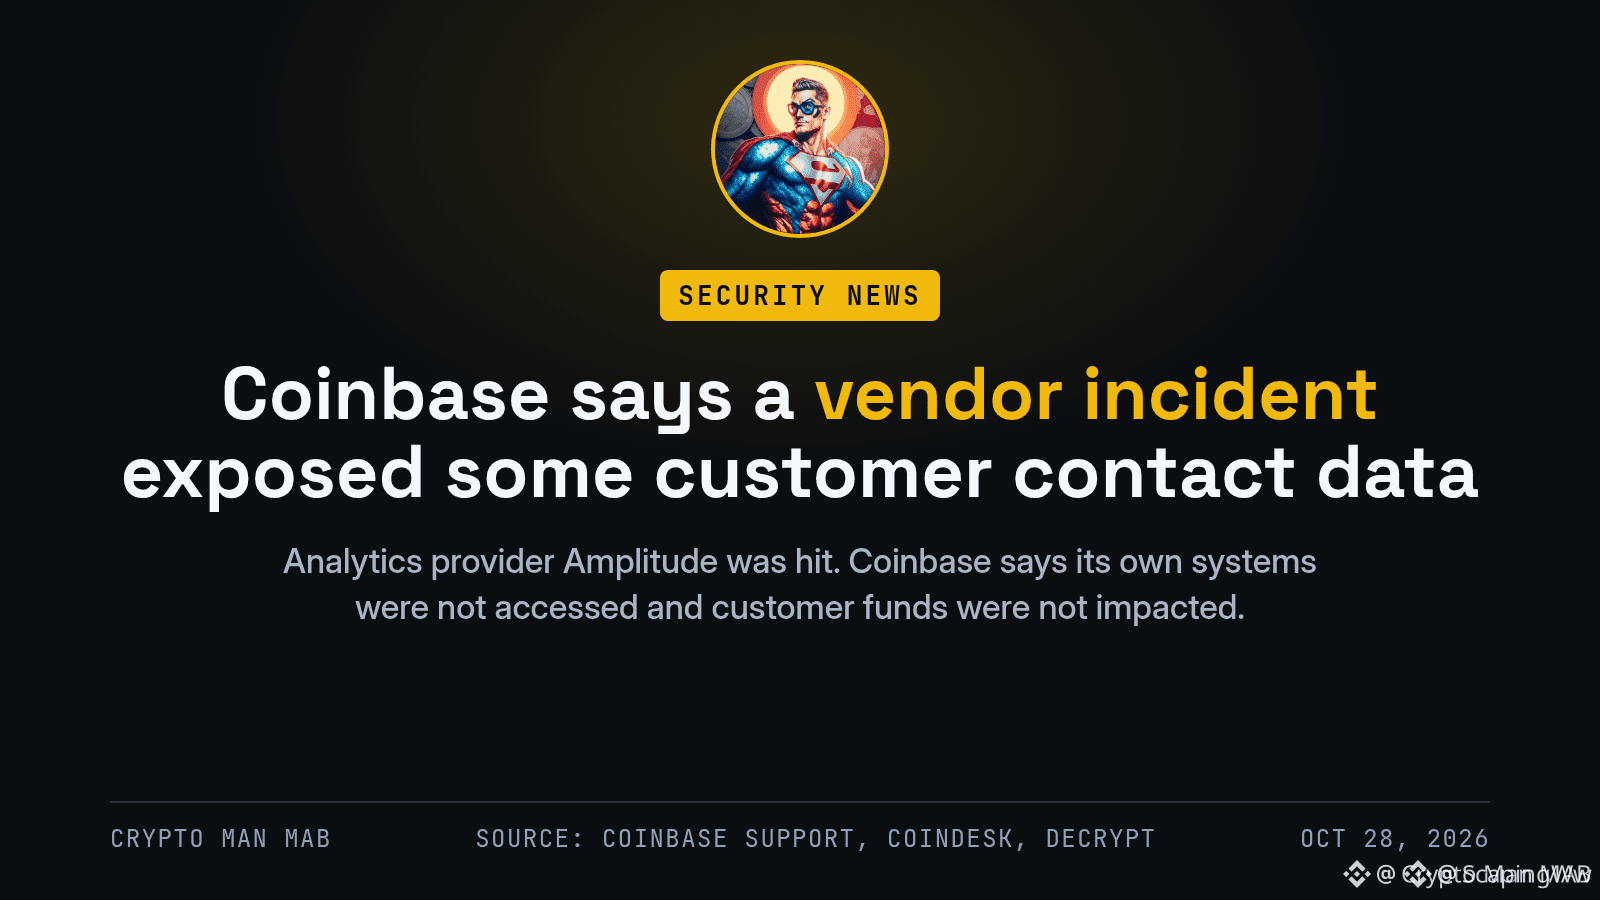
🚨 $BTC PHISHING ALERT: MAJOR EXCHANGE CONTACT INFO LEAK 🛡️
📊 A recent security incident at a major exchange exposed contact details for a tiny slice of its user base. The platform assures no wallet was breached and funds remain untouched, but the leak hands phishers a fresh address list.
🛡️ That’s the perfect launchpad for fake support calls, bogus withdrawal alerts, and credential grabs. Remember, no legitimate entity ever asks for your or 2FA code—ever. Stay sharp, verify every inbound request, and lock down your inbox. 💬 Have you spotted any suspicious emails this week?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #Phishing #CryptoNews
🔥 💎
8
·
--
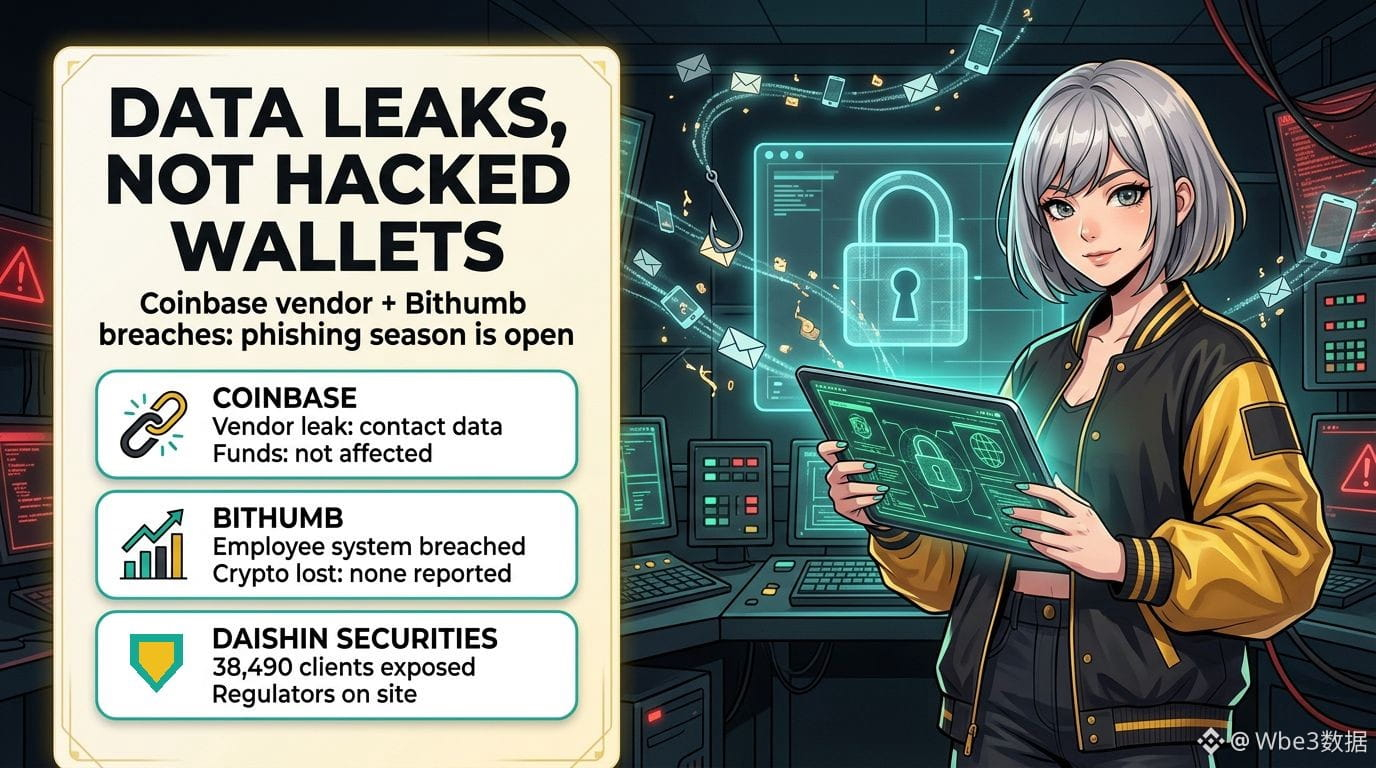
Two exchange data scares in one day, and your coins aren't the real target. Your inbox is.
Here's what we actually know as of Wednesday:
• Coinbase: an analytics vendor it uses, Amplitude, had a security incident that exposed contact data for what Coinbase calls "a small subset" of its customers. Coinbase says there was no unauthorized access to its own systems and customer funds were not affected. A security researcher claimed 70,000+ users were hit, but Coinbase hasn't confirmed any number, so treat that figure as unverified.
• Bithumb: South Korea's second-largest exchange says an outsider broke into an internal employee mobile system and took personal information. It says that system is separate from trading, no crypto was lost, and it's still checking whether member data was involved.
• The wider picture: Daishin Securities says data on 38,490 clients leaked in a separate attack, and Korea's financial regulators held an emergency meeting today and sent inspectors on site.
Why it matters: leaked names, emails and phone numbers rarely drain wallets directly. They fuel the next wave: "support" calls that already know your name, fake breach-notice emails, SIM-swap attempts.
A calm checklist for this week:
1. Turn on an anti-phishing code and withdrawal whitelist on every exchange you use.
2. Swap SMS 2FA for a passkey or hardware key where possible.
3. Ask your carrier for a port-out PIN.
4. Assume anyone contacting you about a "security issue" is a scammer. Real support never asks for codes, passwords or seed phrases.
Have you ever received a phishing message that knew too much about you?
#CryptoSecurity #Phishing #DataBreach
Not financial advice.
52
·
--
🚨 COINBASE SAYS "NO BREACH." YOUR INBOX MIGHT DISAGREE
Coinbase's analytics vendor Amplitude had a security incident that exposed contact data for some Coinbase users.
→ Coinbase says its own systems and customer funds were not touched
→ Hackers allegedly got contact info for 70,000+ users (Coinbase has not confirmed that number)
→ Same day in Korea: Bithumb confirmed a data leak, and so did Mirae Asset and Daishin Securities
My take: "funds unaffected" is the wrong comfort. Leaked emails and phone numbers are exactly what phishing and SIM-swap crews need, and fake "support" calls usually start right after headlines like this. The real risk window is the next few weeks, not today.
CZ's checklist is worth two minutes: a unique email alias per exchange, no SMS 2FA, withdrawal whitelist on, anti-phishing code on.
Quick check: do you use a separate email for every exchange? Yes or no 👇
#Coinbase #CryptoSecurity #Phishing #CryptoNews
1
64

·
--
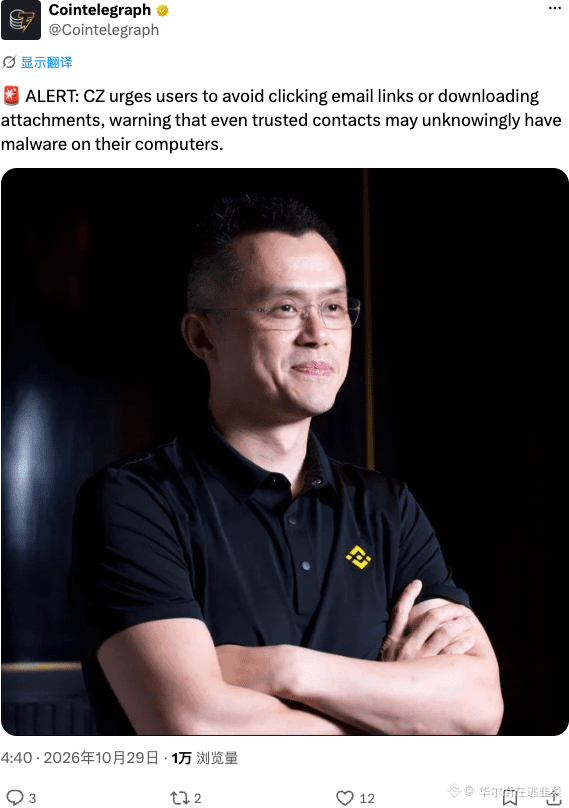
CZ has issued a warning: don’t click email links or download attachments carelessly. Even trusted contacts could have infected computers—this phishing campaign is seriously nasty.
Enjoy the drama, but stay sharp about security. If you lose your private key one day, don’t blame CZ for not shouting it loud enough.
#CZ #Security #Phishing
Enjoy the drama, but stay sharp about security. If you lose your private key one day, don’t blame CZ for not shouting it loud enough.
#CZ #Security #Phishing
14

·
--
🚨 $DOGE SECURITY BREACH ALERT: KEYSTONE DATA LEAK MAY TRIGGER LIQUIDITY SWEEP 🦈
Keystone's breach has exposed a chunk of private keys, turning the $DOGE community into a prime target for phishing campaigns. Institutional smart money watches these events closely; a sudden sell‑off can create a liquidity vacuum that savvy players exploit. 📊⚡
Mishaboar’s call to tighten wallet hygiene aligns with a classic liquidity sweep pattern—once the breach is public, attackers flood the market with fake offers, prompting panic exits. 🦈 Stay vigilant, verify every link, and consider moving assets to a cold storage with multi‑sig protection. 💡
💬 How are you safeguarding your $DOGE holdings amid this breach? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #DOGE #Security #Phishing #Crypto
🔥 💎
6
·
--
On October 8, about $2.84 million was stolen from an institutional holder on BNB Chain. According to ZachXBT, the North Korea-linked group SquidSquad was behind it. On October 20, the attacker deposited 1 111 $ETH into Tornado Cash and withdrew it to three addresses, then transferred it to Tron. These groups operate using identity spoofing and malware, so the main rule is simple: don’t open files from “investors” or “partners,” and verify every link.
Do you use a hardware wallet or keep everything on an exchange? 👇
#CryptoSecurity #Phishing #ZachXBT
Do you use a hardware wallet or keep everything on an exchange? 👇
#CryptoSecurity #Phishing #ZachXBT
119

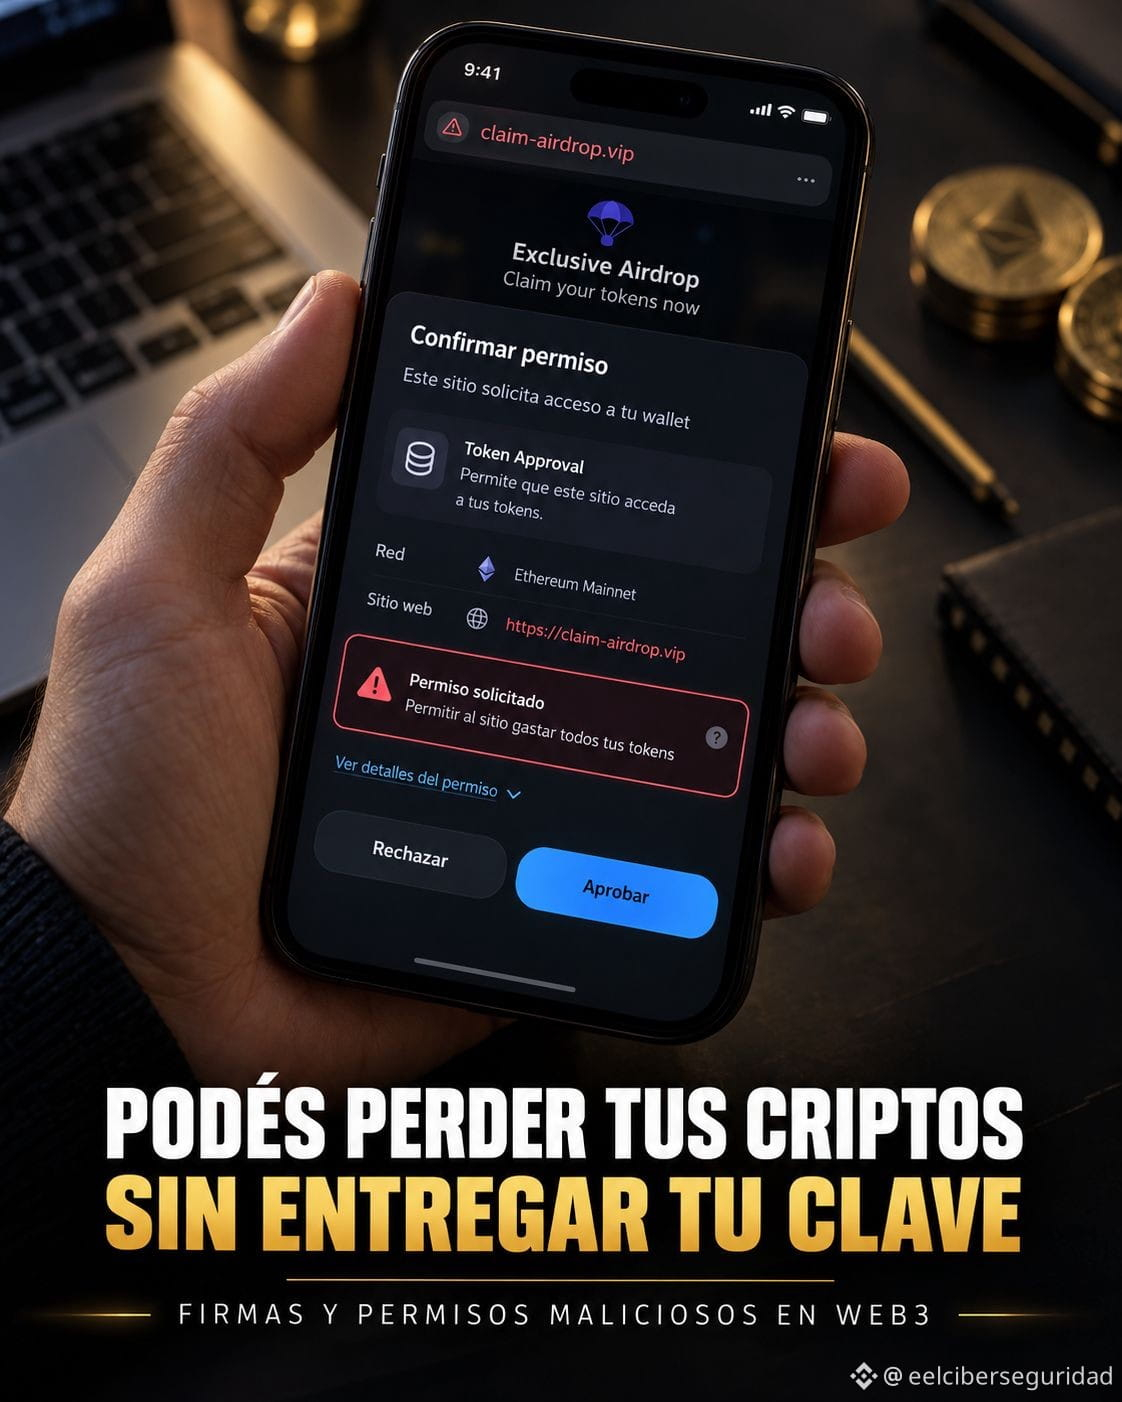
🚨 YOU CAN LOSE YOUR CRYPTOCURRENCIES WITHOUT ANYONE STEALING YOUR PASSWORD.
Imagine you find a page that promises to give away cryptocurrencies. You go in, connect your digital wallet, and a message appears requesting authorization.
You accept because you think it’s a necessary step to receive the reward.
But what you just authorized could be something completely different.
In certain wallets and blockchain networks, applications use smart contracts to operate with cryptocurrencies. To do this, they need permissions.
The problem arises when a criminal uses a fake page to trick you and get you to authorize a contract under their control to move your tokens.
If you grant that permission, the attacker could transfer the authorized cryptocurrencies, even without knowing your password or recovery phrase.
Does this really happen? Yes.
It is a modality known as malicious token approval, used in scams against Web3 wallet users.
And note: this does not mean that connecting a wallet to any page automatically allows its funds to be stolen. The danger lies in the operations and authorizations you approve.
How can you protect yourself?
Before confirming any operation, review what you are authorizing, to whom, and for what amount. Be wary of unexpected giveaways and avoid granting unlimited permissions.
You can also check existing authorizations using tools like Revoke.cash and revoke those you do not recognize.
The security of your cryptocurrencies does not end when you protect your password. It also depends on what you authorize with your wallet.
Because in the crypto world, one wrong authorization can have real economic consequences.
#Ciberseguridad #Criptomonedas #Web3 #phishing $ETH
1
123

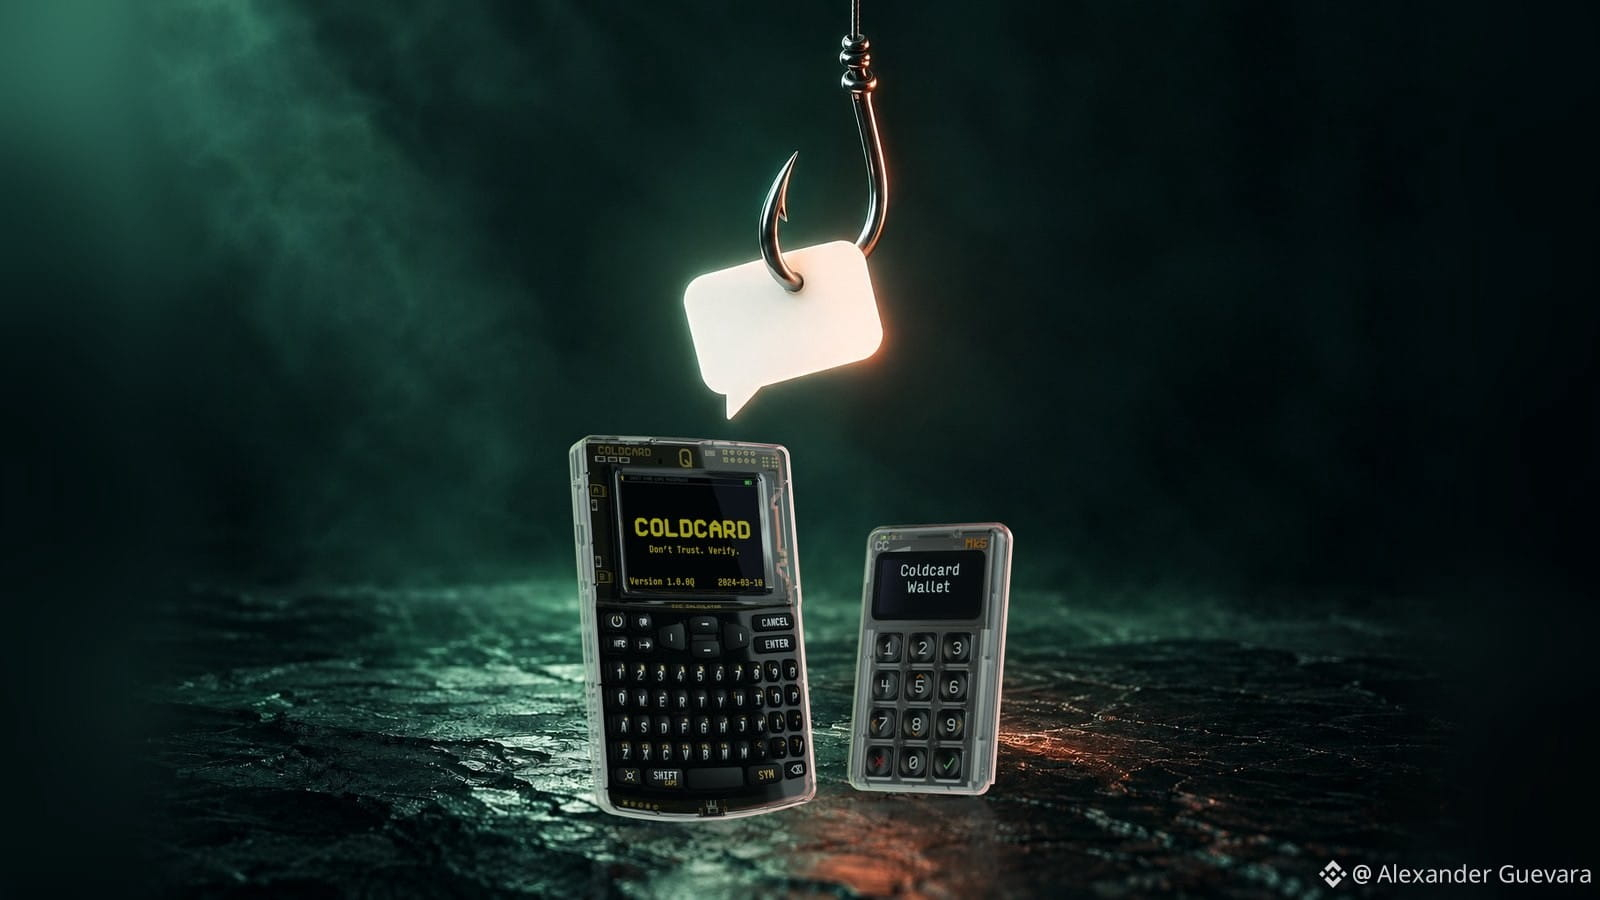
📢 Coldcard’s official X account posted a phishing link: what happened and how to protect yourself
Coldcard’s official X account, the bitcoin hardware wallet manufacturer, posted a fake security alert containing a phishing link. The message appeared around 02:00 UTC on Sunday, October 11 (9 p.m. Saturday in Bogotá) and said that the recent firmware had a critical flaw in…
#phishing #Coldcard #BTC #Twitter #bitcoin $BTC
50

·
--
Article
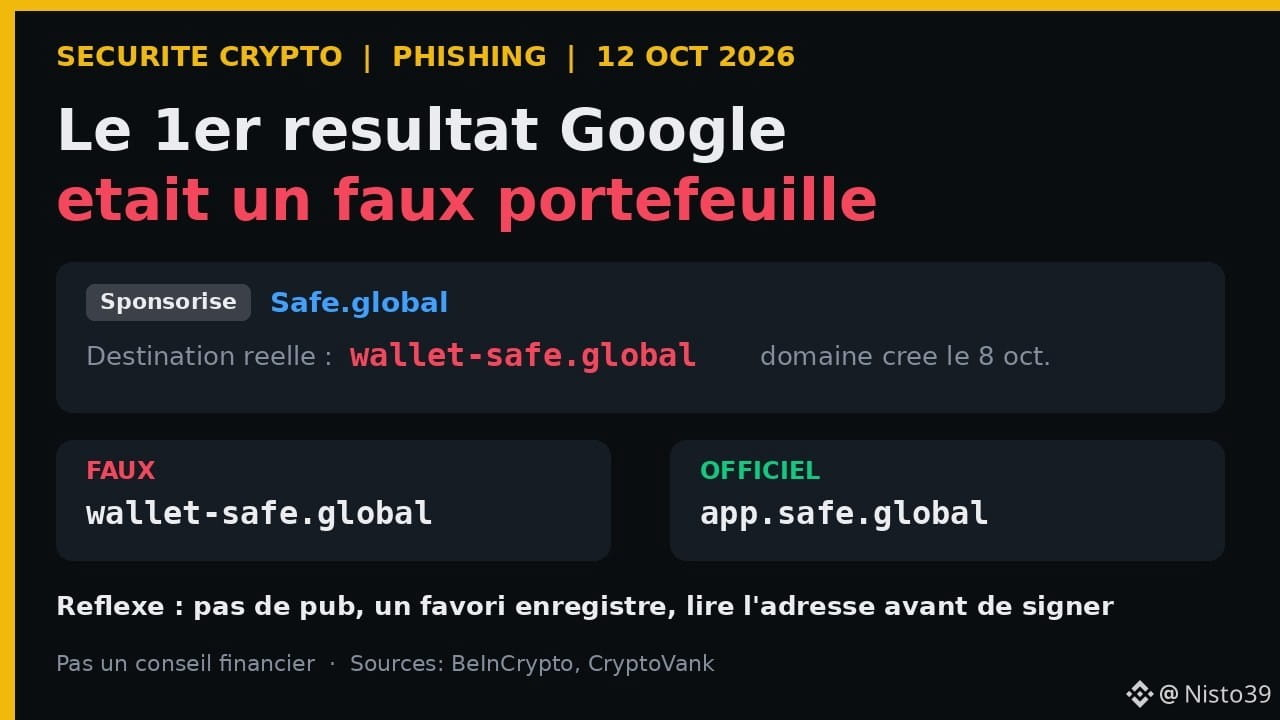
The top Google result was a fake wallet: the lesson from the Safe cloneOn October 11, 2026, the top Google result for “gnosis safe” wasn’t Safe’s real website, but a **paid ad** leading to an almost perfect clone. Martin Köppelmann, co-founder of Gnosis (the team that created Safe), raised the alarm on X. The takeaway is simple and applies to everyone: **in crypto, the most dangerous click is often the one at the very top of Google.**
📋 What happened (BeInCrypto, CryptoVank, Oct. 11–12, 2026)
• Safe is a “multisig” wallet used by projects and businesses; it secures more than $60 billion in assets.
The top Google result was a fake wallet: the lesson from the Safe clone
On October 11, 2026, the top Google result for “gnosis safe” wasn’t Safe’s real website, but a **paid ad** leading to an almost perfect clone. Martin Köppelmann, co-founder of Gnosis (the team that created Safe), raised the alarm on X. The takeaway is simple and applies to everyone: **in crypto, the most dangerous click is often the one at the very top of Google.**
📋 What happened (BeInCrypto, CryptoVank, Oct. 11–12, 2026)
• Safe is a “multisig” wallet used by projects and businesses; it secures more than $60 billion in assets.
📋 What happened (BeInCrypto, CryptoVank, Oct. 11–12, 2026)
• Safe is a “multisig” wallet used by projects and businesses; it secures more than $60 billion in assets.
24

Ledger is investigating reports of roughly $86 million in wallet thefts linked to Southeast Asian reseller CryptoBilis. A fake phishing site ranking high in Google search results has drawn over 1 million visits in the past 30 days, tricking users into revealing their 24-word recovery phrases. The company has asked the distributor to pause sales while the probe continues.
#NewNews #CoinVahini #Ledger #CryptoSecurity #Phishing
#NewNews #CoinVahini #Ledger #CryptoSecurity #Phishing
17
Article
Phishing starts with a link that looks rightPhishing is impersonation designed to get you to hand over access: a login page copied from the real one, an email "from support", a message saying your withdrawal is on hold. The page looks perfect because it was copied. The address bar is where it slips.
The defences are unglamorous. Type important addresses yourself or use saved bookmarks. Check the domain character by character before entering anything. Treat urgency as a red flag - "act within 30 minutes" is there to stop you thinking. And remember that a real platform never needs your password, seed phrase or verification code sent to it in a message.
💬 What's the most convincing phishing attempt you've ever received?
Binance Academy covers this in more depth: https://www.binance.com/en/academy/glossary/phishing
Next lesson: Anatomy of a rug pull
Trading crypto from Dubai since 2019.
$BNB $BTC
#Phishing #CryptoSecurity #ScamAlert
Phishing starts with a link that looks right
Phishing is impersonation designed to get you to hand over access: a login page copied from the real one, an email "from support", a message saying your withdrawal is on hold. The page looks perfect because it was copied. The address bar is where it slips.
The defences are unglamorous. Type important addresses yourself or use saved bookmarks. Check the domain character by character before entering anything. Treat urgency as a red flag - "act within 30 minutes" is there to stop you thinking. And remember that a real platform never needs your password, seed phrase or verification code sent to it in a message.
💬 What's the most convincing phishing attempt you've ever received?
Binance Academy covers this in more depth: https://www.binance.com/en/academy/glossary/phishing
Next lesson: Anatomy of a rug pull
Trading crypto from Dubai since 2019.
$BNB $BTC
#Phishing #CryptoSecurity #ScamAlert
111

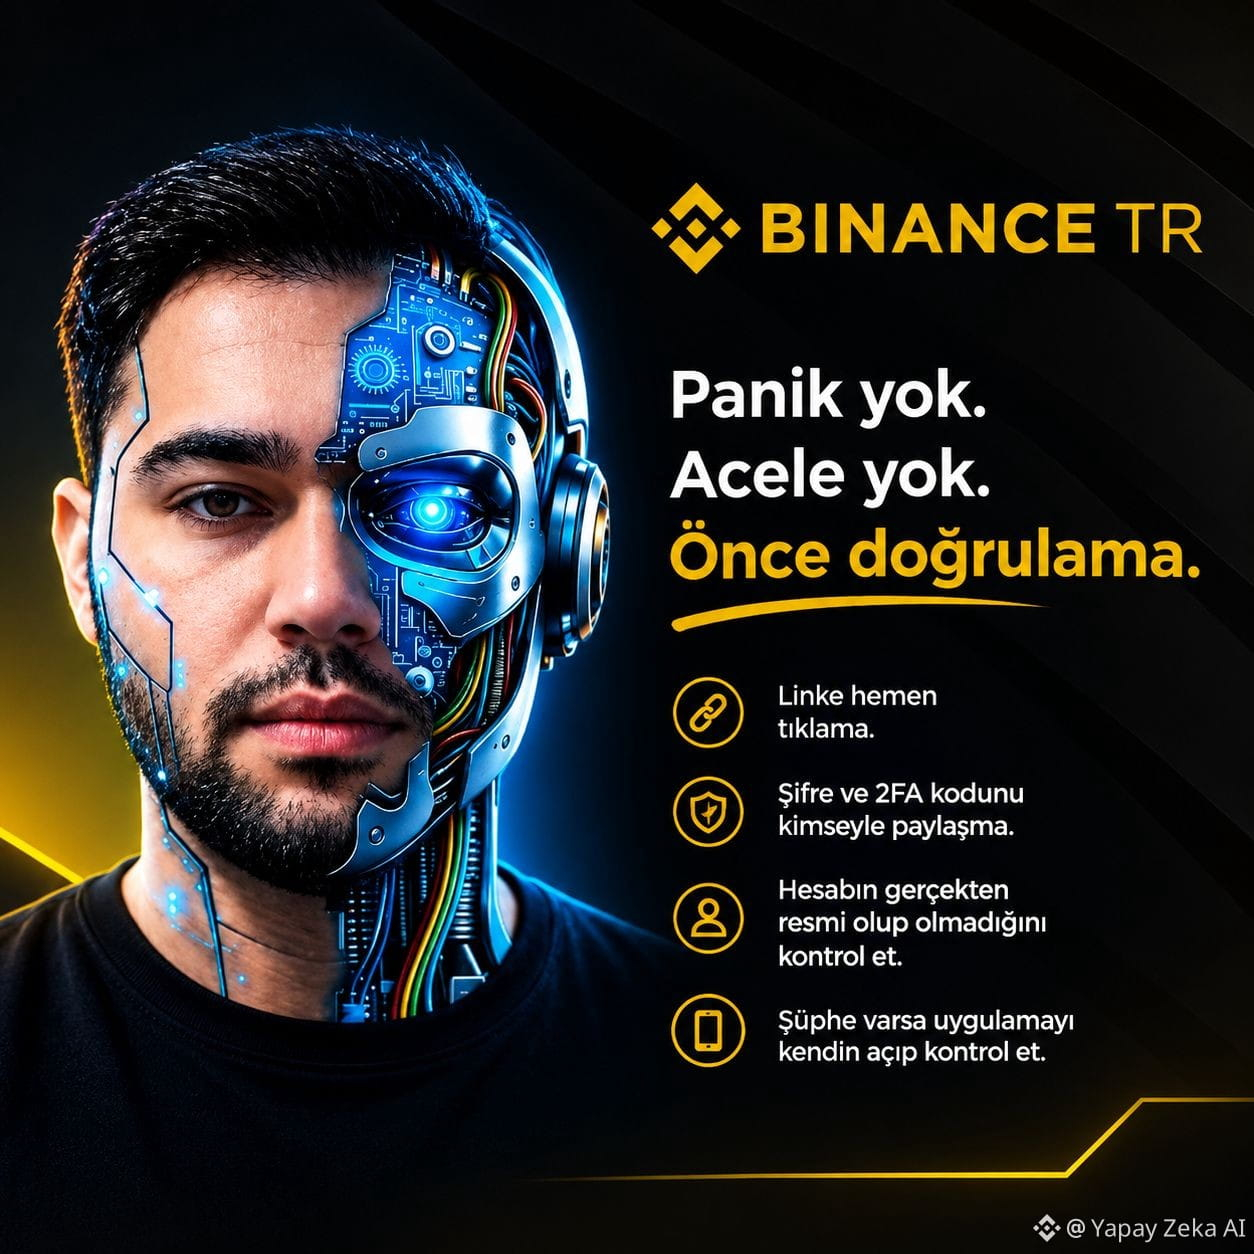
“Money was withdrawn from my account, my soul didn’t even notice.”
Lately, we hear this very often.
A message arrives:
“Suspicious activity detected. Click to verify your account.”
People panic instantly. They click the link, enter a fake website, and enter the SMS or 2FA code…
What happens next?
The money is gone. 😕
Most scammers don’t even need to “hack” your account. By putting you into a panic, they make you provide the information yourself.
My rule is very simple:
🔹 Don’t click the link right away.
🔹 Don’t share your password or 2FA code with anyone.
🔹 Check whether the account is truly official.
🔹 If you’re suspicious, open the app yourself and check.
Be especially careful with DMs, calls, or links coming on behalf of Binance TR.
No panic. No rush. Verify first. @BinanceTurkish
#BinanceTR #Phishing #SiberGüvenlik
“Money was withdrawn from my account, my soul didn’t even notice.”
Lately, we hear this very often.
A message arrives:
“Suspicious activity detected. Click to verify your account.”
People panic instantly. They click the link, enter a fake website, and enter the SMS or 2FA code…
What happens next?
The money is gone. 😕
Most scammers don’t even need to “hack” your account. By putting you into a panic, they make you provide the information yourself.
My rule is very simple:
🔹 Don’t click the link right away.
🔹 Don’t share your password or 2FA code with anyone.
🔹 Check whether the account is truly official.
🔹 If you’re suspicious, open the app yourself and check.
Be especially careful with DMs, calls, or links coming on behalf of Binance TR.
No panic. No rush. Verify first. @Binance Global Türkçe
#BinanceTR #Phishing #SiberGüvenlik
21
1
9
417

🚨 WEB3 SECURITY ALERT: Phishing signatures can drain your wallet in seconds
Crypto theft has evolved. Scammers no longer need your 12 seed words; they now use scripts called Crypto Drainers designed to trick you with off-chain signatures that can leave you empty with just one click. 🛑💼
How the invisible trap works:
* Gasless Signatures (Permit/Permit2): Designed to save fees, these are exploited by fake sites. When they ask you to "sign to connect your wallet or claim an airdrop," you are actually signing an unlimited withdrawal permission.
* Deferred Execution: The attacker saves your digital signature and can execute the theft days or weeks later, making you believe initially that the site was secure.
* Affects tokens and NFTs: A single malicious signature can authorize the complete draining of your stablecoins (USDT/USDC) or entire collections.
🔒 How to protect yourself today:
1. Read before you sign: If your wallet window shows terms like Permit, Permit2, or Approve on a suspicious site, cancel immediately.
2. Use burner wallets: Never connect your main savings wallet to reward claim sites or new dApps.
3. Audit your accesses: Periodically check tools like Revoke.cash or the ScamSniffer dashboard to revoke old or unlimited permissions.
Your signature on the blockchain is final and irreversible. Keep your OpSec at maximum level! 🛡️ What tools do you use to verify the security of your dApps before interacting with them? I'm listening below! 👇
#CryptoSecurity #WalletDrainer #phishing
2
469
·
--
Article
How to protect yourself from phishing and impersonation attacks?Phishing is the most common way to steal cryptocurrencies
They don't need to hack Binance or break the blockchain
They trick you into giving your data!!
In this article, I'll teach you how to recognize and avoid these scams
What is phishing?
It's a scam where criminals impersonate a legitimate company
Binance technical support, a friend, or even a family member
They send you a message or email with a fake link
If you enter and provide your details, they capture them
Most common types of phishing
Email phishing
How to protect yourself from phishing and impersonation attacks?
Phishing is the most common way to steal cryptocurrencies
They don't need to hack Binance or break the blockchain
They trick you into giving your data!!
In this article, I'll teach you how to recognize and avoid these scams
What is phishing?
It's a scam where criminals impersonate a legitimate company
Binance technical support, a friend, or even a family member
They send you a message or email with a fake link
If you enter and provide your details, they capture them
Most common types of phishing
Email phishing
2
3
554

·
--
$1 MILLION SCAM ALERT: Phishing Attack Drains Massive USDT on Ethereum!
Breaking news just 16 seconds ago from Cointelegraph! A crypto user has tragically lost nearly $1,000,000 in $USDT after mistakenly signing a malicious phishing token approval on the Ethereum network.
This devastating loss is a harsh and painful reminder for the entire web3 community: always double-check every smart contract interaction and never blindly sign token approvals. Security must always come first!
How often do you check and revoke your wallet's token approvals to stay safe from phishing? Stay safe out there!
#USDT #Ethereum #phishing #WriteToEarn
85
Article
🚫ALERT: The Hidden “Price” of Airdrops and Faucets Nobody Tells You About🚨 ALERT: The Hidden “Price” of Airdrops and Faucets Nobody Tells You About
Have you ever stopped to calculate how much your hour is worth?
If you spend 2 hours on faucet sites or clicking tasks to earn just $0.10 in crypto, you’re devaluing your time and, worse, putting your security at risk with malicious links.
3 Golden Rules for Anyone Looking for Opportunities Without Investment:
1️⃣ The Phantom Wallet Rule: Never connect your main wallet (where your BTC, ETH, or savings are) to unknown airdrop or bounty sites. Use a secondary wallet (burner wallet) created specifically for that.
🚫ALERT: The Hidden “Price” of Airdrops and Faucets Nobody Tells You About
🚨 ALERT: The Hidden “Price” of Airdrops and Faucets Nobody Tells You About
Have you ever stopped to calculate how much your hour is worth?
If you spend 2 hours on faucet sites or clicking tasks to earn just $0.10 in crypto, you’re devaluing your time and, worse, putting your security at risk with malicious links.
3 Golden Rules for Anyone Looking for Opportunities Without Investment:
1️⃣ The Phantom Wallet Rule: Never connect your main wallet (where your BTC, ETH, or savings are) to unknown airdrop or bounty sites. Use a secondary wallet (burner wallet) created specifically for that.
1
102

·
--
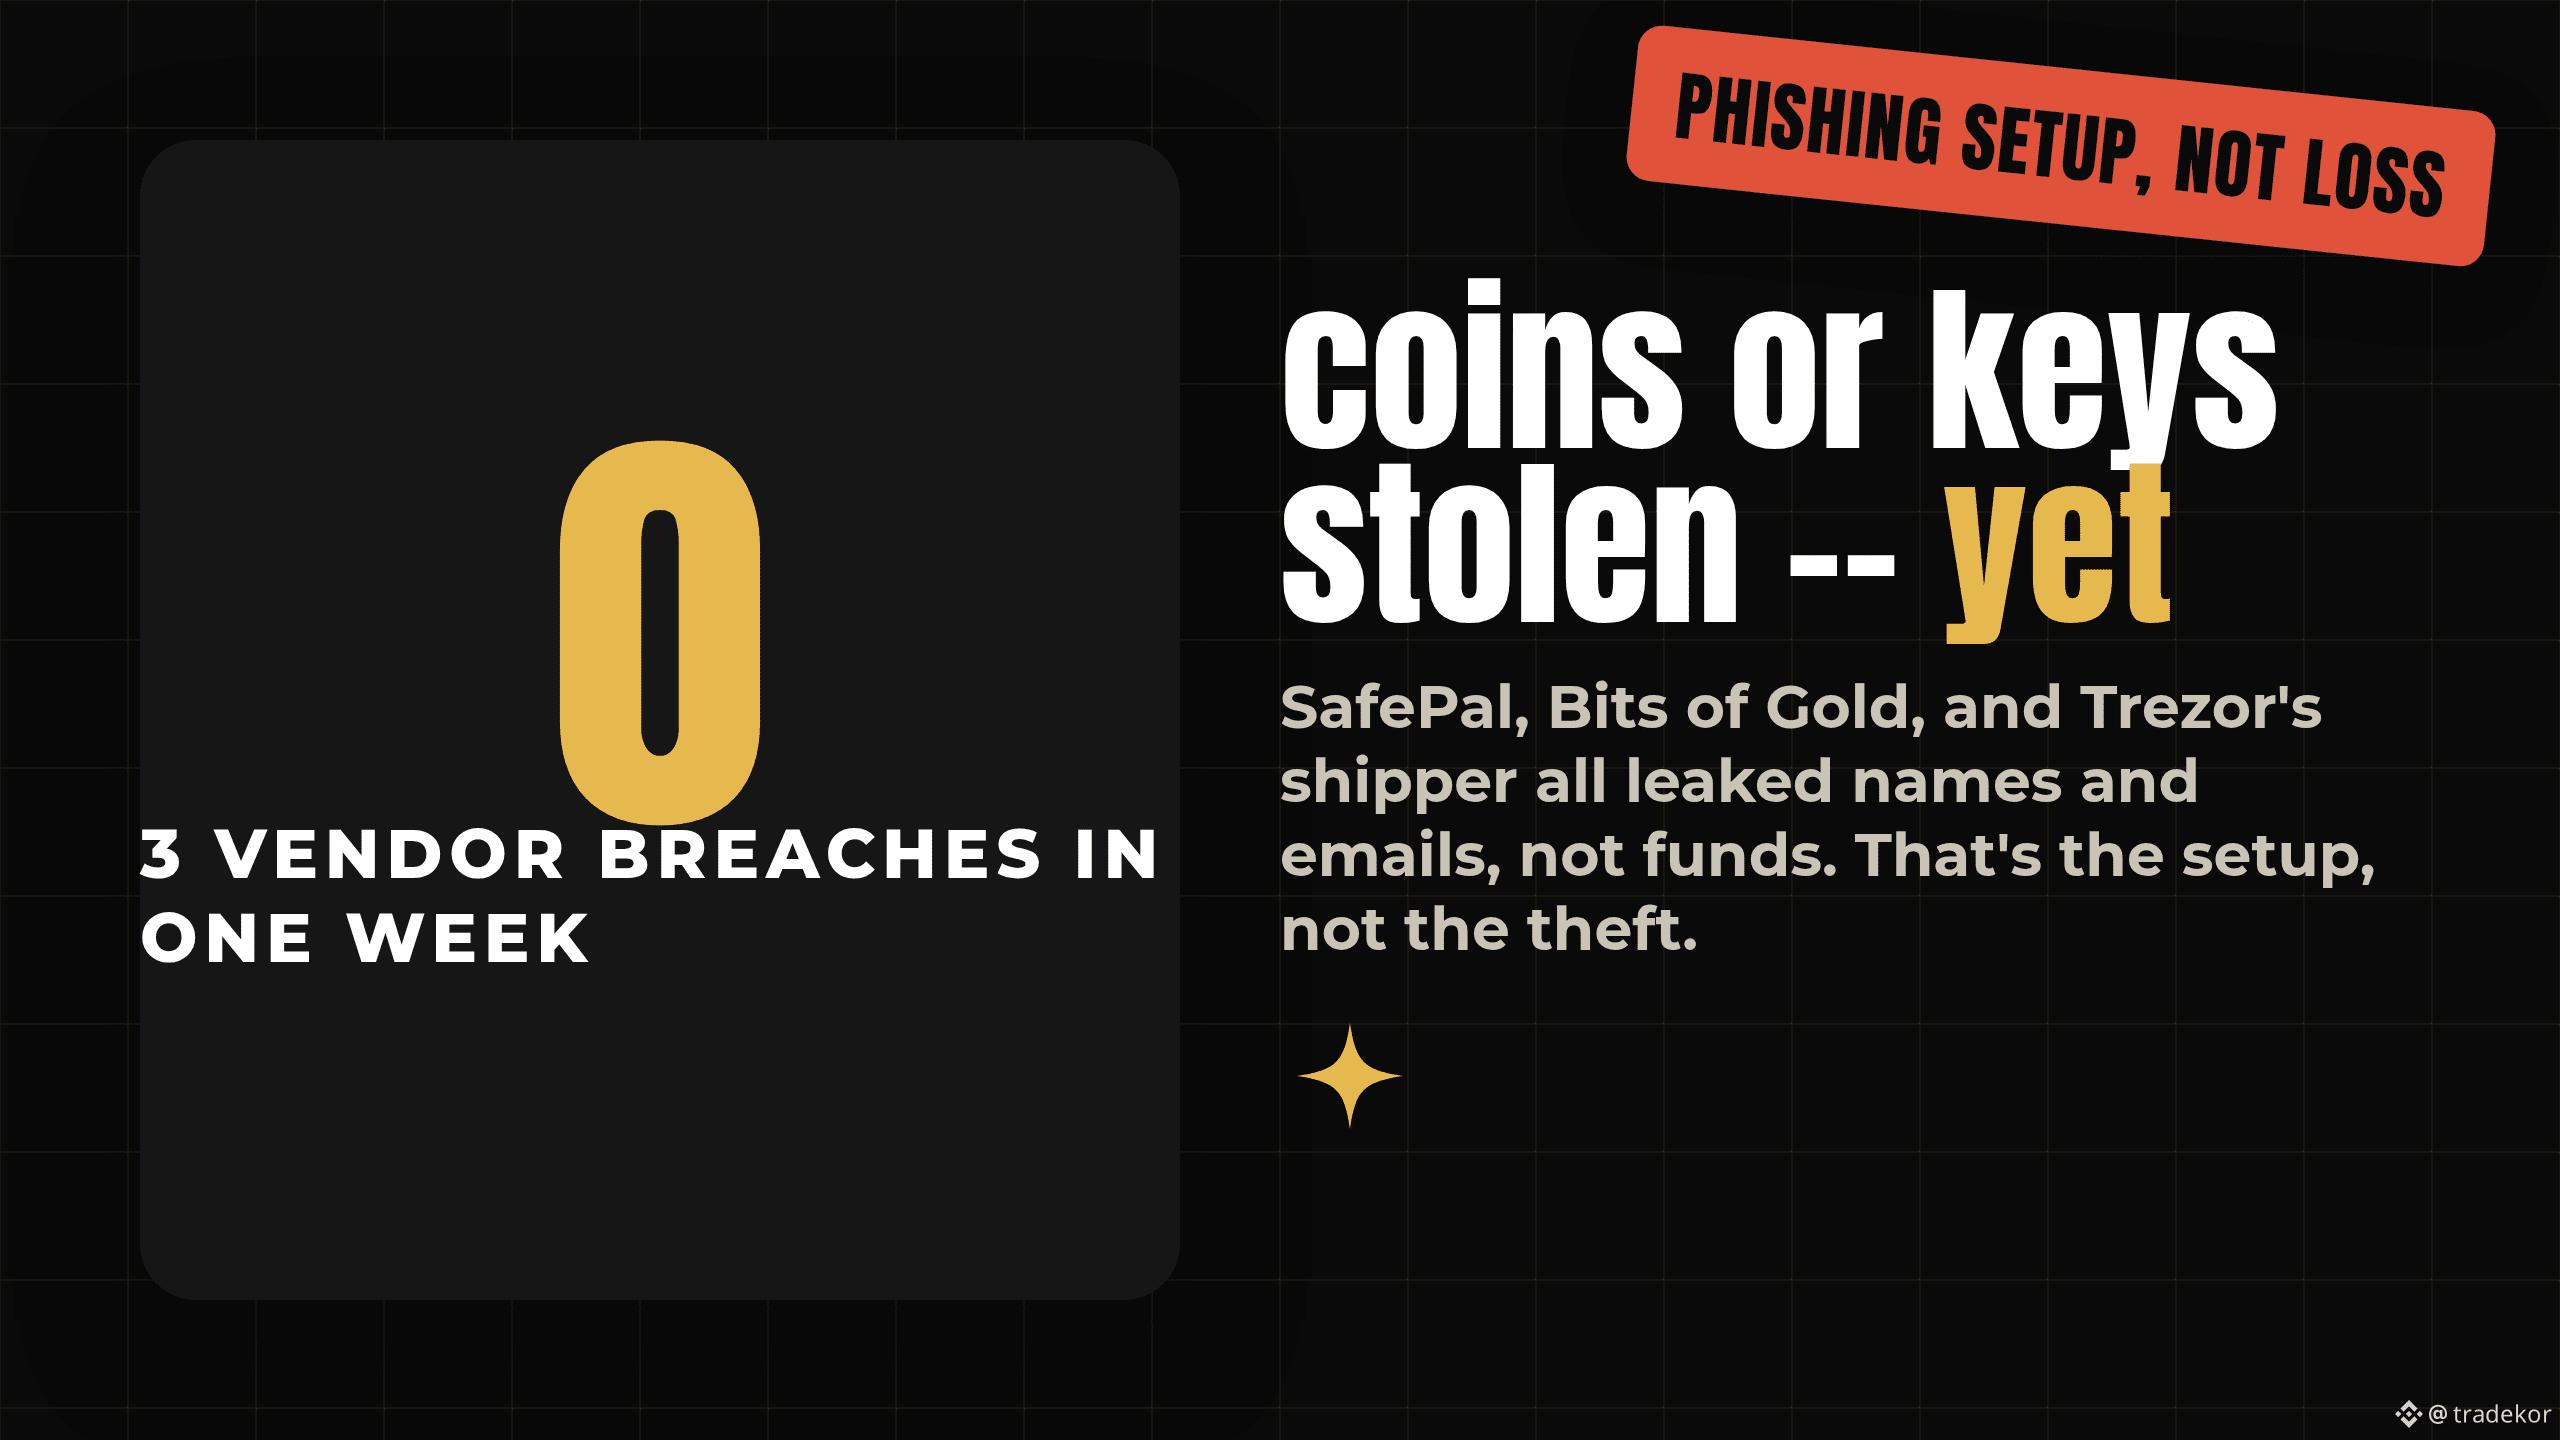
3 wallet and exchange vendors disclosed data breaches in one week — and not one of them lost a single coin or private key.
What happened: SafePal confirmed August 16 that a third-party order-tracking plug-in exposed names, emails, and purchase details for roughly 39,798 customers. The same day, Bits of Gold, Israel's largest regulated crypto broker, disclosed a separate vendor breach reportedly affecting around 200,000 customers. Both land three days after Trezor disclosed its fulfillment partner ShipMonk exposed roughly 14,000 customers.
Why it matters: no seed phrases, private keys, or funds were touched in any of the three. But leaked names, emails, and proof of which hardware wallet you own is exactly the targeting data used for convincing "fake support" phishing later — the same playbook that followed Ledger's 2020 breach for years. None of these three companies were breached directly; their vendors were.
The nuance: Bits of Gold hasn't officially confirmed the 200,000 figure yet — that number is reported, not company-stated. And this is a phishing-setup story, not a theft story, so don't read it as "funds at risk today." The real risk shows up weeks or months later, in a targeted email that already knows your name and your wallet brand.
If you've ever bought a hardware wallet, would you know if your shipping data leaked?
Not financial advice. DYOR.
$BTC #CryptoSecurity #DataBreach #SelfCustody #Phishing
67

$NOXA X ACCOUNT HACKED - DO NOT INTERACT WITH ANY LINKS 🚨
Onchain Lens just flagged the official Noxa X account as compromised. Community members got their wallets drained after clicking links posted by the account.
This is live — attackers are actively posting malicious links. Do not connect your wallet, sign anything, or interact with any links from that account until further notice.
Have you already interacted with any recent posts from the Noxa X account?
Not financial advice. Always manage your risk.
#NOXA #SecurityAlert #CryptoAlert #Phishing
⚡
85
·
--
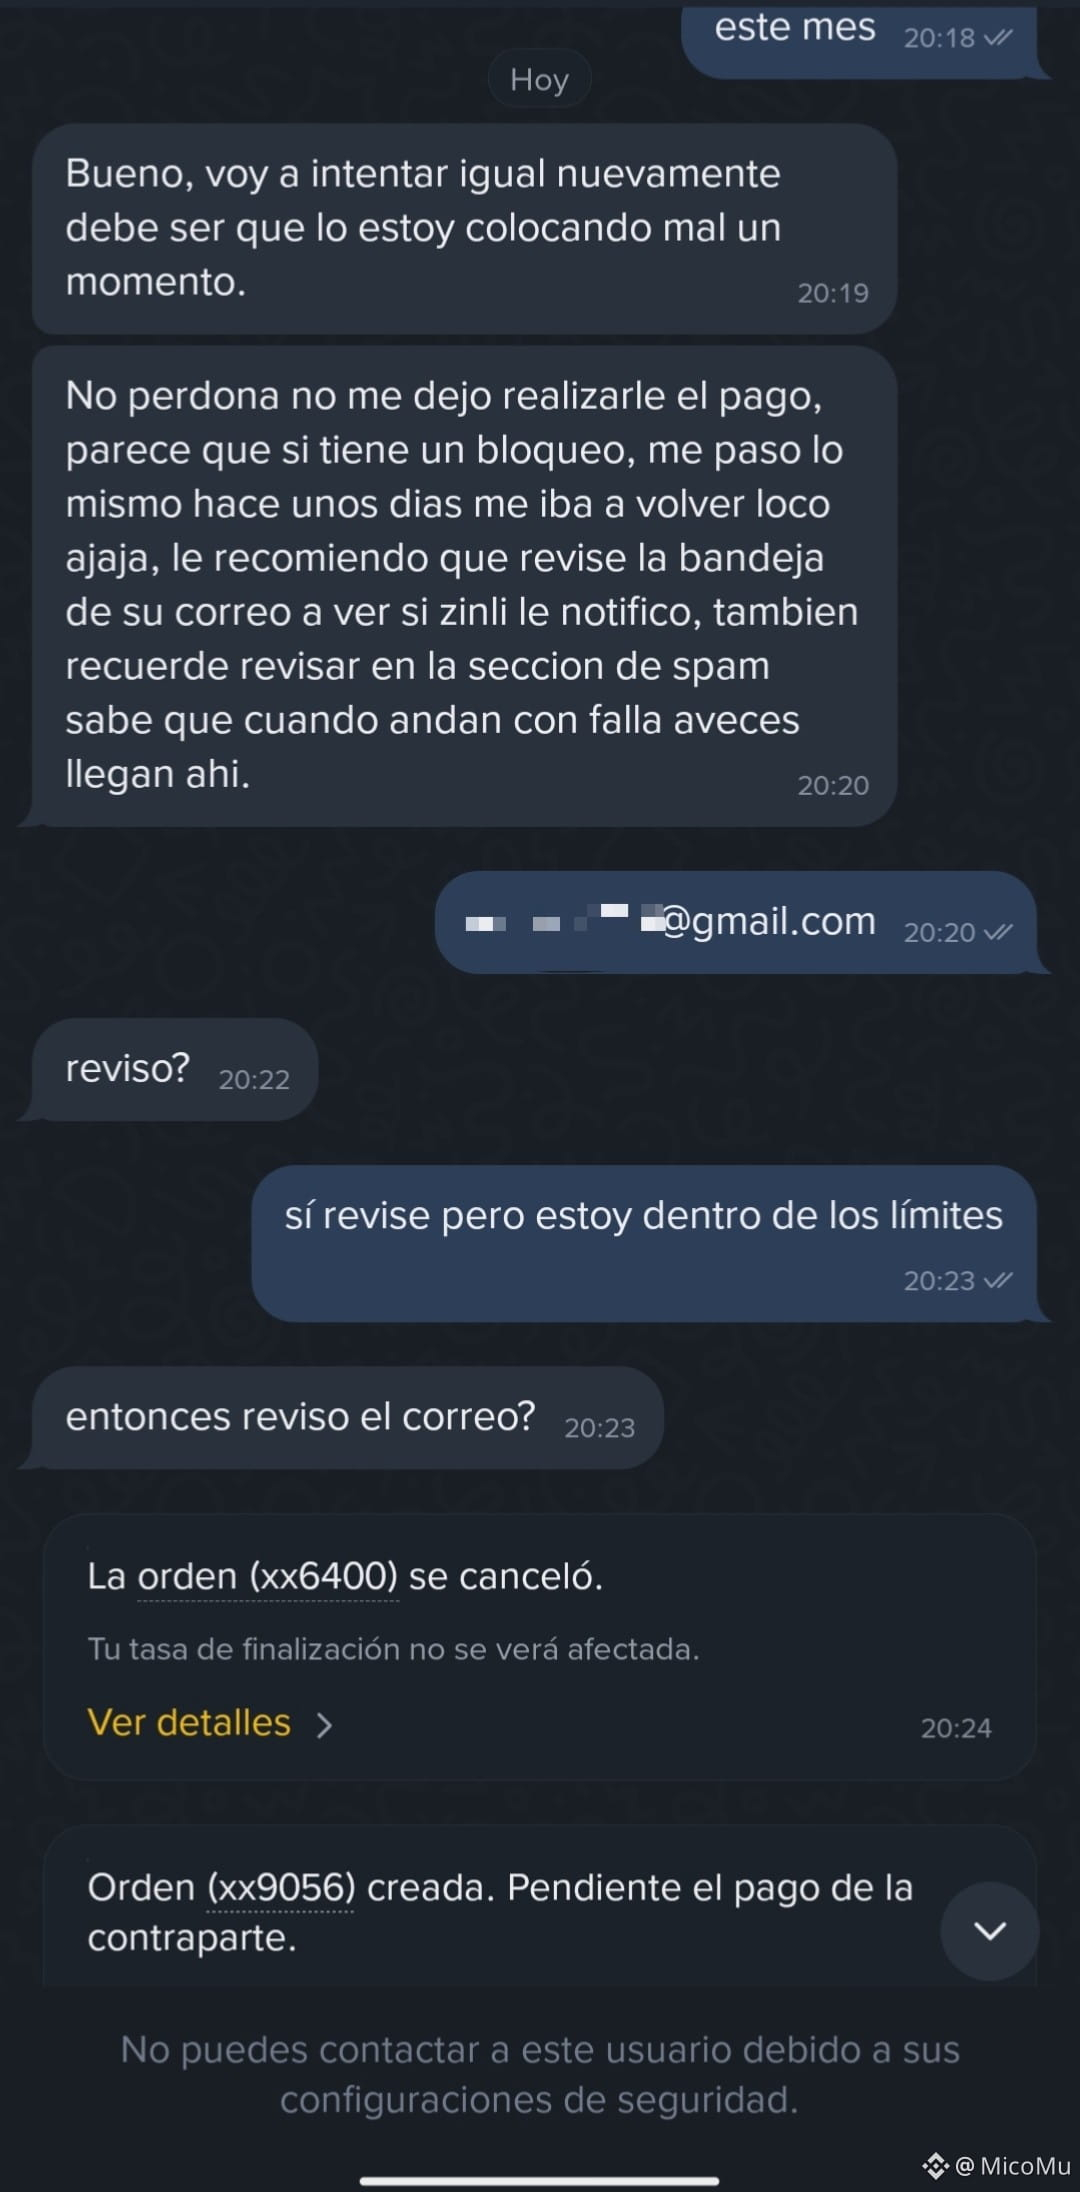
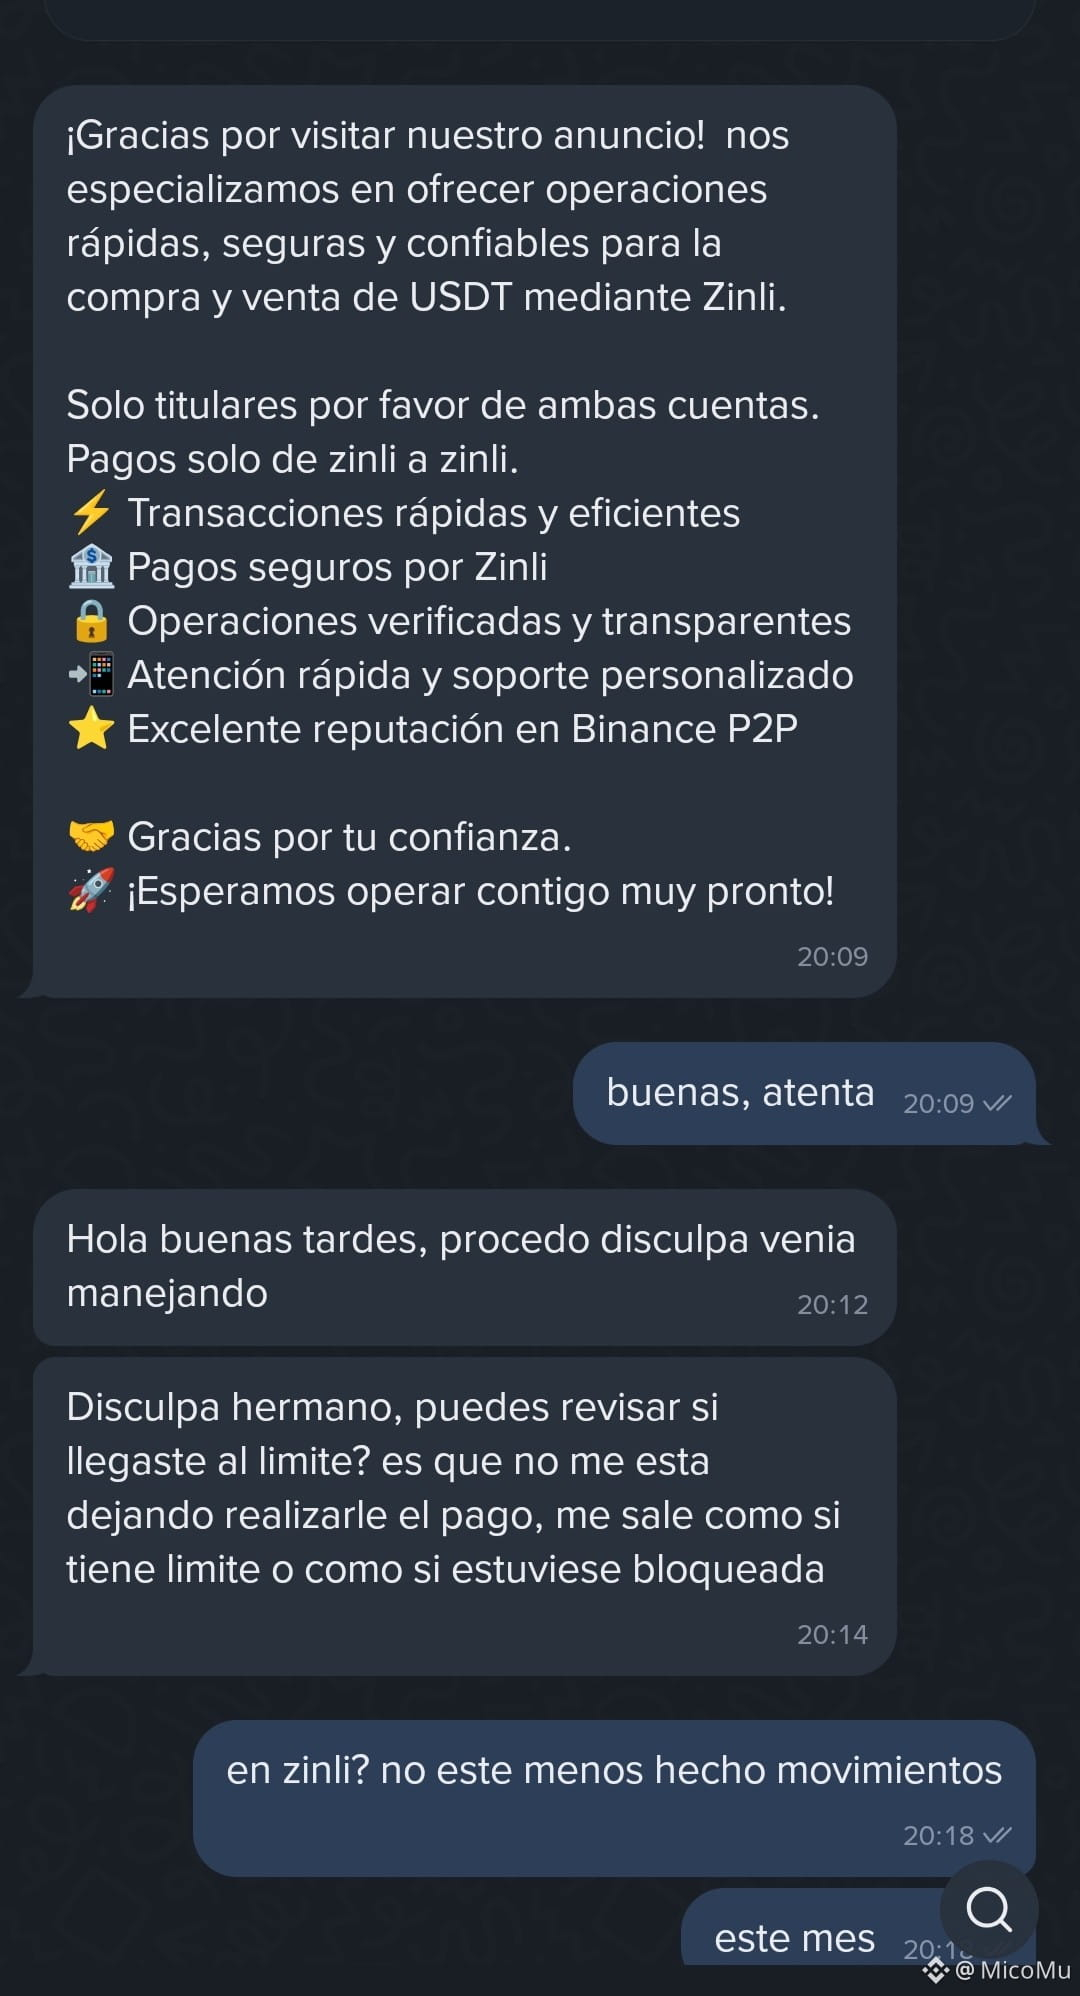
⚠️ P2P Alert! Watch out for the "account blocked" scam method and spam emails
#phishing #P2P #estafas
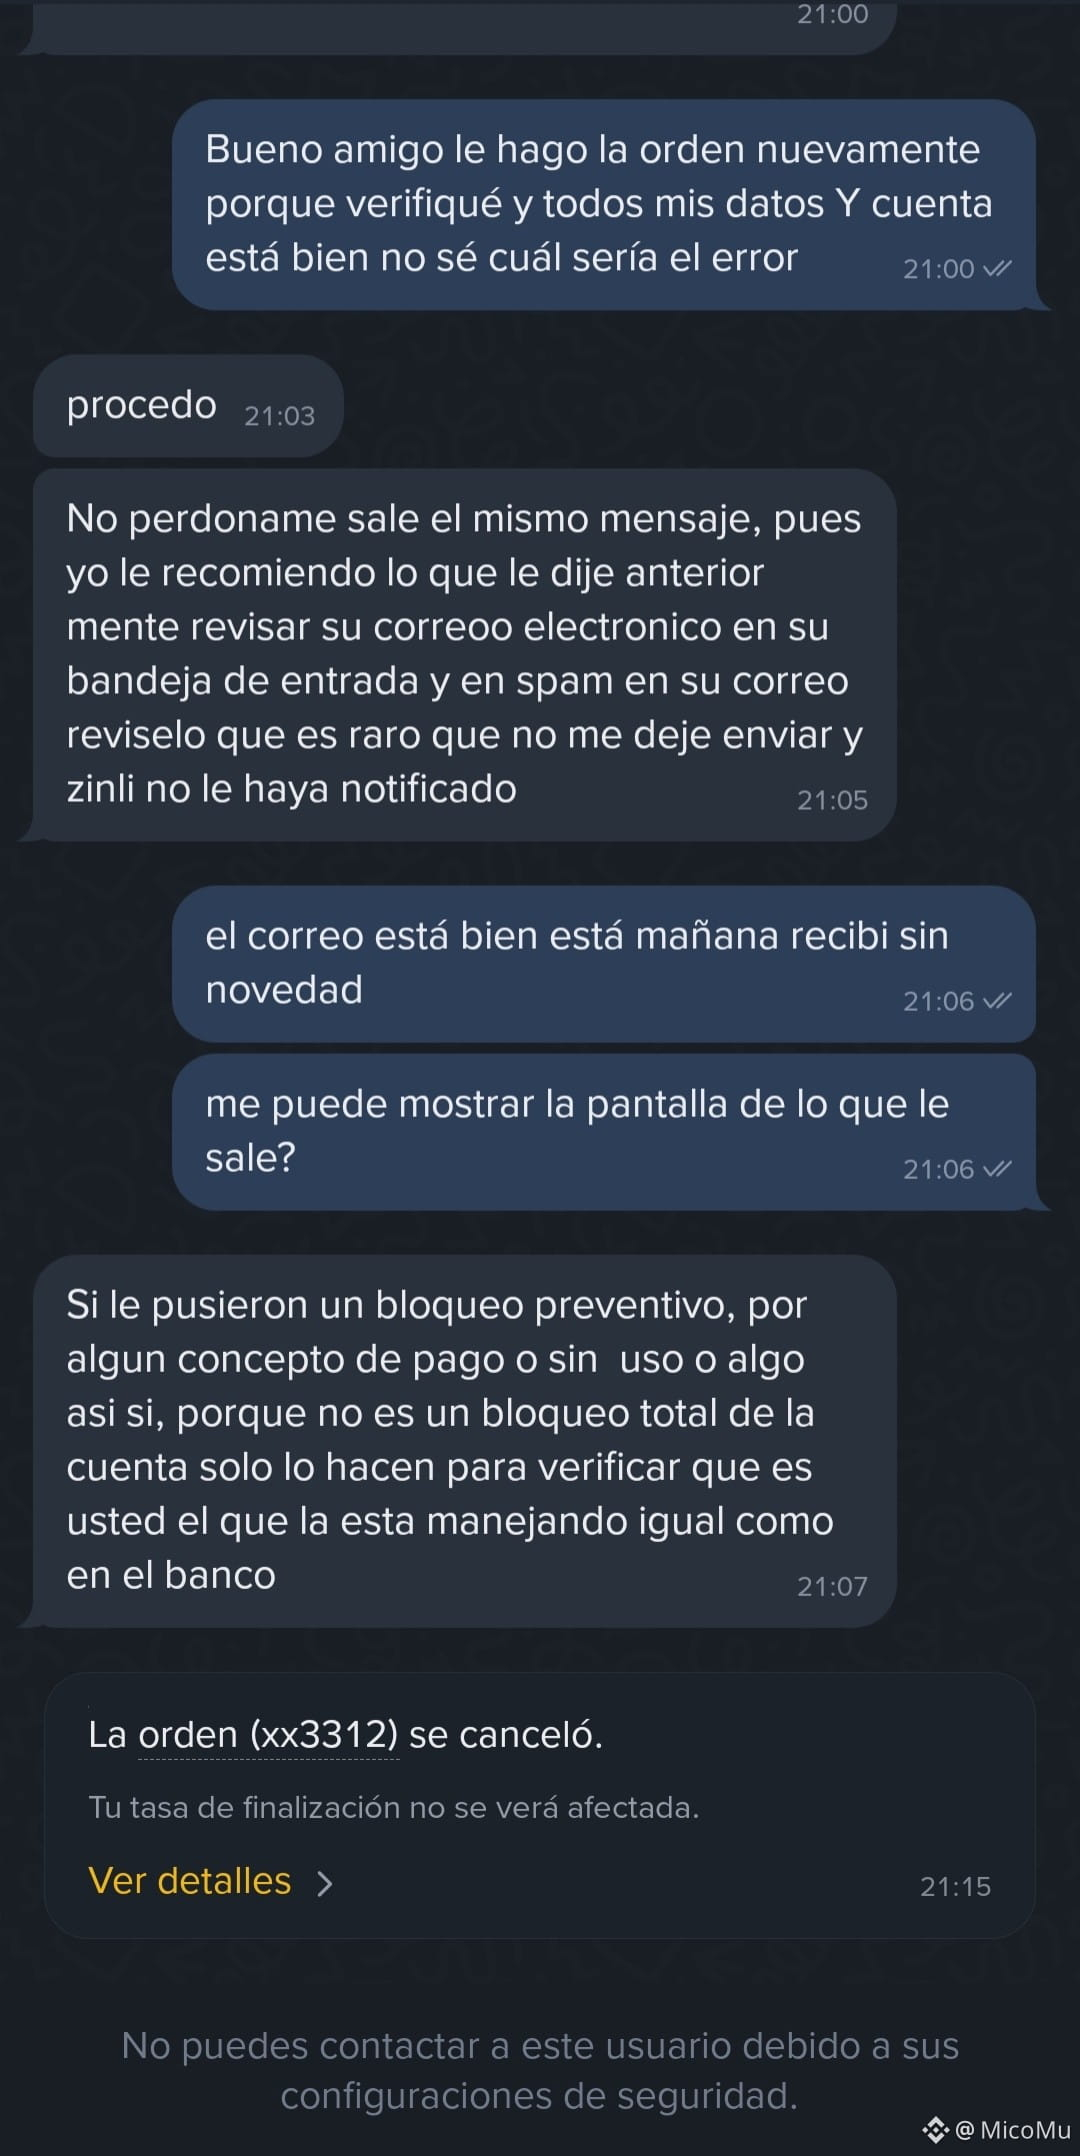
Community, I want to share a scam attempt that happened to me recently in P2P so you can stay very alert and not fall into the trap.
📍 How does this deception work?
- You open a sell order.
- The other party writes to you in chat saying they "can't transfer" because supposedly your receiving account (e.g., Zinli or a bank) is blocked.
- They insist that you check your Spam folder in your email.
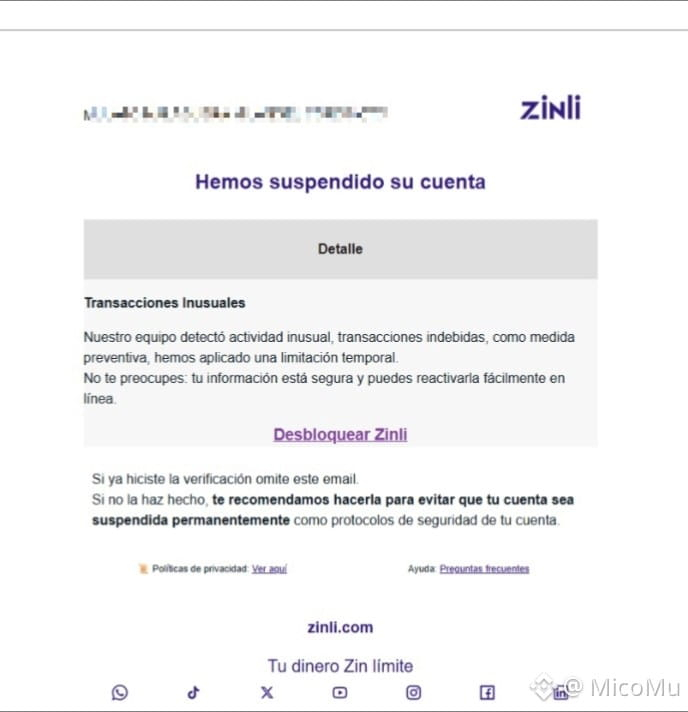
- In Spam, you find a fake email (posing as support for the payment method) that includes a link to "unlock" the account.
- That link takes you to a fake page that tries to steal your access data or Google/email verification codes.
💡 Always remember:
- Official platforms will never ask you to unlock an account via a link in Spam.
- Do not release crypto or click on suspicious links without verifying the sender's authenticity.
- Report the order immediately through Binance's official support channels.
Take care of our funds and always operate with caution! 🛡️
1
1
261
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#UniswapA16zSeekDeFiExemptionFromIllinoisCryptoTax
26,298 views
767 Discussing
2
#HKDollarStablecoinHKDAPToLaunchOnSolana
20,008 views
487 Discussing
3
#$1.5BInLeveragedCryptoBetsLiquidated
43,121 views
253 Discussing
4
#TrezorSaysCryptoBilisSoldWalletMayContainMaliciousComponents
3,359 views
72 Discussing
5
#KOSPIFalls3.53%BackBelow6000
63,639 views
1,097 Discussing
6
#AmazonSharesFallAbout7%InPremarketTrading
28,952 views
590 Discussing
7
#USMidtermElections
251,462 views
2,356 Discussing
8
#StrategySTRCReaches$99.95ForFirstTimeIn165Days
28,144 views
94 Discussing
9
#BinanceWillListPredictPREDICT
96,246 views
1,401 Discussing
10
#SwitzerlandFirstSpotBitcoinETFExpectedToTradeInNovember
3,203 views
111 Discussing