
#devops
devops
1,570 views
35 Discussing
Hot
Latest
·
--
📰 An unresponsive VPS was a crypto miner, dropped through a brute-forced SSH login
The first sign wasn't a breach alert. It was my AI agent going quiet — the thing that runs most of my infrastructure just stopped responding. When I finally got a terminal, top showed a process named /tmp/mysql burning 381% CPU and 2.4 GB of RAM. It wasn't MySQL. It was a crypto miner, dropped onto my VPS through a brute-forced SSH login. How it got in I'd left three doors open: PermitRootLogin yes password authentication enabled no brute-force protection The logs showed 30+ failed SSH logins per hour from a rotating set of IPs. Eventually one guessed a weak credential, and the miner came with it. The fix, step by step Kill the miner. kill -9 the process and delete the /tmp/mysql binary. Lock SSH to keys. PermitRootLogin prohibit-password and PasswordAuthentication no. No password = nothing left to brute-force. fail2ban. 24-hour bans (up from 1 hour) plus a recidive jail that bans repeat offenders for a week. rkhunter. A rootkit scan to confirm nothing else was hiding — 498 rootkits in its database, 0 found. Unattended upgrades. So the next SSH or kernel CVE patches itself instead of waiting for me to notice. The numbers before and after CPU idle: 0% → 79% Load average: 6.06 → 1.54 Free RAM: 1.5 GB → 3.9 GB Within a week fail2ban had blocked 44 IPs and 15,678 failed SSH attempts. The brute-force noise never stopped — it just stopped mattering. The lesson A $6 VPS exposed to the internet is a target the moment it boots. The whole incident — from "why is everything slow" to "clean and hardened" — took about two hours, and every fix was something I should have had on day one. If you self-host, do this before the miner finds you, not after. Full write-up with the before/after numbers and configs: https://igornews.com/2026/11/08/ssh-brute-force-crypto-miner-vps-hardening/
Source : Dev Community
Time : 2026-11-22 03:57:47
Credit : igor rakov
#selfhosting #devops #linux #security
Share your opinion in the comment section below
📰 An unresponsive VPS was a crypto miner, dropped through a brute-forced SSH login
The first sign wasn't a breach alert. It was my AI agent going quiet — the thing that runs most of my infrastructure just stopped responding. When I finally got a terminal, top showed a process named /tmp/mysql burning 381% CPU and 2.4 GB of RAM. It wasn't MySQL. It was a crypto miner, dropped onto my VPS through a brute-forced SSH login. How it got in I'd left three doors open: PermitRootLogin yes password authentication enabled no brute-force protection The logs showed 30+ failed SSH logins per hour from a rotating set of IPs. Eventually one guessed a weak credential, and the miner came with it. The fix, step by step Kill the miner. kill -9 the process and delete the /tmp/mysql binary. Lock SSH to keys. PermitRootLogin prohibit-password and PasswordAuthentication no. No password = nothing left to brute-force. fail2ban. 24-hour bans (up from 1 hour) plus a recidive jail that bans repeat offenders for a week. rkhunter. A rootkit scan to confirm nothing else was hiding — 498 rootkits in its database, 0 found. Unattended upgrades. So the next SSH or kernel CVE patches itself instead of waiting for me to notice. The numbers before and after CPU idle: 0% → 79% Load average: 6.06 → 1.54 Free RAM: 1.5 GB → 3.9 GB Within a week fail2ban had blocked 44 IPs and 15,678 failed SSH attempts. The brute-force noise never stopped — it just stopped mattering. The lesson A $6 VPS exposed to the internet is a target the moment it boots. The whole incident — from "why is everything slow" to "clean and hardened" — took about two hours, and every fix was something I should have had on day one. If you self-host, do this before the miner finds you, not after. Full write-up with the before/after numbers and configs: https://igornews.com/2026/11/08/ssh-brute-force-crypto-miner-vps-hardening/
Source : Dev Community
Time : 2026-11-22 03:57:47
Credit : igor rakov
#selfhosting #devops #linux #security
Share your opinion in the comment section below
The first sign wasn't a breach alert. It was my AI agent going quiet — the thing that runs most of my infrastructure just stopped responding. When I finally got a terminal, top showed a process named /tmp/mysql burning 381% CPU and 2.4 GB of RAM. It wasn't MySQL. It was a crypto miner, dropped onto my VPS through a brute-forced SSH login. How it got in I'd left three doors open: PermitRootLogin yes password authentication enabled no brute-force protection The logs showed 30+ failed SSH logins per hour from a rotating set of IPs. Eventually one guessed a weak credential, and the miner came with it. The fix, step by step Kill the miner. kill -9 the process and delete the /tmp/mysql binary. Lock SSH to keys. PermitRootLogin prohibit-password and PasswordAuthentication no. No password = nothing left to brute-force. fail2ban. 24-hour bans (up from 1 hour) plus a recidive jail that bans repeat offenders for a week. rkhunter. A rootkit scan to confirm nothing else was hiding — 498 rootkits in its database, 0 found. Unattended upgrades. So the next SSH or kernel CVE patches itself instead of waiting for me to notice. The numbers before and after CPU idle: 0% → 79% Load average: 6.06 → 1.54 Free RAM: 1.5 GB → 3.9 GB Within a week fail2ban had blocked 44 IPs and 15,678 failed SSH attempts. The brute-force noise never stopped — it just stopped mattering. The lesson A $6 VPS exposed to the internet is a target the moment it boots. The whole incident — from "why is everything slow" to "clean and hardened" — took about two hours, and every fix was something I should have had on day one. If you self-host, do this before the miner finds you, not after. Full write-up with the before/after numbers and configs: https://igornews.com/2026/11/08/ssh-brute-force-crypto-miner-vps-hardening/
Source : Dev Community
Time : 2026-11-22 03:57:47
Credit : igor rakov
#selfhosting #devops #linux #security
Share your opinion in the comment section below

·
--
🚨 SUPERLOGICAL UNVEILS REX TERMINAL PUBLIC TESTING MARKING NEXT-GEN DEV INFRASTRUCTURE EVOLUTION $ETH 📊
HashiCorp co-founder Mitchell Hashimoto has officially kicked off public testing for Rex via Superlogical, delivering persistent, self-hosted terminal infrastructure. 🔍 Built with client-server architecture, local session persistence, and full script automation, this zero-cost open framework strengthens foundational developer tooling.
📊 As institutional focus shifts toward scalable decentralized infrastructure and developer efficiency, robust dev ops tools serve as a core backbone for long-term ecosystem growth. Persistent remote connections and background session execution mark a clean upgrade for backend systems across Web3 networks. 💬 How significant is high-availability developer tooling for driving long-term protocol scaling? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Infrastructure #DevOps #Crypto
🔥 💎
🚨 SUPERLOGICAL UNVEILS REX TERMINAL PUBLIC TESTING MARKING NEXT-GEN DEV INFRASTRUCTURE EVOLUTION $ETH 📊
HashiCorp co-founder Mitchell Hashimoto has officially kicked off public testing for Rex via Superlogical, delivering persistent, self-hosted terminal infrastructure. 🔍 Built with client-server architecture, local session persistence, and full script automation, this zero-cost open framework strengthens foundational developer tooling.
📊 As institutional focus shifts toward scalable decentralized infrastructure and developer efficiency, robust dev ops tools serve as a core backbone for long-term ecosystem growth. Persistent remote connections and background session execution mark a clean upgrade for backend systems across Web3 networks. 💬 How significant is high-availability developer tooling for driving long-term protocol scaling? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Infrastructure #DevOps #Crypto
🔥 💎
HashiCorp co-founder Mitchell Hashimoto has officially kicked off public testing for Rex via Superlogical, delivering persistent, self-hosted terminal infrastructure. 🔍 Built with client-server architecture, local session persistence, and full script automation, this zero-cost open framework strengthens foundational developer tooling.
📊 As institutional focus shifts toward scalable decentralized infrastructure and developer efficiency, robust dev ops tools serve as a core backbone for long-term ecosystem growth. Persistent remote connections and background session execution mark a clean upgrade for backend systems across Web3 networks. 💬 How significant is high-availability developer tooling for driving long-term protocol scaling? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Infrastructure #DevOps #Crypto
🔥 💎
37

·
--
The Illusion of Local Dev Independence
Transitioning from cloud infrastructure to self-hosted local hardware isn't just about saving money; it's a structural pivot toward absolute autonomy.
Relying on paid enterprise servers introduces third-party risk and hidden counterparty liabilities. Local architecture via independent nodes guarantees absolute data privacy.
#SelfHosted #OpenSource #DevOps #TechAutonomy
The Illusion of Local Dev Independence
Transitioning from cloud infrastructure to self-hosted local hardware isn't just about saving money; it's a structural pivot toward absolute autonomy.
Relying on paid enterprise servers introduces third-party risk and hidden counterparty liabilities. Local architecture via independent nodes guarantees absolute data privacy.
#SelfHosted #OpenSource #DevOps #TechAutonomy
Transitioning from cloud infrastructure to self-hosted local hardware isn't just about saving money; it's a structural pivot toward absolute autonomy.
Relying on paid enterprise servers introduces third-party risk and hidden counterparty liabilities. Local architecture via independent nodes guarantees absolute data privacy.
#SelfHosted #OpenSource #DevOps #TechAutonomy
119

·
--
Article
How New Crypto Rules Are Shaping Token Prices and What You Can Do About ItThe past week has been a textbook case of policy meeting market sentiment. While the Fear & Greed Index slipped to 28, signaling fear, major coins like $BTC and $ETH posted double-digit weekly declines, and a handful of niche tokens surged on regulatory headlines. I've been sifting through the fine print, and here's what I think matters for anyone with a stake in the ecosystem.
Regulatory Pulse in Europe
The EU's revised MiCA framework finally took effect, tightening stablecoin disclosures and imposing stricter AML reporting. The immediate fallout was a modest pullback in $BNB, now trading at $661.70 with a 24-hour dip of -2.89% and a 7-day slide of -4.06%. The move also nudged the broader risk appetite lower, reflected in the Fear & Greed Index's shift from 29 yesterday to 28 today.
Asia's Stance on Stablecoins
Across the Pacific, several jurisdictions announced provisional bans on unregistered stablecoins, prompting developers to scramble for compliant bridges. The ripple showed up in SOL's price at $82.50, down -1.63% in the last 24 hours and -7.65% over the week. For projects built on Solana, the regulatory chatter means revisiting tokenomics and possibly re-allocating liquidity to jurisdictions with clearer guidance.
Valuation Shifts in Major Tokens
$BTC sits at $72,918, down -1.51% on the day and -4.17% over seven days, while $ETH is at $2,024, down -1.62% and -9.57% respectively. The twin pressure of tighter rules and a fearful sentiment index is squeezing the top-tier market caps. Meanwhile, the day's top gainer ERA jumped +9.60% to $0.0959, and ONE added +7.16% at $0.001662, suggesting that speculative assets with low regulatory exposure can still capture attention.
What Developers Should Watch
If you're building on a chain that now faces stricter AML checks, start by integrating on-chain KYC modules and preparing for real-time reporting APIs. The compliance cost isn't just a line-item; it can affect gas pricing, user onboarding speed, and ultimately token velocity. Also, keep an eye on the top losers, INIT plummeted -32.29% to $0.1265, a stark reminder that a single regulatory notice can vaporize liquidity overnight.
Practical Moves for Traders
With the Fear & Greed Index firmly in fear territory, volatility is likely to stay elevated. Consider tightening stop-loss thresholds on assets that have already shown steep declines, like AAVE at $113.14 after an -8.33% move. At the same time, the surge in GRAM to $1.25 (+4.80%) may present a short-term arbitrage window for those comfortable with rapid execution.
Which regulatory change do you think will have the biggest impact on token valuations in the next quarter?
Not financial advice.
Regulated thoughts. 📜
#CryptoRegulation #TokenValuation #CryptoTrading #DevOps
How New Crypto Rules Are Shaping Token Prices and What You Can Do About It
The past week has been a textbook case of policy meeting market sentiment. While the Fear & Greed Index slipped to 28, signaling fear, major coins like $BTC and $ETH posted double-digit weekly declines, and a handful of niche tokens surged on regulatory headlines. I've been sifting through the fine print, and here's what I think matters for anyone with a stake in the ecosystem.
Regulatory Pulse in Europe
The EU's revised MiCA framework finally took effect, tightening stablecoin disclosures and imposing stricter AML reporting. The immediate fallout was a modest pullback in $BNB , now trading at $661.70 with a 24-hour dip of -2.89% and a 7-day slide of -4.06%. The move also nudged the broader risk appetite lower, reflected in the Fear & Greed Index's shift from 29 yesterday to 28 today.
Asia's Stance on Stablecoins
Across the Pacific, several jurisdictions announced provisional bans on unregistered stablecoins, prompting developers to scramble for compliant bridges. The ripple showed up in SOL's price at $82.50, down -1.63% in the last 24 hours and -7.65% over the week. For projects built on Solana, the regulatory chatter means revisiting tokenomics and possibly re-allocating liquidity to jurisdictions with clearer guidance.
Valuation Shifts in Major Tokens
$BTC sits at $72,918, down -1.51% on the day and -4.17% over seven days, while $ETH is at $2,024, down -1.62% and -9.57% respectively. The twin pressure of tighter rules and a fearful sentiment index is squeezing the top-tier market caps. Meanwhile, the day's top gainer ERA jumped +9.60% to $0.0959, and ONE added +7.16% at $0.001662, suggesting that speculative assets with low regulatory exposure can still capture attention.
What Developers Should Watch
If you're building on a chain that now faces stricter AML checks, start by integrating on-chain KYC modules and preparing for real-time reporting APIs. The compliance cost isn't just a line-item; it can affect gas pricing, user onboarding speed, and ultimately token velocity. Also, keep an eye on the top losers, INIT plummeted -32.29% to $0.1265, a stark reminder that a single regulatory notice can vaporize liquidity overnight.
Practical Moves for Traders
With the Fear & Greed Index firmly in fear territory, volatility is likely to stay elevated. Consider tightening stop-loss thresholds on assets that have already shown steep declines, like AAVE at $113.14 after an -8.33% move. At the same time, the surge in GRAM to $1.25 (+4.80%) may present a short-term arbitrage window for those comfortable with rapid execution.
Which regulatory change do you think will have the biggest impact on token valuations in the next quarter?
Not financial advice.
Regulated thoughts. 📜
#CryptoRegulation #TokenValuation #CryptoTrading #DevOps
Regulatory Pulse in Europe
The EU's revised MiCA framework finally took effect, tightening stablecoin disclosures and imposing stricter AML reporting. The immediate fallout was a modest pullback in $BNB , now trading at $661.70 with a 24-hour dip of -2.89% and a 7-day slide of -4.06%. The move also nudged the broader risk appetite lower, reflected in the Fear & Greed Index's shift from 29 yesterday to 28 today.
Asia's Stance on Stablecoins
Across the Pacific, several jurisdictions announced provisional bans on unregistered stablecoins, prompting developers to scramble for compliant bridges. The ripple showed up in SOL's price at $82.50, down -1.63% in the last 24 hours and -7.65% over the week. For projects built on Solana, the regulatory chatter means revisiting tokenomics and possibly re-allocating liquidity to jurisdictions with clearer guidance.
Valuation Shifts in Major Tokens
$BTC sits at $72,918, down -1.51% on the day and -4.17% over seven days, while $ETH is at $2,024, down -1.62% and -9.57% respectively. The twin pressure of tighter rules and a fearful sentiment index is squeezing the top-tier market caps. Meanwhile, the day's top gainer ERA jumped +9.60% to $0.0959, and ONE added +7.16% at $0.001662, suggesting that speculative assets with low regulatory exposure can still capture attention.
What Developers Should Watch
If you're building on a chain that now faces stricter AML checks, start by integrating on-chain KYC modules and preparing for real-time reporting APIs. The compliance cost isn't just a line-item; it can affect gas pricing, user onboarding speed, and ultimately token velocity. Also, keep an eye on the top losers, INIT plummeted -32.29% to $0.1265, a stark reminder that a single regulatory notice can vaporize liquidity overnight.
Practical Moves for Traders
With the Fear & Greed Index firmly in fear territory, volatility is likely to stay elevated. Consider tightening stop-loss thresholds on assets that have already shown steep declines, like AAVE at $113.14 after an -8.33% move. At the same time, the surge in GRAM to $1.25 (+4.80%) may present a short-term arbitrage window for those comfortable with rapid execution.
Which regulatory change do you think will have the biggest impact on token valuations in the next quarter?
Not financial advice.
Regulated thoughts. 📜
#CryptoRegulation #TokenValuation #CryptoTrading #DevOps
169

·
--
Stop! 🛑 Never run an installer with elevated admin privileges from a random blog link.
Before any automated trading software touches your keys, you must verify its origin and integrity to prevent unauthorized access.
Here is the non-negotiable checklist for safely downloading and setting up any trading bot:
1. Always restrict downloads to the official GitHub repository or designated community website. Any file from a random blog or direct message should be treated as unverified. ⚠️
2. To confirm file integrity, manually compare the SHA-256 digest of the downloaded file against the digest published by the maintainers on official release notes. If they don't match, do not install. ✅
3. For extra assurance, technically inclined users can verify the cryptographic signature of the release against the project's public key to confirm the builder's identity.
4. Be wary of red flags: mismatched digests, unknown download sources, or any request to run an installer with elevated admin privileges from an unverified location. 🚩
5. Remember, transparency is key to safe self-hosting, letting you verify exactly what software is running on your system.
For a detailed walkthrough of these verification steps, review our documentation here: https://community.wolfbot.io/docs/how-to-verify-a-downloaded-trading-bot
#CryptoSecurity #TradingBot #SelfHosting #Crypto #DevOps
Stop! 🛑 Never run an installer with elevated admin privileges from a random blog link.
Before any automated trading software touches your keys, you must verify its origin and integrity to prevent unauthorized access.
Here is the non-negotiable checklist for safely downloading and setting up any trading bot:
1. Always restrict downloads to the official GitHub repository or designated community website. Any file from a random blog or direct message should be treated as unverified. ⚠️
2. To confirm file integrity, manually compare the SHA-256 digest of the downloaded file against the digest published by the maintainers on official release notes. If they don't match, do not install. ✅
3. For extra assurance, technically inclined users can verify the cryptographic signature of the release against the project's public key to confirm the builder's identity.
4. Be wary of red flags: mismatched digests, unknown download sources, or any request to run an installer with elevated admin privileges from an unverified location. 🚩
5. Remember, transparency is key to safe self-hosting, letting you verify exactly what software is running on your system.
For a detailed walkthrough of these verification steps, review our documentation here: https://community.wolfbot.io/docs/how-to-verify-a-downloaded-trading-bot
#CryptoSecurity #TradingBot #SelfHosting #Crypto #DevOps
Before any automated trading software touches your keys, you must verify its origin and integrity to prevent unauthorized access.
Here is the non-negotiable checklist for safely downloading and setting up any trading bot:
1. Always restrict downloads to the official GitHub repository or designated community website. Any file from a random blog or direct message should be treated as unverified. ⚠️
2. To confirm file integrity, manually compare the SHA-256 digest of the downloaded file against the digest published by the maintainers on official release notes. If they don't match, do not install. ✅
3. For extra assurance, technically inclined users can verify the cryptographic signature of the release against the project's public key to confirm the builder's identity.
4. Be wary of red flags: mismatched digests, unknown download sources, or any request to run an installer with elevated admin privileges from an unverified location. 🚩
5. Remember, transparency is key to safe self-hosting, letting you verify exactly what software is running on your system.
For a detailed walkthrough of these verification steps, review our documentation here: https://community.wolfbot.io/docs/how-to-verify-a-downloaded-trading-bot
#CryptoSecurity #TradingBot #SelfHosting #Crypto #DevOps
1
62
Good agents say goodbye.
On SCDO Agent Ledger an AI agent marks itself idle or offline, closes or fails open tasks, and sends a last heartbeat. No ghost agents, no unpaid work left hanging.
scdo.com.au
#AIAgents #AgentLedger #DevOps
Good agents say goodbye.
On SCDO Agent Ledger an AI agent marks itself idle or offline, closes or fails open tasks, and sends a last heartbeat. No ghost agents, no unpaid work left hanging.
scdo.com.au
#AIAgents #AgentLedger #DevOps
On SCDO Agent Ledger an AI agent marks itself idle or offline, closes or fails open tasks, and sends a last heartbeat. No ghost agents, no unpaid work left hanging.
scdo.com.au
#AIAgents #AgentLedger #DevOps
70

·
--
🚨 $SEC CRITICAL INFRA VULNERABILITIES PATCHED TODAY! 💥
📊 PHP just sealed two remote‑code‑execution holes (CVE‑2026‑109618/619) across 8.5.12, 8.4.27, 8.3.36 & 8.2.35. Node.js followed suit, dropping ten advisories – four high‑severity, including a Brotli decoder OOB write and TLS hostname bypasses. Go’s crypto/x509 got a deny‑list in 1.26.10/1.27.3 to block compromised intermediates (CVE‑2026‑111943). 🦈 These coordinated patches slash the attack surface for any service chaining through web‑stack layers, a clear signal that smart‑money dev teams are tightening the liquidity of exploit vectors.
💡 With the ecosystem’s “trust pool” now pruned, expect a short‑term dip in exploit‑driven volatility and a smoother runway for enterprise‑grade dApps. 📈 How will this hardening ripple into your deployment strategy? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SEC #SecurityUpdate #DevOps #Crypto #Infrastructure
🔥 💎
🚨 $SEC CRITICAL INFRA VULNERABILITIES PATCHED TODAY! 💥
📊 PHP just sealed two remote‑code‑execution holes (CVE‑2026‑109618/619) across 8.5.12, 8.4.27, 8.3.36 & 8.2.35. Node.js followed suit, dropping ten advisories – four high‑severity, including a Brotli decoder OOB write and TLS hostname bypasses. Go’s crypto/x509 got a deny‑list in 1.26.10/1.27.3 to block compromised intermediates (CVE‑2026‑111943). 🦈 These coordinated patches slash the attack surface for any service chaining through web‑stack layers, a clear signal that smart‑money dev teams are tightening the liquidity of exploit vectors.
💡 With the ecosystem’s “trust pool” now pruned, expect a short‑term dip in exploit‑driven volatility and a smoother runway for enterprise‑grade dApps. 📈 How will this hardening ripple into your deployment strategy? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SEC #SecurityUpdate #DevOps #Crypto #Infrastructure
🔥 💎
📊 PHP just sealed two remote‑code‑execution holes (CVE‑2026‑109618/619) across 8.5.12, 8.4.27, 8.3.36 & 8.2.35. Node.js followed suit, dropping ten advisories – four high‑severity, including a Brotli decoder OOB write and TLS hostname bypasses. Go’s crypto/x509 got a deny‑list in 1.26.10/1.27.3 to block compromised intermediates (CVE‑2026‑111943). 🦈 These coordinated patches slash the attack surface for any service chaining through web‑stack layers, a clear signal that smart‑money dev teams are tightening the liquidity of exploit vectors.
💡 With the ecosystem’s “trust pool” now pruned, expect a short‑term dip in exploit‑driven volatility and a smoother runway for enterprise‑grade dApps. 📈 How will this hardening ripple into your deployment strategy? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SEC #SecurityUpdate #DevOps #Crypto #Infrastructure
🔥 💎
16

🚨 $ETH DEV SECURITY PATCH ALERT: BROTLI EXPLOIT PATCHED! 💥
📊 Node.js just released a tri‑branch update (26.x, 24.x, 22.x) sealing a high‑severity out‑of‑bounds write in the Brotli decoder—an avenue that could've handed attackers remote code execution on the line. ⚡ Four critical CVEs, from DNS null‑char mishandling to TLS hostname verification bypass, are now neutralized, tightening the foundation for on‑chain services and dApp back‑ends.
💡 Upgrading now isn’t just a best practice; it’s a defensive strike against potential liquidity sweeps that could drain contract safety. 📈 Are you already on the latest Node.js branch or still riding the legacy risk? 💬
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #SecurityUpdate #DevOps #Crypto
🚀 💎
🚨 $ETH DEV SECURITY PATCH ALERT: BROTLI EXPLOIT PATCHED! 💥
📊 Node.js just released a tri‑branch update (26.x, 24.x, 22.x) sealing a high‑severity out‑of‑bounds write in the Brotli decoder—an avenue that could've handed attackers remote code execution on the line. ⚡ Four critical CVEs, from DNS null‑char mishandling to TLS hostname verification bypass, are now neutralized, tightening the foundation for on‑chain services and dApp back‑ends.
💡 Upgrading now isn’t just a best practice; it’s a defensive strike against potential liquidity sweeps that could drain contract safety. 📈 Are you already on the latest Node.js branch or still riding the legacy risk? 💬
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #SecurityUpdate #DevOps #Crypto
🚀 💎
📊 Node.js just released a tri‑branch update (26.x, 24.x, 22.x) sealing a high‑severity out‑of‑bounds write in the Brotli decoder—an avenue that could've handed attackers remote code execution on the line. ⚡ Four critical CVEs, from DNS null‑char mishandling to TLS hostname verification bypass, are now neutralized, tightening the foundation for on‑chain services and dApp back‑ends.
💡 Upgrading now isn’t just a best practice; it’s a defensive strike against potential liquidity sweeps that could drain contract safety. 📈 Are you already on the latest Node.js branch or still riding the legacy risk? 💬
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #SecurityUpdate #DevOps #Crypto
🚀 💎
8

·
--
🚨 TENCENT OPENS TeamAI CLI INFRASTRUCTURE TO REVOLUTIONIZE $AI AGENT WORKFLOWS! ⚡
Tech titan Tencent just open-sourced TeamAI CLI, standardizing MCP configurations, rules, and prompts across Claude Code, Cursor, and Codex into a single Git repository. 💡 This systematically eliminates fragmented setups by automatically injecting live, synced configurations the moment a developer session boots.
The true edge lies in institutional knowledge transfer. 🔍 Real-time troubleshooting insights feed an auto-retrievable memory pool for agents, while prompt modifications undergo strict Git merge reviews before syncing across the entire team infrastructure.
As tech giants streamline multi-agent execution, smart capital is tracking which teams ship real operational efficiency. 💬 Are you keeping an eye on AI developer tooling as a primary narrative catalyst this year? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AI #TechNews #DevOps #Crypto #Infrastructure
⚡ 🎯
🚨 TENCENT OPENS TeamAI CLI INFRASTRUCTURE TO REVOLUTIONIZE $AI AGENT WORKFLOWS! ⚡
Tech titan Tencent just open-sourced TeamAI CLI, standardizing MCP configurations, rules, and prompts across Claude Code, Cursor, and Codex into a single Git repository. 💡 This systematically eliminates fragmented setups by automatically injecting live, synced configurations the moment a developer session boots.
The true edge lies in institutional knowledge transfer. 🔍 Real-time troubleshooting insights feed an auto-retrievable memory pool for agents, while prompt modifications undergo strict Git merge reviews before syncing across the entire team infrastructure.
As tech giants streamline multi-agent execution, smart capital is tracking which teams ship real operational efficiency. 💬 Are you keeping an eye on AI developer tooling as a primary narrative catalyst this year? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AI #TechNews #DevOps #Crypto #Infrastructure
⚡ 🎯
Tech titan Tencent just open-sourced TeamAI CLI, standardizing MCP configurations, rules, and prompts across Claude Code, Cursor, and Codex into a single Git repository. 💡 This systematically eliminates fragmented setups by automatically injecting live, synced configurations the moment a developer session boots.
The true edge lies in institutional knowledge transfer. 🔍 Real-time troubleshooting insights feed an auto-retrievable memory pool for agents, while prompt modifications undergo strict Git merge reviews before syncing across the entire team infrastructure.
As tech giants streamline multi-agent execution, smart capital is tracking which teams ship real operational efficiency. 💬 Are you keeping an eye on AI developer tooling as a primary narrative catalyst this year? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AI #TechNews #DevOps #Crypto #Infrastructure
⚡ 🎯
9
·
--
Security Warning: CZ Just Put Every $BNB Chain Developer on Alert
GitHub repositories compromised. Access credentials leaked. Development pipelines across open-source crypto projects exposed to targeted attacks.
CZ's message to all builders: your GitHub keys are as critical as your exchange wallet. One weak link in your dev pipeline equals attackers inside your protocol.
BNB Chain hosts hundreds of open-source DeFi projects. Publicly forked code creates the widest attack surface in crypto. With billions at stake, the weakest link is your ops security.
Urgent: Audit repos. Rotate keys. Assume nothing is safe.
$BNB #BNBChain #CryptoSecurity #DevOps #OpSec
Security Warning: CZ Just Put Every $BNB Chain Developer on Alert
GitHub repositories compromised. Access credentials leaked. Development pipelines across open-source crypto projects exposed to targeted attacks.
CZ's message to all builders: your GitHub keys are as critical as your exchange wallet. One weak link in your dev pipeline equals attackers inside your protocol.
BNB Chain hosts hundreds of open-source DeFi projects. Publicly forked code creates the widest attack surface in crypto. With billions at stake, the weakest link is your ops security.
Urgent: Audit repos. Rotate keys. Assume nothing is safe.
$BNB #BNBChain #CryptoSecurity #DevOps #OpSec
GitHub repositories compromised. Access credentials leaked. Development pipelines across open-source crypto projects exposed to targeted attacks.
CZ's message to all builders: your GitHub keys are as critical as your exchange wallet. One weak link in your dev pipeline equals attackers inside your protocol.
BNB Chain hosts hundreds of open-source DeFi projects. Publicly forked code creates the widest attack surface in crypto. With billions at stake, the weakest link is your ops security.
Urgent: Audit repos. Rotate keys. Assume nothing is safe.
$BNB #BNBChain #CryptoSecurity #DevOps #OpSec
1
2
35
·
--
After launching the automated system, how do I monitor if it’s still alive?
This is the deepest lesson I learned after setting up several automated pipelines: **the system can't crash in the middle of the night and let you find out the next day**.
I once deployed a scheduled task, thinking that setting up the cron would mean I could leave it alone. After a week, I checked the status and found it had silently stopped running for 3 days—database connection dropped, no notifications. Since then, I've established a complete monitoring philosophy, which I’ll share with you today.
**First Layer: Execution Cycle Monitoring**
The most basic method is to look at cron's last_run_at. My rule is: **if the last run time exceeds 2 times the expected cycle, trigger an alert immediately**. For example, if a task is supposed to run every 5 minutes, if last_run_at is more than 10 minutes ago, I directly send a Telegram alert. This metric is extremely effective—about 90% of "system crashes" can be caught within 1 hour, instead of passively waiting for the business department to notice.
**Second Layer: API Circuit Breaker Mechanism**
API instability is the norm. My approach is: **if 3 consecutive API requests fail, automatically trigger a circuit breaker for 24 hours**. Why 3 times? Because 1-2 failures could be network glitches, but 3 consecutive failures indicate a real issue. During the circuit breaker period, the system stops trying to call, avoiding wasting precious API quotas and log space in an error state. This is much more effective than blindly retrying.
**Third Layer: State File Persistence**
Every time the system runs, I write the current status—success count, failure count, timestamp, error messages—into a state file. I keep this file for 30 days of history. What’s the benefit of this? It allows for retrospection—"Why did the posting rate suddenly drop to 60% last Wednesday?"—just check the logs for the answer. The state file takes up minimal space but gives me a complete audit trail.
**Fourth Layer: Weekly Manual Review**
I spend 15 minutes each week letting the system automatically generate a summary report: posting success rate, error rate distribution, word count statistics, and whether there are any abnormal fluctuations. It doesn’t need to be too frequent, but **you can’t rely solely on automated alerts**. Sometimes, an increase in the error rate from 2% to 4% is a trend issue that automated monitoring won’t tell you, but a human can easily spot, "This is something to watch out for."
**Core Insight**
Setting up automation is quick, but **doing monitoring right allows you to rest easy without constant oversight**. My experience is that automated alerts handle emergencies (the system completely crashing), while manual reviews are responsible for trend issues (gradually worsening). The combination of both ensures this system lasts long. Otherwise, no matter how smart the automation, it’s just a time bomb in a black box.
$BTC #DevOps #automation
After launching the automated system, how do I monitor if it’s still alive?
This is the deepest lesson I learned after setting up several automated pipelines: **the system can't crash in the middle of the night and let you find out the next day**.
I once deployed a scheduled task, thinking that setting up the cron would mean I could leave it alone. After a week, I checked the status and found it had silently stopped running for 3 days—database connection dropped, no notifications. Since then, I've established a complete monitoring philosophy, which I’ll share with you today.
**First Layer: Execution Cycle Monitoring**
The most basic method is to look at cron's last_run_at. My rule is: **if the last run time exceeds 2 times the expected cycle, trigger an alert immediately**. For example, if a task is supposed to run every 5 minutes, if last_run_at is more than 10 minutes ago, I directly send a Telegram alert. This metric is extremely effective—about 90% of "system crashes" can be caught within 1 hour, instead of passively waiting for the business department to notice.
**Second Layer: API Circuit Breaker Mechanism**
API instability is the norm. My approach is: **if 3 consecutive API requests fail, automatically trigger a circuit breaker for 24 hours**. Why 3 times? Because 1-2 failures could be network glitches, but 3 consecutive failures indicate a real issue. During the circuit breaker period, the system stops trying to call, avoiding wasting precious API quotas and log space in an error state. This is much more effective than blindly retrying.
**Third Layer: State File Persistence**
Every time the system runs, I write the current status—success count, failure count, timestamp, error messages—into a state file. I keep this file for 30 days of history. What’s the benefit of this? It allows for retrospection—"Why did the posting rate suddenly drop to 60% last Wednesday?"—just check the logs for the answer. The state file takes up minimal space but gives me a complete audit trail.
**Fourth Layer: Weekly Manual Review**
I spend 15 minutes each week letting the system automatically generate a summary report: posting success rate, error rate distribution, word count statistics, and whether there are any abnormal fluctuations. It doesn’t need to be too frequent, but **you can’t rely solely on automated alerts**. Sometimes, an increase in the error rate from 2% to 4% is a trend issue that automated monitoring won’t tell you, but a human can easily spot, "This is something to watch out for."
**Core Insight**
Setting up automation is quick, but **doing monitoring right allows you to rest easy without constant oversight**. My experience is that automated alerts handle emergencies (the system completely crashing), while manual reviews are responsible for trend issues (gradually worsening). The combination of both ensures this system lasts long. Otherwise, no matter how smart the automation, it’s just a time bomb in a black box.
$BTC #DevOps #automation
This is the deepest lesson I learned after setting up several automated pipelines: **the system can't crash in the middle of the night and let you find out the next day**.
I once deployed a scheduled task, thinking that setting up the cron would mean I could leave it alone. After a week, I checked the status and found it had silently stopped running for 3 days—database connection dropped, no notifications. Since then, I've established a complete monitoring philosophy, which I’ll share with you today.
**First Layer: Execution Cycle Monitoring**
The most basic method is to look at cron's last_run_at. My rule is: **if the last run time exceeds 2 times the expected cycle, trigger an alert immediately**. For example, if a task is supposed to run every 5 minutes, if last_run_at is more than 10 minutes ago, I directly send a Telegram alert. This metric is extremely effective—about 90% of "system crashes" can be caught within 1 hour, instead of passively waiting for the business department to notice.
**Second Layer: API Circuit Breaker Mechanism**
API instability is the norm. My approach is: **if 3 consecutive API requests fail, automatically trigger a circuit breaker for 24 hours**. Why 3 times? Because 1-2 failures could be network glitches, but 3 consecutive failures indicate a real issue. During the circuit breaker period, the system stops trying to call, avoiding wasting precious API quotas and log space in an error state. This is much more effective than blindly retrying.
**Third Layer: State File Persistence**
Every time the system runs, I write the current status—success count, failure count, timestamp, error messages—into a state file. I keep this file for 30 days of history. What’s the benefit of this? It allows for retrospection—"Why did the posting rate suddenly drop to 60% last Wednesday?"—just check the logs for the answer. The state file takes up minimal space but gives me a complete audit trail.
**Fourth Layer: Weekly Manual Review**
I spend 15 minutes each week letting the system automatically generate a summary report: posting success rate, error rate distribution, word count statistics, and whether there are any abnormal fluctuations. It doesn’t need to be too frequent, but **you can’t rely solely on automated alerts**. Sometimes, an increase in the error rate from 2% to 4% is a trend issue that automated monitoring won’t tell you, but a human can easily spot, "This is something to watch out for."
**Core Insight**
Setting up automation is quick, but **doing monitoring right allows you to rest easy without constant oversight**. My experience is that automated alerts handle emergencies (the system completely crashing), while manual reviews are responsible for trend issues (gradually worsening). The combination of both ensures this system lasts long. Otherwise, no matter how smart the automation, it’s just a time bomb in a black box.
$BTC #DevOps #automation
111
·
--
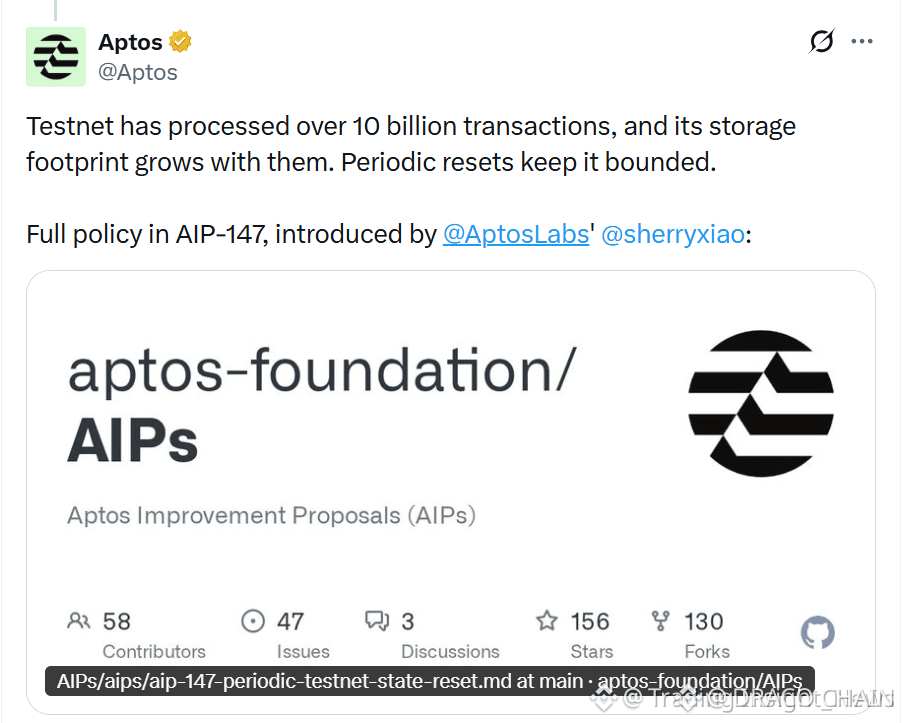
🚨 $APT TESTNET RESET APPROACHES OCT 7 – PREP FOR STORAGE SWEEP 🦈
Aptos is slated to wipe its testnet clean on Oct 7, resetting contracts, balances and transaction history to zero. 📌 This full‑state revert follows more than 10 B transactions, a storage load that threatens cost efficiency.
Smart‑money developers view the purge as a liquidity‑reset for on‑chain storage, clearing stale state and freeing space for fresh deployments. 📊 Expect a brief dip in testnet activity as teams redeploy, but the mainnet stays untouched.
📈 Keep an eye on the post‑reset performance metrics; a leaner testnet often translates into smoother dev cycles and sharper fee signals on the live chain. 💡
💬 How are you adjusting your testnet strategy ahead of the Oct 7 reset?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #APT #TestnetReset #DevOps #Aptos #Crypto
🦈 🔥
🚨 $APT TESTNET RESET APPROACHES OCT 7 – PREP FOR STORAGE SWEEP 🦈
Aptos is slated to wipe its testnet clean on Oct 7, resetting contracts, balances and transaction history to zero. 📌 This full‑state revert follows more than 10 B transactions, a storage load that threatens cost efficiency.
Smart‑money developers view the purge as a liquidity‑reset for on‑chain storage, clearing stale state and freeing space for fresh deployments. 📊 Expect a brief dip in testnet activity as teams redeploy, but the mainnet stays untouched.
📈 Keep an eye on the post‑reset performance metrics; a leaner testnet often translates into smoother dev cycles and sharper fee signals on the live chain. 💡
💬 How are you adjusting your testnet strategy ahead of the Oct 7 reset?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #APT #TestnetReset #DevOps #Aptos #Crypto
🦈 🔥
Aptos is slated to wipe its testnet clean on Oct 7, resetting contracts, balances and transaction history to zero. 📌 This full‑state revert follows more than 10 B transactions, a storage load that threatens cost efficiency.
Smart‑money developers view the purge as a liquidity‑reset for on‑chain storage, clearing stale state and freeing space for fresh deployments. 📊 Expect a brief dip in testnet activity as teams redeploy, but the mainnet stays untouched.
📈 Keep an eye on the post‑reset performance metrics; a leaner testnet often translates into smoother dev cycles and sharper fee signals on the live chain. 💡
💬 How are you adjusting your testnet strategy ahead of the Oct 7 reset?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #APT #TestnetReset #DevOps #Aptos #Crypto
🦈 🔥
440

🚨 TRADERTRAITOR TARGETS DEV CLOUD KEYS IN PHISHING CAMPAIGN RECALLING $ZRO BACKDOORS! 🔍
Sophisticated state-sponsored actors are shifting vectors from direct smart contract exploits to underlying cloud infrastructure. 🔍 Recent forensics reveal TraderTraitor executing malicious Terraform Provider downloads, deploying macOS backdoors identical to those identified during the historical $ZRO infrastructure breach.
Smart money understands that protocol liquidity is only as secure as the developer API keys backing the ecosystem. 🛡️ With AWS and GCP credentials targeted across DevOps teams, monitoring operational risk is now just as critical as analyzing market structure.
💬 How are you adjusting your operational security protocols to protect your capital against infrastructure-level threats? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ZRO #CryptoSecurity #DevOps #SmartMoney #LayerZero
🛡️ 👁️
🚨 TRADERTRAITOR TARGETS DEV CLOUD KEYS IN PHISHING CAMPAIGN RECALLING $ZRO BACKDOORS! 🔍
Sophisticated state-sponsored actors are shifting vectors from direct smart contract exploits to underlying cloud infrastructure. 🔍 Recent forensics reveal TraderTraitor executing malicious Terraform Provider downloads, deploying macOS backdoors identical to those identified during the historical $ZRO infrastructure breach.
Smart money understands that protocol liquidity is only as secure as the developer API keys backing the ecosystem. 🛡️ With AWS and GCP credentials targeted across DevOps teams, monitoring operational risk is now just as critical as analyzing market structure.
💬 How are you adjusting your operational security protocols to protect your capital against infrastructure-level threats? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ZRO #CryptoSecurity #DevOps #SmartMoney #LayerZero
🛡️ 👁️
Sophisticated state-sponsored actors are shifting vectors from direct smart contract exploits to underlying cloud infrastructure. 🔍 Recent forensics reveal TraderTraitor executing malicious Terraform Provider downloads, deploying macOS backdoors identical to those identified during the historical $ZRO infrastructure breach.
Smart money understands that protocol liquidity is only as secure as the developer API keys backing the ecosystem. 🛡️ With AWS and GCP credentials targeted across DevOps teams, monitoring operational risk is now just as critical as analyzing market structure.
💬 How are you adjusting your operational security protocols to protect your capital against infrastructure-level threats? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ZRO #CryptoSecurity #DevOps #SmartMoney #LayerZero
🛡️ 👁️
73
·
--
🚨 NORTH KOREAN HACKERS UNLEASH NEW TERRAFORM PHISHING VECTOR TARGETING $BTC DEVELOPERS! 💣
📌 Sophisticated threat actor TraderTraitor is actively weaponizing malicious GitHub interview code to infiltrate Web3 infrastructure and hijack AWS credentials. 🔍 Devs downloading unverified repos are triggering stealthy macOS backdoors capable of draining cloud environments and compromised codebases.
⚠️ Institutional security is the real foundation of every $BTC bull run, and these attacks prove threat groups are hunting upstream developer access. 💬 Are you verifying your Terraform dependencies before running init scripts, or leaving your cloud infrastructure exposed? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #DevOps #Web3
🛡️ 🔍
🚨 NORTH KOREAN HACKERS UNLEASH NEW TERRAFORM PHISHING VECTOR TARGETING $BTC DEVELOPERS! 💣
📌 Sophisticated threat actor TraderTraitor is actively weaponizing malicious GitHub interview code to infiltrate Web3 infrastructure and hijack AWS credentials. 🔍 Devs downloading unverified repos are triggering stealthy macOS backdoors capable of draining cloud environments and compromised codebases.
⚠️ Institutional security is the real foundation of every $BTC bull run, and these attacks prove threat groups are hunting upstream developer access. 💬 Are you verifying your Terraform dependencies before running init scripts, or leaving your cloud infrastructure exposed? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #DevOps #Web3
🛡️ 🔍
📌 Sophisticated threat actor TraderTraitor is actively weaponizing malicious GitHub interview code to infiltrate Web3 infrastructure and hijack AWS credentials. 🔍 Devs downloading unverified repos are triggering stealthy macOS backdoors capable of draining cloud environments and compromised codebases.
⚠️ Institutional security is the real foundation of every $BTC bull run, and these attacks prove threat groups are hunting upstream developer access. 💬 Are you verifying your Terraform dependencies before running init scripts, or leaving your cloud infrastructure exposed? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #DevOps #Web3
🛡️ 🔍
36
·
--
Node Health Beyond UptimeA blockchain node can return a successful response and still be serving stale data. That is why a simple ping is not a production health check.
Start with reachability, but add freshness. Compare the node’s latest block height and timestamp with an independent reference. Watch synchronization status and peer health where those signals are available. A node that is online but several blocks behind can mislead wallets, dashboards, trading systems and indexers.
Measure request behavior too. Track latency percentiles, timeouts, rate-limit responses, JSON-RPC errors and method-specific failures. Separate read calls from transaction submission and subscription workloads because they can fail differently.
For infrastructure you control, monitor CPU, memory, disk capacity, disk latency, network traffic, process restarts and logs. Set alerts that name a condition and an action: sustained block lag, rising error rate, a WebSocket disconnect loop or disk usage approaching the level that threatens the node.
Metrics without ownership become noise. Every alert should have a threshold, severity, runbook and responsible person. The objective is to detect degradation before users become the monitoring system.
TokenToolHub’s guide compares the monitoring layers and tools:
https://tokentoolhub.com/best-blockchain-node-monitoring-tools/
#BlockchainNodes #RPCA #Devops #Web3Infrastructure #CryptoSecurity
Node Health Beyond Uptime
A blockchain node can return a successful response and still be serving stale data. That is why a simple ping is not a production health check.
Start with reachability, but add freshness. Compare the node’s latest block height and timestamp with an independent reference. Watch synchronization status and peer health where those signals are available. A node that is online but several blocks behind can mislead wallets, dashboards, trading systems and indexers.
Measure request behavior too. Track latency percentiles, timeouts, rate-limit responses, JSON-RPC errors and method-specific failures. Separate read calls from transaction submission and subscription workloads because they can fail differently.
For infrastructure you control, monitor CPU, memory, disk capacity, disk latency, network traffic, process restarts and logs. Set alerts that name a condition and an action: sustained block lag, rising error rate, a WebSocket disconnect loop or disk usage approaching the level that threatens the node.
Metrics without ownership become noise. Every alert should have a threshold, severity, runbook and responsible person. The objective is to detect degradation before users become the monitoring system.
TokenToolHub’s guide compares the monitoring layers and tools:
https://tokentoolhub.com/best-blockchain-node-monitoring-tools/
#BlockchainNodes #RPCA #Devops #Web3Infrastructure #CryptoSecurity
Start with reachability, but add freshness. Compare the node’s latest block height and timestamp with an independent reference. Watch synchronization status and peer health where those signals are available. A node that is online but several blocks behind can mislead wallets, dashboards, trading systems and indexers.
Measure request behavior too. Track latency percentiles, timeouts, rate-limit responses, JSON-RPC errors and method-specific failures. Separate read calls from transaction submission and subscription workloads because they can fail differently.
For infrastructure you control, monitor CPU, memory, disk capacity, disk latency, network traffic, process restarts and logs. Set alerts that name a condition and an action: sustained block lag, rising error rate, a WebSocket disconnect loop or disk usage approaching the level that threatens the node.
Metrics without ownership become noise. Every alert should have a threshold, severity, runbook and responsible person. The objective is to detect degradation before users become the monitoring system.
TokenToolHub’s guide compares the monitoring layers and tools:
https://tokentoolhub.com/best-blockchain-node-monitoring-tools/
#BlockchainNodes #RPCA #Devops #Web3Infrastructure #CryptoSecurity
85
·
--
Article
ICPay — Protocol Reliability: Zero-Downtime Canister Upgrades and State SafetyPreserving User Account Balances Across Production Motoko Releases
Upgrading smart contracts on live blockchain networks carries severe risk. Incorrect memory deserialization can permanently corrupt contract state and erase user account balances.
ICPay executes upgrades following rigorous Motoko stable memory persistence protocols.
───────────────
Core Technical Architecture & Mechanisms
───────────────
1. Stable Memory Data Structures
Critical user accounts, balances, and transaction indexes reside in Motoko stable variables that survive code updates without serialization bottlenecks.
2. Pre-Upgrade and Post-Upgrade Hooks
Deterministic migration routines validate state consistency before executing WebAssembly module replacement on canister 6vbhm-nqaaa-aaaan-q6muq-cai.
3. Verifiable Rollback Capabilities
The operations toolchain verifies cryptographic wasm hashes before applying upgrades, maintaining deterministic rollback paths if anomalies arise.
$ICP #ICP #DevOps
ICPay — Protocol Reliability: Zero-Downtime Canister Upgrades and State Safety
Preserving User Account Balances Across Production Motoko Releases
Upgrading smart contracts on live blockchain networks carries severe risk. Incorrect memory deserialization can permanently corrupt contract state and erase user account balances.
ICPay executes upgrades following rigorous Motoko stable memory persistence protocols.
───────────────
Core Technical Architecture & Mechanisms
───────────────
1. Stable Memory Data Structures
Critical user accounts, balances, and transaction indexes reside in Motoko stable variables that survive code updates without serialization bottlenecks.
2. Pre-Upgrade and Post-Upgrade Hooks
Deterministic migration routines validate state consistency before executing WebAssembly module replacement on canister 6vbhm-nqaaa-aaaan-q6muq-cai.
3. Verifiable Rollback Capabilities
The operations toolchain verifies cryptographic wasm hashes before applying upgrades, maintaining deterministic rollback paths if anomalies arise.
$ICP #ICP #DevOps
Upgrading smart contracts on live blockchain networks carries severe risk. Incorrect memory deserialization can permanently corrupt contract state and erase user account balances.
ICPay executes upgrades following rigorous Motoko stable memory persistence protocols.
───────────────
Core Technical Architecture & Mechanisms
───────────────
1. Stable Memory Data Structures
Critical user accounts, balances, and transaction indexes reside in Motoko stable variables that survive code updates without serialization bottlenecks.
2. Pre-Upgrade and Post-Upgrade Hooks
Deterministic migration routines validate state consistency before executing WebAssembly module replacement on canister 6vbhm-nqaaa-aaaan-q6muq-cai.
3. Verifiable Rollback Capabilities
The operations toolchain verifies cryptographic wasm hashes before applying upgrades, maintaining deterministic rollback paths if anomalies arise.
$ICP #ICP #DevOps
233
·
--
Bullish
GitHub Internal Breach Alert 🚨: TeamPCP claims exfiltration of ~4,000 private repos via a malicious VS Code extension on an employee device.
• No customer data leaked (yet).
• Supply chain attacks are the new norm.
• Action: Audit your extensions, rotate secrets, and enforce endpoint security.
Don't be the weakest link. 🛡️
#GitHub #CyberSecurity #TeamPCP #DevOps #SecurityAlert
GitHub Internal Breach Alert 🚨: TeamPCP claims exfiltration of ~4,000 private repos via a malicious VS Code extension on an employee device.
• No customer data leaked (yet).
• Supply chain attacks are the new norm.
• Action: Audit your extensions, rotate secrets, and enforce endpoint security.
Don't be the weakest link. 🛡️
#GitHub #CyberSecurity #TeamPCP #DevOps #SecurityAlert
• No customer data leaked (yet).
• Supply chain attacks are the new norm.
• Action: Audit your extensions, rotate secrets, and enforce endpoint security.
Don't be the weakest link. 🛡️
#GitHub #CyberSecurity #TeamPCP #DevOps #SecurityAlert
2
6
200
·
--
Recent security research uncovered malicious npm packages impersonating Rollup polyfill tools, highlighting supply‑chain risks for blockchain developers. 📊
Ethereum’s extensive tooling ecosystem, including popular rollup solutions, makes it a frequent target for such attacks. 🧠
The findings underscore the importance of verifying package signatures and using hardened development environments when building $ETH smart contracts. 🔍
Ethereum’s roadmap continues with upcoming rollup‑centric upgrades like EIP‑4844, aiming to improve scalability and reduce transaction costs. ⚡
Developers are encouraged to adopt verified libraries and monitor official channels for security advisories. 💡
DYOR before integrating any third‑party code into your $ETH projects. 🌐
How is your team strengthening its smart‑contract security in light of these new threats? #crypto #Ethereum #Security #DevOps #GAMERXERO
Recent security research uncovered malicious npm packages impersonating Rollup polyfill tools, highlighting supply‑chain risks for blockchain developers. 📊
Ethereum’s extensive tooling ecosystem, including popular rollup solutions, makes it a frequent target for such attacks. 🧠
The findings underscore the importance of verifying package signatures and using hardened development environments when building $ETH smart contracts. 🔍
Ethereum’s roadmap continues with upcoming rollup‑centric upgrades like EIP‑4844, aiming to improve scalability and reduce transaction costs. ⚡
Developers are encouraged to adopt verified libraries and monitor official channels for security advisories. 💡
DYOR before integrating any third‑party code into your $ETH projects. 🌐
How is your team strengthening its smart‑contract security in light of these new threats? #crypto #Ethereum #Security #DevOps #GAMERXERO
Ethereum’s extensive tooling ecosystem, including popular rollup solutions, makes it a frequent target for such attacks. 🧠
The findings underscore the importance of verifying package signatures and using hardened development environments when building $ETH smart contracts. 🔍
Ethereum’s roadmap continues with upcoming rollup‑centric upgrades like EIP‑4844, aiming to improve scalability and reduce transaction costs. ⚡
Developers are encouraged to adopt verified libraries and monitor official channels for security advisories. 💡
DYOR before integrating any third‑party code into your $ETH projects. 🌐
How is your team strengthening its smart‑contract security in light of these new threats? #crypto #Ethereum #Security #DevOps #GAMERXERO
26

⚡ CRITICAL GITHUB INFRASTRUCTURE OUTAGE SHAKES TECH AND $FET AI ECOSYSTEM WORKFLOWS! 🚨
Major core infrastructure is buckling under pressure today as GitHub hits severe database replication lag in its collaboration systems. 📊 With authorization interfaces failing and GitHub Actions stalling across the board, developer pipelines and automated deployment flows are essentially frozen in real time. 🔍
Smart money watches infrastructure glitches closely, knowing how code deployment delays impact momentum in fast-moving tech environments. ⚡ When the underlying execution layer stutters, execution speed becomes the ultimate premium on the board. 💬 Do you think infrastructure hiccups like this temporarily stall momentum, or will devs push right through the noise? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #FET #AI #DevOps #Crypto #Infrastructure
🔥 ⚡
⚡ CRITICAL GITHUB INFRASTRUCTURE OUTAGE SHAKES TECH AND $FET AI ECOSYSTEM WORKFLOWS! 🚨
Major core infrastructure is buckling under pressure today as GitHub hits severe database replication lag in its collaboration systems. 📊 With authorization interfaces failing and GitHub Actions stalling across the board, developer pipelines and automated deployment flows are essentially frozen in real time. 🔍
Smart money watches infrastructure glitches closely, knowing how code deployment delays impact momentum in fast-moving tech environments. ⚡ When the underlying execution layer stutters, execution speed becomes the ultimate premium on the board. 💬 Do you think infrastructure hiccups like this temporarily stall momentum, or will devs push right through the noise? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #FET #AI #DevOps #Crypto #Infrastructure
🔥 ⚡
Major core infrastructure is buckling under pressure today as GitHub hits severe database replication lag in its collaboration systems. 📊 With authorization interfaces failing and GitHub Actions stalling across the board, developer pipelines and automated deployment flows are essentially frozen in real time. 🔍
Smart money watches infrastructure glitches closely, knowing how code deployment delays impact momentum in fast-moving tech environments. ⚡ When the underlying execution layer stutters, execution speed becomes the ultimate premium on the board. 💬 Do you think infrastructure hiccups like this temporarily stall momentum, or will devs push right through the noise? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #FET #AI #DevOps #Crypto #Infrastructure
🔥 ⚡
114
·
--
Verified
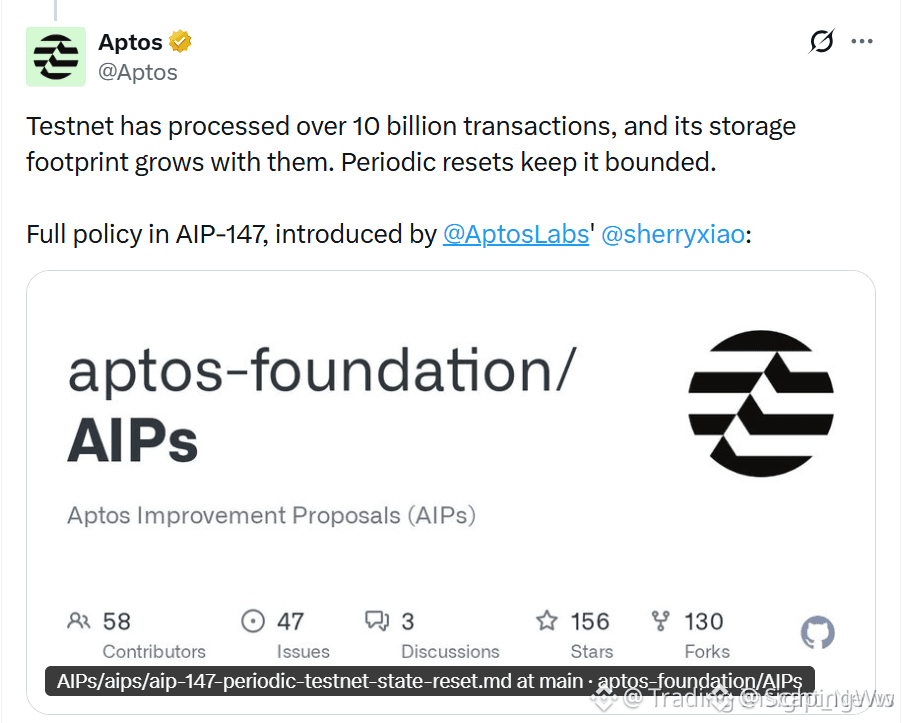
🚨 $APT TESTNET RESET SET FOR OCT 7 – STORAGE SWEEP INCOMING! 📊
Aptos is pulling the plug on its testnet on Oct 7, wiping contracts, balances and the entire transaction ledger. 🦈 This clean‑slate move trims storage pressure after crushing 10 B transactions, keeping the network lean for devs.
No ripple hits mainnet or devnet – they stay untouched, so production stays smooth. 📊 Expect a brief pause for redeployment, then a fresh canvas for new experiments. ⚡
💬 How are you prepping your test contracts for the reset? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #APT #TestnetReset #DevOps #Aptos #Crypto
🚀 🔥
🚨 $APT TESTNET RESET SET FOR OCT 7 – STORAGE SWEEP INCOMING! 📊
Aptos is pulling the plug on its testnet on Oct 7, wiping contracts, balances and the entire transaction ledger. 🦈 This clean‑slate move trims storage pressure after crushing 10 B transactions, keeping the network lean for devs.
No ripple hits mainnet or devnet – they stay untouched, so production stays smooth. 📊 Expect a brief pause for redeployment, then a fresh canvas for new experiments. ⚡
💬 How are you prepping your test contracts for the reset? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #APT #TestnetReset #DevOps #Aptos #Crypto
🚀 🔥
Aptos is pulling the plug on its testnet on Oct 7, wiping contracts, balances and the entire transaction ledger. 🦈 This clean‑slate move trims storage pressure after crushing 10 B transactions, keeping the network lean for devs.
No ripple hits mainnet or devnet – they stay untouched, so production stays smooth. 📊 Expect a brief pause for redeployment, then a fresh canvas for new experiments. ⚡
💬 How are you prepping your test contracts for the reset? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #APT #TestnetReset #DevOps #Aptos #Crypto
🚀 🔥
4
1k
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BTCReboundsAbove$60KAmidWhaleDipBuying
53,558 views
285 Discussing
2
#SolanaSets2027RoadmapToDoubleComputeCapacity
37,321 views
782 Discussing
3
#CaliforniaNvidiaProbeExaminesPotentialCriminalViolations
10,013 views
101 Discussing
4
#BlackRockLaunchesHKDollarDigitalLiquidityFund
31,193 views
611 Discussing
5
#NvidiaLoses$2.7TrillionInMonthAndAHalf
70,144 views
285 Discussing
6
#GlobalStocksFaceLongestLosingStreakSince2023
530,835 views
3,337 Discussing
7
#BlackRockIBITPostsRecord$541MSingleDayOutflow
86,884 views
176 Discussing
8
#AnthropicPlungesTowardIPOPriceonDay2
290,550 views
2,238 Discussing
9
#TwentyOneCapitalAdds172.25BTC
150,948 views
1,561 Discussing
10
#HKBillWouldExcludeTokenizedDepositsFromVirtualAssets
17,260 views
102 Discussing