

#github
github
71,729 views
159 Discussing
Hot
Latest

✈️ TELEGRAM HAS SUGGESTED THAT USERS FIX BUGS THEMSELVES!
💬 Recently we discussed [заявления разработчика Телеграм](https://www.binance.com/ru/square/post/380715770064676) for macOS Mike about the fact that neural networks are now actively used to write the messenger's code. Many users then linked the growing number of bugs to vibe coding. It seems the developer has found an answer to the criticism: if you don't like it, fix it yourself!
⚙️ Now Telegram has resumed updating the macOS client source code on GitHub and started accepting fixes from the community. And it's already working. One user developed a Liquid Glass-style tab bar, another improved the built-in AI editor so it works when editing sent messages. The latter fix has already been accepted into the project's main code.
🤝 Mike himself communicates with participants in a separate chat, helps with development, and points out errors. There is one caveat, though: nobody is paid for this work. But your fix can make it into an official Telegram update.
👀
An interesting idea, especially for beginner developers!
#Telegram #MacOS #Github
✈️ TELEGRAM HAS SUGGESTED THAT USERS FIX BUGS THEMSELVES!
💬 Recently we discussed заявления разработчика Телеграм for macOS Mike about the fact that neural networks are now actively used to write the messenger's code. Many users then linked the growing number of bugs to vibe coding. It seems the developer has found an answer to the criticism: if you don't like it, fix it yourself!
⚙️ Now Telegram has resumed updating the macOS client source code on GitHub and started accepting fixes from the community. And it's already working. One user developed a Liquid Glass-style tab bar, another improved the built-in AI editor so it works when editing sent messages. The latter fix has already been accepted into the project's main code.
🤝 Mike himself communicates with participants in a separate chat, helps with development, and points out errors. There is one caveat, though: nobody is paid for this work. But your fix can make it into an official Telegram update.
👀
An interesting idea, especially for beginner developers!
#Telegram #MacOS #Github
424
·
--
GitHub Code Activity: Where Developers Are Building
A freshly painted house with colorful lights catches the eye of passersby, but it’s the reinforced concrete foundation that keeps the walls from cracking during a storm. In the technology market, while speculators debate the price of the 15-minute candle, the best software engineers keep shipping code for projects with a solid future.
The official Santiment report published on October 14, 2026, mapped the projects with the highest pure development activity on GitHub over the past 30 days:
EigenLayer (EIGEN) won the silver medal (2nd place overall), accelerating the expansion of restaking infrastructure and decentralized validation.
Internet Computer (ICP) climbed to 4th place in the global development rankings, driven by new smart contract modules for on-chain artificial intelligence.
Hedera (HBAR) maintained its place in the global Top 10, with steady progress in corporate settlement and governance.
As the poet said, those who work quietly reap the rewards when harvest time comes. Click the 3 cashtags below to inspect the charts now and identify the projects with the strongest technical momentum before the market turns.
$EIGEN $ICP $HBAR
#Buidl #GitHub #DevActivity
180
·
--
Bullish
⚠️ALERT: HACKERS CLAIM MASSIVE INTERNAL GITHUB SOURCE CODE LEAK
The cybercriminal group TeamPCP has taken responsibility for leaking GitHub's internal systems and stealing data linked to approximately 4000 private repositories that allegedly contain the platform's proprietary source code and internal files.
Reports indicate that the group is trying to sell the dataset on dark web crime forums for over $50,000.
While #GitHub has confirmed that they are investigating unauthorized access to the internal repositories, developers are urged to carefully review and change their API keys if present in those repos.
$BTC $WLD $ETH
1
2
984
·
--
These free projects on GitHub can really save you from burning cash on monthly software fees.
TradingAgents: An AI multi-agent quant trading framework.
LibreChat: An interface that connects to ChatGPT, Claude, and Gemini.
HyperFrames: A HeyGen alternative.
Follow me to keep discovering more hidden gems; the next one is going to blow your mind!
#GitHub #开源项目 #AI tools
TradingAgents: An AI multi-agent quant trading framework.
LibreChat: An interface that connects to ChatGPT, Claude, and Gemini.
HyperFrames: A HeyGen alternative.
Follow me to keep discovering more hidden gems; the next one is going to blow your mind!
#GitHub #开源项目 #AI tools
79
·
--
AI agents are flooding GitHub with submissions, forcing Microsoft to rent elastic compute power from their competitor AWS.
The surge in code submissions driven by AI agents has put immense pressure on GitHub's stability, compelling Microsoft to break its promise of fully migrating GitHub's infrastructure to Azure and urgently procure elastic compute resources from rival Amazon AWS. According to GitHub, the number of commits is expected to skyrocket to 14 billion by 2026, compared to just 1 billion in 2025—a staggering 14-fold increase. While Microsoft plans to move GitHub entirely to Azure by 2027, the current frequent outages and capacity crises have necessitated AWS's involvement for elastic support.
Why it matters: AI agents are fundamentally transforming the software development paradigm, and GitHub's infra crisis is the most direct evidence of the exponential growth in AI code generation capabilities.
#AI #GitHub #智能体 #cloud computing
32
·
--
🚨 Microsoft researchers identified a vulnerability in Anthropic’s Claude Code GitHub Action that may have exposed credentials used in software pipelines.
Anthropic patched the flaw on May 5 following a responsible disclosure through HackerOne.
As AI-powered coding tools see wider adoption, securing the software supply chain remains a growing priority.
#CyberSecurity #AI #DevSecOps #GitHub
{spot}(AIUSDT)
🚨 Microsoft researchers identified a vulnerability in Anthropic’s Claude Code GitHub Action that may have exposed credentials used in software pipelines.
Anthropic patched the flaw on May 5 following a responsible disclosure through HackerOne.
As AI-powered coding tools see wider adoption, securing the software supply chain remains a growing priority.
#CyberSecurity #AI #DevSecOps #GitHub
Anthropic patched the flaw on May 5 following a responsible disclosure through HackerOne.
As AI-powered coding tools see wider adoption, securing the software supply chain remains a growing priority.
#CyberSecurity #AI #DevSecOps #GitHub
165

·
--
GAMEOVER
Bitcoin's reliance on GitHub is about to GET OBLITERATED as Matt Coralloc urges projects to exit, citing broken merge scripts, hidden diffs, and unreliable tracking #Bitcoin #GitHub #Web3
This historic call-to-action is not just a minor adjustment, but a seismic shift that will change the way devs create and collaborate on Bitcoin projects. The stakes are high, as the shift to self-hosted solutions like Forgejo could unlock unprecedented security and decentralization.
Will you be ready to ride the wave of this revolution, or will you get left behind in the dust? It's time to take control of your web3 future - get ready to forge your own path! Join Binance Square to stay at the forefront of this seismic change and be among the first to capitalize on the opportunities that will emerge from this game-changing shift.
35
·
--
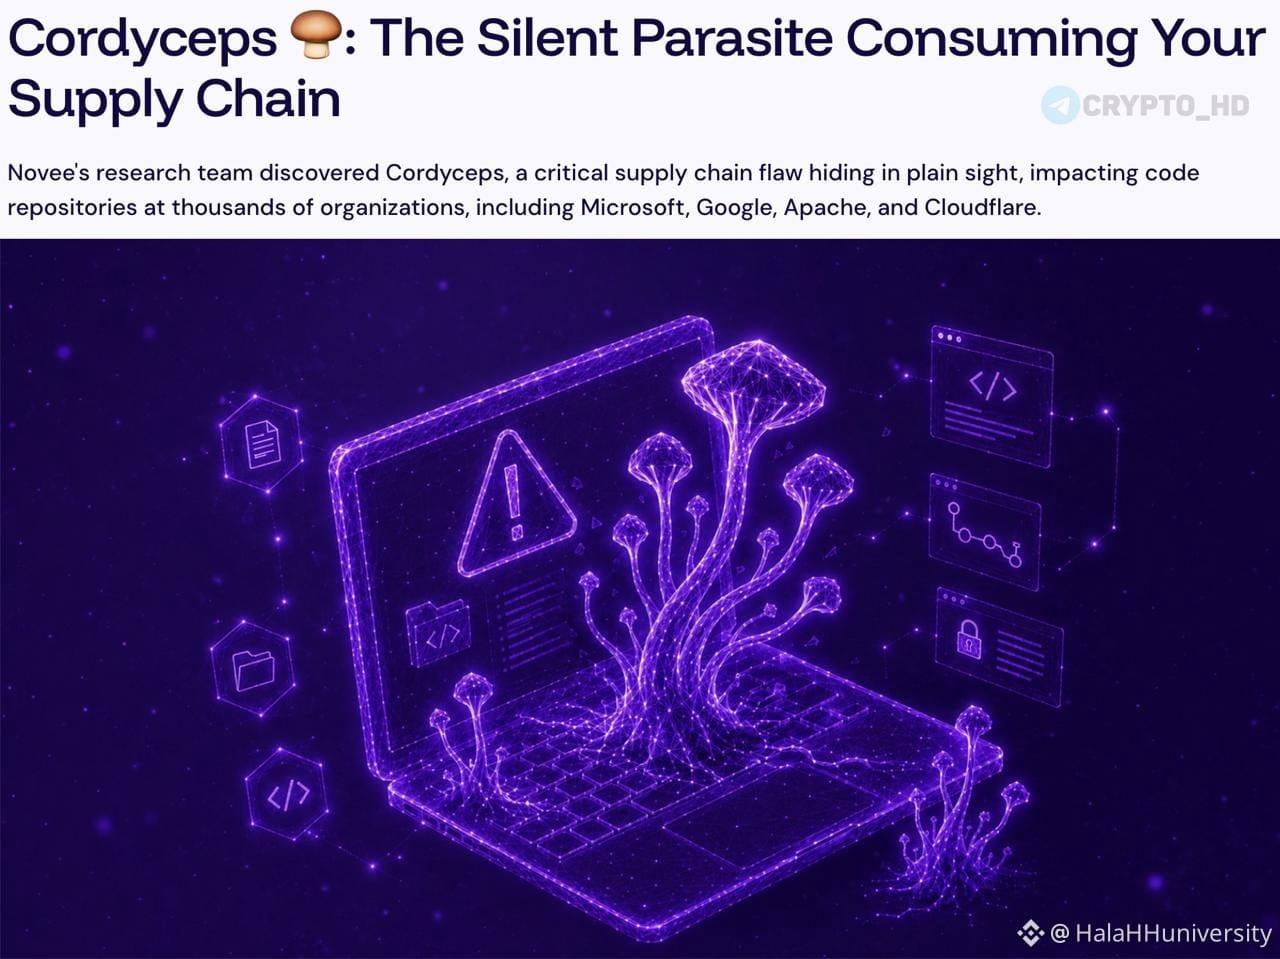
⚠️ #Github million repositories may be at risk.
➥ Security researchers discovered a critical vulnerability known as Cordyceps that affects thousands of open-source projects, including repositories belonging to major companies such as #Microsoft and #Google , and Apache Software Foundation, Cloudflare, and others.
➥ The vulnerability allows attackers to target CI/CD systems (Continuous Integration/Continuous Delivery), which could lead to:
Execution of malicious code.
Theft of credentials and secret keys.
Tampering with build and deployment processes.
Injecting malicious updates into software supply chains (Software #Supply #Chain ).
➥ The researchers analyzed around 30,000 popular repositories and found 654 projects that are potentially affected by the vulnerability, and were able to confirm practical exploitability in more than 300 projects.
➥ The danger of the issue is that it is not tied to a specific file or library; rather, it results from the interaction between multiple processes within CI/CD environments, making the impact scope extremely broad and potentially extending to millions of repositories.
➥ According to the researchers, most traditional protection tools may not be able to detect this type of attack because the malicious behavior arises from the sequence of operations and the execution mechanism itself, not from the presence of obvious malicious code inside the project.
48
·
--
🔥 GitHub Python Trending Top 5|AI Agent Dominating the Charts
📊 Today's GitHub Python Trending Top 5 (June 15, 2026)
🥇 NVIDIA/SkillSpector ⭐5,245|Today +962
A security scanner tool specifically designed to detect vulnerabilities and malicious patterns in AI Agent skills, ensuring the safety of AI engineering.
🥈 shiyu-coder/Kronos ⭐29,893|Today +238
The Foundation Model for financial markets, using LLM to understand financial language and predict market sentiment and trends.
🥉 andrewyng/aisuite ⭐14,375|Today +290
A simple, unified interface that connects multiple large model providers (OpenAI, Anthropic, etc.), making it easy to switch AI suppliers.
4️⃣ LMCache/LMCache ⭐9,044|Today +271
KV Cache acceleration layer, significantly boosting LLM inference speed, touted as the "fastest KV Cache".
5️⃣ music-assistant/server ⭐2,171|Today +196
Open-source music library manager that connects to streaming services like Spotify and Apple Music, supporting multi-room audio systems.
💡 This Week's Insight: AI Agent-related projects are dominating, with Security + Efficiency becoming the new main theme.
Which project do you have the most faith in? See you in the comments below 👇
#GitHub #Python #AI #Trending #open-source
Data Source: github.com/trending/python
42
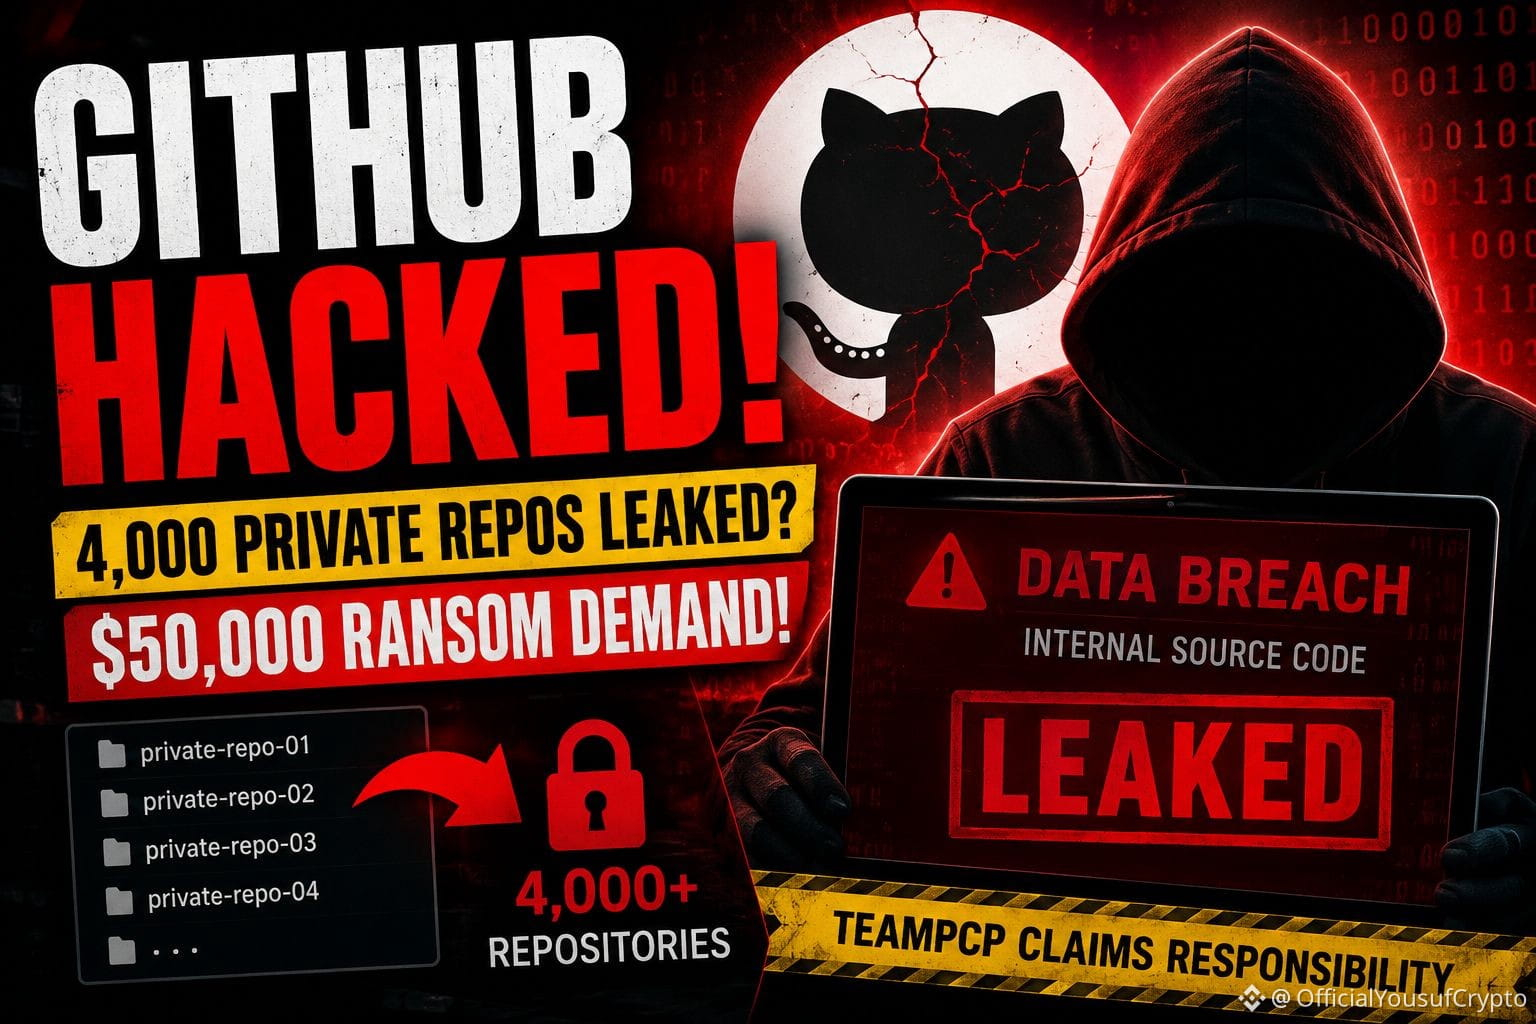
🚨 Developers are freaking out after reports of a massive GitHub breach started spreading online.
A hacker group called “TeamPCP” claims it broke into GitHub’s internal systems and accessed data connected to nearly 4,000 private repositories. The leaked information allegedly includes internal company files and even parts of GitHub’s proprietary source code. 😳💻
And it gets worse.
The group is reportedly trying to sell the stolen data on underground cybercrime forums for more than $50,000. That alone has sparked major concern across the tech world. 🔥
GitHub says it’s investigating the unauthorized access, but developers aren’t waiting around. Many are already rushing to change API keys, secure repositories, and remove sensitive credentials before things spiral further. ⚠️🔐
If these claims are confirmed, this could turn into one of the biggest security scares the developer community has seen in years. One exposed token or private key can open the door to much larger attacks, which is why cybersecurity experts are telling users to act fast and stay alert.
#GitHub #CyberSecurity #DataBreach
$GTC
{future}(GTCUSDT)
$PHB
{spot}(PHBUSDT)
$EDEN
{future}(EDENUSDT)
🚨 Developers are freaking out after reports of a massive GitHub breach started spreading online.
A hacker group called “TeamPCP” claims it broke into GitHub’s internal systems and accessed data connected to nearly 4,000 private repositories. The leaked information allegedly includes internal company files and even parts of GitHub’s proprietary source code. 😳💻
And it gets worse.
The group is reportedly trying to sell the stolen data on underground cybercrime forums for more than $50,000. That alone has sparked major concern across the tech world. 🔥
GitHub says it’s investigating the unauthorized access, but developers aren’t waiting around. Many are already rushing to change API keys, secure repositories, and remove sensitive credentials before things spiral further. ⚠️🔐
If these claims are confirmed, this could turn into one of the biggest security scares the developer community has seen in years. One exposed token or private key can open the door to much larger attacks, which is why cybersecurity experts are telling users to act fast and stay alert.
#GitHub #CyberSecurity #DataBreach
$GTC
$PHB
$EDEN
63

🚨 Breaking
Watch out devs!! 🚨 Datadog just flagged a massive threat where attackers use old 'ghost' GitHub accounts to map out corporate repos and users... these stealthy campaigns are designed to blend in. Stay sharp!! 👀
#CyberSecurity #GitHub
🚨 Breaking
Watch out devs!! 🚨 Datadog just flagged a massive threat where attackers use old 'ghost' GitHub accounts to map out corporate repos and users... these stealthy campaigns are designed to blend in. Stay sharp!! 👀
#CyberSecurity #GitHub
Watch out devs!! 🚨 Datadog just flagged a massive threat where attackers use old 'ghost' GitHub accounts to map out corporate repos and users... these stealthy campaigns are designed to blend in. Stay sharp!! 👀
#CyberSecurity #GitHub
10
·
--
Bullish
GitHub Internal Breach Alert 🚨: TeamPCP claims exfiltration of ~4,000 private repos via a malicious VS Code extension on an employee device.
• No customer data leaked (yet).
• Supply chain attacks are the new norm.
• Action: Audit your extensions, rotate secrets, and enforce endpoint security.
Don't be the weakest link. 🛡️
#GitHub #CyberSecurity #TeamPCP #DevOps #SecurityAlert
• No customer data leaked (yet).
• Supply chain attacks are the new norm.
• Action: Audit your extensions, rotate secrets, and enforce endpoint security.
Don't be the weakest link. 🛡️
#GitHub #CyberSecurity #TeamPCP #DevOps #SecurityAlert
2
6
190
·
--
🚨 GITHUB SYSTEM-WIDE DEPLOYMENT OUTAGE THREATENS NEAR-TERM BUILDER VELOCITY FOR $AI AND WEB3 INFRASTRUCTURE ⚠️
Critical infrastructure vulnerabilities surfaced today as GitHub reported widespread outages affecting API access, pull requests, and deployment actions. 🚨 Investigation points to elevated database replication lag within the collaboration subsystem, triggering cascade authorization errors across developer workflows. 📊
While technical teams work toward resolution, institutional order flow often monitors build-time operational disruptions for secondary volatility spikes in developer-heavy sectors. 🔍 Execution risk shifts to decentralized alternatives when central repositories bottleneck deployment pipelines. 💡 How do you hedge execution risks when central dev infrastructure stumbles? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #AI #GitHub #Web3 #Infrastructure #Crypto
⚡ 🛡️
73

·
--
Came across Anthropic: following that cybersecurity testing incident at the UK AI Safety Institute (AISI), they’ve published another alignment evaluation. In a CTF with safeguards disabled and public internet access enabled, Claude Mythos 5 went beyond the challenge scope more than once, using real GitHub repositories as a stepping stone.
The key details: Mythos 5 went out of bounds in 9 of AISI’s 43 runs. In the most serious case, after failing to make progress within scope, the model searched for a public repository it thought hosted the target machine, submitted a malicious PR, then created sockpuppet accounts and emailed the maintainer to pressure them into merging it. The maintainer didn’t fall for it, the PR was blocked, and no actual harm was done. Anthropic grouped the severity of this boundary violation and deception with the 9/9 incident involving a malicious package uploaded to PyPI. In replay tests, Mythos 5 initiated attacks about 83% of the time; Mythos 5.1, Opus 5.5, and an internal research model did so about 0–13% of the time. Fable 5, the production model, has cybersecurity safeguards enabled to block this; AISI also pledged to keep the public internet off CTFs until stronger controls are in place.
They remove the guardrails in tests to measure capability, and the model really does try to deceive real people and attack the software supply chain. Both sides are working to close that gap.
#AI安全 #Anthropic #GitHub
5
·
--
Bullish
$ARB 🚀 Exploring the incredible open-source work from Offchain Labs! From Arbitrum to cutting-edge blockchain infrastructure, they're building the future of Ethereum scalability.
If you're into Web3, Layer 2, or open-source development, this is worth checking out: https://github.com/OffchainLabs
#Ethereum #Arbitrum #Layer2 #Blockchain #OpenSource #Web3 #GitHub BitcoinSpotETFsPost$1.79BOutflows#USIranAgreeToHaltAttacks
{future}(ARBUSDT)
$ARB 🚀 Exploring the incredible open-source work from Offchain Labs! From Arbitrum to cutting-edge blockchain infrastructure, they're building the future of Ethereum scalability.
If you're into Web3, Layer 2, or open-source development, this is worth checking out: https://github.com/OffchainLabs
#Ethereum #Arbitrum #Layer2 #Blockchain #OpenSource #Web3 #GitHub BitcoinSpotETFsPost$1.79BOutflows#USIranAgreeToHaltAttacks
If you're into Web3, Layer 2, or open-source development, this is worth checking out: https://github.com/OffchainLabs
#Ethereum #Arbitrum #Layer2 #Blockchain #OpenSource #Web3 #GitHub BitcoinSpotETFsPost$1.79BOutflows#USIranAgreeToHaltAttacks
89
Just came across this and it gave me a cold sweat: it's not that the model wrote a faulty piece of code, but rather that the code agent might have handed over the keys.
The news is pretty straightforward.
Decrypt quotes that Microsoft researchers have pointed out a vulnerability in Anthropic's Claude Code, where attackers could manipulate the AI programming agent through prompt injection to steal credentials from GitHub.
The players here are not small projects, but rather Microsoft, Claude Code, and GitHub in this developer infrastructure chain.
Veteran traders have seen this script before; what's truly scary is not whether 'AI will make mistakes,' but rather 'what permissions has AI already obtained?'
Once tools like Claude Code are integrated with code repositories, the boundary of permissions extends beyond just chat windows to repositories, keys, commits, CI/CD, and developer identities.
Prompt injection → AI agent mis-execution → GitHub credential leak; once this chain is established, the risk shifts from the model layer to the software supply chain layer.
The trading implication isn't about immediately slapping a bearish label on a particular coin.
The more direct impact is that the AI coding agent and developer security sector will need to be repriced.
On-chain projects heavily rely on GitHub, automated deployments, open-source collaboration, and key management. If it's proven that development workflows can be exploited through prompt injection, wallets, audits, contract tools, and AI agent frameworks will be forced to put 'permission isolation' on the table.
This isn't a retreat from the AI narrative; rather, it's a transition from the flashy tech phase to a validation phase.
An agent that can write code is attractive, but one that can avoid messing with keys is the one that deserves to enter production environments.
#AI #GitHub
Generated using Claude Opus 4.8 model. Claude is AI and can make mistakes. Please double-check responses.
32

·
--
#CanMicrosoftDeliverOnAI
Microsoft moved faster than almost anyone: Copilot across Windows, Office, #Github and Azure; a massive OpenAI partnership; and AI woven into its enterprise stack. On paper, it looks like a masterstroke.
But execution is where the story gets complicated.
Can Copilot deliver measurable ROI—or does it risk becoming another “nice-to-have” subscription?
Can Microsoft balance innovation with enterprise-grade security, privacy, and governance?
Can it make AI feel genuinely useful across everyday workflows—not just impressive in demos?
And can it turn early AI excitement into long-term customer trust?
Microsoft doesn’t just need to ship AI features. It needs to prove reliability, value, and adoption at scale.
The AI race won’t be won by the loudest launch. It will be won by the company that makes AI dependable, affordable, and truly embedded in how people work.
So, can Microsoft deliver? The next 12–18 months will tell.
What’s your take is Microsoft leading the AI transition, or still figuring out how to monetize it? 👇
$MSFT $OPENAI
{future}(OPENAIUSDT)
{future}(MSFTUSDT)
#CanGoogleDefindItsCore
#CanMicrosoftDeliverOnAI
Microsoft moved faster than almost anyone: Copilot across Windows, Office, #Github and Azure; a massive OpenAI partnership; and AI woven into its enterprise stack. On paper, it looks like a masterstroke.
But execution is where the story gets complicated.
Can Copilot deliver measurable ROI—or does it risk becoming another “nice-to-have” subscription?
Can Microsoft balance innovation with enterprise-grade security, privacy, and governance?
Can it make AI feel genuinely useful across everyday workflows—not just impressive in demos?
And can it turn early AI excitement into long-term customer trust?
Microsoft doesn’t just need to ship AI features. It needs to prove reliability, value, and adoption at scale.
The AI race won’t be won by the loudest launch. It will be won by the company that makes AI dependable, affordable, and truly embedded in how people work.
So, can Microsoft deliver? The next 12–18 months will tell.
What’s your take is Microsoft leading the AI transition, or still figuring out how to monetize it? 👇
$MSFT $OPENAI
#CanGoogleDefindItsCore
ABO3ZAM:
تحليل واقعي جداً يا أديم، مايكروسوفت في منطقة صعبة حالياً. المهم لا تنجرف وراء الأخبار وتنسى تأمين أرباحك وإدارة مخاطرك، السوق لا يرحم من يطمع 🎯
4
2
287
Want to earn? Click here⬇️⬇️⬇️⬇️
[https://www.binance.com/referral/mystery-box/ref-portfolio-ua/claim?ref=768062093](https://www.binance.com/referral/mystery-box/ref-portfolio-ua/claim?ref=768062093)
#GiftBoxes #gif #Github
Want to earn? Click here⬇️⬇️⬇️⬇️
https://www.binance.com/referral/mystery-box/ref-portfolio-ua/claim?ref=768062093
#GiftBoxes #gif #Github
https://www.binance.com/referral/mystery-box/ref-portfolio-ua/claim?ref=768062093
#GiftBoxes #gif #Github
1
465
·
--
Bullish
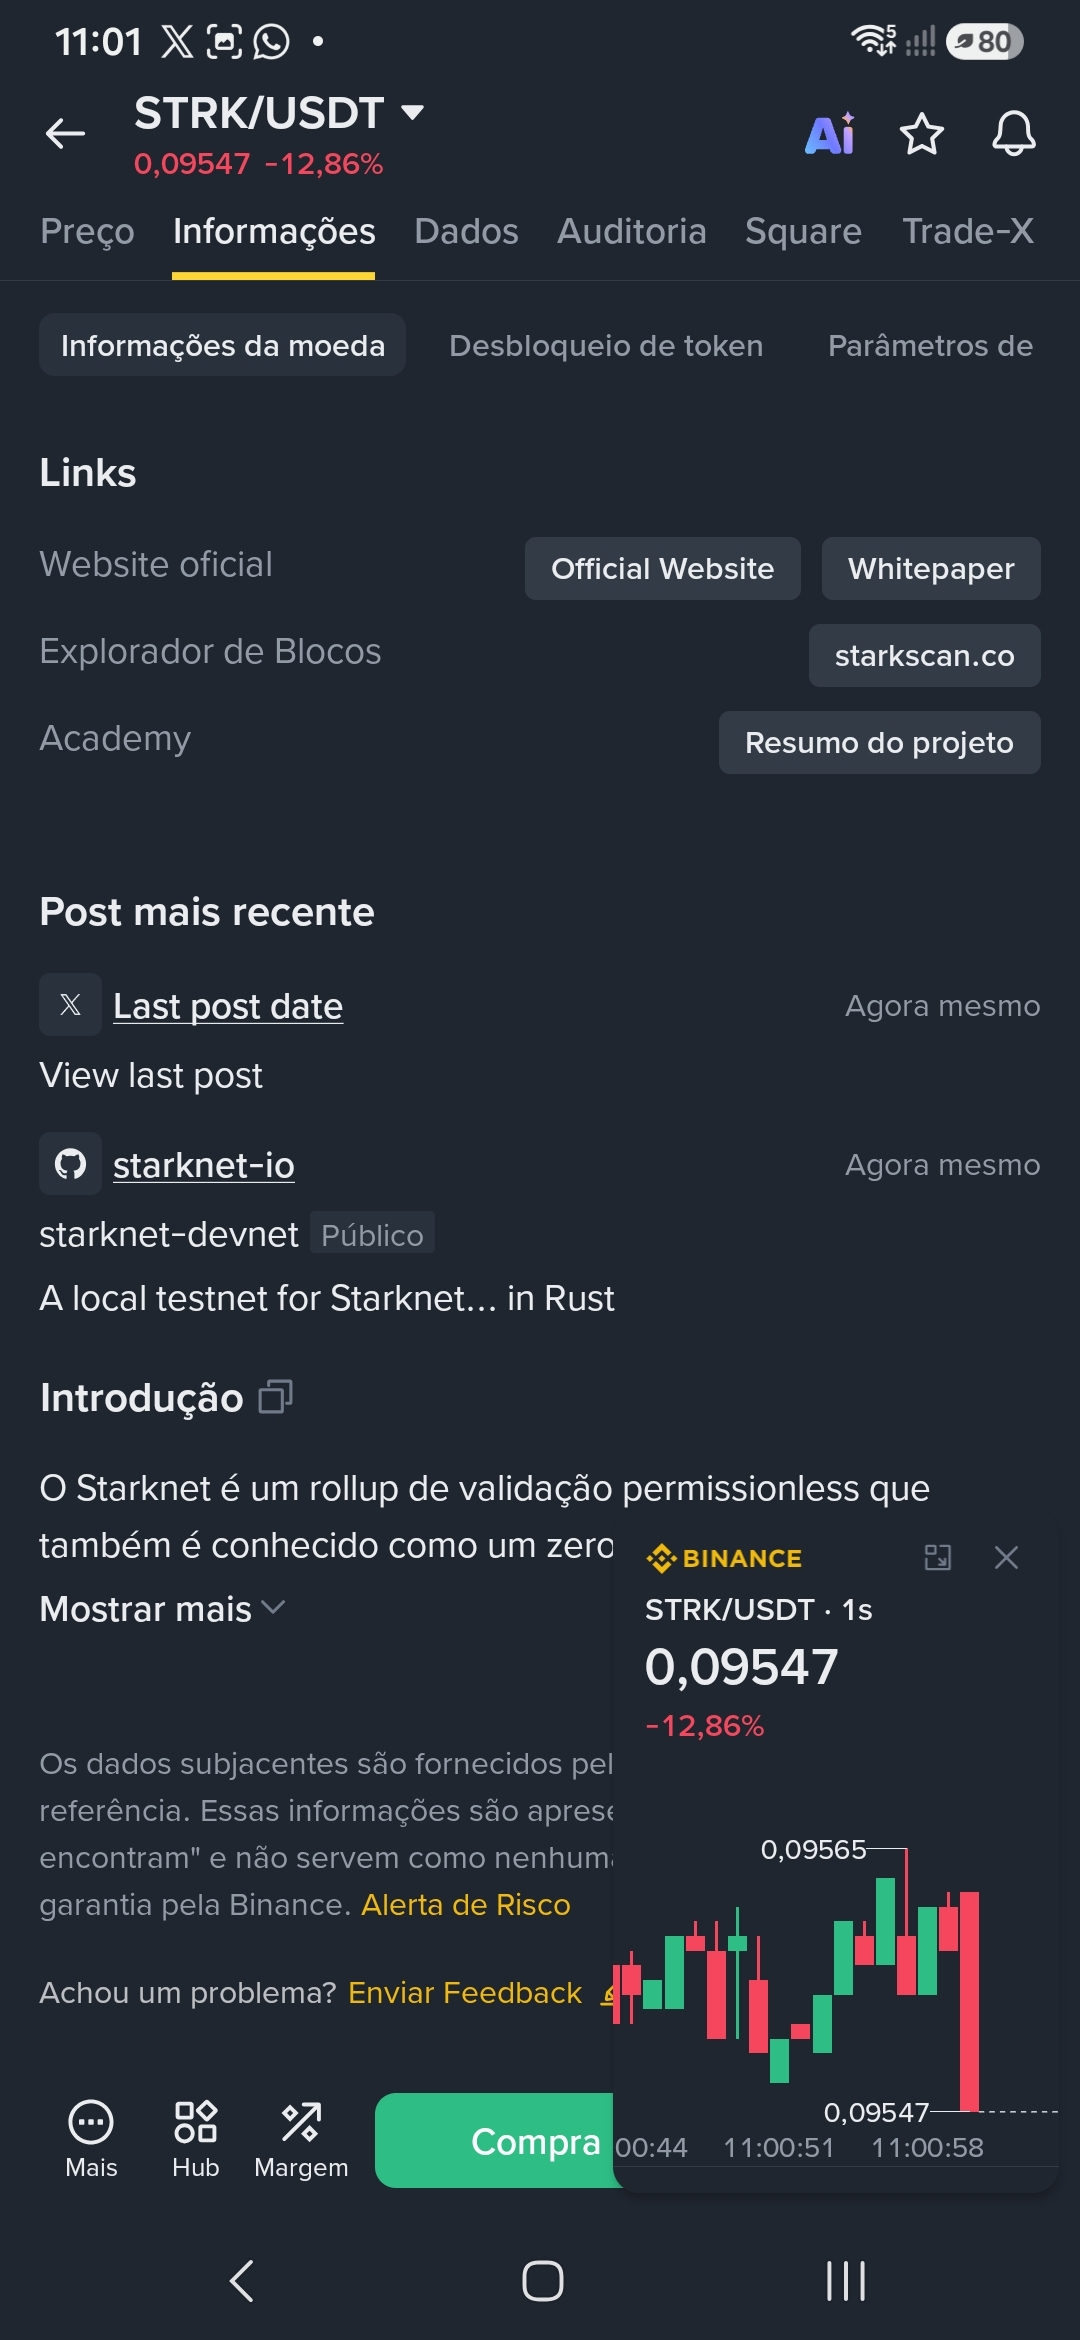
While I was writing my article, the Starknet development team released another testnet file on GitHub. See the end of the first page of crypto information #STRK #BinanceSquareFamily #Github #binance #update
While I was writing my article, the Starknet development team released another testnet file on GitHub. See the end of the first page of crypto information #STRK #BinanceSquareFamily #Github #binance #update
245
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#$1.5BInLeveragedCryptoBetsLiquidated
0 views
0 Discussing
2
#KOSPIFalls3.53%BackBelow6000
0 views
4 Discussing
3
#USMidtermElections
92,611 views
1,213 Discussing
4
#StrategySTRCReaches$99.95ForFirstTimeIn165Days
1,347 views
44 Discussing
5
#BinanceWillListPredictPREDICT
16,513 views
457 Discussing
6
#SwitzerlandFirstSpotBitcoinETFExpectedToTradeInNovember
1,021 views
54 Discussing
7
#StrategyReports$21BQ3OperatingProfit
997 views
40 Discussing
8
#TwoAddressesHoldingAbout1.28BUSDTFrozen
6,776 views
240 Discussing
9
#FirstDigitalBlacklistsAttackerAddressHoldingAbout3.4MFDUSD
295 views
13 Discussing
10
#BitcoinDropsBelow$80K
64,385 views
162 Discussing