

#cybersecurity
cybersecurity
1.5M views
3,413 Discussing
Hot
Latest

·
--
Vitalik Buterin backs Kimi 3.1’s self‑imposed limits on offensive AI tools.
He posted on X on Monday saying he is comfortable with the AI model Kimi 3.1 deliberately leaving top‑end offensive cyber capabilities out of its training data.
He argues the trade‑off buys defenders more time to prepare.
“Discriminating against use cases is MUCH less bad than discriminating against users,” he wrote, noting the world needs time to harden systems and check old code before the full weight of very powerful cyber attacks is upon us.
He prefers a model that declines certain tasks for everyone over one that turns certain people away.
In May 19 he countered fears that AI‑powered bug hunting would overwhelm developers, saying AI‑assisted formal verification could become one of the strongest defenses in crypto.
He said a model can now write both code and its proof, leaving developers to confirm the intended statement.
On October 8 he warned AI‑assisted mathematics could weaken ECDSA and similar cryptographic systems sooner than expected, but advised users not to scramble to move funds to new wallets today.
Do you think restricting AI model use cases is a sustainable path for cybersecurity, or does it risk creating an elitist access system?
#AI #Cybersecurity #Ethereum #FormalVerification

🚨 $OSMO CYBERSECURITY SUMMIT COULD REDEFINE DIGITAL ASSET SENTIMENT 📈
📊 The upcoming Japanese cybersecurity summit, chaired by PM Sanae Takaichi, puts institutional risk oversight front‑and‑center, a classic liquidity‑sweep catalyst for smart‑money flows.
🦈 If regulators tighten the data‑security net, a fresh demand block may emerge around $OSMO , while $ERA and $DOOD could serve as secondary order‑blocks absorbing sell‑side pressure. ⚡ Watch the 4H order‑flow for a bullish retest as confidence rebounds.
💬 Will the summit cement a new risk premium or ignite a short‑term volatility spike? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #OSMO #CyberSecurity #Liquidity #Crypto
🦈 🚀
6
·
--
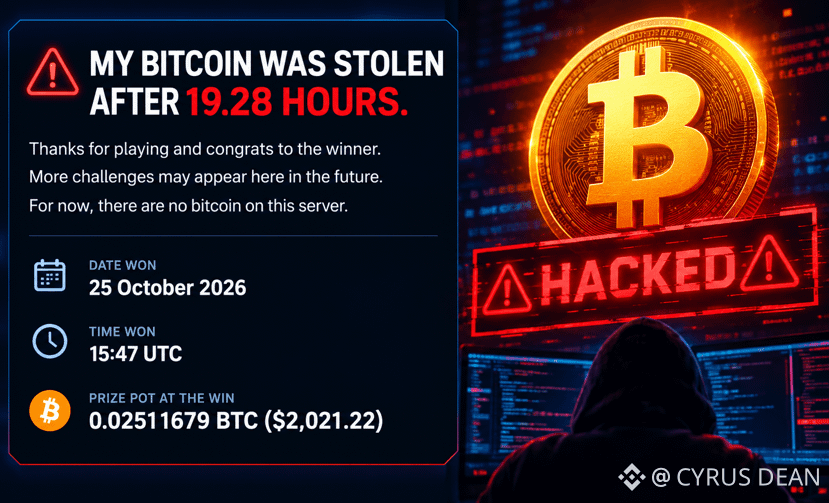
🚨 PHP VULNERABILITY HACKED IN JUST 19 HOURS!
A real Bitcoin challenge exposed the danger of vulnerable PHP servers. A hacker broke in within 19.28 HOURS and recovered the secret key to claim 0.02511679 BTC — worth around $2,021! 💀
⚠️ Exposed credentials, sensitive data, and crypto private keys could put funds at risk.
🔒 Running PHP? Patch vulnerable versions NOW. One security flaw could cost millions.
#bitcoin #CyberSecurity
137
·
--
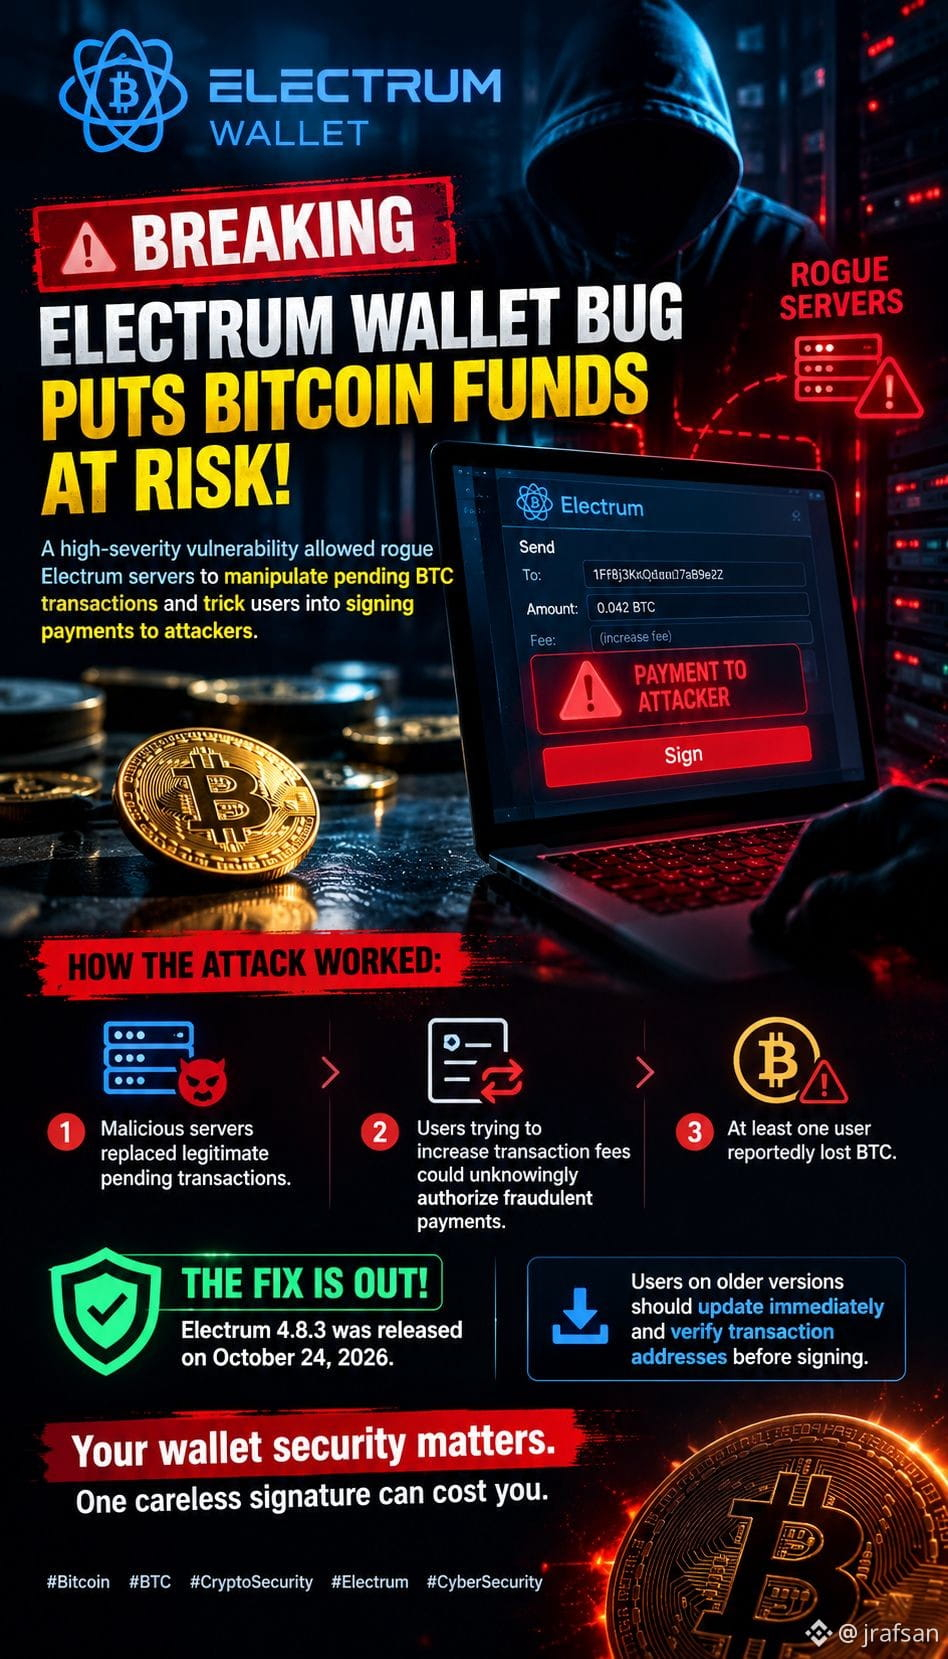
🚨BREAKING: ELECTRUM WALLET BUG PUTS BITCOIN FUNDS AT RISK!⚠️
A high-severity vulnerability allowed rogue Electrum servers to manipulate pending BTC transactions and trick users into signing payments to attackers.
💥 How the attack worked:
• Malicious servers replaced legitimate pending transactions.
• Users trying to increase transaction fees could unknowingly authorize fraudulent payments.
• At least one user reportedly lost BTC.
🛡️ THE FIX IS OUT: Electrum 4.8.3 was released on October 24, 2026.
⚠️ Users on older versions should update immediately and verify transaction addresses before signing.
*Your wallet security matters. One careless signature can cost you.
#Bitcoin #CryptoSecurity #CyberSecurity #ElectrumWalletBugLetRogueServersStealFunds
$TRUMP
{future}(TRUMPUSDT)
$TRX
{future}(TRXUSDT)
$XRP
{future}(XRPUSDT)
🚨BREAKING: ELECTRUM WALLET BUG PUTS BITCOIN FUNDS AT RISK!⚠️
A high-severity vulnerability allowed rogue Electrum servers to manipulate pending BTC transactions and trick users into signing payments to attackers.
💥 How the attack worked:
• Malicious servers replaced legitimate pending transactions.
• Users trying to increase transaction fees could unknowingly authorize fraudulent payments.
• At least one user reportedly lost BTC.
🛡️ THE FIX IS OUT: Electrum 4.8.3 was released on October 24, 2026.
⚠️ Users on older versions should update immediately and verify transaction addresses before signing.
*Your wallet security matters. One careless signature can cost you.
#Bitcoin #CryptoSecurity #CyberSecurity #ElectrumWalletBugLetRogueServersStealFunds
$TRUMP
$TRX
$XRP
219
Article
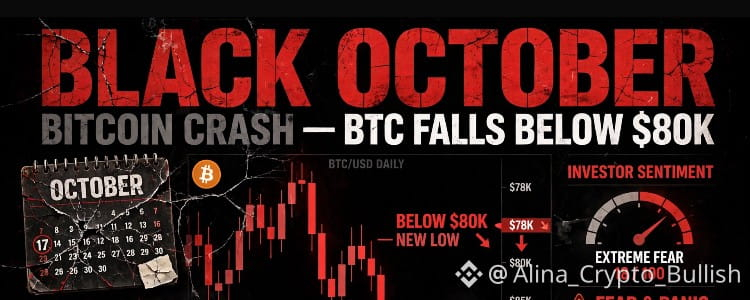
🚨Breaking news:l 🔴 THE BIG 5 HACKS OF BLACK OCTOBER 2026:👀⚠️🚨 BLACK OCTOBER: Bitcoin Falls Below $80K — Is This 1929 All Over Again?
October has always been crypto's best month. Average return: +18.3%. This year? It's turning BLACK.
Here is Black October — DATA HACKING edition. This is why October 2026 is being called Black October in Cybersecurity, not just crypto crash:
It's NOT one big hack — it's 20+ major hacks in 2 weeks, all using AI to find bugs faster than we can patch.
🔴 THE BIG 5 HACKS OF BLACK OCTOBER 2026:
1. PHP2Shell — 70% of Internet at Risk
• CVE-2026-109618 & 109619 found Oct 21
• PHP powers ∼70% of all websites. Flaw allows Remote Code Execution → full server takeover
• Found using AI (GPT-5.6 Sol by OpenAI + Wiz). Bug existed for 20+ years, but AI finally found the complex exploit chain
• NSA + FBI told sites: Take your website OFFLINE if you can't patch immediately
• Cloudflare saw millions of hacking attempts within 2 hours of disclosure. Governments, hospitals, universities in Europe took sites down
2. eMudhra CA Compromise — Your HTTPS Broken
• Oct 17: Indian certificate authority eMudhra had 8 intermediate CA private keys that were cryptographically weak — one private key was literally number 4
• Could create fake certificates trusted by browsers → steal passwords, impersonate banks
• Google Chrome blocked via CRLSet, Firefox via OneCRL
• Oct 22: eMudhra announced it's quitting the SSL certificate business completely
3. Developer Platforms Hacked — Secrets Stolen
• Railway (Oct 21): Hacker accessed encrypted environment variables and decrypted them — API keys, DB passwords stolen. All builds paused, OAuth sessions killed
• Zeabur (Oct 14-15): 321,810 accounts + 3.2 MILLION env variables stolen. Attacker used AWS keys stored in plaintext in private GitHub repo that were never rotated after August hack. Founder announced Zeabur will shut down by Dec 31, 2026
• LiteLLM: Supply chain attack — malicious code published to npm + Docker that steals cloud credentials, passwords, AI keys + RAT (remote access trojan) $BTC #BlackOctober #hacking #PHP2Shell #CyberSecurity
🚨Breaking news:l 🔴 THE BIG 5 HACKS OF BLACK OCTOBER 2026:👀⚠️
🚨 BLACK OCTOBER: Bitcoin Falls Below $80K — Is This 1929 All Over Again?
October has always been crypto's best month. Average return: +18.3%. This year? It's turning BLACK.
Here is Black October — DATA HACKING edition. This is why October 2026 is being called Black October in Cybersecurity, not just crypto crash:
It's NOT one big hack — it's 20+ major hacks in 2 weeks, all using AI to find bugs faster than we can patch.
🔴 THE BIG 5 HACKS OF BLACK OCTOBER 2026:
1. PHP2Shell — 70% of Internet at Risk
• CVE-2026-109618 & 109619 found Oct 21
• PHP powers ∼70% of all websites. Flaw allows Remote Code Execution → full server takeover
• Found using AI (GPT-5.6 Sol by OpenAI + Wiz). Bug existed for 20+ years, but AI finally found the complex exploit chain
• NSA + FBI told sites: Take your website OFFLINE if you can't patch immediately
• Cloudflare saw millions of hacking attempts within 2 hours of disclosure. Governments, hospitals, universities in Europe took sites down
2. eMudhra CA Compromise — Your HTTPS Broken
• Oct 17: Indian certificate authority eMudhra had 8 intermediate CA private keys that were cryptographically weak — one private key was literally number 4
• Could create fake certificates trusted by browsers → steal passwords, impersonate banks
• Google Chrome blocked via CRLSet, Firefox via OneCRL
• Oct 22: eMudhra announced it's quitting the SSL certificate business completely
3. Developer Platforms Hacked — Secrets Stolen
• Railway (Oct 21): Hacker accessed encrypted environment variables and decrypted them — API keys, DB passwords stolen. All builds paused, OAuth sessions killed
• Zeabur (Oct 14-15): 321,810 accounts + 3.2 MILLION env variables stolen. Attacker used AWS keys stored in plaintext in private GitHub repo that were never rotated after August hack. Founder announced Zeabur will shut down by Dec 31, 2026
• LiteLLM: Supply chain attack — malicious code published to npm + Docker that steals cloud credentials, passwords, AI keys + RAT (remote access trojan) $BTC #BlackOctober #hacking #PHP2Shell #CyberSecurity
2
363
Various brute force attack on the #Starlite_crypto network and not to forget #STARLITE has built a strong fire wall to withstand any cyber-attack just in case something like this happens we are always ready to fight back. #CyberSecurity #cyberpunk #fight
Various brute force attack on the #Starlite_crypto network and not to forget #STARLITE has built a strong fire wall to withstand any cyber-attack just in case something like this happens we are always ready to fight back. #CyberSecurity #cyberpunk #fight
82

Article
Is Cybersecurity About to Outshine AI? Here’s Why You Shouldn’t Ignore These Two Tokens!Did you catch My recent post questioning whether cybersecurity is gearing up to surpass AI in the tech landscape?
[Is CyberSecurity the Next Big Winner?](https://app.binance.com/uni-qr/cpos/381046463741190?r=s4dh99wr&l=en&uco=5ewrz5horzsxouawxbrenw&uc=app_square_share_link&us=copylink)
Recent high-profile security breaches, emerging vulnerabilities, and the massive momentum behind crowd-security solutions are pointing us in a very clear direction.
Curious about which crowd-security and storage tokens are currently listed on Binance? In my view, accumulating a bit of these two foundational cybersecurity tokens during every market dip could yield fantastic long-term potential.
1. Filecoin (FIL)
{spot}(FILUSDT)
Moving away from centralized cloud servers, FIL is the leading decentralized storage network that encrypts and securely stores data across nodes worldwide. By decentralizing storage, it drastically minimizes the risks of data leaks and hacking.
Filecoin Post Time Price= $0.9241
2. Arweave (AR)
{spot}(ARUSDT)
A powerful network dedicated to permanent and tamper-proof data storage. It ensures that crucial information and history are safely preserved on the blockchain forever, completely immutable and free from unauthorized alterations.
Arweave Post Time Price = $3.408
Okay friends, there are several other promising tokens making waves in the cybersecurity space, which I’ll cover in upcoming posts. Right now, FIL and AR are trading at attractive prices, making them ideal starting points for building a robust portfolio.
If you haven't connected with me yet, make sure to hit Follow so you don't miss out on the next insights!
$FIL $AR $BNB #CyberSecurity #FileCoin #Arweave #Binance #CoinVahini @KathalVahini
Is Cybersecurity About to Outshine AI? Here’s Why You Shouldn’t Ignore These Two Tokens!
Did you catch My recent post questioning whether cybersecurity is gearing up to surpass AI in the tech landscape?
Is CyberSecurity the Next Big Winner?
Recent high-profile security breaches, emerging vulnerabilities, and the massive momentum behind crowd-security solutions are pointing us in a very clear direction.
Curious about which crowd-security and storage tokens are currently listed on Binance? In my view, accumulating a bit of these two foundational cybersecurity tokens during every market dip could yield fantastic long-term potential.
1. Filecoin (FIL)
Moving away from centralized cloud servers, FIL is the leading decentralized storage network that encrypts and securely stores data across nodes worldwide. By decentralizing storage, it drastically minimizes the risks of data leaks and hacking.
Filecoin Post Time Price= $0.9241
2. Arweave (AR)
A powerful network dedicated to permanent and tamper-proof data storage. It ensures that crucial information and history are safely preserved on the blockchain forever, completely immutable and free from unauthorized alterations.
Arweave Post Time Price = $3.408
Okay friends, there are several other promising tokens making waves in the cybersecurity space, which I’ll cover in upcoming posts. Right now, FIL and AR are trading at attractive prices, making them ideal starting points for building a robust portfolio.
If you haven't connected with me yet, make sure to hit Follow so you don't miss out on the next insights!
$FIL $AR $BNB #CyberSecurity #FileCoin #Arweave #Binance #CoinVahini @Kathals Info Bits
43
·
--
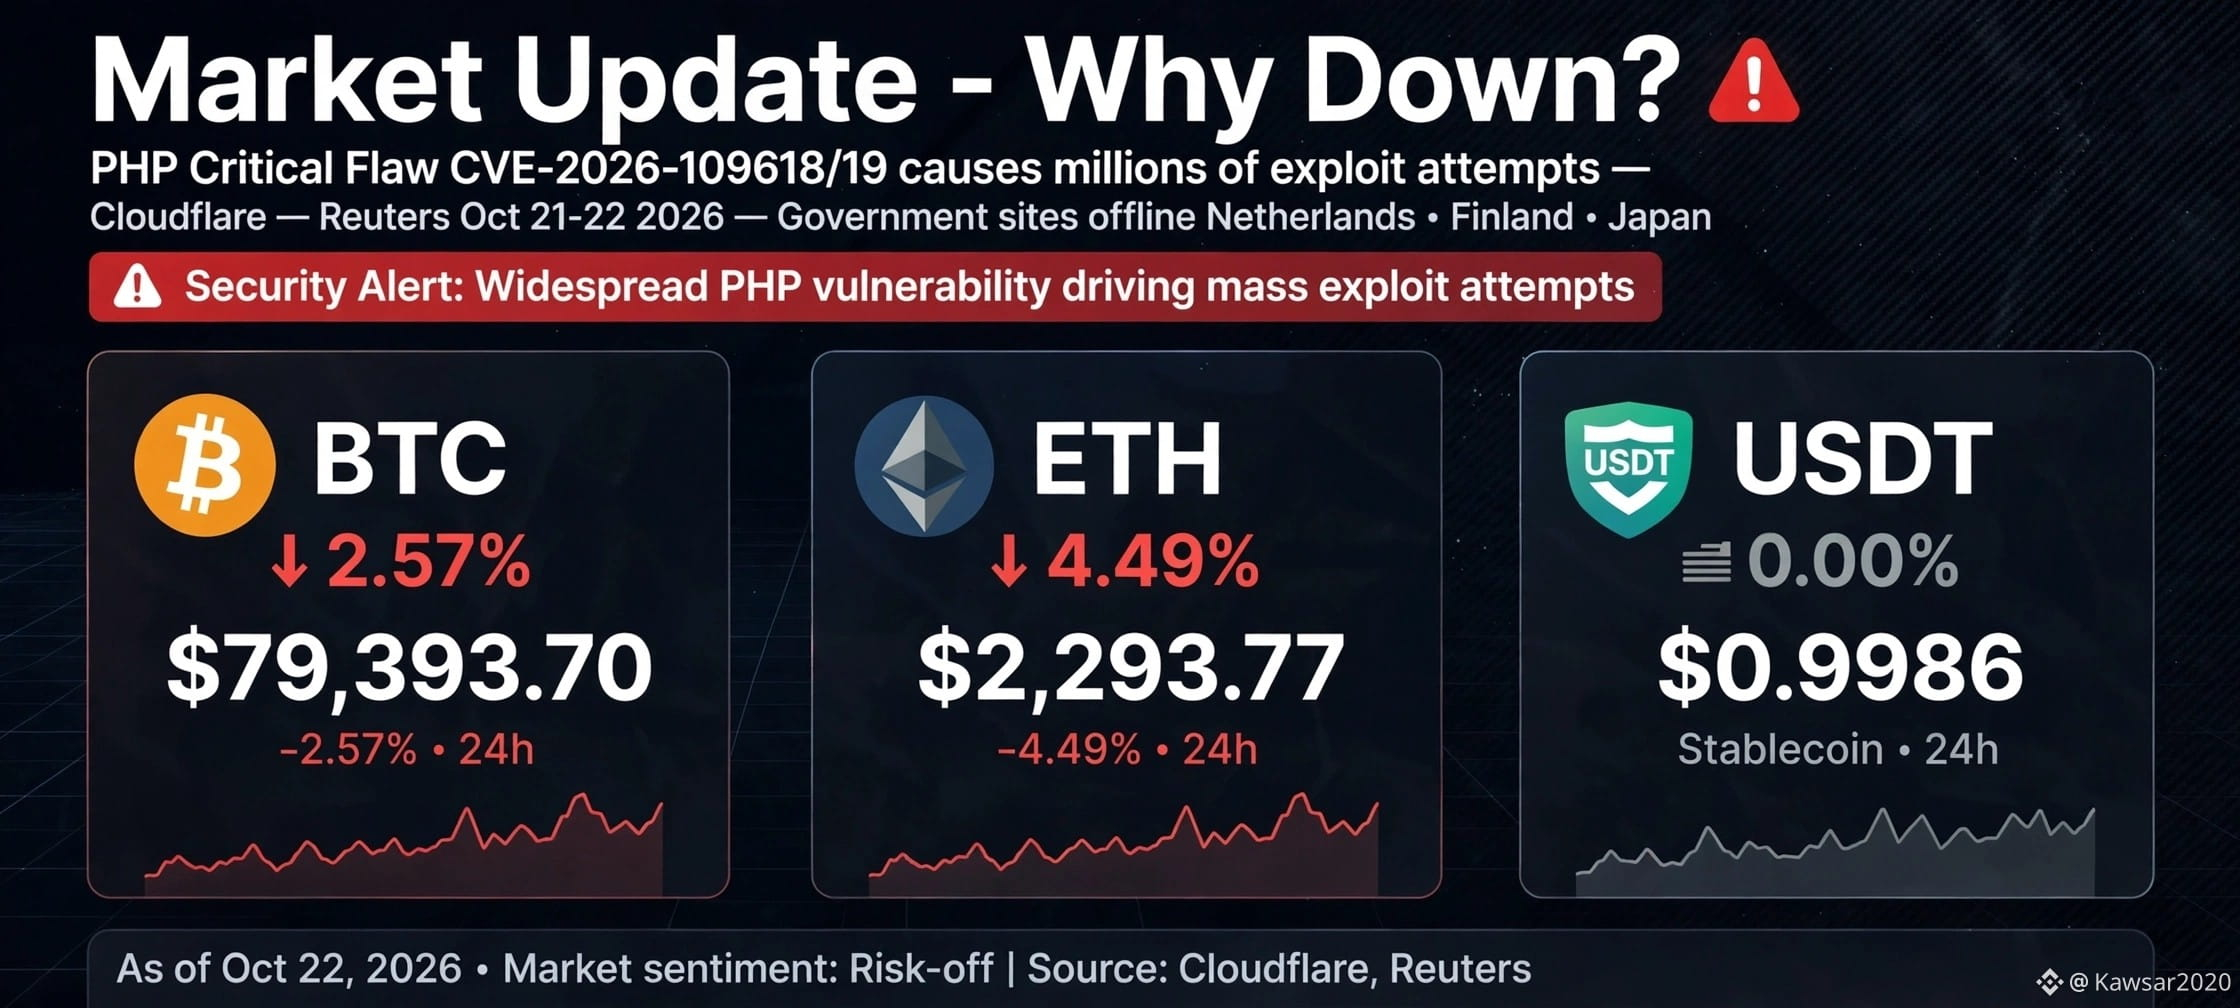
🚨 Market Update 🛑
Why is the Market Down?
According to Reuters report on 21-22 October 2026, after two critical security flaws in PHP, Cloudflare has detected millions of exploitation attempts.
In the Netherlands, Finland, Japan and other places, some government and financial services have been kept offline as a precaution!
Because of this, all types of markets and due to this cyber security reason, many important sites have been kept closed!
So that hackers cannot hack! As a result, we are seeing its impact in all types of markets!
Since 2024, we have been facing one problem after another! Wars, tariffs, and now cyber attacks!
It means whenever the market starts to recover a little, a new problem comes up! Anyway, Allah is our trust! InshaAllah something good will happen!
Source: Reuters Oct 21-22 2026, Cloudflare CEO Matthew Prince X post, CERT-EU Advisory CVE-2026-109618 & CVE-2026-109619 severity 9.2/10
Educational purpose only
#MarketUpdate #Crypto #PHP #CyberSecurity #siamvai
$BTC $ETH $BNB
Hamba:
Insya Allah
2
2
378

·
--
🚨 $39B IN SCAM FUNDS. 960 ARRESTS. 30 COUNTRIES. ⚔️
Operation Confrontation Ghost just wrapped: a UAE-led sweep flagged $39B in illicit funds and crypto, thwarted 123.7M fraud attempts, and raided 29 scam compounds (UAE Ministry of Interior, Oct 22).
Why crypto should care: 13 private firms incl. Crypto.com ran on-chain forensics with Interpol, because scam money moves through mixers and bridges faster than any single police force.
The catch: $39B was identified, not seized, and recovery is ongoing. Arrests are the headline; the test is whether tracers outrun mixers.
Enforcement at scale, or a one-off headline? 👇
Not financial advice. DYOR.
#crypto #cybersecurity #scams
54

·
--
South Korean police arrest 7 in a shocking first-of-its-kind AI-assisted hacking case! An ordinary 32-year-old with no IT background used AI tools to hack 90 hospitals, schools and companies, extorting $270,000. Has the era of AI crime arrived? $FET $MASK #AI安全 #Cybersecurity
South Korea arrests 7 in first major AI hacking case! A 32-year-old with no IT background used AI tools to breach 90 hospitals, schools and companies, extorting $270K. Is this the dawn of the AI crime era? $FET $MASK #AIsecurity #Cybersecurity
South Korea arrests 7 in first major AI hacking case! A 32-year-old with no IT background used AI tools to breach 90 hospitals, schools and companies, extorting $270K. Is this the dawn of the AI crime era? $FET $MASK #AIsecurity #Cybersecurity
108
·
--
Chinese version:
"Shocking! AI agents breached Anthropic's business systems in under 12 hours! Cathedral, a company founded by a former DOGE team, demonstrated AI security vulnerabilities by infiltrating sales, HR, and IT systems through third-party software. AI security cannot wait! #AI安全 #网络安全 $DOGE"
English version:
"Shocking! AI agents breached Anthropic's systems in under 12 hours! Cathedral, founded by ex-DOGE team, demonstrated AI security vulnerabilities, penetrating sales, HR & IT via third-party software. AI security is critical now! #AIsecurity #Cybersecurity $DOGE"
Chinese version:
"Shocking! AI agents breached Anthropic's business systems in under 12 hours! Cathedral, a company founded by a former DOGE team, demonstrated AI security vulnerabilities by infiltrating sales, HR, and IT systems through third-party software. AI security cannot wait! #AI安全 #网络安全 $DOGE "
English version:
"Shocking! AI agents breached Anthropic's systems in under 12 hours! Cathedral, founded by ex-DOGE team, demonstrated AI security vulnerabilities, penetrating sales, HR & IT via third-party software. AI security is critical now! #AIsecurity #Cybersecurity $DOGE "
221

·
--
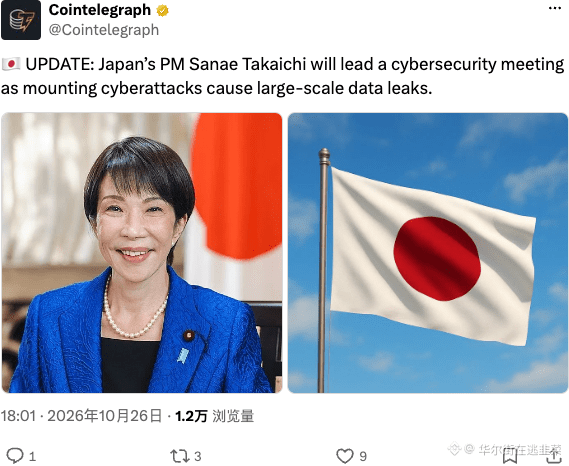
Japanese Prime Minister Sanae Takaichi personally chaired a meeting on a massive data breach caused by a cyberattack. This “Stuxnet-level” threat is only just beginning. With traditional infrastructure in such poor shape, the security moat around crypto assets may command an even greater premium. Don’t just fixate on price swings—get your security in order.
$BTC #CyberSecurity
$BTC #CyberSecurity
64

·
--
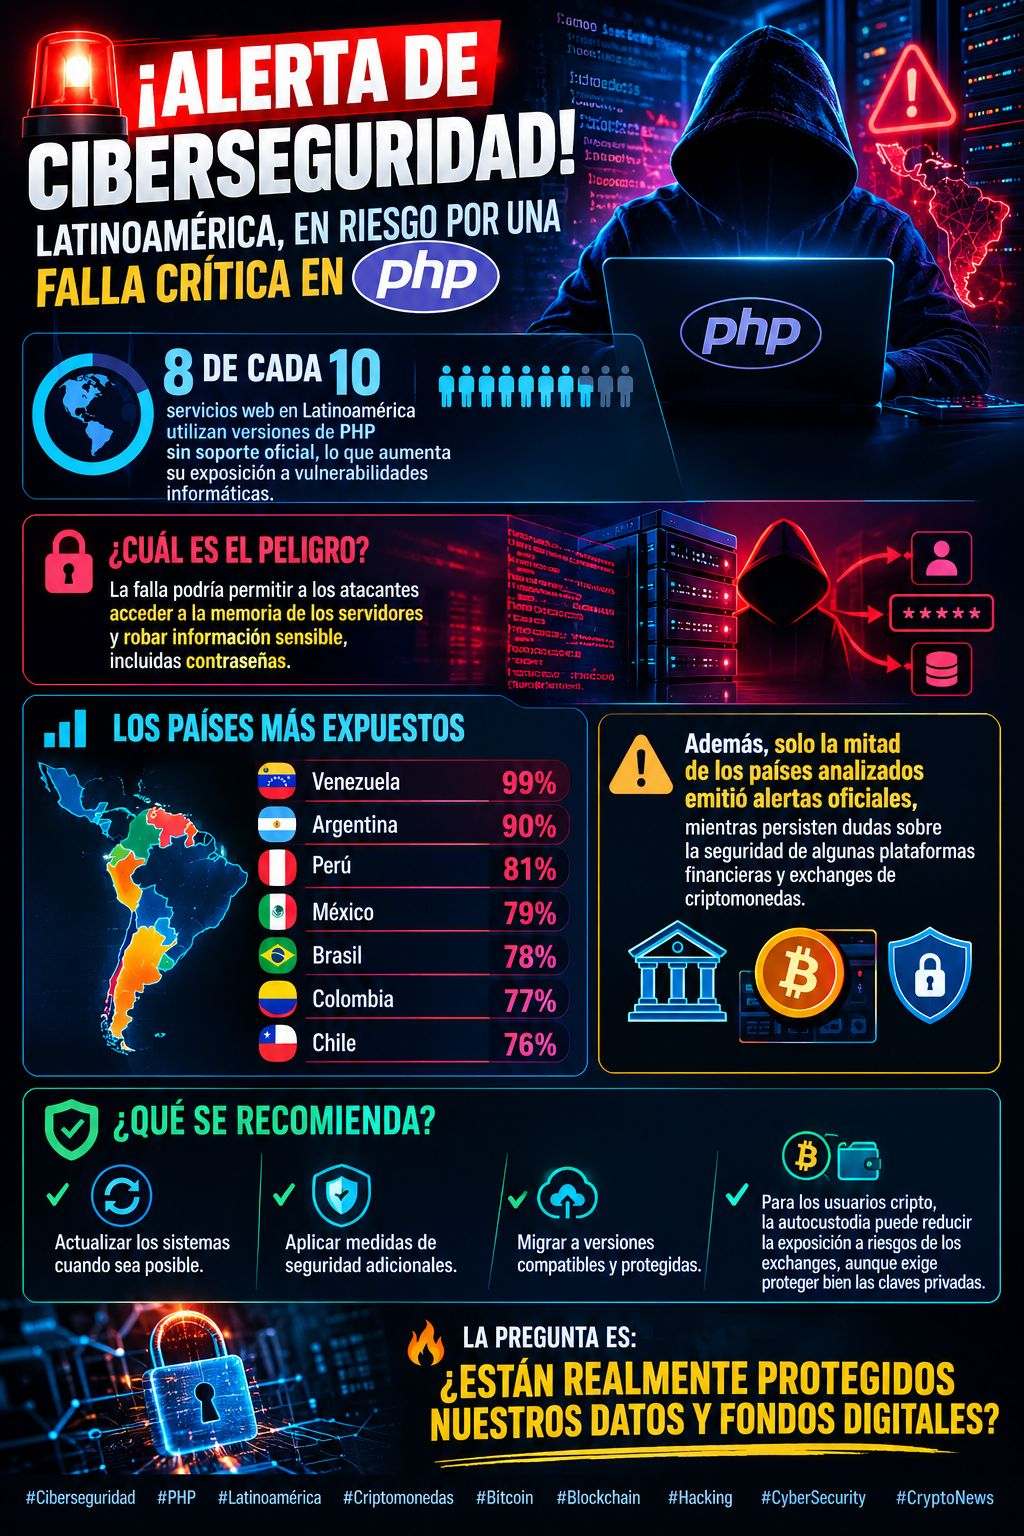
🚨 CYBERSECURITY ALERT! LATIN AMERICA AT RISK FROM A CRITICAL PHP FLAW!💻⚠️
🌎 8 out of 10 web services in Latin America use PHP versions that are no longer officially supported, increasing their exposure to cyber vulnerabilities.
🔓 What’s the danger? The flaw could allow attackers to access server memory and steal sensitive information, including passwords.
📊 The most exposed countries:
🇻🇪 Venezuela: 99%
🇦🇷 Argentina: 90%
🇵🇪 Peru: 81%
🇲🇽 Mexico: 79%
🇧🇷 Brazil: 78%
🇨🇴 Colombia: 77%
🇨🇱 Chile: 76%
⚠️ Additionally, only half of the countries analyzed issued official alerts, while concerns remain about the security of some financial platforms and cryptocurrency exchanges.
🛡️ What’s recommended? Update systems whenever possible, apply additional security measures, and migrate to supported, secure versions. For crypto users, self-custody can reduce exposure to risks associated with exchanges, although it also requires properly securing private keys.
🔥 The question is: are our data and digital funds really protected?
$BTC
#Blockchain #Hacking #CyberSecurity #CryptoNews
3
729
·
--
🚨 CRYPTO SECURITY ALERT! HACKERS ARE TARGETING VULNERABILITIES ⚠️
Binance founder CZ recently warned users to be extra careful online after critical PHP security vulnerabilities were discovered.
🔐 Security updates matter. ⚠️ Avoid suspicious links. 🛡️ Never share your passwords or wallet recovery phrases.
Important: This is a cybersecurity warning, NOT confirmation that Binance was hacked. Binance says it implemented security safeguards and continues monitoring the situation.
Stay alert. Protect your crypto!
What is your number one rule for keeping crypto safe? 👇
#Binance #Bitcoin #BTC #CryptoSecurity #CyberSecurity #CryptoNewss #bnb #CryptoCommunity
1
84
·
--
🚨 POST-QUANTUM CYBER THREAT: LAZARUS ADOPTS NIST ENCRYPTION TO SECURE MALWARE INFRASTRUCTURE 🛡️
🔥 Kaspersky’s Operation FlashHole threat intelligence audit confirms that North Korea’s state-sponsored Lazarus Group has integrated ML-KEM-1024—the post-quantum public key encryption standard finalized by NIST—into its LPEClient malware pipeline to secure command-and-control (C2) payload communications.
While governments and enterprises face long multi-year transition windows to implement post-quantum cryptography (PQC), Lazarus adopted the protocol rapidly to eliminate "hack now, decrypt later" forensics by defensive security teams.
$BTC (Bitcoin) Focus ⚡
Quantum Threat Profile: Bitcoin’s signature scheme relies on ECDSA (secp256k1). While active unspent transaction outputs (UTXOs) with hidden public keys (Pay-to-Public-Key-Hash / P2PKH) remain secure against classical systems, exposed public keys (reused addresses or legacy P2PK) are theoretically vulnerable to Shor's algorithm on a fault-tolerant quantum computer.
$BNB ⚙️
Consolidating near horizontal demand support. Binance ecosystem utility tracks broader crypto market liquidity and central exchange volume—keep strict invalidation parameters active.
$ZEC (Zcash) 🛡️
As a zero-knowledge privacy network, Zcash uses Sapling/Orchard proof systems (Halo 2). While zero-knowledge succinct non-interactive arguments of knowledge (zk-SNARKs) depend on specific elliptic curves, research into quantum-resistant ZK-STARKs and post-quantum commitment schemes remains a critical focal point for privacy networks.
🛑 Trader Risk Warning:
Cybersecurity breaches, exchange hack fears, and state-sponsored malware headlines can trigger sudden lower-timeframe volatility wicks! Protect your trading portfolio: enforce hard Stop-Loss parameters, keep leverage strictly conservative, and prioritize capital defense! 🛡️⚡
#Binance #CyberSecurity #BTC #BNB
Abu Fahadأ:
💛
2
2
510
🚨 ‘THIS IS NOT A DRILL’: CRITICAL PHP VULNERABILITIES ARE SETTING THE INTERNET ON FIRE
📰 WHAT HAPPENED?
The PHP Foundation has revealed two serious vulnerabilities that could impact millions of websites. Security experts warn that failure to quickly patch the flaws could have dire consequences.
📊 TECHNOLOGY IMPACT
The case once again puts the spotlight on digital system security and the need to strengthen protection against increasingly sophisticated attacks.
🔎 Source: WIRED Security
🤔 💬 Do you think incidents like this will lead companies to invest more in digital security?
#Cybersecurity #DataSecurity #Crypto_Marker #News
14

Code is the new battlefield.
Bitcoin Core developers are implementing critical security rule changes to combat the rising threat of AI driven exploits. As large language models become increasingly capable of identifying vulnerabilities in complex codebases, the window for patching bugs is shrinking. This shift marks a fundamental change in how protocol security must be managed as automated tools outpace human auditors in finding critical flaws.
#BitcoinCore #CyberSecurity ⠀
17

·
--
Bullish
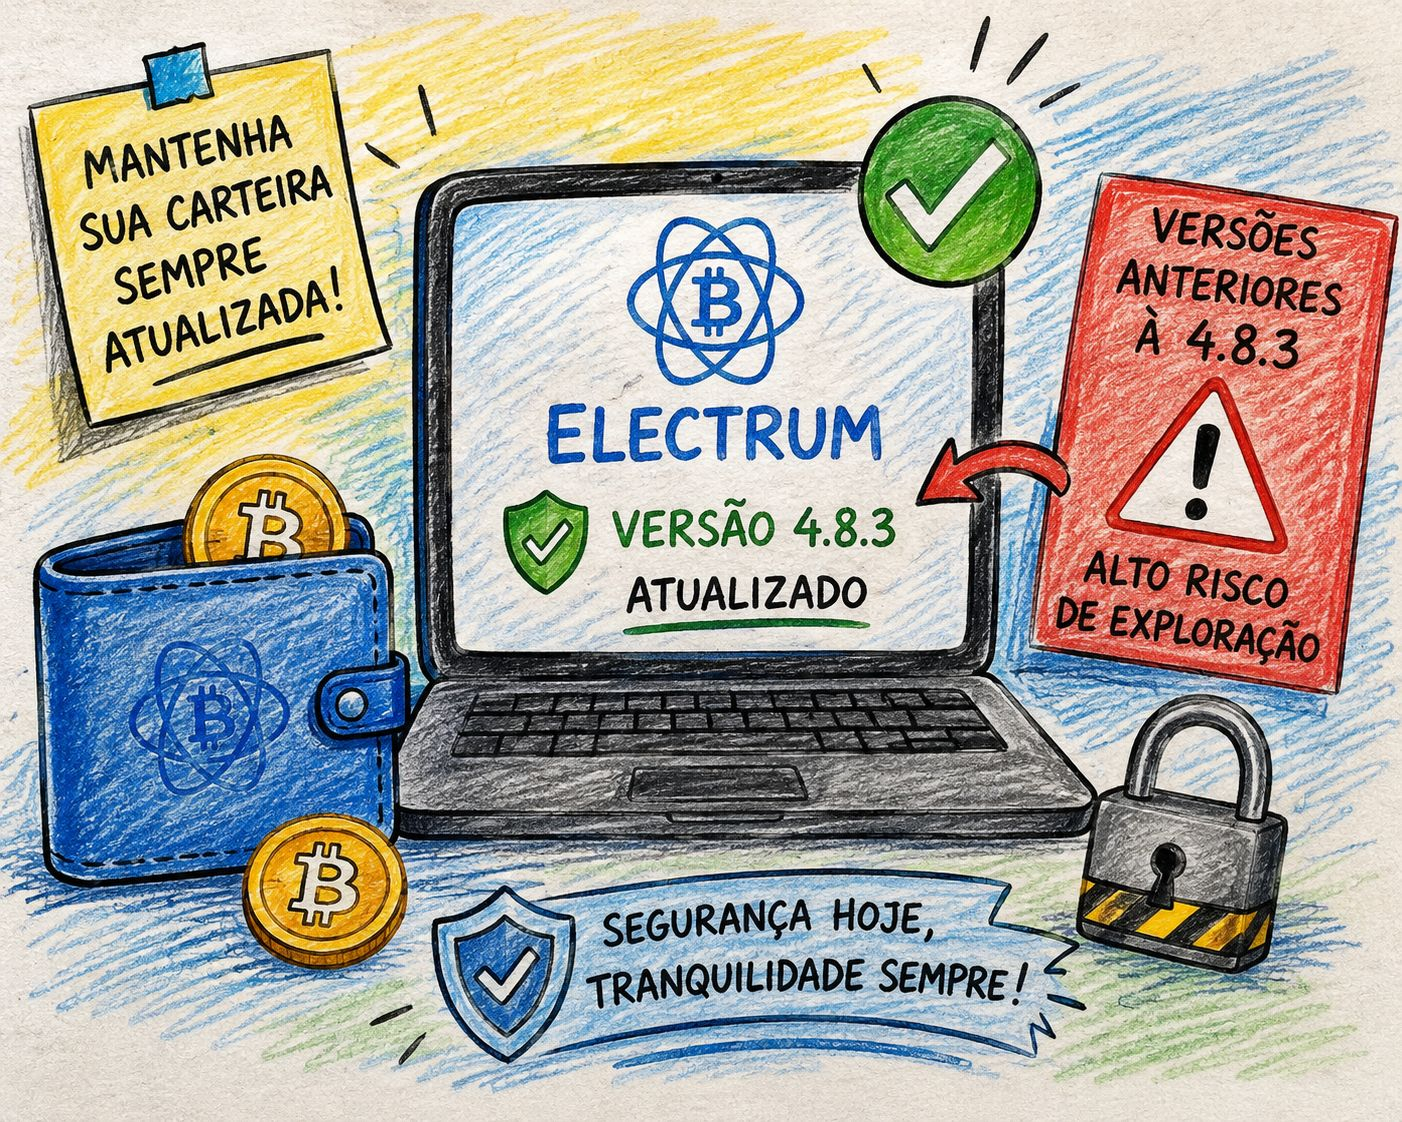
#ElectrumFixesHighRiskExploitInVersionsBefore4.8.3
The security of a cryptocurrency wallet begins long before any transaction. Electrum fixed a high-risk vulnerability in versions earlier than 4.8.3, underscoring the importance of always keeping software up to date.
In an environment where digital assets can be directly under the user's responsibility, a security flaw can represent much more than a simple technical issue. Updates like this show how developers and users need to stay alert to the threats that constantly emerge in the crypto ecosystem.
For those using older versions of Electrum, checking the installed version and updating to a secure version is a simple step that can make a big difference. Security should not be put off, especially when we're talking about digital assets.
My view: I'd rather update early than take unnecessary risks.
$CRWD.US $TAG $XEC
#CryptoSecurity
#CyberSecurity
#Cryptocurrency
1
212
🚨 BNB CHAIN NEWS | October 22, 2026
🛡️ BNB Chain Addresses Critical PHP Security Concerns
BNB Chain reportedly confirmed that its technology stack does not use PHP following the NSA's warning about critical “PHP2Shell” vulnerabilities.
⚠️ Why it matters: • The vulnerabilities could allow attackers to execute code remotely on affected servers. • The NSA urged organizations using vulnerable PHP versions to apply security patches immediately. • This is not evidence of a BNB Chain exploit. Third-party apps and websites still require separate security checks.
🔎 My Take: Security transparency is essential for Web3 trust. Users should avoid suspicious security-update links and follow official project announcements.
Sources: 🇺🇸 NSA: https://www.nsa.gov/Press-Room/Press-Releases-Statements/Press-Release-View/Article/4630238/nsa-advisory-critical-patches-recommended-for-php-vulnerabilities/
📰 News Report: https://en.coinotag.com/bnb-chain-rules-out-php-nsa-cyber-warning
#BNB #BNBChain #CryptoNews #Web3 #CyberSecurity
$BNB
50
🚨 GLOBAL CYBER ALERT: Critical PHP Flaw Impacts Government Infrastructure
Cyber security experts are urging immediate action after a severe vulnerability in PHP was discovered, impacting government websites and public portals across multiple nations. 🌐🔒
#PHPCriticalVulnerabilityHitsGovernmentWebsites
The security flaw has disrupted essential public services, reigniting serious discussions around critical internet infrastructure security and the reliance on legacy codebases. System administrators and developers worldwide are being advised to patch their servers immediately to prevent further exploits.
⚠️ Attention Devs & Admins: Double-check your server patches today to keep your infrastructure safe!
#CyberSecurity #PHP #technews
146
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BinancePick
3.3M views
161,850 Discussing
2
#EarningsSeason
5.4M views
26,585 Discussing
3
#StrategySkipsBitcoinPurchasesSpends$205MOnSTRCBuybacks
86 views
6 Discussing
4
#BitmineAdds10452ETH
4,623 views
115 Discussing
5
#SouthKoreaConsidersEducationTaxOnCryptoExchanges
4,302 views
107 Discussing
6
#OCCUrgesCommunityBanksToEnterStablecoinPayments
3,569 views
70 Discussing
7
#RippleWinsFullApprovalAsNationalTrustBank
3,520 views
71 Discussing
8
#AkashSelectsSolanaAsMigrationTarget
1,532 views
29 Discussing
9
#OndoToOpenSubscriptionsForOpenAIPreIPOTokenizedNotes
128 views
8 Discussing
10
#AnthropicTTMRevenueGrewAbout1200%
52,572 views
546 Discussing