

#zil
zil
616,043 views
4,213 Discussing
Hot
Latest
Article
🚀 $ZIL Ready for Its Next Big Move?🚀 $ZIL Ready for Its Next Big Move? 📈🔥
👀 Zilliqa is on my watchlist! Could the next bullish move be around the corner? 🌙💎
📊 Watching momentum and waiting for confirmation before making a move.
🟢 $ZIL — Potential Breakout Watch! 🚀
#ZIL #LONG #Futures
{spot}(ZILUSDT)
#Altcoins #LowCapGems #CryptoTrading #BinanceSquare
⚠️ Trade smart, manage your risk, and DYOR.
🚀 $ZIL Ready for Its Next Big Move?
🚀 $ZIL Ready for Its Next Big Move? 📈🔥
👀 Zilliqa is on my watchlist! Could the next bullish move be around the corner? 🌙💎
📊 Watching momentum and waiting for confirmation before making a move.
🟢 $ZIL — Potential Breakout Watch! 🚀
#ZIL #LONG #Futures
#Altcoins #LowCapGems #CryptoTrading #BinanceSquare
⚠️ Trade smart, manage your risk, and DYOR.
1
489
·
--
Bullish
🚀 $ZIL — 📈 HIGH TARGETS 🎯
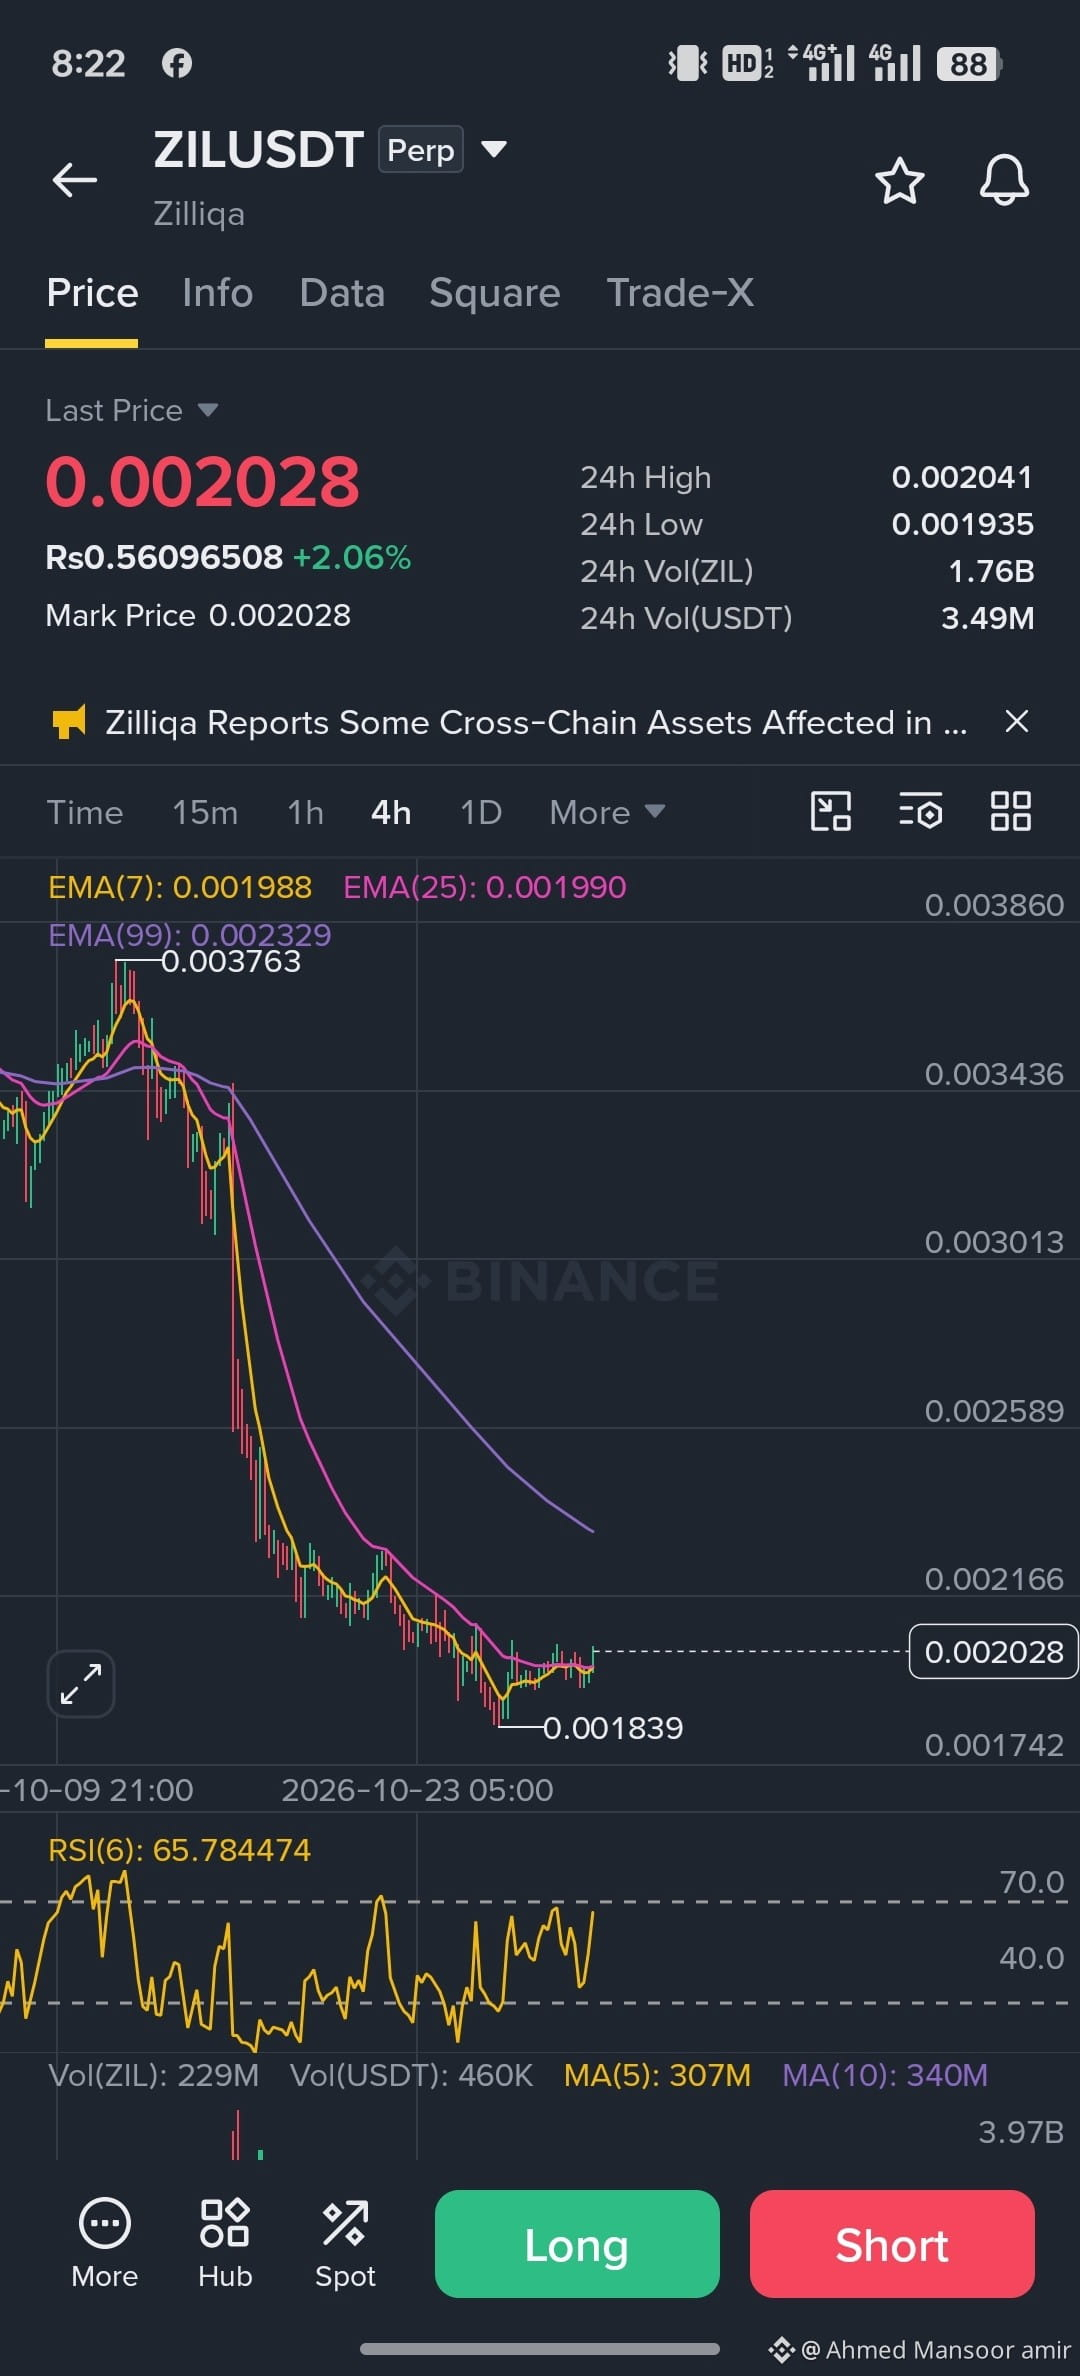
💰 Current Price: $0.002028
📊 TRADE SIGNAL: LONG
🎯 Entry Zone: $0.002000–$0.002030
🔥 Targets:
🥇 TP1: $0.002100
🥈 TP2: $0.002166
🥉 TP3: $0.002300
🚀 TP4: $0.002500
🛑 Stop Loss: $0.001930
📈 Why ZIL?
✅ Price is trading above EMA 7 & EMA 25.
✅ RSI near 66 shows strong short-term momentum.
✅ A breakout above $0.002041 could open the door toward higher resistance levels.
⚠️ Important: The 4H trend remains bearish below EMA 99 at $0.002329. Wait for breakout confirmation and manage risk carefully.
💬 Can ZIL hit $0.0025 next? 🔥
Comment “ZIL 🚀” if you're watching this setup!
#ZIL #Zilliqa #CryptoSignals #BinanceSquare #Altcoins
{spot}(ZILUSDT)
🚀 $ZIL — 📈 HIGH TARGETS 🎯
💰 Current Price: $0.002028
📊 TRADE SIGNAL: LONG
🎯 Entry Zone: $0.002000–$0.002030
🔥 Targets:
🥇 TP1: $0.002100
🥈 TP2: $0.002166
🥉 TP3: $0.002300
🚀 TP4: $0.002500
🛑 Stop Loss: $0.001930
📈 Why ZIL?
✅ Price is trading above EMA 7 & EMA 25.
✅ RSI near 66 shows strong short-term momentum.
✅ A breakout above $0.002041 could open the door toward higher resistance levels.
⚠️ Important: The 4H trend remains bearish below EMA 99 at $0.002329. Wait for breakout confirmation and manage risk carefully.
💬 Can ZIL hit $0.0025 next? 🔥
Comment “ZIL 🚀” if you're watching this setup!
#ZIL #Zilliqa #CryptoSignals #BinanceSquare #Altcoins
FARRUKHJON:
Я просматриваю на эту токен скоро вылетим на космос
1
172
·
--
Bullish
$ZIL L — Blockchain scalability remains an important goal! ⚙️
Ready to Post ✅
*Caption for $ZIL:*
$ZIL — Blockchain scalability remains an important goal! ⚙️
Blockchain scalability remains an important goal
ZILLIQA SCALABILITY • FUTURISTIC • LAYER-1
Scalable • Secure • High Throughput • Sharded Network
Zilliqa
#zil #Zilliqa #Scalability #Binance
$ZIL L — Blockchain scalability remains an important goal! ⚙️
Ready to Post ✅
*Caption for $ZIL :*
$ZIL — Blockchain scalability remains an important goal! ⚙️
Blockchain scalability remains an important goal
ZILLIQA SCALABILITY • FUTURISTIC • LAYER-1
Scalable • Secure • High Throughput • Sharded Network
Zilliqa
#zil #Zilliqa #Scalability #Binance
Ready to Post ✅
*Caption for $ZIL :*
$ZIL — Blockchain scalability remains an important goal! ⚙️
Blockchain scalability remains an important goal
ZILLIQA SCALABILITY • FUTURISTIC • LAYER-1
Scalable • Secure • High Throughput • Sharded Network
Zilliqa
#zil #Zilliqa #Scalability #Binance
6
$ZIL — Zilliqa could attract short-term traders if buyers reclaim resistance; confirm the move with volume and check that support holds afterward.
$RVN — Ravencoin's asset-creation focus remains a project-specific theme; review current network activity and chart liquidity before expecting a trend change.
$CKB — Nervos Network is worth watching for a stronger market structure; a higher low and sustained resistance break would improve the bullish case.
#ZIL #RVN #CKB #CryptoAnalysis #TradingSignals
1
39

·
--
Bullish
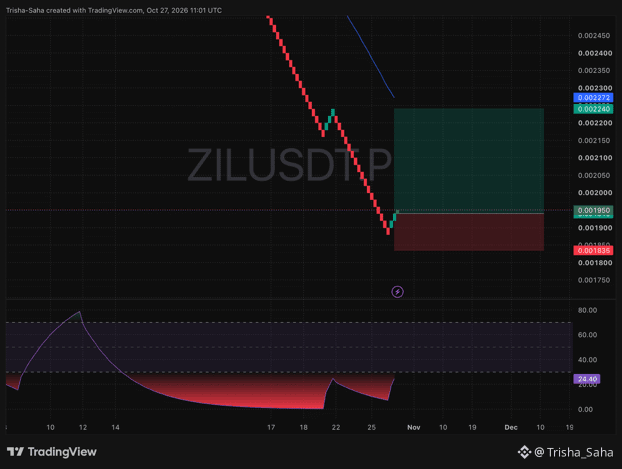
💣 $ZIL just flipped the switch and this relief rally is about to explode! 📈
📍 Trade Setup:
• Entry Zone: $0.001930 –$0.001955
• Stop Loss: $0.001835
• Target: $0.002240
📌 Chart Analysis:
• The heavy sell-off is officially dead as sellers ran out of ammo right below $0.001900.
• Three clean green candles just stepped up in a row while bottom momentum curls sharply upward from the floor (24.40).
• Zero major roadblocks sit between current price and the blue resistance line waiting up at $0.002240.
🛡️ Protect your capital by moving your Stop Loss to Break-Even the second this trade hits +3% to +4% profit.
My position is open and locked in. Are you banking this move with me? Smash a 💰 below! 👇
#ZIL #ZILUSDT #BinanceSquare #CryptoSignals
{future}(ZILUSDT)
💣 $ZIL just flipped the switch and this relief rally is about to explode! 📈
📍 Trade Setup:
• Entry Zone: $0.001930 –$0.001955
• Stop Loss: $0.001835
• Target: $0.002240
📌 Chart Analysis:
• The heavy sell-off is officially dead as sellers ran out of ammo right below $0.001900.
• Three clean green candles just stepped up in a row while bottom momentum curls sharply upward from the floor (24.40).
• Zero major roadblocks sit between current price and the blue resistance line waiting up at $0.002240.
🛡️ Protect your capital by moving your Stop Loss to Break-Even the second this trade hits +3% to +4% profit.
My position is open and locked in. Are you banking this move with me? Smash a 💰 below! 👇
#ZIL #ZILUSDT #BinanceSquare #CryptoSignals
193
·
--
$ZIL +3.97% | $ZAMA +3.46% | $COCOS +3.44%
#ZIL nudged up to $0.00201500, gaining +3.97% on $1.3 M of volume. The 2017‑launched token is seeing modest buying pressure that could signal renewed interest.
#ZAMA rose to $0.0718, up +3.46% with $5.0 M changing hands. The volume surge outpaces its peers, hinting at stronger market participation.
#COCOS climbed to $1.75, +3.44% on $1.5 M of volume. Its steady rise keeps it in the spotlight among the day’s gainers.
👀 Watch if ZAMA’s higher volume can sustain its edge over the more modest flows in ZIL and COCOS.
#Write2Earn #Binance
9
·
--
Zilliqa CEO Alexander Zahnd Resigns; X-Bridge Security Incident Under Investigation
After a security incident, the market generally goes through three stages:
1) Panic: The news hits, and selling pressure surges;
2) Assessment: How much are the losses relative to market cap, and could the stolen funds enter the market?
3) Recovery: The team’s response and progress determine whether confidence can return.
$ZIL latest: 0.002001, 24h +0.2%. Don’t rush to judgment—wait until the second stage becomes clearer.
#ZIL
10

·
--
Just sharing a quick thought—every time I see hacker news, it really makes me uneasy.
“Zilliqa CEO Alexander Zahnd resigns; X-Bridge security incident under investigation”
My own habits: regularly revoke wallet permissions, keep large amounts of assets in separate wallets, and avoid links from unknown sources. Holders of $ZIL should also keep an eye on further developments.
How do you usually manage your wallets?
#ZIL
Just my personal perspective; it may not be accurate, so please take it with a grain of salt.
24

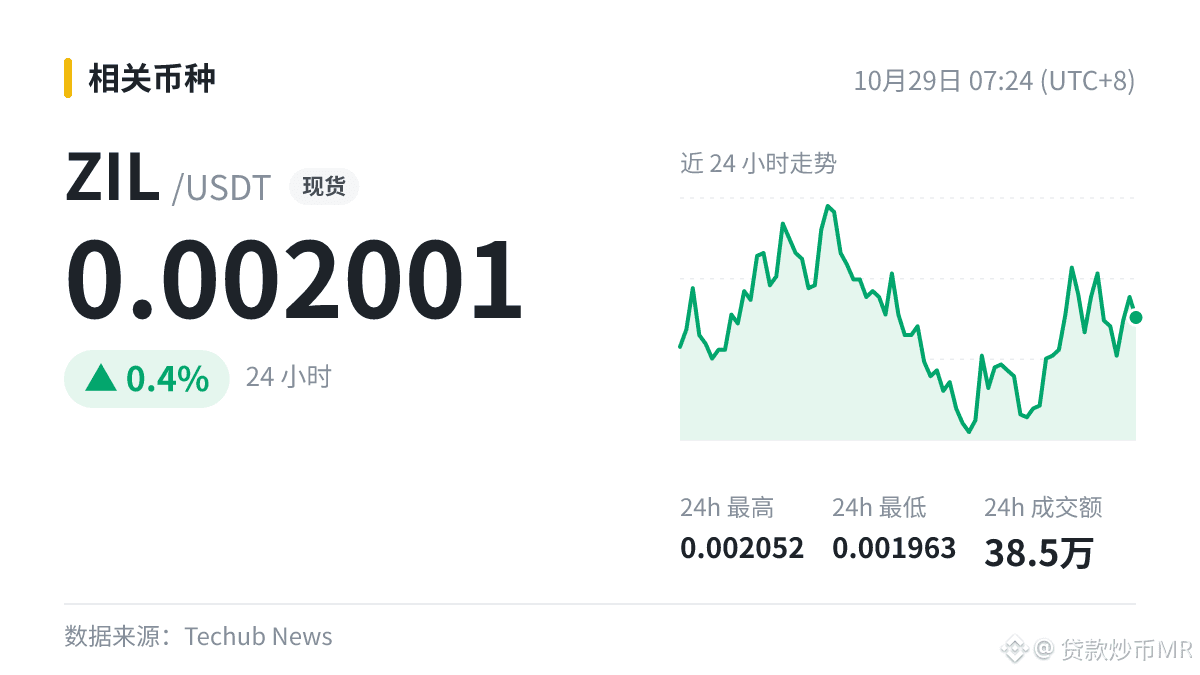
Zilliqa CEO Alexander Zahnd has resigned, and the X-Bridge security incident is under investigation.
When something like this happens, it usually takes time to restore confidence in the projects involved.
Looking at the chart, the upper and lower boundaries of the range are the levels that really matter.
$ZIL latest: 0.001993, 24h: +0.45%.
#ZIL
When something like this happens, it usually takes time to restore confidence in the projects involved.
Looking at the chart, the upper and lower boundaries of the range are the levels that really matter.
$ZIL latest: 0.001993, 24h: +0.45%.
#ZIL
10

📢 Zilliqa CEO Alexander Zahnd resigns; the X-Bridge security incident is under investigation
Three on-chain safety rules: don't click unfamiliar links, regularly revoke approvals, and spread large assets across multiple wallets. Following all three is rarer than perfectly timing the market bottom.
$ZIL is worth keeping an eye on. Asset security always comes first.
#ZIL
Three on-chain safety rules: don't click unfamiliar links, regularly revoke approvals, and spread large assets across multiple wallets. Following all three is rarer than perfectly timing the market bottom.
$ZIL is worth keeping an eye on. Asset security always comes first.
#ZIL
5
·
--
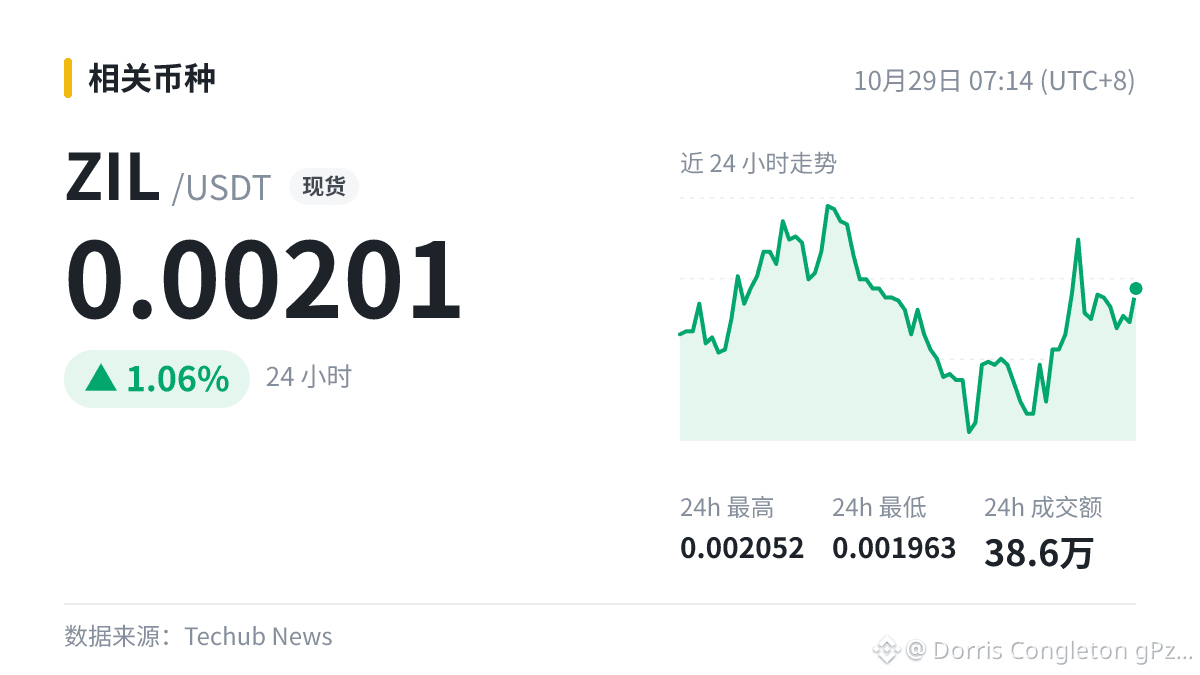
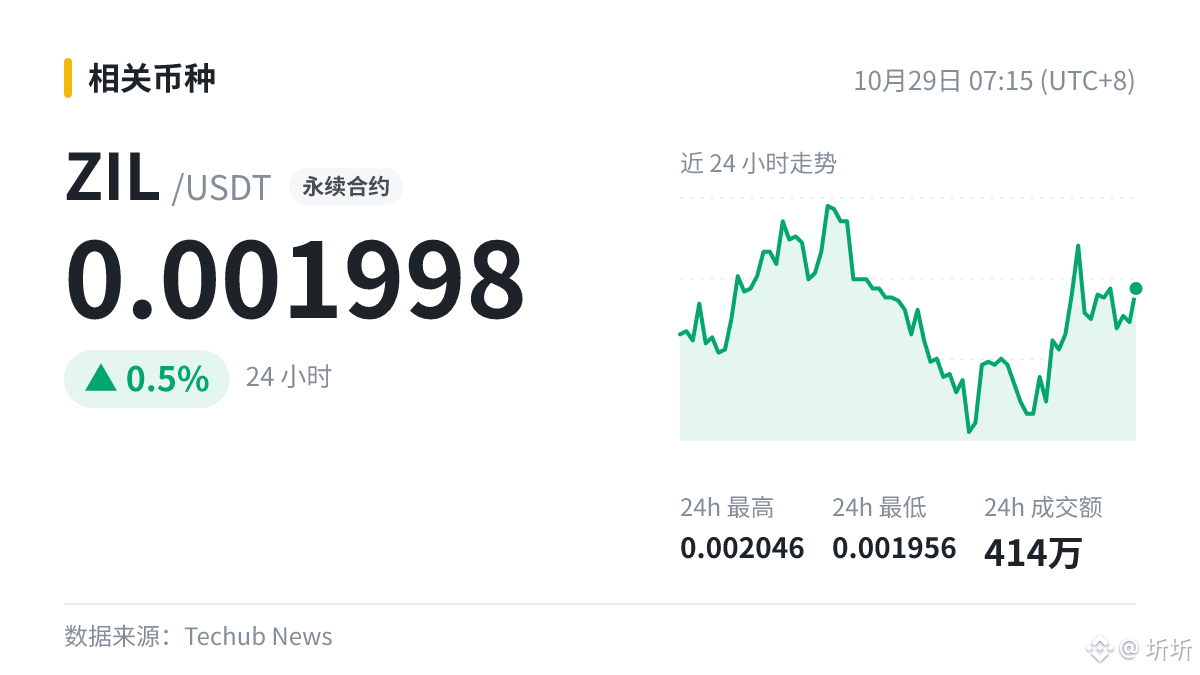
Latest: Zilliqa announced on X that its CEO, Alexander Zahnd, has resigned. The company is currently being managed directly by the board, and no successor has been appointed.
$ZIL is currently trading at 0.001998. Safety first. How do you usually manage your wallets?
#ZIL
Just my personal opinion—take it with a grain of salt; this is not advice.
$ZIL is currently trading at 0.001998. Safety first. How do you usually manage your wallets?
#ZIL
Just my personal opinion—take it with a grain of salt; this is not advice.
10
·
--
Zilliqa CEO Alexander Zahnd resigns, X-Bridge security incident under investigation
Honestly, there’s news every day. What really helps people make fewer mistakes is keeping a steady pace. Amid bearish news, I’m more concerned with whether buyers will step in at the previous low.
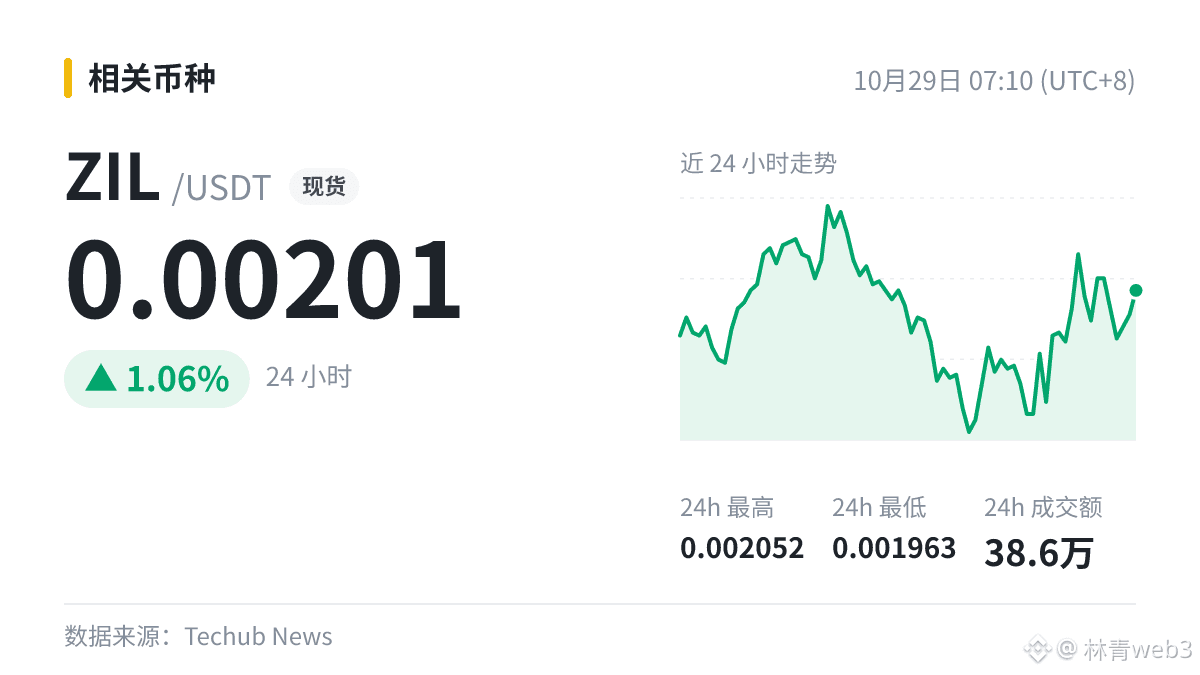
$ZIL 0.00201
#ZIL
Zilliqa CEO Alexander Zahnd resigns, X-Bridge security incident under investigation
Honestly, there’s news every day. What really helps people make fewer mistakes is keeping a steady pace. Amid bearish news, I’m more concerned with whether buyers will step in at the previous low.
$ZIL 0.00201
#ZIL
Honestly, there’s news every day. What really helps people make fewer mistakes is keeping a steady pace. Amid bearish news, I’m more concerned with whether buyers will step in at the previous low.
$ZIL 0.00201
#ZIL
5
·
--
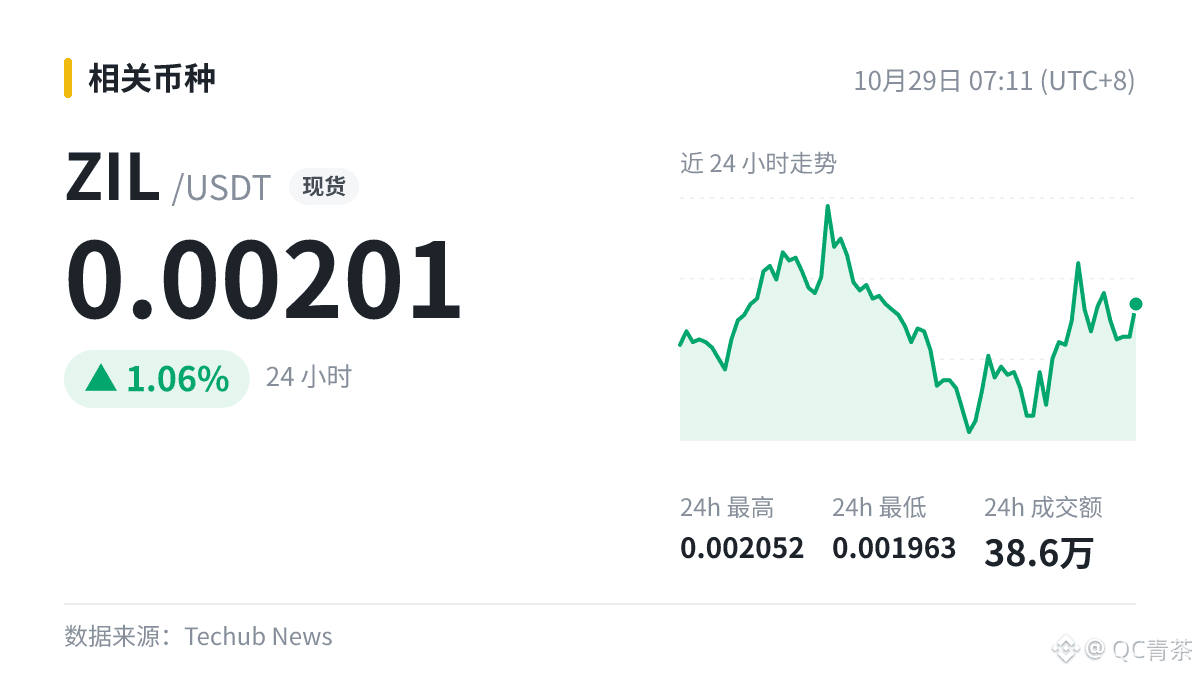
⏰ Zilliqa CEO Alexander Zahnd resigns; X-Bridge security incident under investigation
Whenever I see news like this, I instinctively review my wallet approvals—even though there isn't much in my wallet, it's the principle that counts.
Friends connected to $ZIL , keep an eye on official updates. How often do you check your wallet approvals?
#ZIL
Whenever I see news like this, I instinctively review my wallet approvals—even though there isn't much in my wallet, it's the principle that counts.
Friends connected to $ZIL , keep an eye on official updates. How often do you check your wallet approvals?
#ZIL
72

A proxy contract being compromised and a private key being stolen are two entirely different things, but the market doesn’t seem to be distinguishing between them. In Zilliqa’s case, X-Bridge and the proxy contract were both affected, and the CEO resigned on the same day. Yet ZIL is currently at 0.001994, up 0.60% over 24 hours—that price action suggests the people setting the price still haven’t figured out what was lost.
First, let’s look at the nature of the incident. In an upgradeable contract architecture, a proxy contract holds upgrade permissions, not a private key. That means the attacker may not have gained the ability to “transfer out any amount of money,” but rather the ability to “decide what logic this contract will execute from now on.” These risks differ by an order of magnitude: the former is a one-time loss that can be calculated on-chain; the latter is a persistent backdoor. As long as control hasn’t been transferred, the attacker could theoretically define a new implementation contract at any time, including one with minting logic, a withdrawal whitelist, or balance mapping. So the official claim that the situation is “under control” and the claim that “the attacker has lost access” are not the same thing. There are three signals to look for: whether proxy admin control has been transferred to a new address, whether the new implementation contract has passed an independent audit, and whether X-Bridge restarts with an entirely new contract rather than being restored in place. Until all three are done, the incident is ongoing, not over.
Now let’s look at the leverage side, where there’s more information than in the price. The 4-hour funding rate is just +0.0004%, or roughly 0.44% annualized—basically zero. For a project that has just suffered a dual breach involving its bridge and proxy contract, the perpetual funding rate is somehow positive and close to neutral. That points to one of two things: either existing longs haven’t caught on yet, or there simply isn’t any meaningful leveraged capital in this contract to price the event. Open interest makes that clear: 3 million USDT. With 24-hour trading volume of 4.1M, that level of OI is typical of a thin order book. Thin order books amplify marginal selling pressure. A trade worth a few hundred thousand dollars would be noise in a deep pool, but here it can make a sharp move. So the 24-hour gain of 0.60% shouldn’t be read as “buyers are coming back”; it’s more likely just random movement in low liquidity.
The long-account ratio is 58.9%, a figure worth calling out on its own. A high proportion of long accounts alongside a neutral funding rate and tiny OI usually means small retail long positions are piling up, while professional capital hasn’t entered to take a directional position. This structure is fragile during bad news: if the price breaks down, that 58.9% of positions could turn into concentrated stop-loss selling, with too few buyers on the other side to absorb it. In other words, the current price isn’t being supported by “bullish sentiment”; it’s being supported by “nobody trading.”
Then there’s the CEO’s resignation on the same day. This is often dismissed as gossip, but in a security incident it’s a substantive factor. Fixing a bridge and a proxy contract isn’t as simple as writing a patch. It requires the team to spend weeks restructuring permissions, resetting multisig arrangements, reconciling cross-chain assets, and communicating one by one with exchanges and market makers. These tasks require someone to make decisions and someone to provide external assurances. The CEO’s departure on the same day leaves the question of “who is responsible for restoring trust?” unanswered. Historically, projects dealing with security incidents alongside departures of key figures tend to take longer to recover than projects facing purely technical incidents, because external parties—custodians, LPs, and CEXs—will first wait to see whether governance is stable before deciding whether to continue working with the project.
Finally, here’s the risk I think is easiest to overlook: fixing a vulnerability in an upgradeable contract often requires using upgrade permissions again. In other words, the team will have to use the same permission mechanism—one that has just been shown to be vulnerable—to fix things. If the breach was caused by an insufficient multisig threshold, a signer's device being compromised, or a deployer’s private key being held by a single party, then until the root cause is publicly explained, any announcement that the issue has been “fixed” only tells half the story.
My view: this is a situation to wait for confirmation, not an opportunity to buy the dip. Watch three things—the on-chain record of proxy admin control being transferred, whether the bridge restarts with a new contract, and whether the funding rate and OI show a directional shift. The funding rate is still +0.0004%, which means the market is signaling with real money that, for now, nobody is willing to pay for the assumption that “the recovery was successful.”
Risk warning: with small-cap tokens driven by events like this, slippage in thin order books can easily wipe out all short-term profits. Figure out how much you can afford to lose before thinking about how much you could make.
#ZIL #Crypto
14

·
--
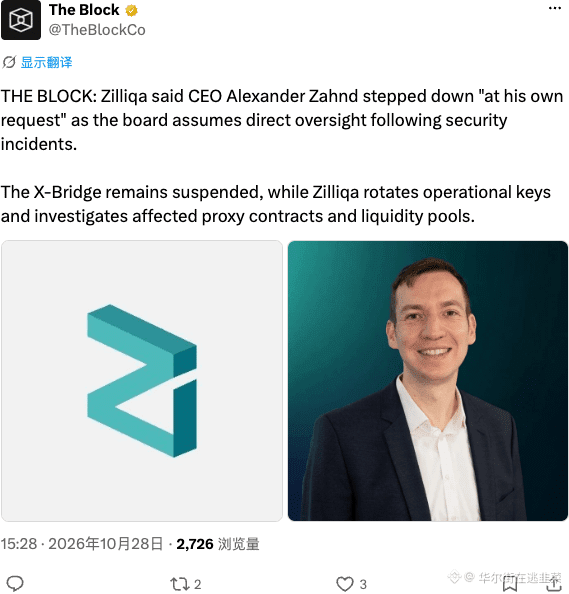
Zilliqa CEO resigns voluntarily; board takes over after a serious security incident. X-Bridge has triggered its circuit breaker, and an urgent investigation into liquidity risks is underway.
The CEO just up and left, and the security incident blew up. X-Bridge was shut down outright, and liquidity looks toast. The board parachuted in to put out the fire, but trust has taken a serious hit. Don’t try to catch a falling knife—the risk is too high.
#Zilliqa #ZIL #Security #Crypto
The CEO just up and left, and the security incident blew up. X-Bridge was shut down outright, and liquidity looks toast. The board parachuted in to put out the fire, but trust has taken a serious hit. Don’t try to catch a falling knife—the risk is too high.
#Zilliqa #ZIL #Security #Crypto
稳态HK:
黑红也是红,加仓
1
447
·
--
Take it easy—here’s the rundown: Zilliqa security incident update: X-Bridge remains paused, and the CEO has stepped down voluntarily.
Regulatory news reads like a final exam syllabus: you’re given the topics, but not told what exactly will be on the test.
$ZIL might be worth keeping an eye on. When was the last time you got carried away?
#ZIL
Regulatory news reads like a final exam syllabus: you’re given the topics, but not told what exactly will be on the test.
$ZIL might be worth keeping an eye on. When was the last time you got carried away?
#ZIL
148
Zilliqa’s X-Bridge just suffered a security breach involving liquidity pools for four types of tokens, including zUSDT and SEED. Did the CEO just resign and run off?
$ZIL is still up 2.08%—the security incident hasn’t shaken it at all. There’s no major sell-off, which could mean the tokens are concentrated in a few hands or retail traders haven’t reacted yet.
If you’re holding $ZIL spot, don’t rush to sell. Wait until the official compensation plan is announced. If you’re trading futures, keep leverage below 3x and set your stop-loss at the previous daily low. Don’t hold on when you should cut your losses.
Want to see if your judgment is right? Spot Trading Tournament S8 is underway—join in and get a feel for how events like this play out in real time.
Do you still have a position in $ZIL ? Reply 1 if you’re holding, or 2 if you’ve already sold everything.
#Write2Earn #BinanceSquare #ZIL #Futures #TradingTournament
9
·
--
Don't draw a conclusion from a single data point; compare across at least a few dimensions.
For example, this item: Zilliqa: cross-chain bridge and proxy contracts compromised, CEO has resigned, $ZIL intraday +2.43%.
On the face of it, these are negative factors. Assess their actual impact proportionately.
#ZIL
For example, this item: Zilliqa: cross-chain bridge and proxy contracts compromised, CEO has resigned, $ZIL intraday +2.43%.
On the face of it, these are negative factors. Assess their actual impact proportionately.
#ZIL
103
·
--
📢 30-second rundown
① Zilliqa security incident update: Some cross-chain assets affected; CEO resigns
② Reported by 5 media outlets, mostly neutral
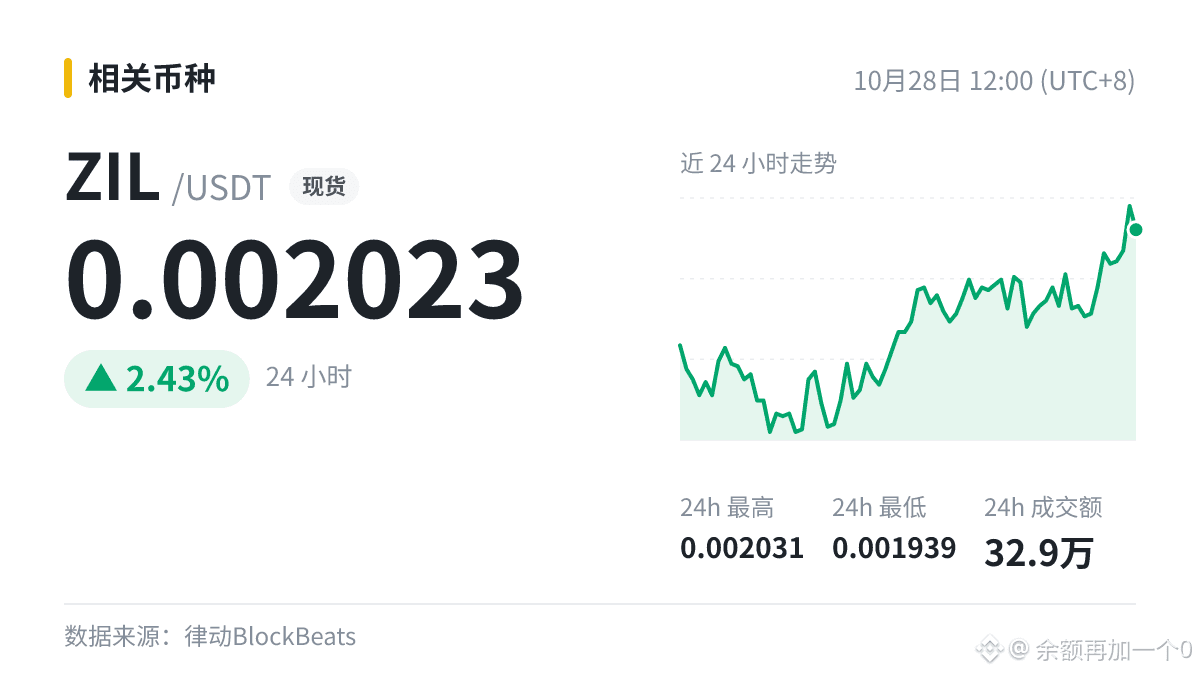
③ $ZIL Current price: 0.002023, 24h +2.43%
#ZIL
Do your own research before making a move.
📢 30-second rundown
① Zilliqa security incident update: Some cross-chain assets affected; CEO resigns
② Reported by 5 media outlets, mostly neutral
③ $ZIL Current price: 0.002023, 24h +2.43%
#ZIL
Do your own research before making a move.
① Zilliqa security incident update: Some cross-chain assets affected; CEO resigns
② Reported by 5 media outlets, mostly neutral
③ $ZIL Current price: 0.002023, 24h +2.43%
#ZIL
Do your own research before making a move.
28

·
--
🆕 Multiple media outlets report: Public blockchain Zilliqa has posted an update on the recent security incident, saying its investigation with an external cybersecurity firm is still ongoing.
$ZIL is worth adding to your watchlist. The headline is just the starting point; the market reaction is the answer. Stay tuned.
#ZIL
$ZIL is worth adding to your watchlist. The headline is just the starting point; the market reaction is the answer. Stay tuned.
#ZIL
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#FedWatch
16.3M views
39,418 Discussing
2
#EarningsSeason
6.4M views
32,112 Discussing
3
#USMidtermElections
43,486 views
631 Discussing
4
#BitcoinDropsBelow$80K
29,346 views
121 Discussing
5
#BoEOpensConsultationOnTokenizedCollateralForClearing
660 views
30 Discussing
6
#BrazilCryptoExchangesMustApplyForLicensesByFriday
33,332 views
506 Discussing
7
#ICEPartnersWithTradeXYZToBringPerpetualContractsToUS
708 views
19 Discussing
8
#SolidusLabsReportsSuspected$170MSpoofingOnHyperliquidOilContracts
1,643 views
28 Discussing
9
#StanDruckenmillerBecomesInvestorInTradeXYZ
25,841 views
440 Discussing
10
#RussiaProposedNonCustodialWalletLimitsExcludeIntlSettlements
2,146 views
41 Discussing