

#phishingawareness
phishingawareness
9,252 views
18 Discussing
Hot
Latest


·
--
Phishing attacks are getting smarter 🎣
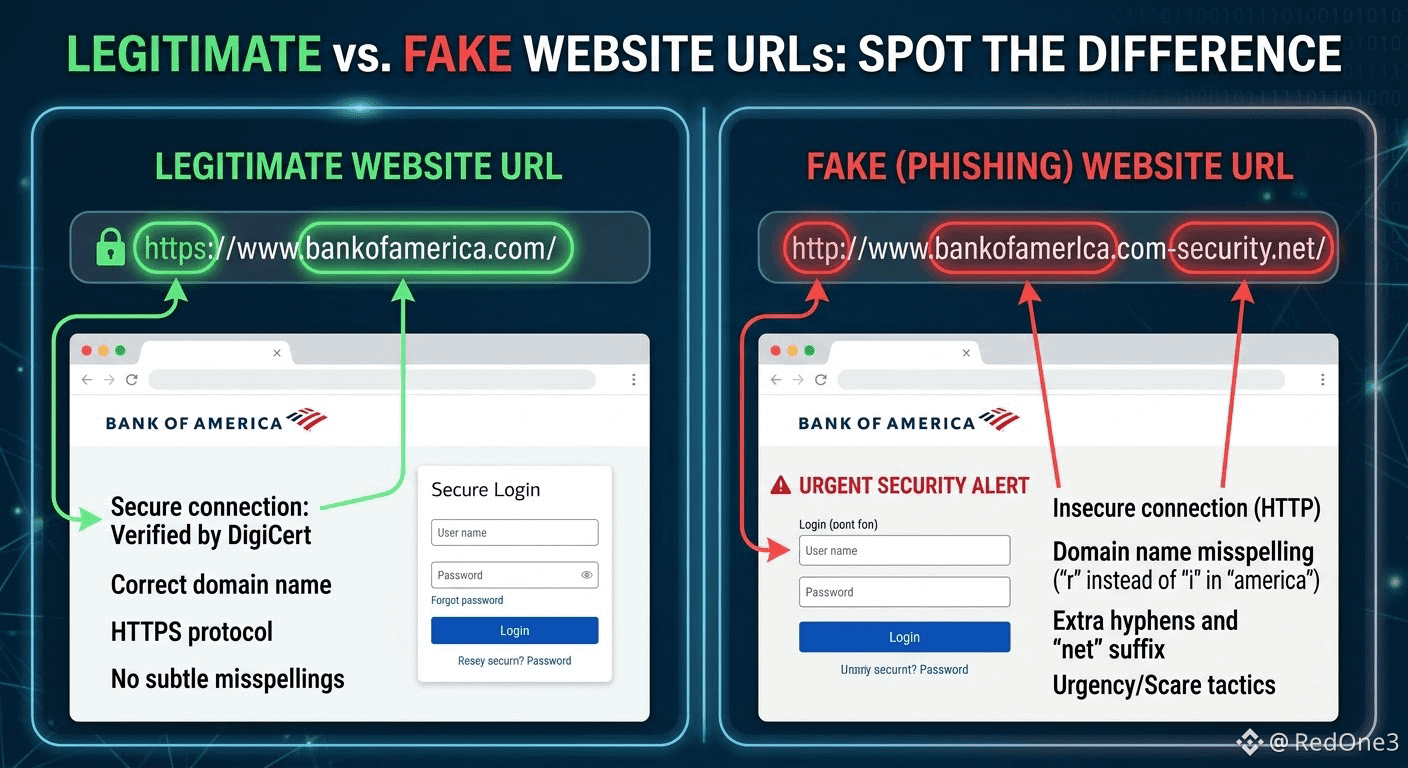
Scammers create 99% identical copies of legitimate websites, changing only 1-2 letters in the URL 👁️
Always verify the exact URL before entering credentials - copy-paste from official channels only 🔍
#KeepItLegit
#PhishingAwareness #CyberSecurity #StaySafe .
Phishing attacks are getting smarter 🎣
Scammers create 99% identical copies of legitimate websites, changing only 1-2 letters in the URL 👁️
Always verify the exact URL before entering credentials - copy-paste from official channels only 🔍
#KeepItLegit
#PhishingAwareness #CyberSecurity #StaySafe .
Scammers create 99% identical copies of legitimate websites, changing only 1-2 letters in the URL 👁️
Always verify the exact URL before entering credentials - copy-paste from official channels only 🔍
#KeepItLegit
#PhishingAwareness #CyberSecurity #StaySafe .
1
446
·
--
🚨 Red Flags Every Crypto Trader Must Spot (Don't Get Phished!)
Security in Web3 is just as important as reading the charts. Scammers are constantly refining their tactics to target your wallet and account credentials.
Here are the top red flags to watch out for before clicking any link:
🔍 1. Fake Domains & Subdomain Tricks
Always inspect the URL carefully. Scammers use subtle typos (b1nance.com) or dangerous subdomains (binance.com.verify-login.xyz) to impersonate official platforms.
⏳ 2. Artificial Urgency
"Your account will be frozen in 2 hours!" Pressure tactics are designed to make you panic and skip double-checking. Real security alerts give you clear instructions, not panic timers.
🔑 3. Unsolicited Requests for Sensitive Data
No legitimate platform or support staff will ever ask for your private keys, seed phrase, 2FA code, or password. Period.
📩 4. Direct Messages from "Support"
If someone DMs you first claiming to be official support or a community manager,,,it's a scam. Official teams do not initiate direct messages to solve account issues.
🔒 Quick Safety Rule: Never click links in unverified emails or DMs. Type the official URL directly into your browser or use your own bookmarks.
Stay sharp and protect your funds! 🛡️
#DYOR #SAFU
#CryptoSecurity #StaySafe #PhishingAwareness .
213
Security and Best Practices in Crypto
🔒 Crypto Security: 4 essential reflexes to protect your assets
The security of your funds is the foundation of your journey in the Web3 and Crypto market.
🛡️ Golden rules:
Enable two-factor authentication (2FA): Prefer an authentication app (Google Authenticator, Passkeys) rather than SMS.
Verify addresses and URLs: Save Binance’s official URL in your bookmarks to avoid phishing attempts.
Beware of suspicious links: Never click on unsolicited links received via private message.
Whitelist your withdrawal addresses: Set up the Withdrawal Whitelist feature to allow withdrawals only to your trusted addresses.
Prudence and vigilance are your best security guarantees.
#SecurityFirst #CryptoSafety #PhishingAwareness #2FA #Binance @Square-Creator-ab1773406
Security and Best Practices in Crypto
🔒 Crypto Security: 4 essential reflexes to protect your assets
The security of your funds is the foundation of your journey in the Web3 and Crypto market.
🛡️ Golden rules:
Enable two-factor authentication (2FA): Prefer an authentication app (Google Authenticator, Passkeys) rather than SMS.
Verify addresses and URLs: Save Binance’s official URL in your bookmarks to avoid phishing attempts.
Beware of suspicious links: Never click on unsolicited links received via private message.
Whitelist your withdrawal addresses: Set up the Withdrawal Whitelist feature to allow withdrawals only to your trusted addresses.
Prudence and vigilance are your best security guarantees.
#SecurityFirst #CryptoSafety #PhishingAwareness #2FA #Binance @eden
81

🚨 $SFP DATA BREACH: 40K ORDERS EXPOSED — BUT YOUR KEYS SURVIVED THE STORM 💣
📌 Nearly 40,000 SafePal customers just got swept into a data leak through a vulnerable order-tracking plugin — names, emails, shipping addresses, phone numbers, and purchase details are now floating in the wild. That stings, no sugarcoating it. But here's the line that matters: no mnemonics, no private keys, no wallet passwords were touched. 🔍 Your crypto is still locked behind cryptographic steel.
💥 The real threat now isn't the breach itself — it's the phishing flood that always follows. Scammers will dress up as SafePal support, build fake verification pages, and weaponize your leaked shipping address to look scarily legit. 👁️ The team has patched the plugin, notified every affected user by email, and posted an official check page. If you ordered between March 2025 and April 2026, verify through the official portal — and ignore any message asking for your seed phrase.
💬 How do you separate legitimate security warnings from the phishing noise that rides every breach? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SFP #SecurityAlert #PhishingAwareness #CryptoNews #DataBreach
🛡️ 🔒
51
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#NFPWatch
10.5M views
17,748 Discussing
2
#BitcoinFundingRateTriplesTo10%
1,852 views
127 Discussing
3
#BitcoinSurpasses$86KUp2.99%
1,116 views
26 Discussing
4
#ZcashFalls21%FromSeptemberPeak
9,608 views
210 Discussing
5
#USSeptemberPayrollsAdd29KUnemploymentRises4.2%
1,048 views
69 Discussing
6
#XRPPostsFirstThreeGreenMonthsInQ3
11,301 views
276 Discussing
7
#BNBChainTokenizedStocksTop$1BAt30%Share
71 views
21 Discussing
8
#BitcoinRisesToward$85K
50,626 views
112 Discussing
9
#AmazonPlansToSell$8BNvidiaChips
5,750 views
77 Discussing
10
#NEARFallsToAround$4.70Down14%
39,327 views
101 Discussing