
#web3auth
web3auth
20,781 views
45 Discussing
Hot
Latest

⚠️ $ATOM SOCIAL LOGIN BREACH EXPOSES MILLIONS – ACT FAST! 🛑
Web3Auth’s social‑login flaw let the private keys behind Google and Apple sign‑ins leak, prompting Keplr to freeze those entry points. Bitquery flagged roughly $6 M siphoned from ~44k Cosmos Hub wallets, with some staked $ATOM pulled without the usual unbonding delay. 📊
If you’re on a Google/Apple login, treat the account as compromised – move any liquid balance to a seed‑phrase or hardware wallet and avoid new deposits. Ignore unsolicited DMs promising “recovery”; only official Keplr or Web3Auth channels are legit. 🦈💡
💬 Have you secured your $ATOM holdings yet? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ATOM #SecurityAlert #CryptoSafety #Web3Auth
🚀 🛡️
⚠️ $ATOM SOCIAL LOGIN BREACH EXPOSES MILLIONS – ACT FAST! 🛑
Web3Auth’s social‑login flaw let the private keys behind Google and Apple sign‑ins leak, prompting Keplr to freeze those entry points. Bitquery flagged roughly $6 M siphoned from ~44k Cosmos Hub wallets, with some staked $ATOM pulled without the usual unbonding delay. 📊
If you’re on a Google/Apple login, treat the account as compromised – move any liquid balance to a seed‑phrase or hardware wallet and avoid new deposits. Ignore unsolicited DMs promising “recovery”; only official Keplr or Web3Auth channels are legit. 🦈💡
💬 Have you secured your $ATOM holdings yet? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ATOM #SecurityAlert #CryptoSafety #Web3Auth
🚀 🛡️
Web3Auth’s social‑login flaw let the private keys behind Google and Apple sign‑ins leak, prompting Keplr to freeze those entry points. Bitquery flagged roughly $6 M siphoned from ~44k Cosmos Hub wallets, with some staked $ATOM pulled without the usual unbonding delay. 📊
If you’re on a Google/Apple login, treat the account as compromised – move any liquid balance to a seed‑phrase or hardware wallet and avoid new deposits. Ignore unsolicited DMs promising “recovery”; only official Keplr or Web3Auth channels are legit. 🦈💡
💬 Have you secured your $ATOM holdings yet? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ATOM #SecurityAlert #CryptoSafety #Web3Auth
🚀 🛡️
65

·
--
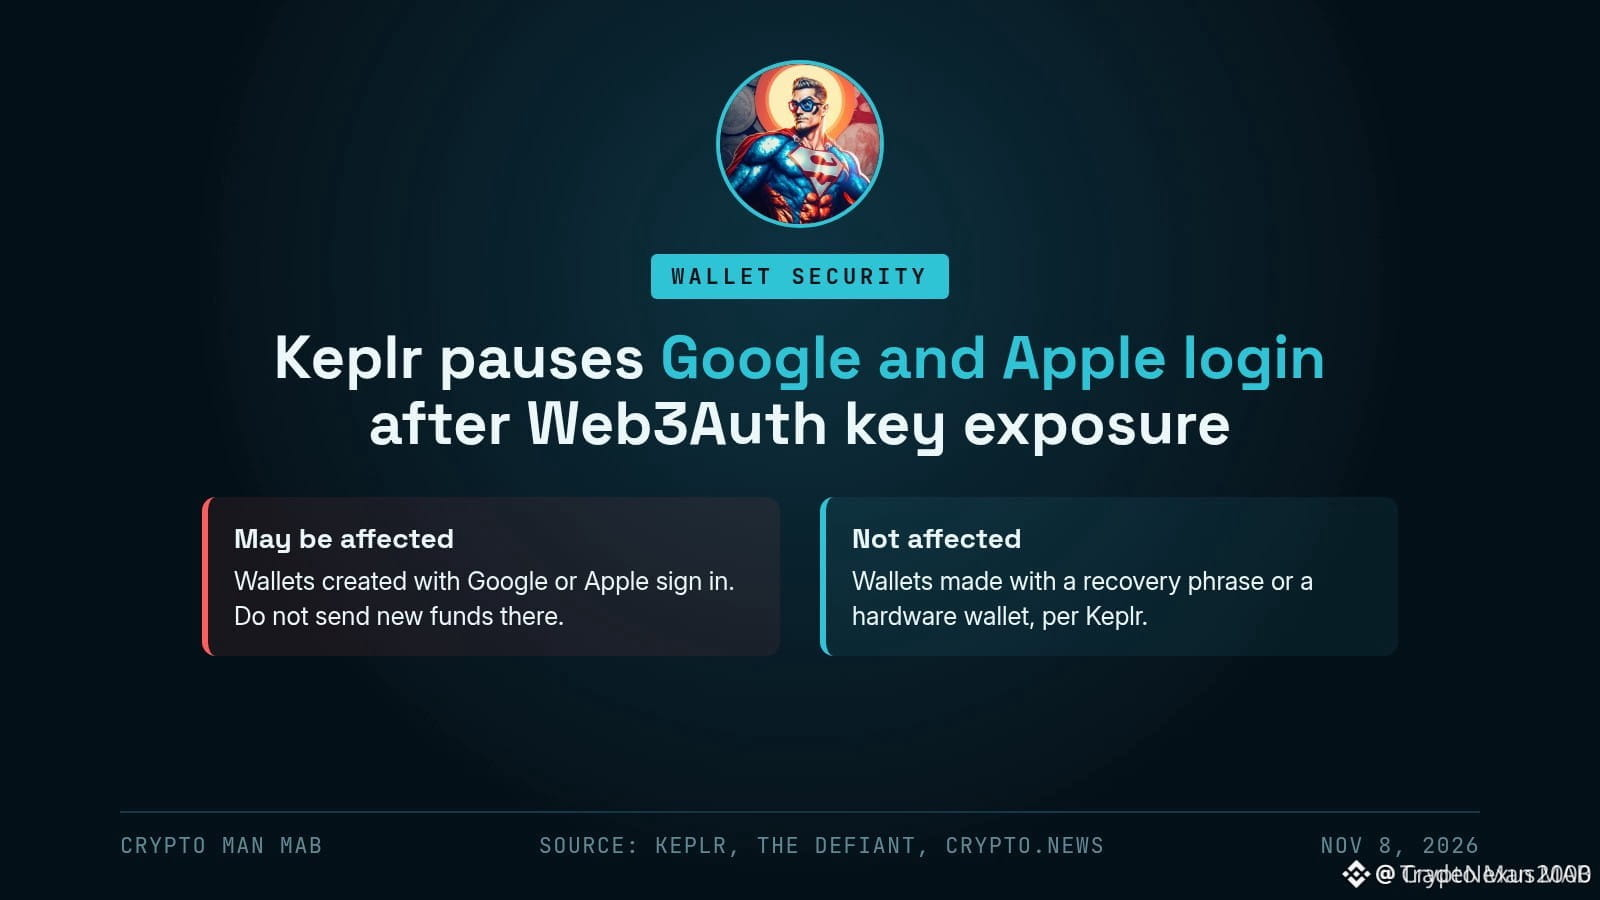
Over $6 million drained from at least 44,000 wallets using Google login
▫️Keplr confirmed unauthorized transfers from accounts signed in with Google or Apple; the issue lies with the social login service Web3Auth
▫️On-chain data shows at least 44,000 wallets affected, with about $6.01 million involved; the funds have not yet been transferred out
▫️Even after the official warning, 86% of the victims’ wallets were still drained
▫️The attackers also bypassed the 21-day unbonding period and withdrew about 1.96 million staked ATOM
Accounts using seed phrases or hardware wallets don’t appear to have been affected so far; these two social login options have been suspended
One-click login is convenient, but you may not actually hold the keys
Will you still feel comfortable logging into your wallet with a social account? 👇 (Not investment advice)
#Keplr #Web3Auth #WalletSecurity
Over $6 million drained from at least 44,000 wallets using Google login
▫️Keplr confirmed unauthorized transfers from accounts signed in with Google or Apple; the issue lies with the social login service Web3Auth
▫️On-chain data shows at least 44,000 wallets affected, with about $6.01 million involved; the funds have not yet been transferred out
▫️Even after the official warning, 86% of the victims’ wallets were still drained
▫️The attackers also bypassed the 21-day unbonding period and withdrew about 1.96 million staked ATOM
Accounts using seed phrases or hardware wallets don’t appear to have been affected so far; these two social login options have been suspended
One-click login is convenient, but you may not actually hold the keys
Will you still feel comfortable logging into your wallet with a social account? 👇 (Not investment advice)
#Keplr #Web3Auth #WalletSecurity
▫️Keplr confirmed unauthorized transfers from accounts signed in with Google or Apple; the issue lies with the social login service Web3Auth
▫️On-chain data shows at least 44,000 wallets affected, with about $6.01 million involved; the funds have not yet been transferred out
▫️Even after the official warning, 86% of the victims’ wallets were still drained
▫️The attackers also bypassed the 21-day unbonding period and withdrew about 1.96 million staked ATOM
Accounts using seed phrases or hardware wallets don’t appear to have been affected so far; these two social login options have been suspended
One-click login is convenient, but you may not actually hold the keys
Will you still feel comfortable logging into your wallet with a social account? 👇 (Not investment advice)
#Keplr #Web3Auth #WalletSecurity
2
2.5k
·
--
Keplr social login private keys exposed: $5.6 million moved to recovery addresses, ATOM falls 3.6%Web3Auth infrastructure vulnerability affects Keplr wallets. Odaily cited an official update saying that the private keys of some Keplr wallets created by signing in with Google or Apple were exposed; Web3Auth proactively transferred about $5.6 million in assets to secure addresses. The 12 recovery addresses include about 2.49 million ATOM, worth roughly $3.3 million.
At least another $6.01 million in cross-chain transfers flowed through related addresses, though the actual losses have yet to be verified. Keplr co-founder Josh Lee estimates that about 20% of accounts using Google or Apple sign-in were affected, but only a small fraction of them were actually exploited. Keplr advises users to stop depositing funds and move their remaining assets to a seed phrase or hardware wallet; staked and locked assets will take longer to address.
Keplr social login private keys exposed: $5.6 million moved to recovery addresses, ATOM falls 3.6%
Web3Auth infrastructure vulnerability affects Keplr wallets. Odaily cited an official update saying that the private keys of some Keplr wallets created by signing in with Google or Apple were exposed; Web3Auth proactively transferred about $5.6 million in assets to secure addresses. The 12 recovery addresses include about 2.49 million ATOM, worth roughly $3.3 million.
At least another $6.01 million in cross-chain transfers flowed through related addresses, though the actual losses have yet to be verified. Keplr co-founder Josh Lee estimates that about 20% of accounts using Google or Apple sign-in were affected, but only a small fraction of them were actually exploited. Keplr advises users to stop depositing funds and move their remaining assets to a seed phrase or hardware wallet; staked and locked assets will take longer to address.
At least another $6.01 million in cross-chain transfers flowed through related addresses, though the actual losses have yet to be verified. Keplr co-founder Josh Lee estimates that about 20% of accounts using Google or Apple sign-in were affected, but only a small fraction of them were actually exploited. Keplr advises users to stop depositing funds and move their remaining assets to a seed phrase or hardware wallet; staked and locked assets will take longer to address.
108

·
--
Web3Auth moved funds out of Keplr wallets: rescue or theft?
There’s an update on the Keplr social login incident. At 14:23 Beijing time on November 8, Web3Auth posted that, with Keplr’s assistance, it was moving assets from affected wallets into secure recovery wallets.
It also clarified that some transfers outsiders had mistaken for actions by the attacker were actually rescues. It then published a list of “verified recovery addresses” covering networks including Cosmos Hub, Osmosis, Celestia, Injective, and dYdX, plus one EVM address (said to cover eight chains), and said the list would continue to be updated. Keplr also reposted the notice, confirming that these were recovery addresses, not attacker addresses.
A few things to keep straight:
1. If your balance has been moved, first compare the destination address with the official list. Don’t assume you’ve been hacked based on a hunch.
2. Neither party has yet disclosed the number of affected wallets or the amount of losses. Don’t take figures circulating online as fact.
3. The official warning is to trust only official channels. Treat anyone who reaches out via DM offering to “help recover your assets” as a scammer.
CZ also reposted a reminder: anyone who has used a “social login” wallet should look into this carefully. Self-custody means taking responsibility yourself—including understanding who actually holds the keys.
#Keplr #钱包安全 #Web3Auth
Web3Auth moved funds out of Keplr wallets: rescue or theft?
There’s an update on the Keplr social login incident. At 14:23 Beijing time on November 8, Web3Auth posted that, with Keplr’s assistance, it was moving assets from affected wallets into secure recovery wallets.
It also clarified that some transfers outsiders had mistaken for actions by the attacker were actually rescues. It then published a list of “verified recovery addresses” covering networks including Cosmos Hub, Osmosis, Celestia, Injective, and dYdX, plus one EVM address (said to cover eight chains), and said the list would continue to be updated. Keplr also reposted the notice, confirming that these were recovery addresses, not attacker addresses.
A few things to keep straight:
1. If your balance has been moved, first compare the destination address with the official list. Don’t assume you’ve been hacked based on a hunch.
2. Neither party has yet disclosed the number of affected wallets or the amount of losses. Don’t take figures circulating online as fact.
3. The official warning is to trust only official channels. Treat anyone who reaches out via DM offering to “help recover your assets” as a scammer.
CZ also reposted a reminder: anyone who has used a “social login” wallet should look into this carefully. Self-custody means taking responsibility yourself—including understanding who actually holds the keys.
#Keplr #钱包安全 #Web3Auth
There’s an update on the Keplr social login incident. At 14:23 Beijing time on November 8, Web3Auth posted that, with Keplr’s assistance, it was moving assets from affected wallets into secure recovery wallets.
It also clarified that some transfers outsiders had mistaken for actions by the attacker were actually rescues. It then published a list of “verified recovery addresses” covering networks including Cosmos Hub, Osmosis, Celestia, Injective, and dYdX, plus one EVM address (said to cover eight chains), and said the list would continue to be updated. Keplr also reposted the notice, confirming that these were recovery addresses, not attacker addresses.
A few things to keep straight:
1. If your balance has been moved, first compare the destination address with the official list. Don’t assume you’ve been hacked based on a hunch.
2. Neither party has yet disclosed the number of affected wallets or the amount of losses. Don’t take figures circulating online as fact.
3. The official warning is to trust only official channels. Treat anyone who reaches out via DM offering to “help recover your assets” as a scammer.
CZ also reposted a reminder: anyone who has used a “social login” wallet should look into this carefully. Self-custody means taking responsibility yourself—including understanding who actually holds the keys.
#Keplr #钱包安全 #Web3Auth
53

·
--
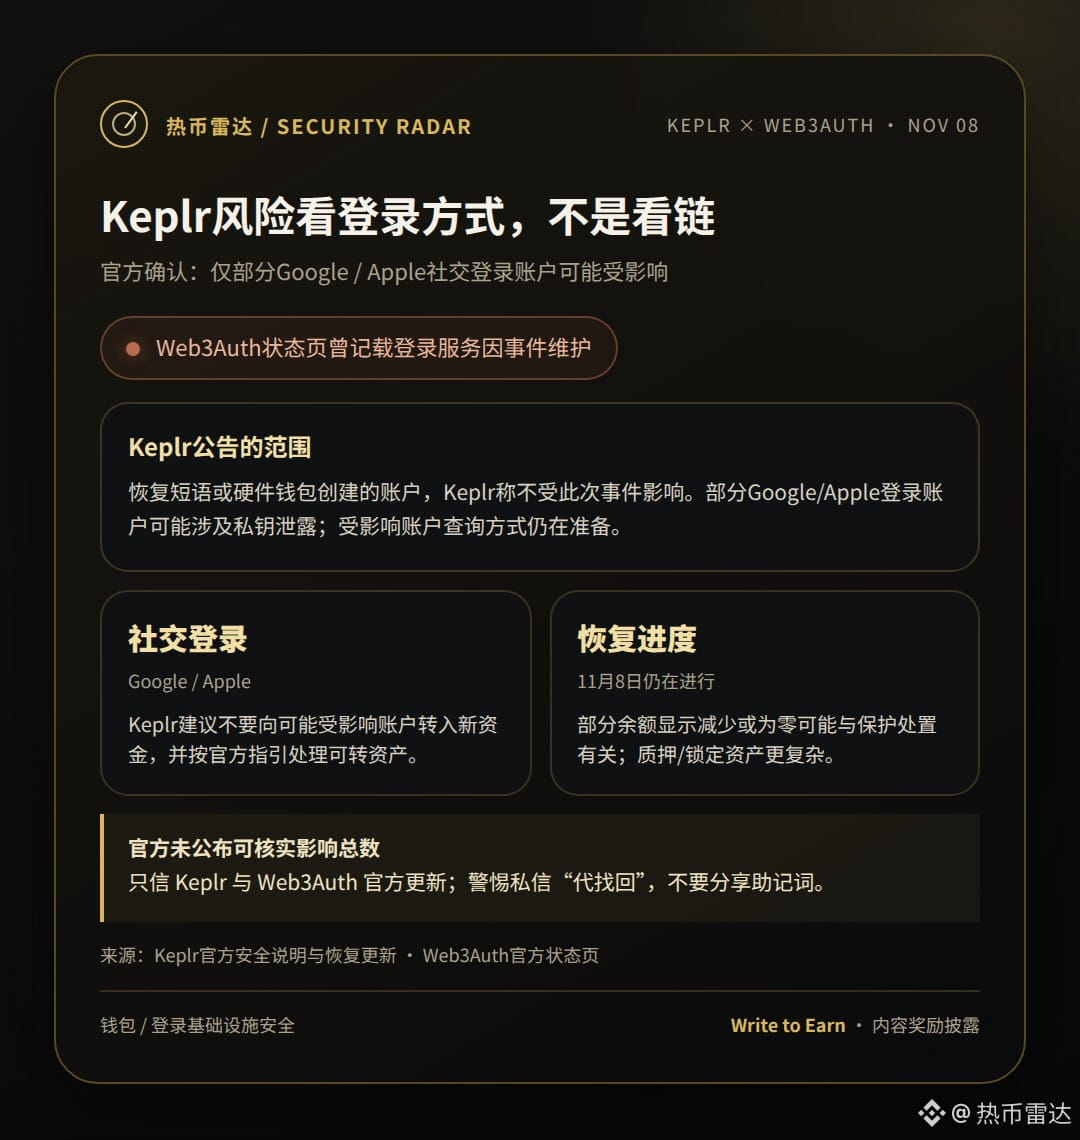
The risk with Keplr this time depends on how you log in—not “all wallets are affected”: Keplr says accounts created with a recovery phrase or hardware wallet are unaffected by this incident; some accounts using Google/Apple social login may have been affected by private key exposure.
Keplr has warned these users not to transfer any new funds into those accounts and to handle any remaining transferable assets according to official guidance. Some balances may have decreased or dropped to zero as part of protective measures; staked/locked assets take longer to process. As of November 8, Keplr said recovery efforts were ongoing and it was still preparing a way to check whether an account was affected; the company has not published a verifiable total number of affected accounts or losses.
Trust only updates from Keplr and Web3Auth, and beware of unsolicited messages offering to “recover” your account. At what point should a wallet clearly explain the key security risks of social login?
Sources: [Keplr official statement](https://x.com/keplrwallet/status/2119117067500806350)|[Keplr recovery updates](https://x.com/keplrwallet/status/2119316885737177339)|[Web3Auth status page](https://status.web3auth.io/events/maintenance/461)
Disclosure: This post may qualify for Binance Square Write to Earn content rewards; eligibility and rewards are subject to platform rules and actual results. Not investment advice.
#Keplr #Web3Auth #Security
The risk with Keplr this time depends on how you log in—not “all wallets are affected”: Keplr says accounts created with a recovery phrase or hardware wallet are unaffected by this incident; some accounts using Google/Apple social login may have been affected by private key exposure.
Keplr has warned these users not to transfer any new funds into those accounts and to handle any remaining transferable assets according to official guidance. Some balances may have decreased or dropped to zero as part of protective measures; staked/locked assets take longer to process. As of November 8, Keplr said recovery efforts were ongoing and it was still preparing a way to check whether an account was affected; the company has not published a verifiable total number of affected accounts or losses.
Trust only updates from Keplr and Web3Auth, and beware of unsolicited messages offering to “recover” your account. At what point should a wallet clearly explain the key security risks of social login?
Sources: [Keplr official statement](https://x.com/keplrwallet/status/2119117067500806350)|[Keplr recovery updates](https://x.com/keplrwallet/status/2119316885737177339)|[Web3Auth status page](https://status.web3auth.io/events/maintenance/461)
Disclosure: This post may qualify for Binance Square Write to Earn content rewards; eligibility and rewards are subject to platform rules and actual results. Not investment advice.
#Keplr #Web3Auth #Security
Keplr has warned these users not to transfer any new funds into those accounts and to handle any remaining transferable assets according to official guidance. Some balances may have decreased or dropped to zero as part of protective measures; staked/locked assets take longer to process. As of November 8, Keplr said recovery efforts were ongoing and it was still preparing a way to check whether an account was affected; the company has not published a verifiable total number of affected accounts or losses.
Trust only updates from Keplr and Web3Auth, and beware of unsolicited messages offering to “recover” your account. At what point should a wallet clearly explain the key security risks of social login?
Sources: [Keplr official statement](https://x.com/keplrwallet/status/2119117067500806350)|[Keplr recovery updates](https://x.com/keplrwallet/status/2119316885737177339)|[Web3Auth status page](https://status.web3auth.io/events/maintenance/461)
Disclosure: This post may qualify for Binance Square Write to Earn content rewards; eligibility and rewards are subject to platform rules and actual results. Not investment advice.
#Keplr #Web3Auth #Security
68
·
--
Keplr balances are falling—don’t count every protective transfer as theft
If you created your Keplr wallet using Google or Apple, stop transferring funds into that account for now. A zero balance neither proves that everything was stolen nor means the assets have been returned. What matters is verifying where the funds went and what arrangements are in place for their return.
On November 7, Keplr said a vulnerability in Web3Auth’s infrastructure exposed the private keys of some social-login users. According to its preliminary statement, accounts created with a seed phrase or hardware wallet were not affected by this incident. Don’t generalize the risk to mean that all Keplr wallets have been compromised.
On November 8, Web3Auth published the recovery addresses used for protective transfers, saying that some transfers had been mistaken for actions by an attacker. The Block reported that those addresses held approximately $5.6 million in assets at the time of its report. That figure is the estimated value of assets in the recovery addresses—not the final amount stolen, and certainly not money already returned to users.
So keep two things in mind at once: some balance reductions may be due to protective transfers, but the risk of exposed private keys and users being temporarily unable to control their assets has not gone away. Keplr recommends moving liquid assets that can still be transferred to an account created with a seed phrase or hardware wallet. Staked and locked assets are more complicated to handle, so don’t assume they can be dealt with on the same timeline as liquid assets.
Over the next two or three days, check the official affected-account lookup, updates to the recovery addresses, and the return process. This is a monitoring window, not a promise of a refund. Lower the risk assessment only once the scope is clear and returns can be verified; raise it if abnormal transfers outside the published list appear or the impact expands. Check for updates only through known official channels, and don’t click “recovery” links sent in private messages.
#Keplr #Web3Auth #WalletSecurity
Keplr balances are falling—don’t count every protective transfer as theft
If you created your Keplr wallet using Google or Apple, stop transferring funds into that account for now. A zero balance neither proves that everything was stolen nor means the assets have been returned. What matters is verifying where the funds went and what arrangements are in place for their return.
On November 7, Keplr said a vulnerability in Web3Auth’s infrastructure exposed the private keys of some social-login users. According to its preliminary statement, accounts created with a seed phrase or hardware wallet were not affected by this incident. Don’t generalize the risk to mean that all Keplr wallets have been compromised.
On November 8, Web3Auth published the recovery addresses used for protective transfers, saying that some transfers had been mistaken for actions by an attacker. The Block reported that those addresses held approximately $5.6 million in assets at the time of its report. That figure is the estimated value of assets in the recovery addresses—not the final amount stolen, and certainly not money already returned to users.
So keep two things in mind at once: some balance reductions may be due to protective transfers, but the risk of exposed private keys and users being temporarily unable to control their assets has not gone away. Keplr recommends moving liquid assets that can still be transferred to an account created with a seed phrase or hardware wallet. Staked and locked assets are more complicated to handle, so don’t assume they can be dealt with on the same timeline as liquid assets.
Over the next two or three days, check the official affected-account lookup, updates to the recovery addresses, and the return process. This is a monitoring window, not a promise of a refund. Lower the risk assessment only once the scope is clear and returns can be verified; raise it if abnormal transfers outside the published list appear or the impact expands. Check for updates only through known official channels, and don’t click “recovery” links sent in private messages.
#Keplr #Web3Auth #WalletSecurity
If you created your Keplr wallet using Google or Apple, stop transferring funds into that account for now. A zero balance neither proves that everything was stolen nor means the assets have been returned. What matters is verifying where the funds went and what arrangements are in place for their return.
On November 7, Keplr said a vulnerability in Web3Auth’s infrastructure exposed the private keys of some social-login users. According to its preliminary statement, accounts created with a seed phrase or hardware wallet were not affected by this incident. Don’t generalize the risk to mean that all Keplr wallets have been compromised.
On November 8, Web3Auth published the recovery addresses used for protective transfers, saying that some transfers had been mistaken for actions by an attacker. The Block reported that those addresses held approximately $5.6 million in assets at the time of its report. That figure is the estimated value of assets in the recovery addresses—not the final amount stolen, and certainly not money already returned to users.
So keep two things in mind at once: some balance reductions may be due to protective transfers, but the risk of exposed private keys and users being temporarily unable to control their assets has not gone away. Keplr recommends moving liquid assets that can still be transferred to an account created with a seed phrase or hardware wallet. Staked and locked assets are more complicated to handle, so don’t assume they can be dealt with on the same timeline as liquid assets.
Over the next two or three days, check the official affected-account lookup, updates to the recovery addresses, and the return process. This is a monitoring window, not a promise of a refund. Lower the risk assessment only once the scope is clear and returns can be verified; raise it if abnormal transfers outside the published list appear or the impact expands. Check for updates only through known official channels, and don’t click “recovery” links sent in private messages.
#Keplr #Web3Auth #WalletSecurity
69

·
--
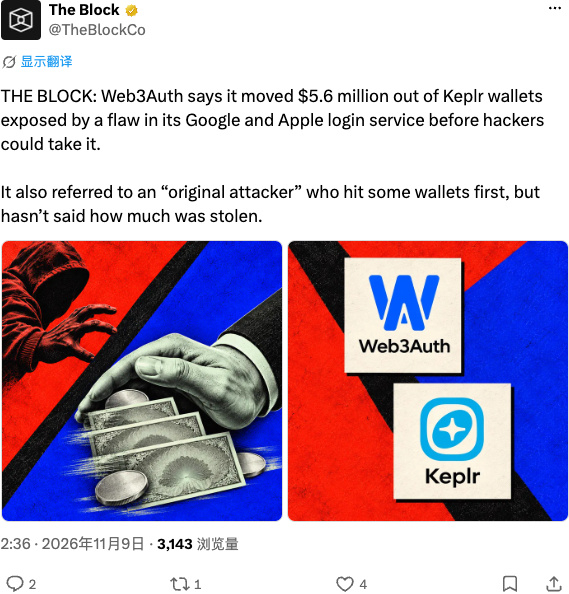
Web3Auth reacted quickly and withdrew 5.6 million right away—the hacker didn't get there in time. After the Google and Apple login vulnerability was exposed, they moved the funds immediately and saved most of them. They didn't say how much the “original attacker” stole, but had this vulnerability been on their radar for a while? Their security awareness is still a little worrying.
#Web3Auth #Security
Web3Auth reacted quickly and withdrew 5.6 million right away—the hacker didn't get there in time. After the Google and Apple login vulnerability was exposed, they moved the funds immediately and saved most of them. They didn't say how much the “original attacker” stole, but had this vulnerability been on their radar for a while? Their security awareness is still a little worrying.
#Web3Auth #Security
#Web3Auth #Security
AAPL+0.80%
GOOGUS+0.82%
·
--
$6 million stolen from Keplr wallets: Nobody clicked the wrong link—the problem was “seed phrase-free” loginFrom late on November 6 through the afternoon of November 7, a wave of Keplr wallets created using Google or Apple accounts were emptied. On-chain analytics firm Bitquery reported that at least 44,041 wallets were affected (about 44,700 including Injective), with a combined total of about $6.01 million sent to two receiving addresses.
The most revealing aspects of this incident aren’t the amount stolen, but three counterintuitive details.
1. The problem wasn’t Keplr, but “seed phrase-free” login
Keplr’s social login is provided by a third-party service, Web3Auth. Users don’t need to remember a seed phrase; each time they log in, the service helps “reconstruct” their private key. Web3Auth has confirmed a vulnerability in its infrastructure that exposed some users’ private keys.
$6 million stolen from Keplr wallets: Nobody clicked the wrong link—the problem was “seed phrase-free” login
From late on November 6 through the afternoon of November 7, a wave of Keplr wallets created using Google or Apple accounts were emptied. On-chain analytics firm Bitquery reported that at least 44,041 wallets were affected (about 44,700 including Injective), with a combined total of about $6.01 million sent to two receiving addresses.
The most revealing aspects of this incident aren’t the amount stolen, but three counterintuitive details.
1. The problem wasn’t Keplr, but “seed phrase-free” login
Keplr’s social login is provided by a third-party service, Web3Auth. Users don’t need to remember a seed phrase; each time they log in, the service helps “reconstruct” their private key. Web3Auth has confirmed a vulnerability in its infrastructure that exposed some users’ private keys.
The most revealing aspects of this incident aren’t the amount stolen, but three counterintuitive details.
1. The problem wasn’t Keplr, but “seed phrase-free” login
Keplr’s social login is provided by a third-party service, Web3Auth. Users don’t need to remember a seed phrase; each time they log in, the service helps “reconstruct” their private key. Web3Auth has confirmed a vulnerability in its infrastructure that exposed some users’ private keys.
41
All day, the whole internet was saying: Keplr wallets were hacked for $6.01 million, and 44,000 wallets were drained overnight.
Then the story flipped that evening. Web3Auth came out and said: Don’t panic—the $6.01 million wasn’t taken by hackers; our own people moved it to safety. They also published official rescue addresses covering 11 Cosmos chains and 8 EVM chains.
But here’s the problem: Bitquery tracked 44,000 wallets and 1.96 million staked ATOM transferred out by bypassing the 21-day lockup period—and the official team hasn’t denied those figures either. How much money ended up in the hackers’ pockets, what exactly the vulnerability was, and whether users will be reimbursed—the official team still hasn’t said a word.
$ATOM is now at $1.36, down 9% in 7 days and 25% in 30 days, and 97% below its all-time high of $43.84. Support is right below at $1.30–$1.33; if it can’t hold, we’ll see a new low. For a rebound, the first level to watch is the 7-day moving average at $1.41.
Pick a side: A) Trust the official account that this was a rescue operation, buy the dip at $1.36 and wait for a rebound after clarification; B) We don’t even know how much the hackers took—wait for a break below $1.30 before discussing it.
$ATOM $BTC
#Keplr #Web3Auth #WalletSecurity
All day, the whole internet was saying: Keplr wallets were hacked for $6.01 million, and 44,000 wallets were drained overnight.
Then the story flipped that evening. Web3Auth came out and said: Don’t panic—the $6.01 million wasn’t taken by hackers; our own people moved it to safety. They also published official rescue addresses covering 11 Cosmos chains and 8 EVM chains.
But here’s the problem: Bitquery tracked 44,000 wallets and 1.96 million staked ATOM transferred out by bypassing the 21-day lockup period—and the official team hasn’t denied those figures either. How much money ended up in the hackers’ pockets, what exactly the vulnerability was, and whether users will be reimbursed—the official team still hasn’t said a word.
$ATOM is now at $1.36, down 9% in 7 days and 25% in 30 days, and 97% below its all-time high of $43.84. Support is right below at $1.30–$1.33; if it can’t hold, we’ll see a new low. For a rebound, the first level to watch is the 7-day moving average at $1.41.
Pick a side: A) Trust the official account that this was a rescue operation, buy the dip at $1.36 and wait for a rebound after clarification; B) We don’t even know how much the hackers took—wait for a break below $1.30 before discussing it.
$ATOM $BTC
#Keplr #Web3Auth #WalletSecurity
Then the story flipped that evening. Web3Auth came out and said: Don’t panic—the $6.01 million wasn’t taken by hackers; our own people moved it to safety. They also published official rescue addresses covering 11 Cosmos chains and 8 EVM chains.
But here’s the problem: Bitquery tracked 44,000 wallets and 1.96 million staked ATOM transferred out by bypassing the 21-day lockup period—and the official team hasn’t denied those figures either. How much money ended up in the hackers’ pockets, what exactly the vulnerability was, and whether users will be reimbursed—the official team still hasn’t said a word.
$ATOM is now at $1.36, down 9% in 7 days and 25% in 30 days, and 97% below its all-time high of $43.84. Support is right below at $1.30–$1.33; if it can’t hold, we’ll see a new low. For a rebound, the first level to watch is the 7-day moving average at $1.41.
Pick a side: A) Trust the official account that this was a rescue operation, buy the dip at $1.36 and wait for a rebound after clarification; B) We don’t even know how much the hackers took—wait for a break below $1.30 before discussing it.
$ATOM $BTC
#Keplr #Web3Auth #WalletSecurity

Web3Auth Breach Does Not Affect Trust Wallet Accounts: Products Need Attention
- A Web3Auth security breach exposed thousands of Keplr wallets across multiple Cosmos networks.
- The attackers stole at least $6 million across 8 networks in the Cosmos ecosystem.
- This attack does not directly affect Trust Wallet.
- Users should check and secure their Web3Auth wallets and related products.
#Web3Auth #TrustWallet #Cosmos #Security #Crypto
$btc $eth
vlikevn Titanbot
Source: U.Today
Web3Auth Breach Does Not Affect Trust Wallet Accounts: Products Need Attention
- A Web3Auth security breach exposed thousands of Keplr wallets across multiple Cosmos networks.
- The attackers stole at least $6 million across 8 networks in the Cosmos ecosystem.
- This attack does not directly affect Trust Wallet.
- Users should check and secure their Web3Auth wallets and related products.
#Web3Auth #TrustWallet #Cosmos #Security #Crypto
$btc $eth
vlikevn Titanbot
Source: U.Today
- A Web3Auth security breach exposed thousands of Keplr wallets across multiple Cosmos networks.
- The attackers stole at least $6 million across 8 networks in the Cosmos ecosystem.
- This attack does not directly affect Trust Wallet.
- Users should check and secure their Web3Auth wallets and related products.
#Web3Auth #TrustWallet #Cosmos #Security #Crypto
$btc $eth
vlikevn Titanbot
Source: U.Today
230
A real-life race is unfolding in the Cosmos scene tonight: hackers are stealing up front, white hats are scrambling after them, and your coins are stuck in the middle awaiting their verdict.
Keplr just came clean: a Web3Auth vulnerability exposed the private keys of users who logged in with Google/Apple, affecting more than 44,000 wallets. On-chain tracking has already identified $6.01 million in transfers, and about one in five social-login accounts may be affected. The official advice: everyone should quickly move their remaining funds to a wallet secured with a recovery phrase. Wait too long and your balance could drop to zero; staked funds will take time to unlock.
A snapshot of the crowd: Google-login users are moving out overnight, hands shaking so much they’re copying their recovery phrases onto the wrong lines; recovery-phrase and hardware-wallet users are calmly watching the drama unfold: “We told you not to take shortcuts.” Most confused are those who can’t tell white hats from black hats—they don’t even know who to thank when their wallet balance shrinks.
$ATOM 1.37 bucks, down 8.8% in 7 days; $INJ 8.2 bucks, still up 17.8% in 5 days. The same rescue list, two different trajectories.
Pick a side: A) Better to get out first; we’ll see who wins between the white hats and black hats / B) Panic selling creates bargains—buy if $ATOM drops below 1.3
#Keplr #Web3Auth #WalletSecurity
A real-life race is unfolding in the Cosmos scene tonight: hackers are stealing up front, white hats are scrambling after them, and your coins are stuck in the middle awaiting their verdict.
Keplr just came clean: a Web3Auth vulnerability exposed the private keys of users who logged in with Google/Apple, affecting more than 44,000 wallets. On-chain tracking has already identified $6.01 million in transfers, and about one in five social-login accounts may be affected. The official advice: everyone should quickly move their remaining funds to a wallet secured with a recovery phrase. Wait too long and your balance could drop to zero; staked funds will take time to unlock.
A snapshot of the crowd: Google-login users are moving out overnight, hands shaking so much they’re copying their recovery phrases onto the wrong lines; recovery-phrase and hardware-wallet users are calmly watching the drama unfold: “We told you not to take shortcuts.” Most confused are those who can’t tell white hats from black hats—they don’t even know who to thank when their wallet balance shrinks.
$ATOM 1.37 bucks, down 8.8% in 7 days; $INJ 8.2 bucks, still up 17.8% in 5 days. The same rescue list, two different trajectories.
Pick a side: A) Better to get out first; we’ll see who wins between the white hats and black hats / B) Panic selling creates bargains—buy if $ATOM drops below 1.3
#Keplr #Web3Auth #WalletSecurity
Keplr just came clean: a Web3Auth vulnerability exposed the private keys of users who logged in with Google/Apple, affecting more than 44,000 wallets. On-chain tracking has already identified $6.01 million in transfers, and about one in five social-login accounts may be affected. The official advice: everyone should quickly move their remaining funds to a wallet secured with a recovery phrase. Wait too long and your balance could drop to zero; staked funds will take time to unlock.
A snapshot of the crowd: Google-login users are moving out overnight, hands shaking so much they’re copying their recovery phrases onto the wrong lines; recovery-phrase and hardware-wallet users are calmly watching the drama unfold: “We told you not to take shortcuts.” Most confused are those who can’t tell white hats from black hats—they don’t even know who to thank when their wallet balance shrinks.
$ATOM 1.37 bucks, down 8.8% in 7 days; $INJ 8.2 bucks, still up 17.8% in 5 days. The same rescue list, two different trajectories.
Pick a side: A) Better to get out first; we’ll see who wins between the white hats and black hats / B) Panic selling creates bargains—buy if $ATOM drops below 1.3
#Keplr #Web3Auth #WalletSecurity
2

·
--
Recovery phrases are safe; ‘one-click sign-in’ is not: Keplr suspends Google and Apple sign-insWallets that took the easy route and signed in with Google or Apple got hit first this time.
On November 6, Web3Auth, which provides embedded wallets and social sign-in, said its service had a security issue and that it had temporarily disabled embedded wallets. It had initially found no evidence that MetaMask users were affected. On November 7, it added that the issue was with Web3Auth’s infrastructure and affected some embedded wallets used by Keplr.
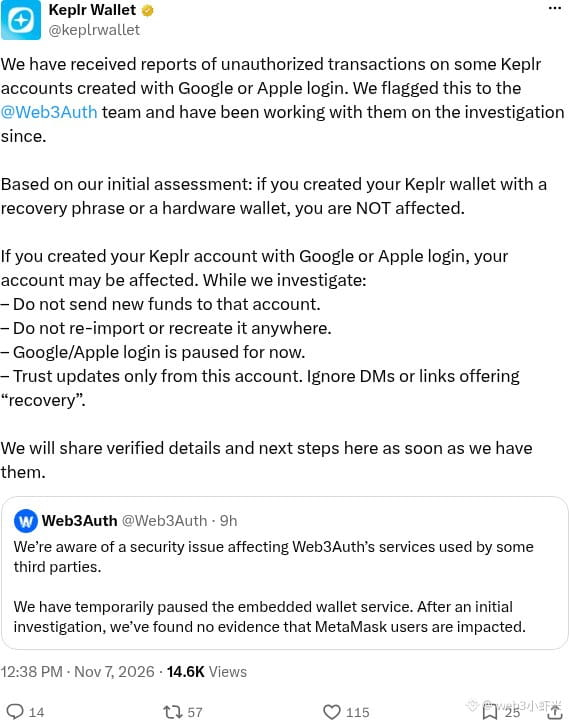
On the same day, Keplr, a wallet commonly used in Cosmos, officially posted that some accounts signed in with Google or Apple had experienced unauthorized transactions, and that it was working with Web3Auth to investigate. The team’s initial assessment was that accounts created with a recovery phrase or hardware wallet were unaffected; Google and Apple sign-ins have been suspended for now. It urged affected users not to add funds to these accounts or reimport their wallets or recreate them elsewhere.
Recovery phrases are safe; ‘one-click sign-in’ is not: Keplr suspends Google and Apple sign-ins
Wallets that took the easy route and signed in with Google or Apple got hit first this time.
On November 6, Web3Auth, which provides embedded wallets and social sign-in, said its service had a security issue and that it had temporarily disabled embedded wallets. It had initially found no evidence that MetaMask users were affected. On November 7, it added that the issue was with Web3Auth’s infrastructure and affected some embedded wallets used by Keplr.
On the same day, Keplr, a wallet commonly used in Cosmos, officially posted that some accounts signed in with Google or Apple had experienced unauthorized transactions, and that it was working with Web3Auth to investigate. The team’s initial assessment was that accounts created with a recovery phrase or hardware wallet were unaffected; Google and Apple sign-ins have been suspended for now. It urged affected users not to add funds to these accounts or reimport their wallets or recreate them elsewhere.
On November 6, Web3Auth, which provides embedded wallets and social sign-in, said its service had a security issue and that it had temporarily disabled embedded wallets. It had initially found no evidence that MetaMask users were affected. On November 7, it added that the issue was with Web3Auth’s infrastructure and affected some embedded wallets used by Keplr.
On the same day, Keplr, a wallet commonly used in Cosmos, officially posted that some accounts signed in with Google or Apple had experienced unauthorized transactions, and that it was working with Web3Auth to investigate. The team’s initial assessment was that accounts created with a recovery phrase or hardware wallet were unaffected; Google and Apple sign-ins have been suspended for now. It urged affected users not to add funds to these accounts or reimport their wallets or recreate them elsewhere.
GOOGUS+0.82%
買不起比特幣只能買比特犬:
所有熱錢包都不要用,並移除所有㽞覽器插件
1
220

·
--
【Google-login wallets were stolen! Keplr shuts down social logins overnight】
On November 7, Keplr, a popular Cosmos wallet, suspended Google and Apple logins: assets were transferred without authorization from some wallets created using social accounts. The issue involved Web3Auth, the third party responsible for social logins. Wallets using a recovery phrase or hardware wallet are unaffected. Don’t deposit funds into these kinds of accounts, and anyone who privately messages you claiming they can “help recover” your funds is a scammer.
$ATOM $OSMO
#Keplr #Web3Auth #WalletSecurity
【Google-login wallets were stolen! Keplr shuts down social logins overnight】
On November 7, Keplr, a popular Cosmos wallet, suspended Google and Apple logins: assets were transferred without authorization from some wallets created using social accounts. The issue involved Web3Auth, the third party responsible for social logins. Wallets using a recovery phrase or hardware wallet are unaffected. Don’t deposit funds into these kinds of accounts, and anyone who privately messages you claiming they can “help recover” your funds is a scammer.
$ATOM $OSMO
#Keplr #Web3Auth #WalletSecurity
On November 7, Keplr, a popular Cosmos wallet, suspended Google and Apple logins: assets were transferred without authorization from some wallets created using social accounts. The issue involved Web3Auth, the third party responsible for social logins. Wallets using a recovery phrase or hardware wallet are unaffected. Don’t deposit funds into these kinds of accounts, and anyone who privately messages you claiming they can “help recover” your funds is a scammer.
$ATOM $OSMO
#Keplr #Web3Auth #WalletSecurity
41

·
--
【Security Alert】Web3Auth has suspended its embedded wallet service due to a security issue, and unauthorized transactions have been reported on some Keplr accounts using social login.
Here are the key facts:
1. The affected accounts were created with Keplr using Google or Apple sign-in. Accounts created with a recovery phrase or hardware wallet are preliminarily believed to be unaffected.
2. Web3Auth says some third-party platforms were affected and has urgently suspended its embedded wallet service. Initial investigations indicate that MetaMask users were not affected.
3. Keplr has reported the issue to Web3Auth and launched a joint investigation. The root cause and further details are pending an official announcement.
Three immediate recommendations for users:
- If you use a Keplr account created with social login, check your assets and authorization records immediately. If necessary, create a new recovery-phrase wallet and transfer your assets.
- Watch out for phishing messages and links from people impersonating official customer support. Rely only on official channels for announcements.
- This incident is another reminder: social login lowers the barrier to entry, but private key management depends on a third party, making its risk model very different from self-custody. For large holdings, consider using a recovery phrase with a hardware wallet.
Convenience and security always involve trade-offs. Await further official information on the root cause and remediation measures.
#Web3安全 #Keplr #Web3Auth
【Security Alert】Web3Auth has suspended its embedded wallet service due to a security issue, and unauthorized transactions have been reported on some Keplr accounts using social login.
Here are the key facts:
1. The affected accounts were created with Keplr using Google or Apple sign-in. Accounts created with a recovery phrase or hardware wallet are preliminarily believed to be unaffected.
2. Web3Auth says some third-party platforms were affected and has urgently suspended its embedded wallet service. Initial investigations indicate that MetaMask users were not affected.
3. Keplr has reported the issue to Web3Auth and launched a joint investigation. The root cause and further details are pending an official announcement.
Three immediate recommendations for users:
- If you use a Keplr account created with social login, check your assets and authorization records immediately. If necessary, create a new recovery-phrase wallet and transfer your assets.
- Watch out for phishing messages and links from people impersonating official customer support. Rely only on official channels for announcements.
- This incident is another reminder: social login lowers the barrier to entry, but private key management depends on a third party, making its risk model very different from self-custody. For large holdings, consider using a recovery phrase with a hardware wallet.
Convenience and security always involve trade-offs. Await further official information on the root cause and remediation measures.
#Web3安全 #Keplr #Web3Auth
Here are the key facts:
1. The affected accounts were created with Keplr using Google or Apple sign-in. Accounts created with a recovery phrase or hardware wallet are preliminarily believed to be unaffected.
2. Web3Auth says some third-party platforms were affected and has urgently suspended its embedded wallet service. Initial investigations indicate that MetaMask users were not affected.
3. Keplr has reported the issue to Web3Auth and launched a joint investigation. The root cause and further details are pending an official announcement.
Three immediate recommendations for users:
- If you use a Keplr account created with social login, check your assets and authorization records immediately. If necessary, create a new recovery-phrase wallet and transfer your assets.
- Watch out for phishing messages and links from people impersonating official customer support. Rely only on official channels for announcements.
- This incident is another reminder: social login lowers the barrier to entry, but private key management depends on a third party, making its risk model very different from self-custody. For large holdings, consider using a recovery phrase with a hardware wallet.
Convenience and security always involve trade-offs. Await further official information on the root cause and remediation measures.
#Web3安全 #Keplr #Web3Auth

【Security Alert】Unauthorized transactions have been reported on some Keplr Wallet accounts using social login. The source of the risk points to Web3Auth, a provider of embedded wallet infrastructure.
Incident timeline:
1. Web3Auth officially confirmed a security issue affecting its services and has suspended its embedded wallet services. Some third-party platforms have been affected. Preliminary investigations found no impact on MetaMask users; further details will be announced by the company.
2. Keplr Wallet said it has received multiple reports of unauthorized transactions on accounts created by logging in with Google or Apple. The reports have been forwarded to the Web3Auth team, and the two parties are investigating jointly.
3. The scope of the impact is clearly defined: Keplr accounts created using a seed phrase or hardware wallet are not affected. Only accounts created through Google/Apple social login may be affected.
Affected users are advised to check their accounts immediately:
- Check account assets and recent authorization records, and stop signing any unfamiliar transactions;
- If you use a social login account, move your assets as soon as possible to a new address controlled by a seed phrase or hardware wallet;
- Beware of phishing links from people impersonating official support or offering airdrop compensation. Rely only on official announcements.
Social login lowers the barrier to using Web3, but relying on third-party infrastructure to manage private keys concentrates risk. This incident is another reminder that self-custody using a seed phrase or hardware wallet remains a safer choice for long-term asset storage.
#Web3安全 #Keplr #Web3Auth
【Security Alert】Unauthorized transactions have been reported on some Keplr Wallet accounts using social login. The source of the risk points to Web3Auth, a provider of embedded wallet infrastructure.
Incident timeline:
1. Web3Auth officially confirmed a security issue affecting its services and has suspended its embedded wallet services. Some third-party platforms have been affected. Preliminary investigations found no impact on MetaMask users; further details will be announced by the company.
2. Keplr Wallet said it has received multiple reports of unauthorized transactions on accounts created by logging in with Google or Apple. The reports have been forwarded to the Web3Auth team, and the two parties are investigating jointly.
3. The scope of the impact is clearly defined: Keplr accounts created using a seed phrase or hardware wallet are not affected. Only accounts created through Google/Apple social login may be affected.
Affected users are advised to check their accounts immediately:
- Check account assets and recent authorization records, and stop signing any unfamiliar transactions;
- If you use a social login account, move your assets as soon as possible to a new address controlled by a seed phrase or hardware wallet;
- Beware of phishing links from people impersonating official support or offering airdrop compensation. Rely only on official announcements.
Social login lowers the barrier to using Web3, but relying on third-party infrastructure to manage private keys concentrates risk. This incident is another reminder that self-custody using a seed phrase or hardware wallet remains a safer choice for long-term asset storage.
#Web3安全 #Keplr #Web3Auth
Incident timeline:
1. Web3Auth officially confirmed a security issue affecting its services and has suspended its embedded wallet services. Some third-party platforms have been affected. Preliminary investigations found no impact on MetaMask users; further details will be announced by the company.
2. Keplr Wallet said it has received multiple reports of unauthorized transactions on accounts created by logging in with Google or Apple. The reports have been forwarded to the Web3Auth team, and the two parties are investigating jointly.
3. The scope of the impact is clearly defined: Keplr accounts created using a seed phrase or hardware wallet are not affected. Only accounts created through Google/Apple social login may be affected.
Affected users are advised to check their accounts immediately:
- Check account assets and recent authorization records, and stop signing any unfamiliar transactions;
- If you use a social login account, move your assets as soon as possible to a new address controlled by a seed phrase or hardware wallet;
- Beware of phishing links from people impersonating official support or offering airdrop compensation. Rely only on official announcements.
Social login lowers the barrier to using Web3, but relying on third-party infrastructure to manage private keys concentrates risk. This incident is another reminder that self-custody using a seed phrase or hardware wallet remains a safer choice for long-term asset storage.
#Web3安全 #Keplr #Web3Auth
1

·
--
Seeing reports about Keplr: Some accounts created using Google / Apple sign-in have had unauthorized transactions. Keplr is investigating with Web3Auth, and social login has been temporarily suspended.
Preliminary guidance: Keplr accounts created with a recovery phrase or hardware wallet do not appear to be affected for now. If you used social login, don’t deposit any more funds for now, and don’t import or recreate the account elsewhere. Web3Auth says its embedded wallet service has been temporarily suspended. So far, MetaMask users do not appear to be affected.
Social login is convenient, but when something goes wrong, it can put everyone at risk all at once. Fake support agents offering to “help you recover your account” will surely show up now—trust only official accounts.
#Keplr #Web3Auth #WalletSecurity
Seeing reports about Keplr: Some accounts created using Google / Apple sign-in have had unauthorized transactions. Keplr is investigating with Web3Auth, and social login has been temporarily suspended.
Preliminary guidance: Keplr accounts created with a recovery phrase or hardware wallet do not appear to be affected for now. If you used social login, don’t deposit any more funds for now, and don’t import or recreate the account elsewhere. Web3Auth says its embedded wallet service has been temporarily suspended. So far, MetaMask users do not appear to be affected.
Social login is convenient, but when something goes wrong, it can put everyone at risk all at once. Fake support agents offering to “help you recover your account” will surely show up now—trust only official accounts.
#Keplr #Web3Auth #WalletSecurity
Preliminary guidance: Keplr accounts created with a recovery phrase or hardware wallet do not appear to be affected for now. If you used social login, don’t deposit any more funds for now, and don’t import or recreate the account elsewhere. Web3Auth says its embedded wallet service has been temporarily suspended. So far, MetaMask users do not appear to be affected.
Social login is convenient, but when something goes wrong, it can put everyone at risk all at once. Fake support agents offering to “help you recover your account” will surely show up now—trust only official accounts.
#Keplr #Web3Auth #WalletSecurity
AAPL+0.80%
GOOGUS+0.82%
23

·
--
Bearish
𝒀𝒐𝒖 𝒕𝒉𝒐𝒖𝒈𝒉𝒕 𝒚𝒐𝒖 𝒉𝒆𝒍𝒅 𝒚𝒐𝒖𝒓 𝒌𝒆𝒚𝒔. 𝑨 𝒃𝒖𝒈 𝒋𝒖𝒔𝒕 𝒑𝒓𝒐𝒗𝒆𝒅 𝒚𝒐𝒖 𝒅𝒊𝒅𝒏’𝒕.
This week, a flaw in Web3Auth exposed the private keys of users who signed into their wallets with a 𝐬𝐨𝐜𝐢𝐚𝐥 𝐥𝐨𝐠𝐢𝐧.Keplr told them to move their funds immediately.
No phishing. No leaked seed phrase. No careless click. Just a bug — in the “convenience” layer everyone told you was safe.
When a wallet lets you “sign in with Google,” it doesn’t remove the private key. 𝐈𝐭 𝐡𝐢𝐝𝐞𝐬 𝐢𝐭 —derived and managed through a company’s infrastructure you never audited.
You felt self-custodial. You were 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥 𝐰𝐢𝐭𝐡 𝐞𝐱𝐭𝐫𝐚 𝐬𝐭𝐞𝐩𝐬.
The seed phrase scared newcomers away, so the industry solved it by 𝐛𝐮𝐫𝐲𝐢𝐧𝐠 𝐭𝐡𝐞 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐧, 𝐧𝐨𝐭 𝐫𝐞𝐦𝐨𝐯𝐢𝐧𝐠 𝐢𝐭.“Be your own bank” quietly became “trust our login.” And when their server has a bad week, the user who did everything right still has to race to save their own funds.
Self-custody protects your keys — 𝘰𝘯𝘭𝘺 𝘪𝘧 𝘵𝘩𝘦 𝘬𝘦𝘺𝘴 𝘸𝘦𝘳𝘦 𝘦𝘷𝘦𝘳 𝘢𝘤𝘵𝘶𝘢𝘭𝘭𝘺 𝘺𝘰𝘶𝘳𝘴.
𝐈𝐟 𝐚 𝐥𝐨𝐠𝐢𝐧 𝐛𝐮𝐠 𝐜𝐚𝐧 𝐥𝐞𝐚𝐤 𝐲𝐨𝐮𝐫 𝐩𝐫𝐢𝐯𝐚𝐭𝐞 𝐤𝐞𝐲, 𝐰𝐞𝐫𝐞 𝐲𝐨𝐮 𝐞𝐯𝐞𝐫 𝐬𝐞𝐥𝐟-𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥 — 𝐨𝐫 𝐣𝐮𝐬𝐭 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥, 𝐰𝐢𝐭𝐡 𝐚 𝐧𝐢𝐜𝐞𝐫 𝐢𝐧𝐭𝐞𝐫𝐟𝐚𝐜𝐞?
🐺 𝟕𝟖𝟔 𝐂𝐑𝐘𝐏𝐓𝐎 𝐖𝐎𝐋𝐅 · 𝐑𝐄𝐒𝐄𝐀𝐑𝐂𝐇
Follow the signal, not the noise.
$BTC $ETH
#KeplrAdvisesSocialLoginUsersToTransferAssets
#SelfCustody #CryptoSecurity #Web3Auth #786CryptoWolf
𝒀𝒐𝒖 𝒕𝒉𝒐𝒖𝒈𝒉𝒕 𝒚𝒐𝒖 𝒉𝒆𝒍𝒅 𝒚𝒐𝒖𝒓 𝒌𝒆𝒚𝒔. 𝑨 𝒃𝒖𝒈 𝒋𝒖𝒔𝒕 𝒑𝒓𝒐𝒗𝒆𝒅 𝒚𝒐𝒖 𝒅𝒊𝒅𝒏’𝒕.
This week, a flaw in Web3Auth exposed the private keys of users who signed into their wallets with a 𝐬𝐨𝐜𝐢𝐚𝐥 𝐥𝐨𝐠𝐢𝐧.Keplr told them to move their funds immediately.
No phishing. No leaked seed phrase. No careless click. Just a bug — in the “convenience” layer everyone told you was safe.
When a wallet lets you “sign in with Google,” it doesn’t remove the private key. 𝐈𝐭 𝐡𝐢𝐝𝐞𝐬 𝐢𝐭 —derived and managed through a company’s infrastructure you never audited.
You felt self-custodial. You were 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥 𝐰𝐢𝐭𝐡 𝐞𝐱𝐭𝐫𝐚 𝐬𝐭𝐞𝐩𝐬.
The seed phrase scared newcomers away, so the industry solved it by 𝐛𝐮𝐫𝐲𝐢𝐧𝐠 𝐭𝐡𝐞 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐧, 𝐧𝐨𝐭 𝐫𝐞𝐦𝐨𝐯𝐢𝐧𝐠 𝐢𝐭.“Be your own bank” quietly became “trust our login.” And when their server has a bad week, the user who did everything right still has to race to save their own funds.
Self-custody protects your keys — 𝘰𝘯𝘭𝘺 𝘪𝘧 𝘵𝘩𝘦 𝘬𝘦𝘺𝘴 𝘸𝘦𝘳𝘦 𝘦𝘷𝘦𝘳 𝘢𝘤𝘵𝘶𝘢𝘭𝘭𝘺 𝘺𝘰𝘶𝘳𝘴.
𝐈𝐟 𝐚 𝐥𝐨𝐠𝐢𝐧 𝐛𝐮𝐠 𝐜𝐚𝐧 𝐥𝐞𝐚𝐤 𝐲𝐨𝐮𝐫 𝐩𝐫𝐢𝐯𝐚𝐭𝐞 𝐤𝐞𝐲, 𝐰𝐞𝐫𝐞 𝐲𝐨𝐮 𝐞𝐯𝐞𝐫 𝐬𝐞𝐥𝐟-𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥 — 𝐨𝐫 𝐣𝐮𝐬𝐭 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥, 𝐰𝐢𝐭𝐡 𝐚 𝐧𝐢𝐜𝐞𝐫 𝐢𝐧𝐭𝐞𝐫𝐟𝐚𝐜𝐞?
🐺 𝟕𝟖𝟔 𝐂𝐑𝐘𝐏𝐓𝐎 𝐖𝐎𝐋𝐅 · 𝐑𝐄𝐒𝐄𝐀𝐑𝐂𝐇
Follow the signal, not the noise.
$BTC $ETH
#KeplrAdvisesSocialLoginUsersToTransferAssets
#SelfCustody #CryptoSecurity #Web3Auth #786CryptoWolf
This week, a flaw in Web3Auth exposed the private keys of users who signed into their wallets with a 𝐬𝐨𝐜𝐢𝐚𝐥 𝐥𝐨𝐠𝐢𝐧.Keplr told them to move their funds immediately.
No phishing. No leaked seed phrase. No careless click. Just a bug — in the “convenience” layer everyone told you was safe.
When a wallet lets you “sign in with Google,” it doesn’t remove the private key. 𝐈𝐭 𝐡𝐢𝐝𝐞𝐬 𝐢𝐭 —derived and managed through a company’s infrastructure you never audited.
You felt self-custodial. You were 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥 𝐰𝐢𝐭𝐡 𝐞𝐱𝐭𝐫𝐚 𝐬𝐭𝐞𝐩𝐬.
The seed phrase scared newcomers away, so the industry solved it by 𝐛𝐮𝐫𝐲𝐢𝐧𝐠 𝐭𝐡𝐞 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐧, 𝐧𝐨𝐭 𝐫𝐞𝐦𝐨𝐯𝐢𝐧𝐠 𝐢𝐭.“Be your own bank” quietly became “trust our login.” And when their server has a bad week, the user who did everything right still has to race to save their own funds.
Self-custody protects your keys — 𝘰𝘯𝘭𝘺 𝘪𝘧 𝘵𝘩𝘦 𝘬𝘦𝘺𝘴 𝘸𝘦𝘳𝘦 𝘦𝘷𝘦𝘳 𝘢𝘤𝘵𝘶𝘢𝘭𝘭𝘺 𝘺𝘰𝘶𝘳𝘴.
𝐈𝐟 𝐚 𝐥𝐨𝐠𝐢𝐧 𝐛𝐮𝐠 𝐜𝐚𝐧 𝐥𝐞𝐚𝐤 𝐲𝐨𝐮𝐫 𝐩𝐫𝐢𝐯𝐚𝐭𝐞 𝐤𝐞𝐲, 𝐰𝐞𝐫𝐞 𝐲𝐨𝐮 𝐞𝐯𝐞𝐫 𝐬𝐞𝐥𝐟-𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥 — 𝐨𝐫 𝐣𝐮𝐬𝐭 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥, 𝐰𝐢𝐭𝐡 𝐚 𝐧𝐢𝐜𝐞𝐫 𝐢𝐧𝐭𝐞𝐫𝐟𝐚𝐜𝐞?
🐺 𝟕𝟖𝟔 𝐂𝐑𝐘𝐏𝐓𝐎 𝐖𝐎𝐋𝐅 · 𝐑𝐄𝐒𝐄𝐀𝐑𝐂𝐇
Follow the signal, not the noise.
$BTC $ETH
#KeplrAdvisesSocialLoginUsersToTransferAssets
#SelfCustody #CryptoSecurity #Web3Auth #786CryptoWolf
100
#keplradvisessocialloginuserstotransferassets
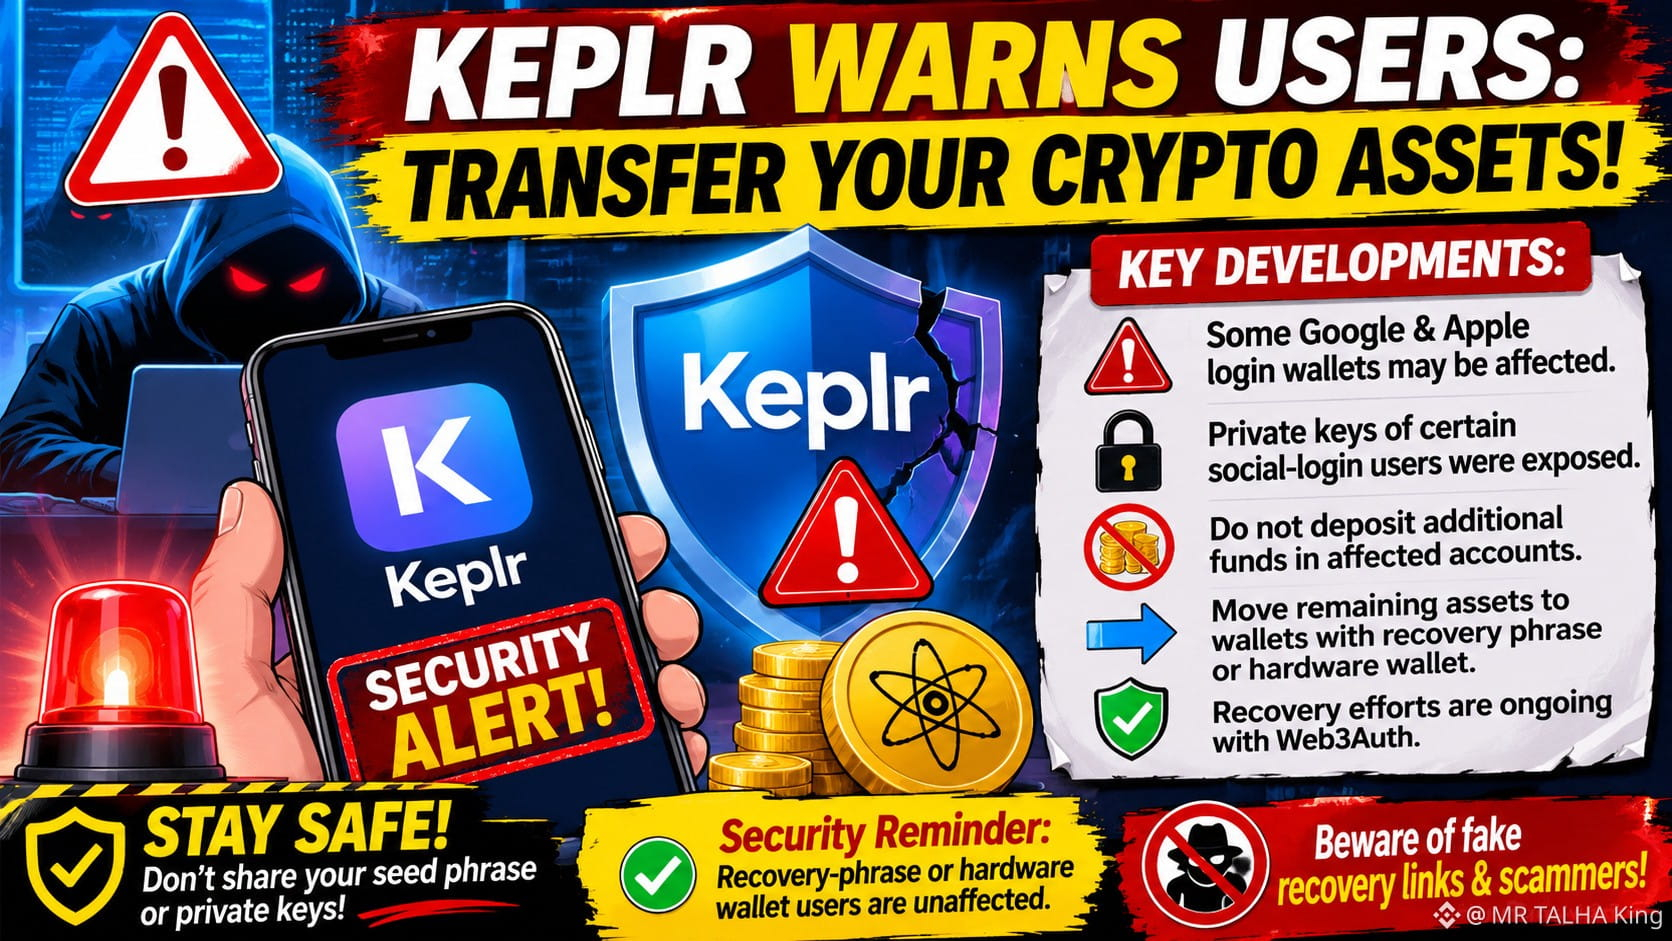
🚨 KEPLR WARNS USERS: TRANSFER YOUR CRYPTO ASSETS! ⚠️🔐
A major security concern has emerged for Keplr Wallet users after a vulnerability in Web3Auth infrastructure reportedly exposed private keys linked to some Google and Apple login accounts.
🔴 Key Developments:
⚠️ Some Google and Apple login wallets may be affected.
🔐 Private keys of certain social-login users were exposed.
💰 Users are advised not to deposit additional funds into potentially affected accounts.
📤 Move remaining liquid assets to wallets secured with a recovery phrase or hardware wallet, following Keplr's official instructions.
🛡️ Recovery and protection efforts are ongoing with Web3Auth.
Important Security Reminder:
Users with recovery-phrase or hardware wallets are currently assessed as unaffected.
🚨 Beware of fake recovery links and scammers. Never share your seed phrase or private keys with anyone.
Is this a warning sign for social-login crypto wallets? 🤔
#Keplr #CryptoSecurity #Web3Auth #CryptoNews
$BTC $ETH $BNB
{spot}(BNBUSDT)
{spot}(ETHUSDT)
{spot}(BTCUSDT)
#keplradvisessocialloginuserstotransferassets
🚨 KEPLR WARNS USERS: TRANSFER YOUR CRYPTO ASSETS! ⚠️🔐
A major security concern has emerged for Keplr Wallet users after a vulnerability in Web3Auth infrastructure reportedly exposed private keys linked to some Google and Apple login accounts.
🔴 Key Developments:
⚠️ Some Google and Apple login wallets may be affected.
🔐 Private keys of certain social-login users were exposed.
💰 Users are advised not to deposit additional funds into potentially affected accounts.
📤 Move remaining liquid assets to wallets secured with a recovery phrase or hardware wallet, following Keplr's official instructions.
🛡️ Recovery and protection efforts are ongoing with Web3Auth.
Important Security Reminder:
Users with recovery-phrase or hardware wallets are currently assessed as unaffected.
🚨 Beware of fake recovery links and scammers. Never share your seed phrase or private keys with anyone.
Is this a warning sign for social-login crypto wallets? 🤔
#Keplr #CryptoSecurity #Web3Auth #CryptoNews
$BTC $ETH $BNB
🚨 KEPLR WARNS USERS: TRANSFER YOUR CRYPTO ASSETS! ⚠️🔐
A major security concern has emerged for Keplr Wallet users after a vulnerability in Web3Auth infrastructure reportedly exposed private keys linked to some Google and Apple login accounts.
🔴 Key Developments:
⚠️ Some Google and Apple login wallets may be affected.
🔐 Private keys of certain social-login users were exposed.
💰 Users are advised not to deposit additional funds into potentially affected accounts.
📤 Move remaining liquid assets to wallets secured with a recovery phrase or hardware wallet, following Keplr's official instructions.
🛡️ Recovery and protection efforts are ongoing with Web3Auth.
Important Security Reminder:
Users with recovery-phrase or hardware wallets are currently assessed as unaffected.
🚨 Beware of fake recovery links and scammers. Never share your seed phrase or private keys with anyone.
Is this a warning sign for social-login crypto wallets? 🤔
#Keplr #CryptoSecurity #Web3Auth #CryptoNews
$BTC $ETH $BNB
Snake info:
karde send id chat
1
1
199
·
--
#KeplrAdvisesSocialLoginUsersToTransferAssets
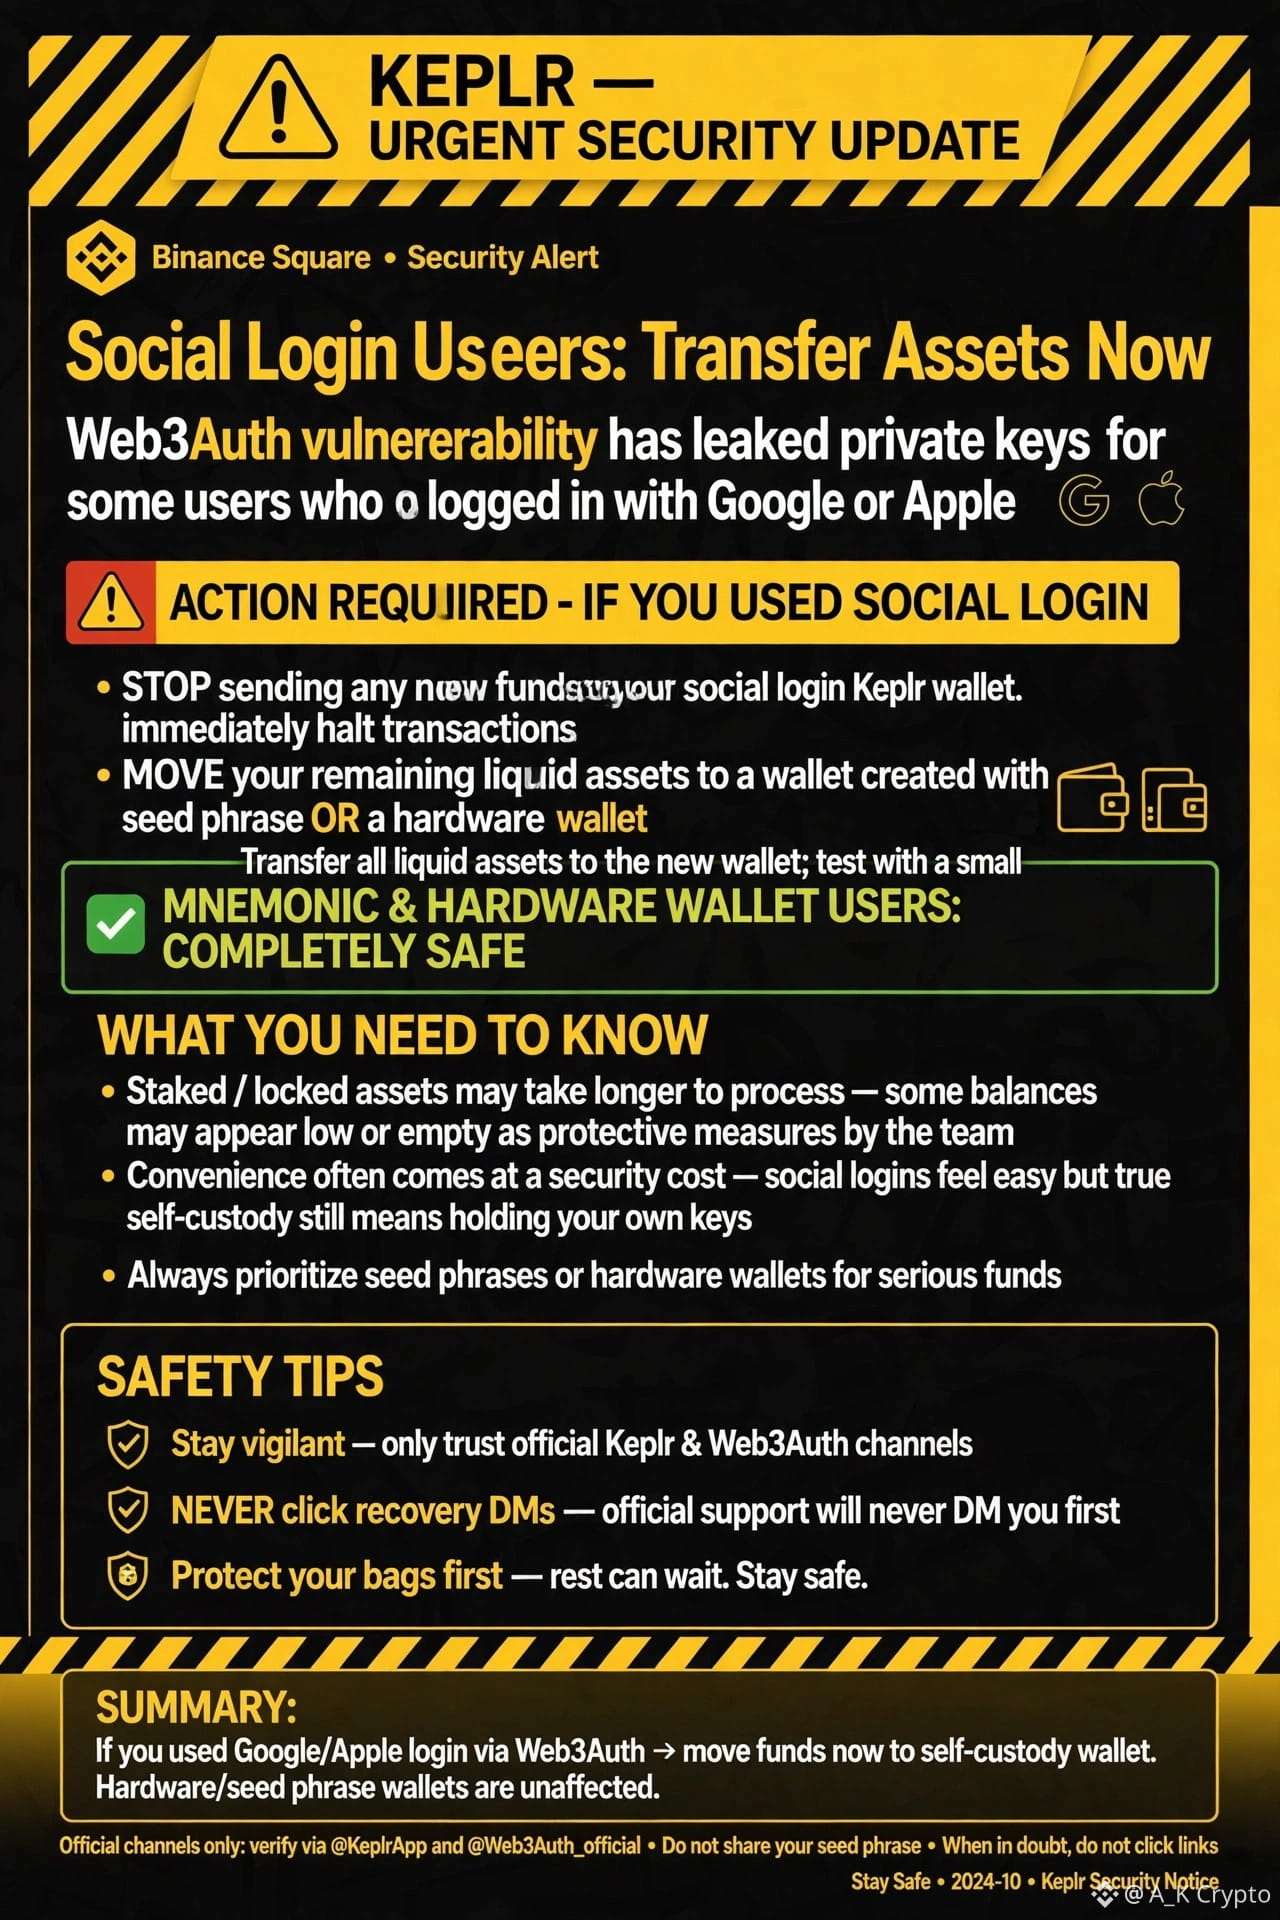
🚨 Keplr just dropped an urgent update: a Web3Auth vulnerability leaked private keys for some users who logged in with Google or Apple.
If you used social login, stop sending any new funds right now and move your remaining liquid assets to a wallet created with a seed phrase or hardware wallet. Mnemonic & hardware users are completely safe. Staked/locked assets may take longer to process, and some balances looking low or empty could be protective measures by the team.
This is another harsh reminder that convenience often comes at a security cost. Social logins feel easy, but true self-custody still means holding your own keys. Always prioritize seed phrases or hardware wallets for any serious funds. Stay vigilant, only trust official Keplr & Web3Auth channels, and never click recovery DMs. Protect your bags first — the rest can wait. Stay safe out there! 🛡️
#Keplr #Web3Auth #CryptoSecurity #Cosmos
#KeplrAdvisesSocialLoginUsersToTransferAssets
🚨 Keplr just dropped an urgent update: a Web3Auth vulnerability leaked private keys for some users who logged in with Google or Apple.
If you used social login, stop sending any new funds right now and move your remaining liquid assets to a wallet created with a seed phrase or hardware wallet. Mnemonic & hardware users are completely safe. Staked/locked assets may take longer to process, and some balances looking low or empty could be protective measures by the team.
This is another harsh reminder that convenience often comes at a security cost. Social logins feel easy, but true self-custody still means holding your own keys. Always prioritize seed phrases or hardware wallets for any serious funds. Stay vigilant, only trust official Keplr & Web3Auth channels, and never click recovery DMs. Protect your bags first — the rest can wait. Stay safe out there! 🛡️
#Keplr #Web3Auth #CryptoSecurity #Cosmos
🚨 Keplr just dropped an urgent update: a Web3Auth vulnerability leaked private keys for some users who logged in with Google or Apple.
If you used social login, stop sending any new funds right now and move your remaining liquid assets to a wallet created with a seed phrase or hardware wallet. Mnemonic & hardware users are completely safe. Staked/locked assets may take longer to process, and some balances looking low or empty could be protective measures by the team.
This is another harsh reminder that convenience often comes at a security cost. Social logins feel easy, but true self-custody still means holding your own keys. Always prioritize seed phrases or hardware wallets for any serious funds. Stay vigilant, only trust official Keplr & Web3Auth channels, and never click recovery DMs. Protect your bags first — the rest can wait. Stay safe out there! 🛡️
#Keplr #Web3Auth #CryptoSecurity #Cosmos
156
·
--
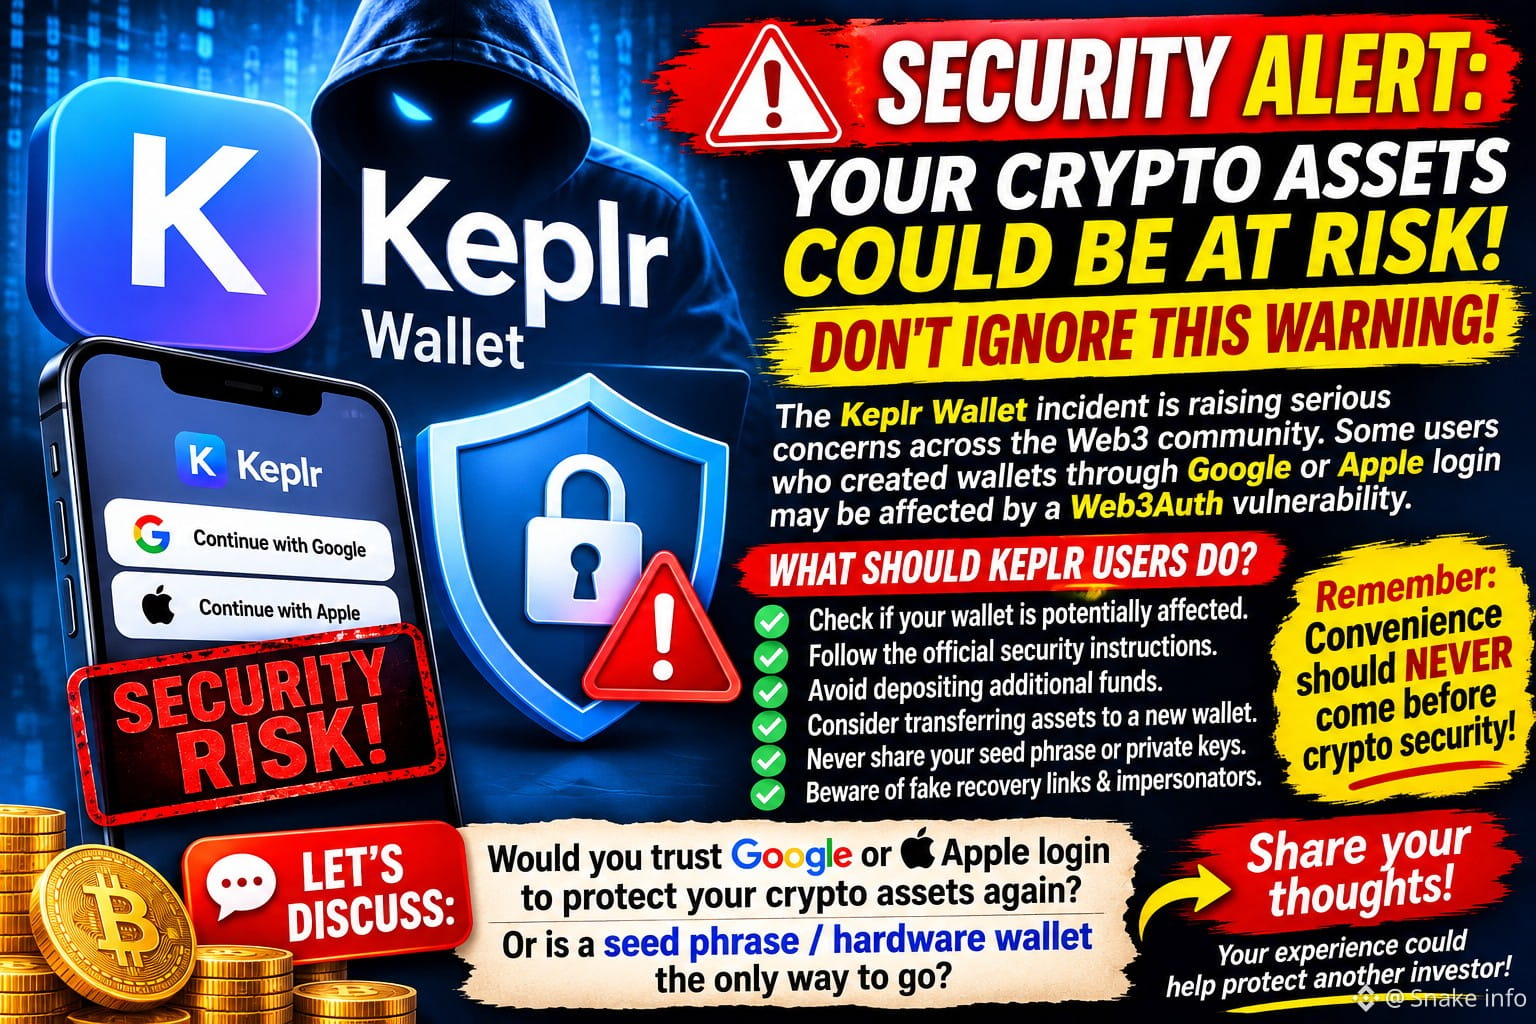
#keplradvisessocialloginuserstotransferassets 🚨 KEPLR WALLET SECURITY ALERT: IS YOUR CRYPTO AT RISK? ⚠️
A security incident involving Keplr Wallet is raising serious concerns across the Web3 community.
Reports indicate that a vulnerability in Web3Auth infrastructure may have affected some users who created wallets using Google or Apple social login.
🔐 WHAT SHOULD KEPLR USERS DO?
1️⃣ Check whether your wallet is potentially affected.
2️⃣ Follow the official security instructions issued by Keplr.
3️⃣ Avoid depositing additional funds into potentially affected wallets.
4️⃣ If advised, transfer eligible assets to a newly secured wallet.
5️⃣ Never share your seed phrase or private keys.
6️⃣ Stay alert for fake recovery websites, phishing links, and impersonators.
🛡️ IMPORTANT SECURITY REMINDER
Your crypto security should never depend on convenience alone. Always protect your recovery phrase and consider using a hardware wallet for long-term storage.
🔥 THE BIG QUESTION:
Would you still trust Google or Apple social login for managing your crypto wallet?
Or do you believe a traditional seed phrase and hardware wallet offer better security?
💬 Share your opinion below. Your experience could help protect another crypto investor!
#KeplrWallet #CryptoSecurity #Web3 #Web3Auth
Stay safe. Verify information through official sources. Not financial advice.
CLICK TO BELOW TRADE👇
$BTC $HYPE $ONE
{future}(ONEUSDT)
{future}(HYPEUSDT)
{future}(BTCUSDT)
#keplradvisessocialloginuserstotransferassets 🚨 KEPLR WALLET SECURITY ALERT: IS YOUR CRYPTO AT RISK? ⚠️
A security incident involving Keplr Wallet is raising serious concerns across the Web3 community.
Reports indicate that a vulnerability in Web3Auth infrastructure may have affected some users who created wallets using Google or Apple social login.
🔐 WHAT SHOULD KEPLR USERS DO?
1️⃣ Check whether your wallet is potentially affected.
2️⃣ Follow the official security instructions issued by Keplr.
3️⃣ Avoid depositing additional funds into potentially affected wallets.
4️⃣ If advised, transfer eligible assets to a newly secured wallet.
5️⃣ Never share your seed phrase or private keys.
6️⃣ Stay alert for fake recovery websites, phishing links, and impersonators.
🛡️ IMPORTANT SECURITY REMINDER
Your crypto security should never depend on convenience alone. Always protect your recovery phrase and consider using a hardware wallet for long-term storage.
🔥 THE BIG QUESTION:
Would you still trust Google or Apple social login for managing your crypto wallet?
Or do you believe a traditional seed phrase and hardware wallet offer better security?
💬 Share your opinion below. Your experience could help protect another crypto investor!
#KeplrWallet #CryptoSecurity #Web3 #Web3Auth
Stay safe. Verify information through official sources. Not financial advice.
CLICK TO BELOW TRADE👇
$BTC $HYPE $ONE
A security incident involving Keplr Wallet is raising serious concerns across the Web3 community.
Reports indicate that a vulnerability in Web3Auth infrastructure may have affected some users who created wallets using Google or Apple social login.
🔐 WHAT SHOULD KEPLR USERS DO?
1️⃣ Check whether your wallet is potentially affected.
2️⃣ Follow the official security instructions issued by Keplr.
3️⃣ Avoid depositing additional funds into potentially affected wallets.
4️⃣ If advised, transfer eligible assets to a newly secured wallet.
5️⃣ Never share your seed phrase or private keys.
6️⃣ Stay alert for fake recovery websites, phishing links, and impersonators.
🛡️ IMPORTANT SECURITY REMINDER
Your crypto security should never depend on convenience alone. Always protect your recovery phrase and consider using a hardware wallet for long-term storage.
🔥 THE BIG QUESTION:
Would you still trust Google or Apple social login for managing your crypto wallet?
Or do you believe a traditional seed phrase and hardware wallet offer better security?
💬 Share your opinion below. Your experience could help protect another crypto investor!
#KeplrWallet #CryptoSecurity #Web3 #Web3Auth
Stay safe. Verify information through official sources. Not financial advice.
CLICK TO BELOW TRADE👇
$BTC $HYPE $ONE
1
986
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#NvidiaInvestigatesAfterHuang’sAffairApology
25,946 views
334 Discussing
2
#BitcoinFiveWeeklyLosses
41,234 views
763 Discussing
3
#AIChipSlumpNasdaq
23,131 views
429 Discussing
4
#SouthKoreaSupremeCourtClarifiesVirtualAssetSeizureRules
27 views
5 Discussing
5
#EthereumSpotETFsPost$365MWeeklyOutflow
1,015 views
30 Discussing
6
#TradFiForBeginners
263,761 views
2,345 Discussing
7
#GalxeToIntegrateIntoGravityGraduallyCloseQuest
61 views
15 Discussing
8
#KeplrAdvisesSocialLoginUsersToTransferAssets
90,883 views
678 Discussing
9
#TetherPlans€28.8MForJuventusCapitalIncrease
60,955 views
494 Discussing
10
#JobsReportRaisesHikeOdds
1M views
4,690 Discussing