
#keplr
keplr
47,318 views
63 Discussing
Hot
Latest
#keplradvisessocialloginuserstotransferassets
🚨 Keplr Warns Social Login Users: Transfer Your Assets Before It's Too Late!
Keplr has issued an important warning to users who access their wallets through social login.
Users relying on social login should take action and transfer their assets to a securely backed-up wallet before they risk losing access.
🔍 What You Need to Know:
Social login users should review their wallet access immediately.
Make sure your recovery credentials and wallet backup are secure.
Transfer assets to a wallet where you control and safely store the recovery phrase.
Never share your seed phrase or private keys with anyone.
⚠️ Why It Matters:
Your crypto security depends on controlling access to your wallet. Losing access to a social login account could create serious problems if you haven't secured your wallet recovery options.
The message is simple: don't wait until you lose access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
#keplradvisessocialloginuserstotransferassets
🚨 Keplr Warns Social Login Users: Transfer Your Assets Before It's Too Late!
Keplr has issued an important warning to users who access their wallets through social login.
Users relying on social login should take action and transfer their assets to a securely backed-up wallet before they risk losing access.
🔍 What You Need to Know:
Social login users should review their wallet access immediately.
Make sure your recovery credentials and wallet backup are secure.
Transfer assets to a wallet where you control and safely store the recovery phrase.
Never share your seed phrase or private keys with anyone.
⚠️ Why It Matters:
Your crypto security depends on controlling access to your wallet. Losing access to a social login account could create serious problems if you haven't secured your wallet recovery options.
The message is simple: don't wait until you lose access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
🚨 Keplr Warns Social Login Users: Transfer Your Assets Before It's Too Late!
Keplr has issued an important warning to users who access their wallets through social login.
Users relying on social login should take action and transfer their assets to a securely backed-up wallet before they risk losing access.
🔍 What You Need to Know:
Social login users should review their wallet access immediately.
Make sure your recovery credentials and wallet backup are secure.
Transfer assets to a wallet where you control and safely store the recovery phrase.
Never share your seed phrase or private keys with anyone.
⚠️ Why It Matters:
Your crypto security depends on controlling access to your wallet. Losing access to a social login account could create serious problems if you haven't secured your wallet recovery options.
The message is simple: don't wait until you lose access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
1
899
#KeplrAdvisesSocialLoginUsersToTransferAssets
🚨⚠️ SECURITY ALERT: YOUR CRYPTO ASSETS COULD BE AT RISK! DON'T IGNORE THIS WARNING!
The Keplr Wallet incident is raising serious concerns across the Web3 community.
Some users who created wallets through Google or Apple social login may be affected by a Web3Auth infrastructure vulnerability.
🔥 What should users know?
🔹 Potentially affected users should follow Keplr's official security instructions.
🔹 Avoid depositing additional funds into affected wallets.
🔹 Consider transferring eligible assets to a newly secured wallet.
🔹 Never share your seed phrase or private keys with anyone.
🔹 Beware of fake recovery links and impersonators.
🛡️ Remember: Convenience should NEVER come before crypto security!
💬 Let's discuss:
Would you trust Google or Apple login to protect your crypto assets again?
Or is a seed phrase / hardware wallet the only way to go?
👇 Share your thoughts. Your experience could help protect another investor!
#Keplr #CryptoSecurity #Web3
$BTC
{future}(BTCUSDT)
$HYPE
{future}(HYPEUSDT)
$ONE
{future}(ONEUSDT)
#KeplrAdvisesSocialLoginUsersToTransferAssets
🚨⚠️ SECURITY ALERT: YOUR CRYPTO ASSETS COULD BE AT RISK! DON'T IGNORE THIS WARNING!
The Keplr Wallet incident is raising serious concerns across the Web3 community.
Some users who created wallets through Google or Apple social login may be affected by a Web3Auth infrastructure vulnerability.
🔥 What should users know?
🔹 Potentially affected users should follow Keplr's official security instructions.
🔹 Avoid depositing additional funds into affected wallets.
🔹 Consider transferring eligible assets to a newly secured wallet.
🔹 Never share your seed phrase or private keys with anyone.
🔹 Beware of fake recovery links and impersonators.
🛡️ Remember: Convenience should NEVER come before crypto security!
💬 Let's discuss:
Would you trust Google or Apple login to protect your crypto assets again?
Or is a seed phrase / hardware wallet the only way to go?
👇 Share your thoughts. Your experience could help protect another investor!
#Keplr #CryptoSecurity #Web3
$BTC
$HYPE
$ONE
🚨⚠️ SECURITY ALERT: YOUR CRYPTO ASSETS COULD BE AT RISK! DON'T IGNORE THIS WARNING!
The Keplr Wallet incident is raising serious concerns across the Web3 community.
Some users who created wallets through Google or Apple social login may be affected by a Web3Auth infrastructure vulnerability.
🔥 What should users know?
🔹 Potentially affected users should follow Keplr's official security instructions.
🔹 Avoid depositing additional funds into affected wallets.
🔹 Consider transferring eligible assets to a newly secured wallet.
🔹 Never share your seed phrase or private keys with anyone.
🔹 Beware of fake recovery links and impersonators.
🛡️ Remember: Convenience should NEVER come before crypto security!
💬 Let's discuss:
Would you trust Google or Apple login to protect your crypto assets again?
Or is a seed phrase / hardware wallet the only way to go?
👇 Share your thoughts. Your experience could help protect another investor!
#Keplr #CryptoSecurity #Web3
$BTC
$HYPE
$ONE
526

·
--
A $6M wallet drain just hit over 44,000 Keplr wallets.
Reported breach of Web3Auth, the login layer behind many wallets, per COINOTAG.
Not a price crash, not a rug. One shared sign-in dependency.
It lands in a week where Binance's record hack and exchange crackdowns already have traders rethinking where keys and funds sit.
Takeaway: the weakest link is often the login, not the chain. Review connected apps and revoke what you don't use.
Which worries you more: exchange custody risk or wallet login/social-recovery risk?
$ATOM $BTC
#CryptoSecurity #Keplr #Web3 #SelfCustody
A $6M wallet drain just hit over 44,000 Keplr wallets.
Reported breach of Web3Auth, the login layer behind many wallets, per COINOTAG.
Not a price crash, not a rug. One shared sign-in dependency.
It lands in a week where Binance's record hack and exchange crackdowns already have traders rethinking where keys and funds sit.
Takeaway: the weakest link is often the login, not the chain. Review connected apps and revoke what you don't use.
Which worries you more: exchange custody risk or wallet login/social-recovery risk?
$ATOM $BTC
#CryptoSecurity #Keplr #Web3 #SelfCustody
Reported breach of Web3Auth, the login layer behind many wallets, per COINOTAG.
Not a price crash, not a rug. One shared sign-in dependency.
It lands in a week where Binance's record hack and exchange crackdowns already have traders rethinking where keys and funds sit.
Takeaway: the weakest link is often the login, not the chain. Review connected apps and revoke what you don't use.
Which worries you more: exchange custody risk or wallet login/social-recovery risk?
$ATOM $BTC
#CryptoSecurity #Keplr #Web3 #SelfCustody
1

·
--
#KeplrAdvisesSocialLoginUsersToTransferAssets
🔄 Keplr Changed Its Advice: Move What's Left Now
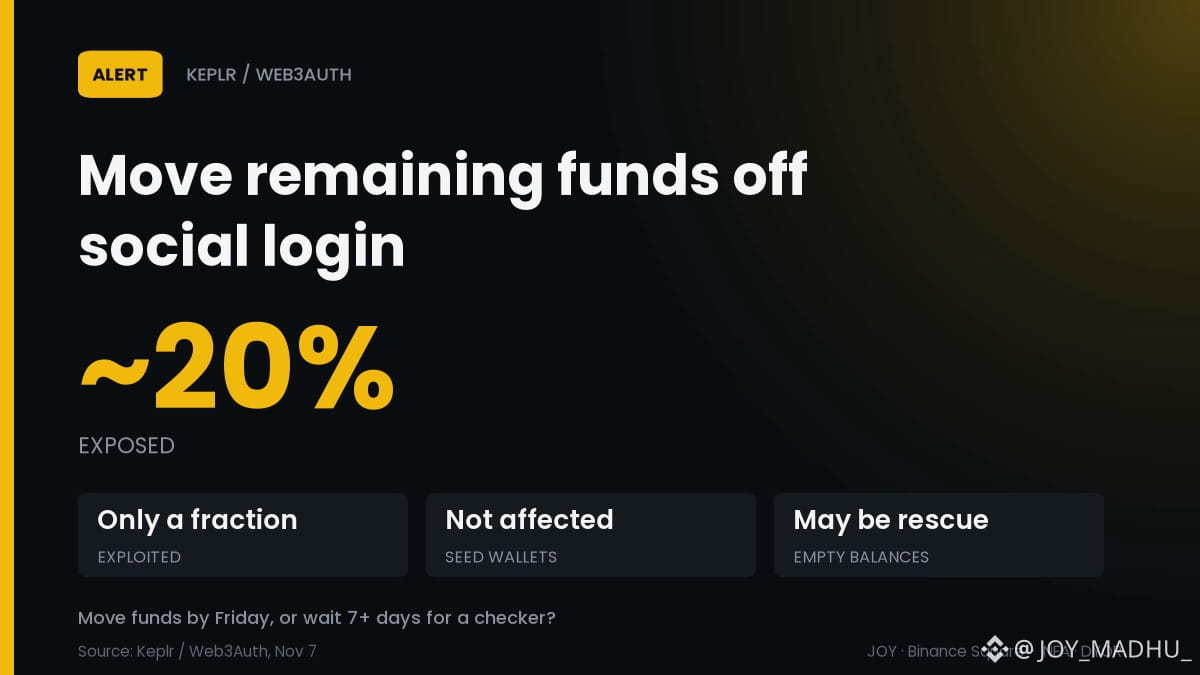
A Web3Auth flaw exposed some Google and Apple login keys, so Keplr now tells those users to move remaining assets.
📊 Early estimate: about 20% of social-login accounts were exposed
⚠️ Only a fraction of that 20% appears fully exploited
🏦 Seed-phrase and hardware-wallet accounts were not affected
📉 Some empty balances may be a white-hat rescue, not the theft
Zoom out: the breach sat at the login provider, not seed wallets.
Move funds by Friday, or wait 7+ days for a checker? 👇
$ATOM
#KeplrAdvisesSocialLoginUsersToTransferAssets #Keplr #Security
#KeplrAdvisesSocialLoginUsersToTransferAssets
🔄 Keplr Changed Its Advice: Move What's Left Now
A Web3Auth flaw exposed some Google and Apple login keys, so Keplr now tells those users to move remaining assets.
📊 Early estimate: about 20% of social-login accounts were exposed
⚠️ Only a fraction of that 20% appears fully exploited
🏦 Seed-phrase and hardware-wallet accounts were not affected
📉 Some empty balances may be a white-hat rescue, not the theft
Zoom out: the breach sat at the login provider, not seed wallets.
Move funds by Friday, or wait 7+ days for a checker? 👇
$ATOM
#KeplrAdvisesSocialLoginUsersToTransferAssets #Keplr #Security
🔄 Keplr Changed Its Advice: Move What's Left Now
A Web3Auth flaw exposed some Google and Apple login keys, so Keplr now tells those users to move remaining assets.
📊 Early estimate: about 20% of social-login accounts were exposed
⚠️ Only a fraction of that 20% appears fully exploited
🏦 Seed-phrase and hardware-wallet accounts were not affected
📉 Some empty balances may be a white-hat rescue, not the theft
Zoom out: the breach sat at the login provider, not seed wallets.
Move funds by Friday, or wait 7+ days for a checker? 👇
$ATOM
#KeplrAdvisesSocialLoginUsersToTransferAssets #Keplr #Security
1
·
--
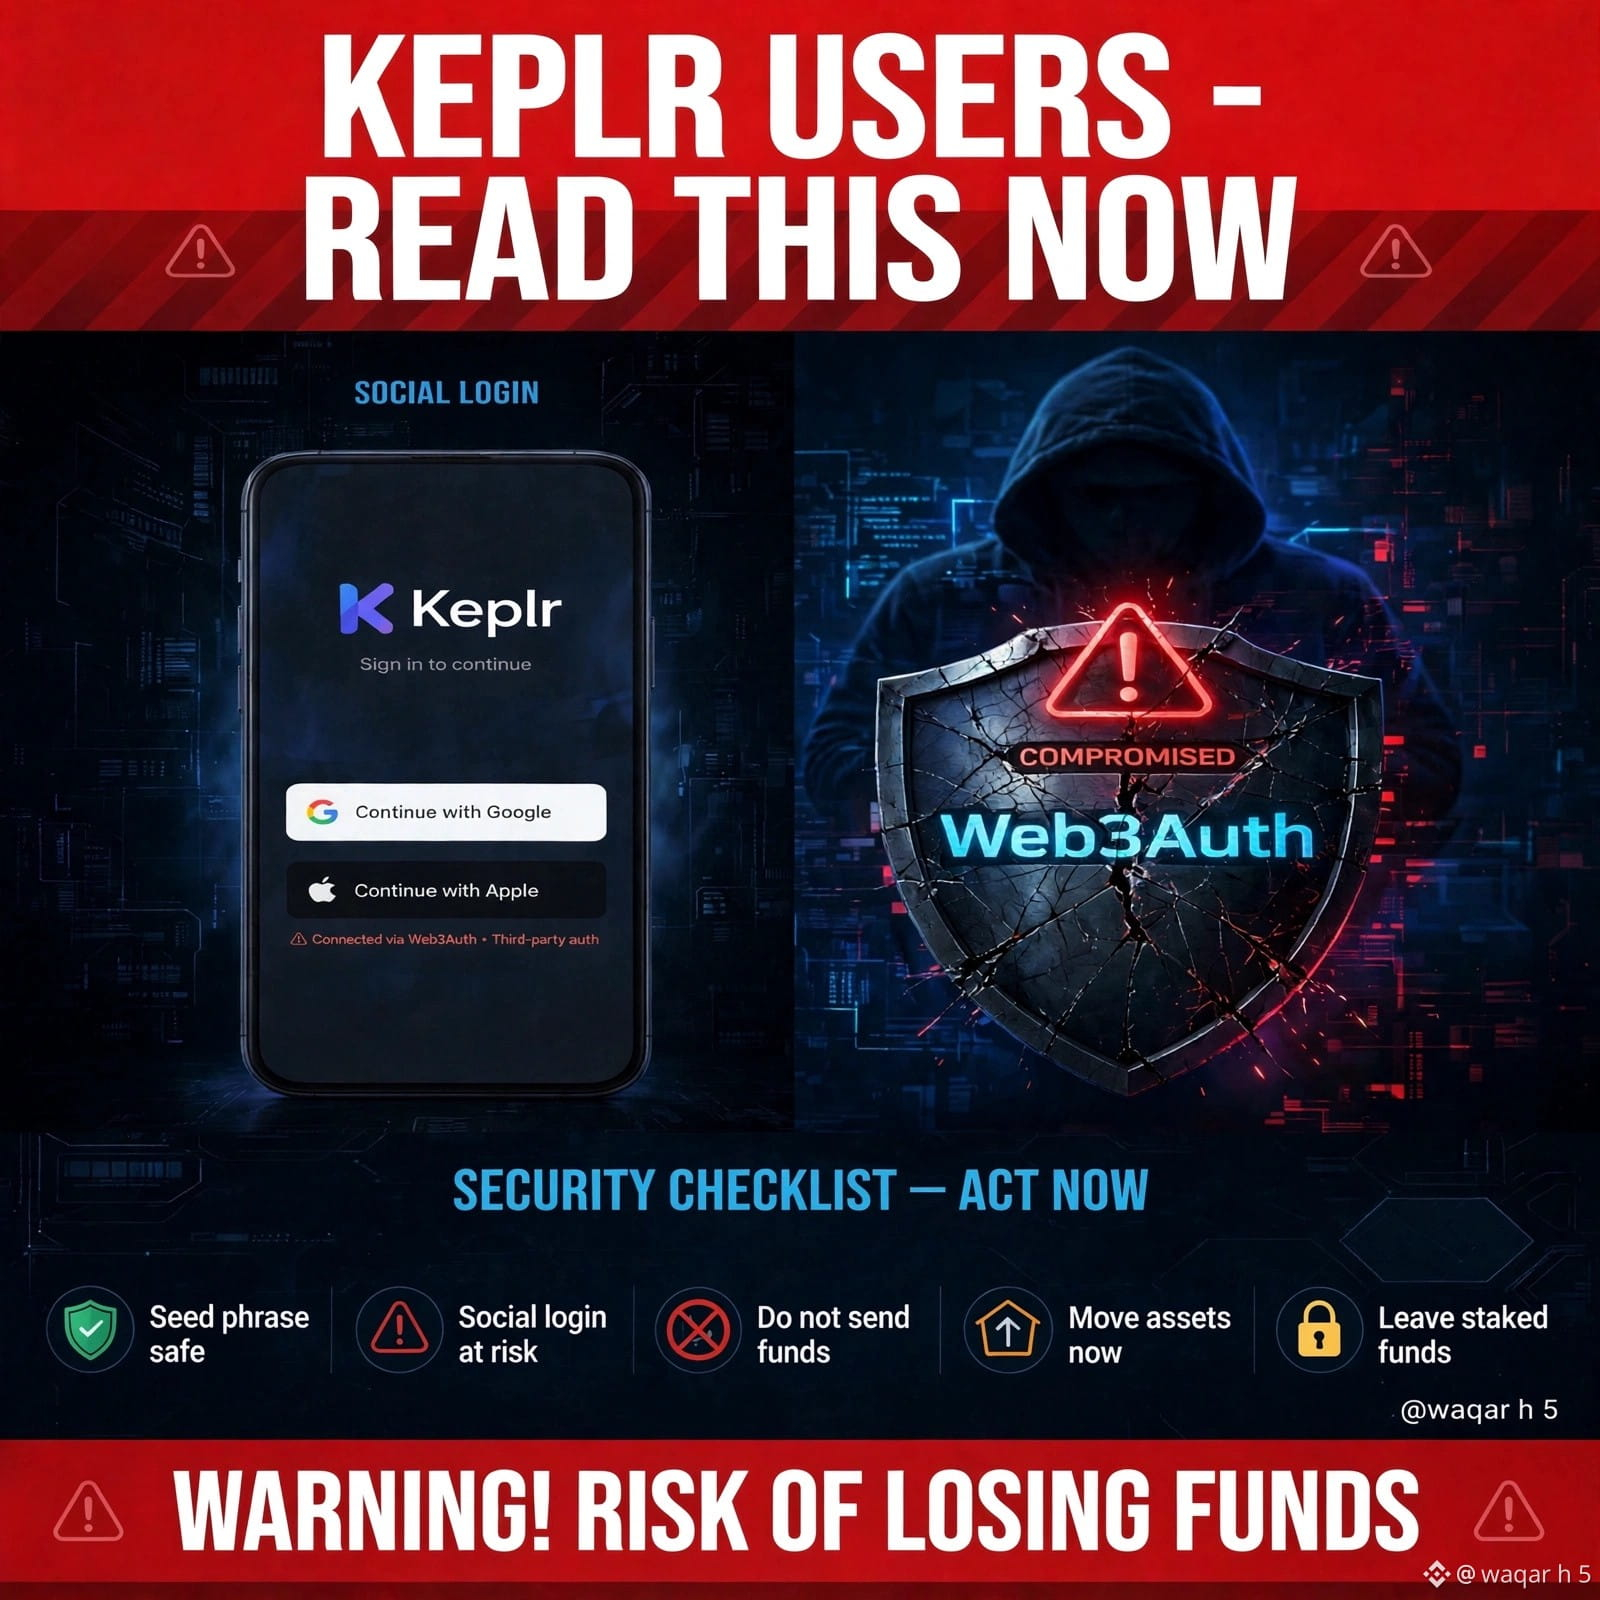
🚨 URGENT: Keplr Security Alert! 🚨
If you logged in to Keplr with Google / Apple — READ THIS!
A Web3Auth vulnerability leaked private keys for some social login users. Your funds may be at risk!
✅ DO THIS NOW:
1. STOP sending funds to old wallet
2. MOVE assets to a new wallet with seed phrase
3. USE hardware wallet for serious funds
Don't wait — Secure your bags first!
#keplr #CryptoSecurity #SecurityAlert
#KeplrAdvisesSocialLoginUsersToTransferAssets
🚨 URGENT: Keplr Security Alert! 🚨
If you logged in to Keplr with Google / Apple — READ THIS!
A Web3Auth vulnerability leaked private keys for some social login users. Your funds may be at risk!
✅ DO THIS NOW:
1. STOP sending funds to old wallet
2. MOVE assets to a new wallet with seed phrase
3. USE hardware wallet for serious funds
Don't wait — Secure your bags first!
#keplr #CryptoSecurity #SecurityAlert
#KeplrAdvisesSocialLoginUsersToTransferAssets
If you logged in to Keplr with Google / Apple — READ THIS!
A Web3Auth vulnerability leaked private keys for some social login users. Your funds may be at risk!
✅ DO THIS NOW:
1. STOP sending funds to old wallet
2. MOVE assets to a new wallet with seed phrase
3. USE hardware wallet for serious funds
Don't wait — Secure your bags first!
#keplr #CryptoSecurity #SecurityAlert
#KeplrAdvisesSocialLoginUsersToTransferAssets
4
232

Article
MASSIVE HACK OF KEPLR CRYPTO WALLETS WORTH $6M, MORE THAN 44,000 WALLETS AT RISK!The cryptocurrency industry has faced yet another major security incident. On November 6–7, 2026, Keplr wallet users began reporting unauthorized transfers of funds. Accounts created using Google and Apple sign-in were affected.
According to blockchain analytics firm Bitquery, which investigated fund movements on Cosmos ecosystem blockchains, suspicious transactions affected more than 44,000 wallets, and the value of the assets transferred reached approximately $6.01 million.
MASSIVE HACK OF KEPLR CRYPTO WALLETS WORTH $6M, MORE THAN 44,000 WALLETS AT RISK!
The cryptocurrency industry has faced yet another major security incident. On November 6–7, 2026, Keplr wallet users began reporting unauthorized transfers of funds. Accounts created using Google and Apple sign-in were affected.
According to blockchain analytics firm Bitquery, which investigated fund movements on Cosmos ecosystem blockchains, suspicious transactions affected more than 44,000 wallets, and the value of the assets transferred reached approximately $6.01 million.
According to blockchain analytics firm Bitquery, which investigated fund movements on Cosmos ecosystem blockchains, suspicious transactions affected more than 44,000 wallets, and the value of the assets transferred reached approximately $6.01 million.
1
3.2k

·
--
Over $6 million drained from at least 44,000 wallets using Google login
▫️Keplr confirmed unauthorized transfers from accounts signed in with Google or Apple; the issue lies with the social login service Web3Auth
▫️On-chain data shows at least 44,000 wallets affected, with about $6.01 million involved; the funds have not yet been transferred out
▫️Even after the official warning, 86% of the victims’ wallets were still drained
▫️The attackers also bypassed the 21-day unbonding period and withdrew about 1.96 million staked ATOM
Accounts using seed phrases or hardware wallets don’t appear to have been affected so far; these two social login options have been suspended
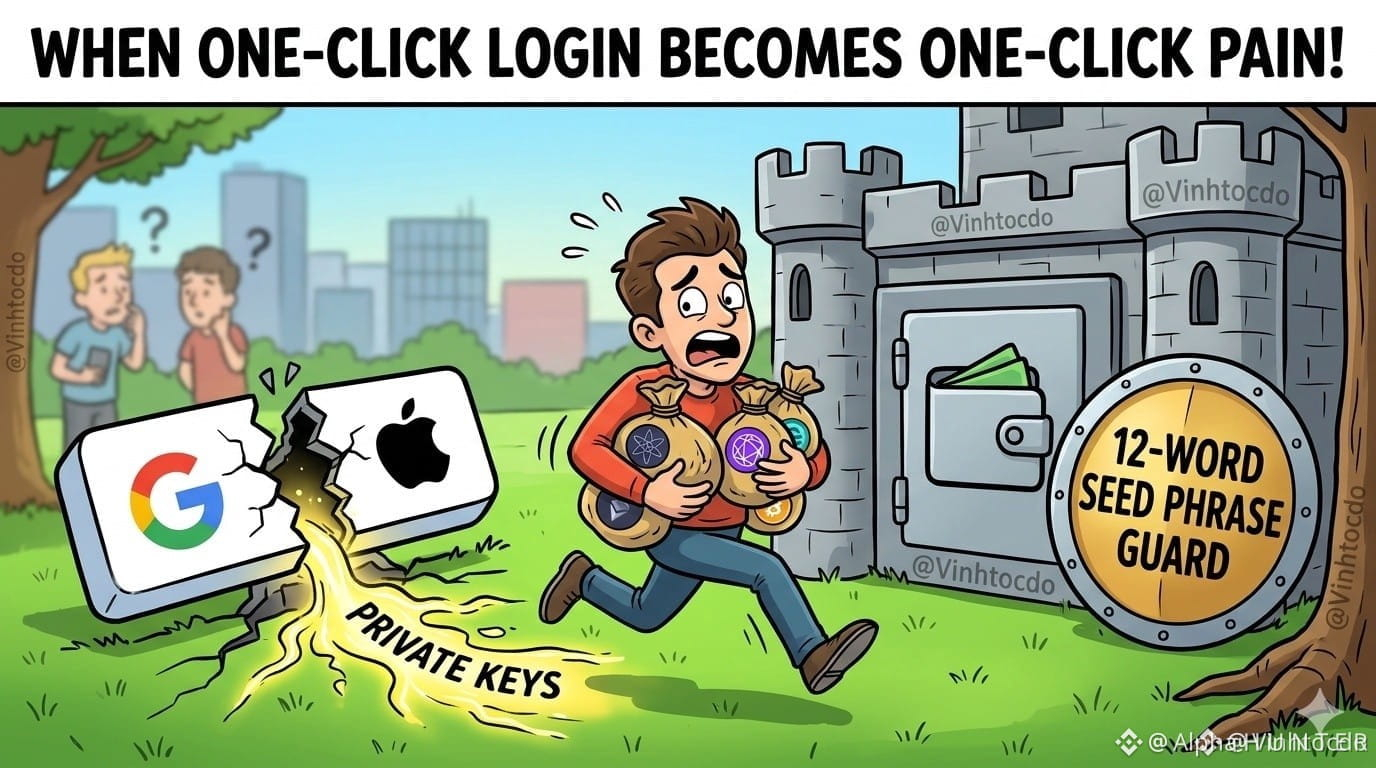
One-click login is convenient, but you may not actually hold the keys
Will you still feel comfortable logging into your wallet with a social account? 👇 (Not investment advice)
#Keplr #Web3Auth #WalletSecurity
Over $6 million drained from at least 44,000 wallets using Google login
▫️Keplr confirmed unauthorized transfers from accounts signed in with Google or Apple; the issue lies with the social login service Web3Auth
▫️On-chain data shows at least 44,000 wallets affected, with about $6.01 million involved; the funds have not yet been transferred out
▫️Even after the official warning, 86% of the victims’ wallets were still drained
▫️The attackers also bypassed the 21-day unbonding period and withdrew about 1.96 million staked ATOM
Accounts using seed phrases or hardware wallets don’t appear to have been affected so far; these two social login options have been suspended
One-click login is convenient, but you may not actually hold the keys
Will you still feel comfortable logging into your wallet with a social account? 👇 (Not investment advice)
#Keplr #Web3Auth #WalletSecurity
▫️Keplr confirmed unauthorized transfers from accounts signed in with Google or Apple; the issue lies with the social login service Web3Auth
▫️On-chain data shows at least 44,000 wallets affected, with about $6.01 million involved; the funds have not yet been transferred out
▫️Even after the official warning, 86% of the victims’ wallets were still drained
▫️The attackers also bypassed the 21-day unbonding period and withdrew about 1.96 million staked ATOM
Accounts using seed phrases or hardware wallets don’t appear to have been affected so far; these two social login options have been suspended
One-click login is convenient, but you may not actually hold the keys
Will you still feel comfortable logging into your wallet with a social account? 👇 (Not investment advice)
#Keplr #Web3Auth #WalletSecurity
2
2.3k

·
--
Article
If you use your Google account to log in to your wallet, today’s news concerns youThis afternoon, Keplr, a wallet in the Cosmos ecosystem, posted an announcement. Some wallets created by signing in with a Google or Apple account have seen transfers that users did not authorize. Keplr has paused both Google and Apple sign-in while it investigates the cause with Web3Auth, the provider of its login technology. Web3Auth has also acknowledged the issue. Just after 11 p.m. last night, it issued a statement saying its service had a security issue and that its embedded wallet service had been suspended.
The problem is with the login process, not the wallet itself. Web3Auth lets you create a wallet using your Google or Apple account without writing down a recovery phrase. It’s convenient, but it means your wallet keys are effectively held by this intermediary layer. If something goes wrong there, your money can be transferred without you confirming it. Keplr’s Josh Lee preliminarily estimates that about 20% of accounts using Google or Apple sign-in were affected. Of those, only some actually had money transferred out; the rest may still be recoverable. These are only preliminary estimates. The team has yet to disclose how many people were affected or how much money was lost.
If you use your Google account to log in to your wallet, today’s news concerns you
This afternoon, Keplr, a wallet in the Cosmos ecosystem, posted an announcement. Some wallets created by signing in with a Google or Apple account have seen transfers that users did not authorize. Keplr has paused both Google and Apple sign-in while it investigates the cause with Web3Auth, the provider of its login technology. Web3Auth has also acknowledged the issue. Just after 11 p.m. last night, it issued a statement saying its service had a security issue and that its embedded wallet service had been suspended.
The problem is with the login process, not the wallet itself. Web3Auth lets you create a wallet using your Google or Apple account without writing down a recovery phrase. It’s convenient, but it means your wallet keys are effectively held by this intermediary layer. If something goes wrong there, your money can be transferred without you confirming it. Keplr’s Josh Lee preliminarily estimates that about 20% of accounts using Google or Apple sign-in were affected. Of those, only some actually had money transferred out; the rest may still be recoverable. These are only preliminary estimates. The team has yet to disclose how many people were affected or how much money was lost.
The problem is with the login process, not the wallet itself. Web3Auth lets you create a wallet using your Google or Apple account without writing down a recovery phrase. It’s convenient, but it means your wallet keys are effectively held by this intermediary layer. If something goes wrong there, your money can be transferred without you confirming it. Keplr’s Josh Lee preliminarily estimates that about 20% of accounts using Google or Apple sign-in were affected. Of those, only some actually had money transferred out; the rest may still be recoverable. These are only preliminary estimates. The team has yet to disclose how many people were affected or how much money was lost.
GOOGUS+1.10%
必备小神器888:
谷歌登录钱包本质是便利换安全,大额别放,等Web3Auth把根因查清再谈信任。
1
799
#keplradvisessocialloginuserstotransferassets
🚨 Keplr warns users who log in via social networks: transfer your assets before it’s too late!
Keplr has issued an important warning to users who access their wallets by logging in with a social media account.
Users who rely on this method should act and transfer their assets to a wallet with a secure backup before they risk losing access.
🔍 What you need to know:
Users who log in via social networks should immediately check their access to their wallet.
Make sure your recovery credentials and wallet backup are secure.
Transfer your assets to a wallet whose recovery phrase you control and can keep in a safe place.
Never share your recovery phrase or private keys with anyone.
⚠️ Why is this important?
The security of your cryptocurrencies depends on your control over access to your wallet. Losing access to a social media account could cause serious problems if you haven’t secured your wallet’s recovery options.
The message is simple: don’t wait until you’ve lost access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
$AIOT
{future}(AIOTUSDT)
$JCT
{future}(JCTUSDT)
$IDOL
{future}(IDOLUSDT)
#keplradvisessocialloginuserstotransferassets
🚨 Keplr warns users who log in via social networks: transfer your assets before it’s too late!
Keplr has issued an important warning to users who access their wallets by logging in with a social media account.
Users who rely on this method should act and transfer their assets to a wallet with a secure backup before they risk losing access.
🔍 What you need to know:
Users who log in via social networks should immediately check their access to their wallet.
Make sure your recovery credentials and wallet backup are secure.
Transfer your assets to a wallet whose recovery phrase you control and can keep in a safe place.
Never share your recovery phrase or private keys with anyone.
⚠️ Why is this important?
The security of your cryptocurrencies depends on your control over access to your wallet. Losing access to a social media account could cause serious problems if you haven’t secured your wallet’s recovery options.
The message is simple: don’t wait until you’ve lost access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
$AIOT
$JCT
$IDOL
🚨 Keplr warns users who log in via social networks: transfer your assets before it’s too late!
Keplr has issued an important warning to users who access their wallets by logging in with a social media account.
Users who rely on this method should act and transfer their assets to a wallet with a secure backup before they risk losing access.
🔍 What you need to know:
Users who log in via social networks should immediately check their access to their wallet.
Make sure your recovery credentials and wallet backup are secure.
Transfer your assets to a wallet whose recovery phrase you control and can keep in a safe place.
Never share your recovery phrase or private keys with anyone.
⚠️ Why is this important?
The security of your cryptocurrencies depends on your control over access to your wallet. Losing access to a social media account could cause serious problems if you haven’t secured your wallet’s recovery options.
The message is simple: don’t wait until you’ve lost access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
$AIOT
$JCT
$IDOL
4
2.3k
·
--
Keplr has paused Google and Apple social logins after users reported transfers they hadn’t made. Keplr says the issue was with the underlying Web3Auth service, where private keys were exposed. Web3Auth confirmed a security incident on November 6 and paused its embedded wallet service. A Keplr co-founder estimates that around 20% of social login accounts may be affected, but neither company has disclosed the amount of losses so far.
Accounts created with a recovery phrase or hardware wallet are not affected. My advice is simple: if you keep your $ATOM or other Cosmos assets in a social login account, don’t transfer any more funds into it for now. Move your liquid assets to an account created with a recovery phrase or hardware wallet. Also, treat any unsolicited messages or links offering to “help you recover your assets” as scams.
Convenience and security: you always have to choose which one to prioritize. #钱包安全 #Keplr
For informational purposes only; this is not investment advice.
Keplr has paused Google and Apple social logins after users reported transfers they hadn’t made. Keplr says the issue was with the underlying Web3Auth service, where private keys were exposed. Web3Auth confirmed a security incident on November 6 and paused its embedded wallet service. A Keplr co-founder estimates that around 20% of social login accounts may be affected, but neither company has disclosed the amount of losses so far.
Accounts created with a recovery phrase or hardware wallet are not affected. My advice is simple: if you keep your $ATOM or other Cosmos assets in a social login account, don’t transfer any more funds into it for now. Move your liquid assets to an account created with a recovery phrase or hardware wallet. Also, treat any unsolicited messages or links offering to “help you recover your assets” as scams.
Convenience and security: you always have to choose which one to prioritize. #钱包安全 #Keplr
For informational purposes only; this is not investment advice.
Accounts created with a recovery phrase or hardware wallet are not affected. My advice is simple: if you keep your $ATOM or other Cosmos assets in a social login account, don’t transfer any more funds into it for now. Move your liquid assets to an account created with a recovery phrase or hardware wallet. Also, treat any unsolicited messages or links offering to “help you recover your assets” as scams.
Convenience and security: you always have to choose which one to prioritize. #钱包安全 #Keplr
For informational purposes only; this is not investment advice.
2

·
--
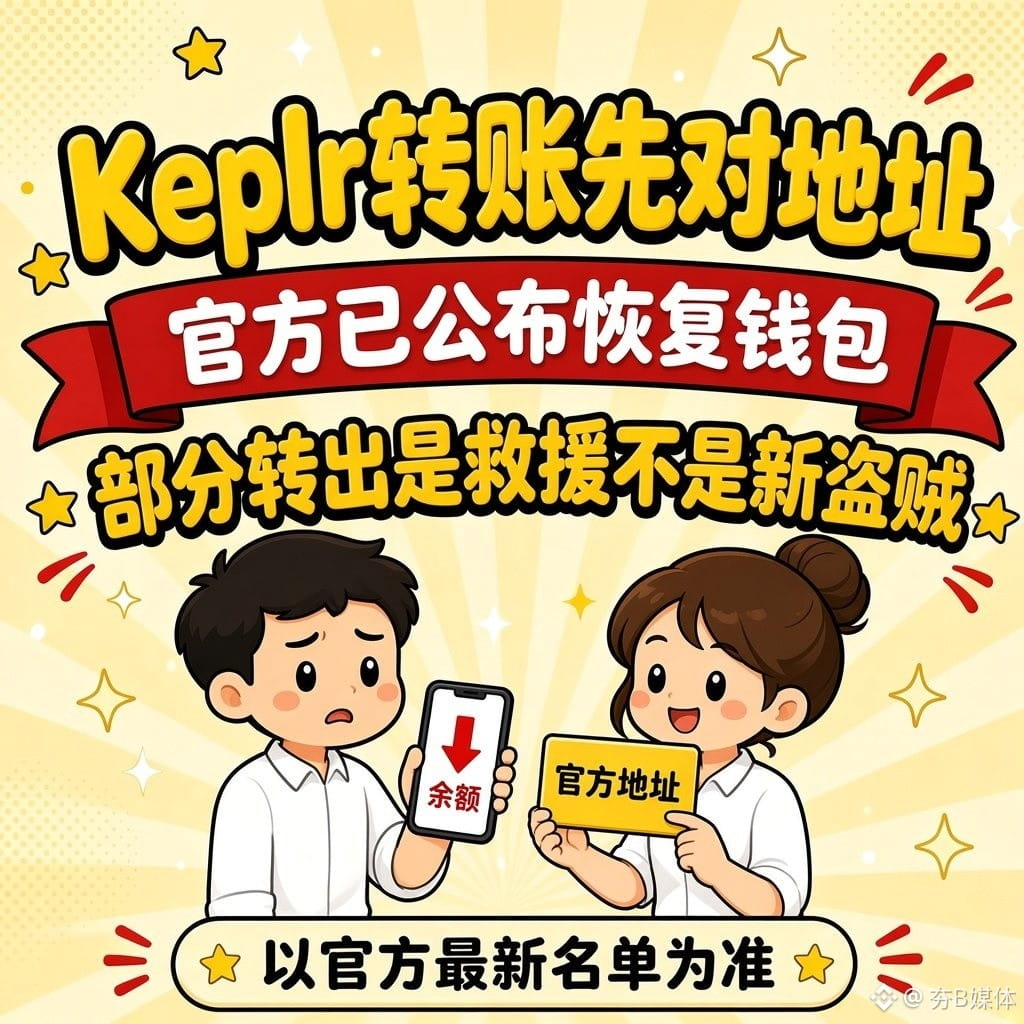
Keplr social login follow-up: Official recovery wallets announced; if your balance is lower, check the addresses first—don’t mistake recovery transfers for a new hack
Web3Auth said in a Sunday update that it is working with Keplr to transfer assets from affected accounts to secure recovery wallets, and published the verified recovery addresses. Keplr also reposted the list. They cautioned that some transfers out had been mistaken for attackers moving funds, but these addresses are being used to safeguard assets and are not wallets controlled by attackers. The list will continue to be updated. Decrypt, PANews, and ChainCatcher all reported on the clarification.
What this means for you: this is a follow-up to the earlier incident affecting some Keplr accounts that used Google or Apple login. It is not a new exchange hack, nor does it mean that all wallets were drained. The official team previously said that accounts created with a recovery phrase or hardware wallet were unaffected. If you use social login and notice a lower balance or an unfamiliar outgoing transfer, first check the address against the official Web3Auth and Keplr accounts before deciding whether it was a recovery transfer. Don’t send more funds to these accounts; the official team has not yet said when or how the recovered assets will be returned. Also watch out for impersonators claiming they can “help you recover your assets.”
The next things to confirm are the complete list of addresses, the scope of impact, and the return process.
If you’ve used Google or Apple login with Keplr, would you check the official addresses first, or move the remaining funds to a recovery phrase or hardware wallet first?
This is not investment advice.
Sources: Web3Auth and Keplr official updates (as reported by Decrypt, PANews, and ChainCatcher) · 2026-11-08 HKT
#Keplr #Web3Auth #钱包安全 #加密安全 #Hyped B Media
Keplr social login follow-up: Official recovery wallets announced; if your balance is lower, check the addresses first—don’t mistake recovery transfers for a new hack
Web3Auth said in a Sunday update that it is working with Keplr to transfer assets from affected accounts to secure recovery wallets, and published the verified recovery addresses. Keplr also reposted the list. They cautioned that some transfers out had been mistaken for attackers moving funds, but these addresses are being used to safeguard assets and are not wallets controlled by attackers. The list will continue to be updated. Decrypt, PANews, and ChainCatcher all reported on the clarification.
What this means for you: this is a follow-up to the earlier incident affecting some Keplr accounts that used Google or Apple login. It is not a new exchange hack, nor does it mean that all wallets were drained. The official team previously said that accounts created with a recovery phrase or hardware wallet were unaffected. If you use social login and notice a lower balance or an unfamiliar outgoing transfer, first check the address against the official Web3Auth and Keplr accounts before deciding whether it was a recovery transfer. Don’t send more funds to these accounts; the official team has not yet said when or how the recovered assets will be returned. Also watch out for impersonators claiming they can “help you recover your assets.”
The next things to confirm are the complete list of addresses, the scope of impact, and the return process.
If you’ve used Google or Apple login with Keplr, would you check the official addresses first, or move the remaining funds to a recovery phrase or hardware wallet first?
This is not investment advice.
Sources: Web3Auth and Keplr official updates (as reported by Decrypt, PANews, and ChainCatcher) · 2026-11-08 HKT
#Keplr #Web3Auth #钱包安全 #加密安全 #Hyped B Media
Web3Auth said in a Sunday update that it is working with Keplr to transfer assets from affected accounts to secure recovery wallets, and published the verified recovery addresses. Keplr also reposted the list. They cautioned that some transfers out had been mistaken for attackers moving funds, but these addresses are being used to safeguard assets and are not wallets controlled by attackers. The list will continue to be updated. Decrypt, PANews, and ChainCatcher all reported on the clarification.
What this means for you: this is a follow-up to the earlier incident affecting some Keplr accounts that used Google or Apple login. It is not a new exchange hack, nor does it mean that all wallets were drained. The official team previously said that accounts created with a recovery phrase or hardware wallet were unaffected. If you use social login and notice a lower balance or an unfamiliar outgoing transfer, first check the address against the official Web3Auth and Keplr accounts before deciding whether it was a recovery transfer. Don’t send more funds to these accounts; the official team has not yet said when or how the recovered assets will be returned. Also watch out for impersonators claiming they can “help you recover your assets.”
The next things to confirm are the complete list of addresses, the scope of impact, and the return process.
If you’ve used Google or Apple login with Keplr, would you check the official addresses first, or move the remaining funds to a recovery phrase or hardware wallet first?
This is not investment advice.
Sources: Web3Auth and Keplr official updates (as reported by Decrypt, PANews, and ChainCatcher) · 2026-11-08 HKT
#Keplr #Web3Auth #钱包安全 #加密安全 #Hyped B Media

·
--
Recovery phrases are safe; ‘one-click sign-in’ is not: Keplr suspends Google and Apple sign-insWallets that took the easy route and signed in with Google or Apple got hit first this time.
On November 6, Web3Auth, which provides embedded wallets and social sign-in, said its service had a security issue and that it had temporarily disabled embedded wallets. It had initially found no evidence that MetaMask users were affected. On November 7, it added that the issue was with Web3Auth’s infrastructure and affected some embedded wallets used by Keplr.
On the same day, Keplr, a wallet commonly used in Cosmos, officially posted that some accounts signed in with Google or Apple had experienced unauthorized transactions, and that it was working with Web3Auth to investigate. The team’s initial assessment was that accounts created with a recovery phrase or hardware wallet were unaffected; Google and Apple sign-ins have been suspended for now. It urged affected users not to add funds to these accounts or reimport their wallets or recreate them elsewhere.
Recovery phrases are safe; ‘one-click sign-in’ is not: Keplr suspends Google and Apple sign-ins
Wallets that took the easy route and signed in with Google or Apple got hit first this time.
On November 6, Web3Auth, which provides embedded wallets and social sign-in, said its service had a security issue and that it had temporarily disabled embedded wallets. It had initially found no evidence that MetaMask users were affected. On November 7, it added that the issue was with Web3Auth’s infrastructure and affected some embedded wallets used by Keplr.
On the same day, Keplr, a wallet commonly used in Cosmos, officially posted that some accounts signed in with Google or Apple had experienced unauthorized transactions, and that it was working with Web3Auth to investigate. The team’s initial assessment was that accounts created with a recovery phrase or hardware wallet were unaffected; Google and Apple sign-ins have been suspended for now. It urged affected users not to add funds to these accounts or reimport their wallets or recreate them elsewhere.
On November 6, Web3Auth, which provides embedded wallets and social sign-in, said its service had a security issue and that it had temporarily disabled embedded wallets. It had initially found no evidence that MetaMask users were affected. On November 7, it added that the issue was with Web3Auth’s infrastructure and affected some embedded wallets used by Keplr.
On the same day, Keplr, a wallet commonly used in Cosmos, officially posted that some accounts signed in with Google or Apple had experienced unauthorized transactions, and that it was working with Web3Auth to investigate. The team’s initial assessment was that accounts created with a recovery phrase or hardware wallet were unaffected; Google and Apple sign-ins have been suspended for now. It urged affected users not to add funds to these accounts or reimport their wallets or recreate them elsewhere.
GOOGUS+1.10%
買不起比特幣只能買比特犬:
所有熱錢包都不要用,並移除所有㽞覽器插件
1
182
·
--
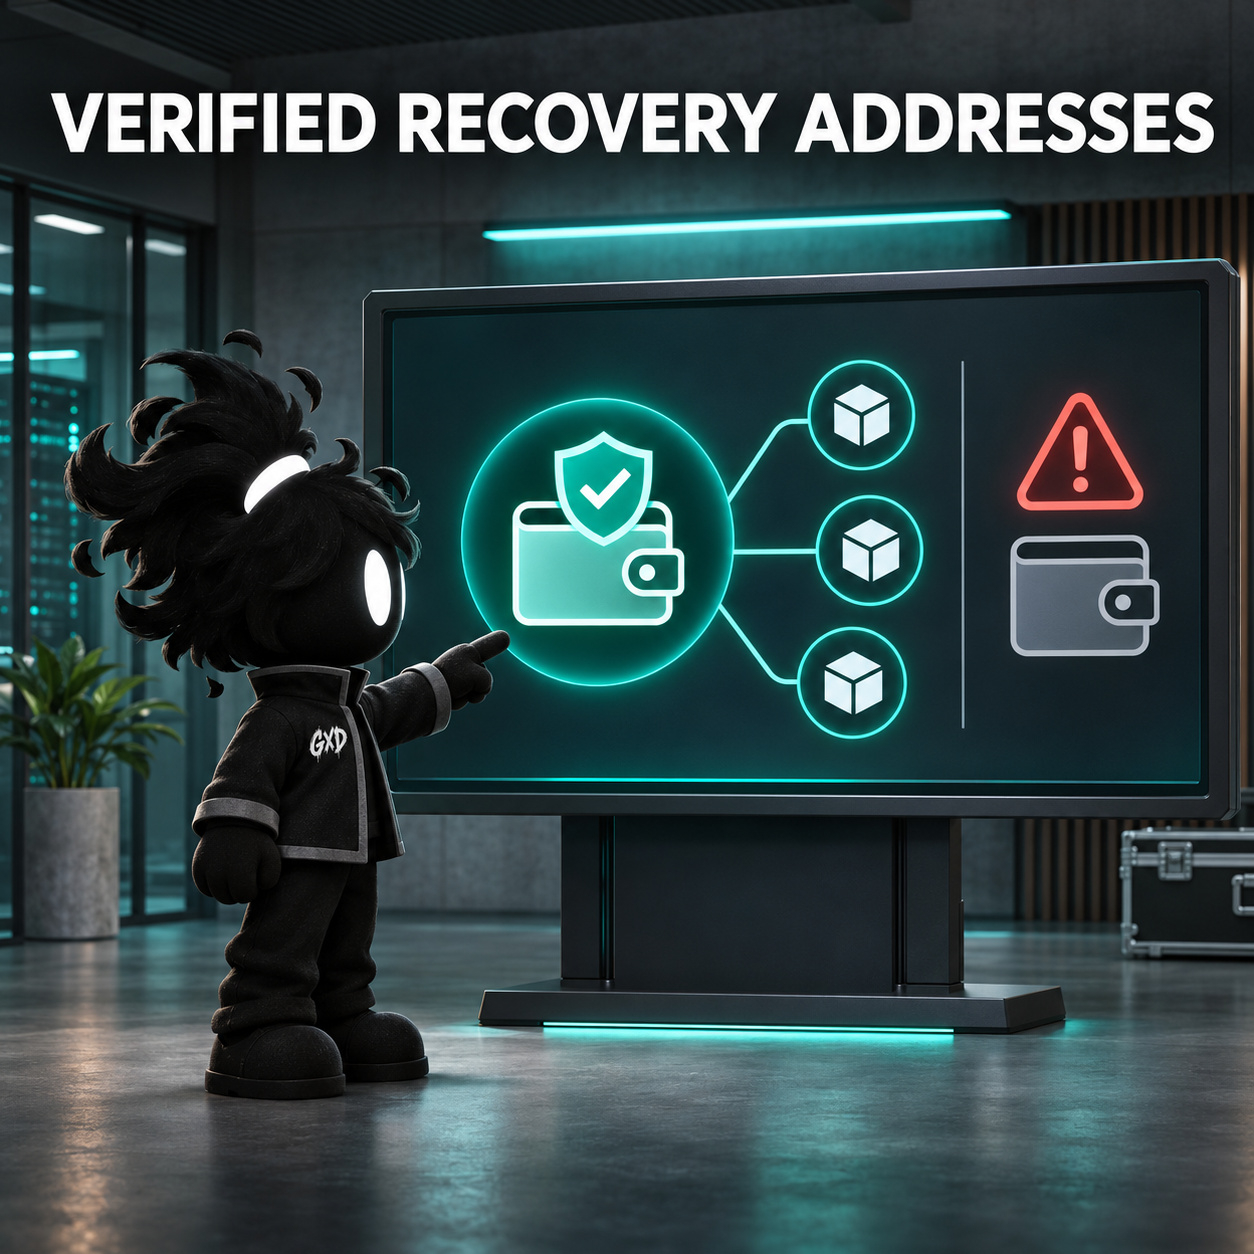
In a new update on the Keplr incident, Web3Auth published verified recovery wallet addresses and said some of the visible transfers were part of rescue efforts. Don’t judge a transfer by how it looks; match the address with the official account and ignore private recovery messages. Have you seen the update? 🛡️🔎🔐
Most traded on Binance at the time of observation (13:07 Istanbul time, 24-hour trading ranking): $BTC $ETH $BNB. General market monitoring, with no causal connection to the incident.
#Keplr #DigitalSecurity
In a new update on the Keplr incident, Web3Auth published verified recovery wallet addresses and said some of the visible transfers were part of rescue efforts. Don’t judge a transfer by how it looks; match the address with the official account and ignore private recovery messages. Have you seen the update? 🛡️🔎🔐
Most traded on Binance at the time of observation (13:07 Istanbul time, 24-hour trading ranking): $BTC $ETH $BNB . General market monitoring, with no causal connection to the incident.
#Keplr #DigitalSecurity
Most traded on Binance at the time of observation (13:07 Istanbul time, 24-hour trading ranking): $BTC $ETH $BNB . General market monitoring, with no causal connection to the incident.
#Keplr #DigitalSecurity
71
·
--
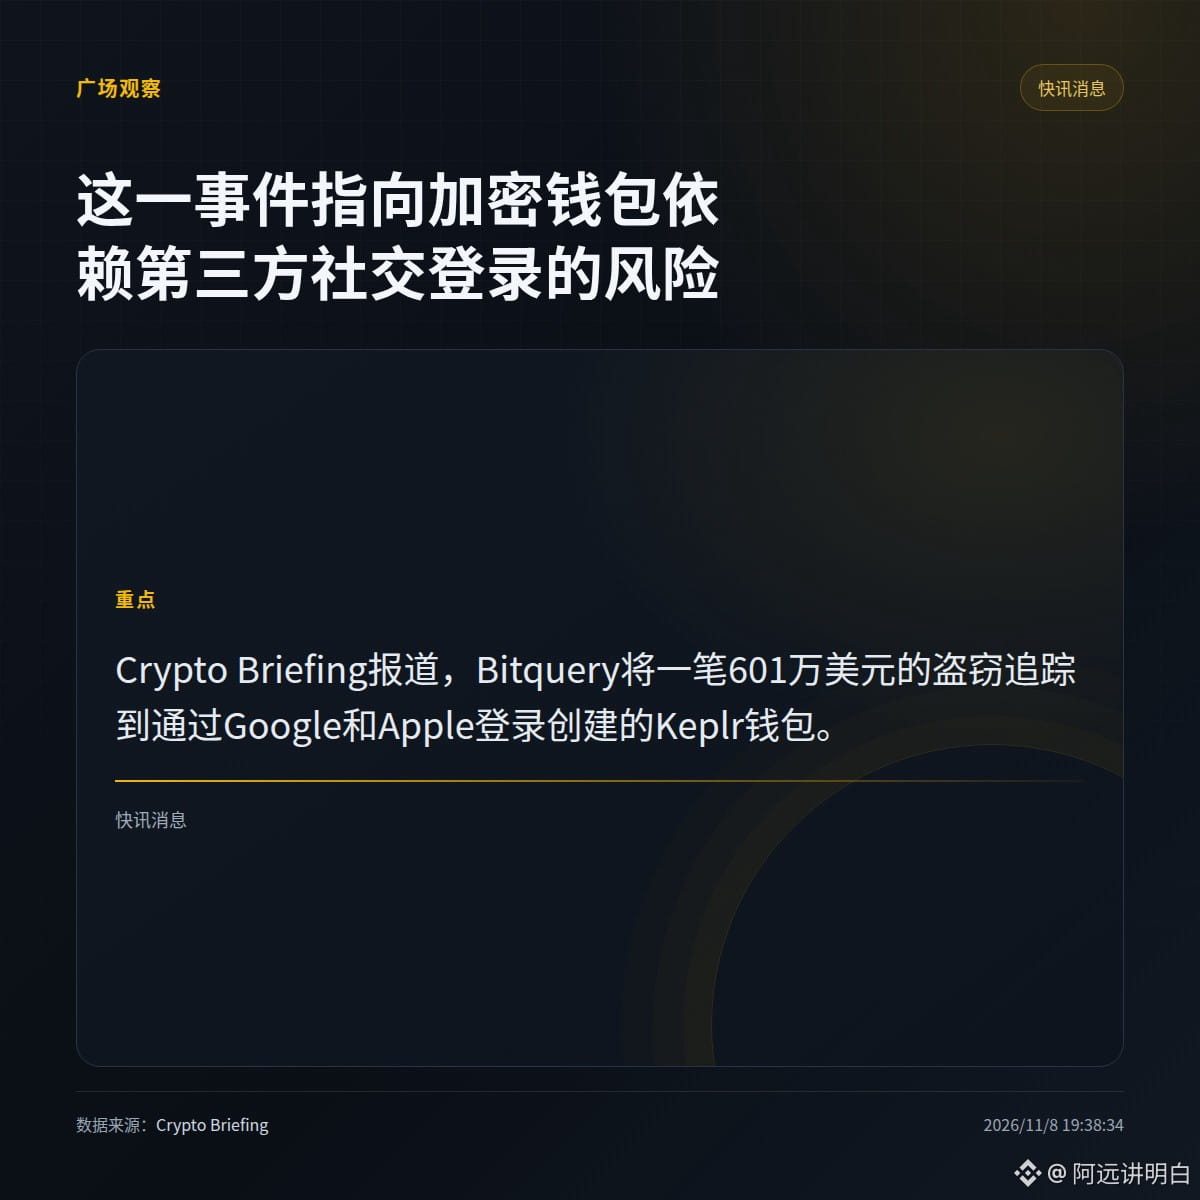
Bitquery traced the theft of $6.01 million to Keplr wallets created using Google and Apple sign-in.
According to Crypto Briefing, the incident highlights the risks of crypto wallets relying on third-party social logins.
· Affected users were Keplr users whose wallets were generated by signing in with social accounts.
· The source only provides the tracing conclusion and does not explain the specific path of losses from hot wallets, so it cannot be inferred that all social login wallets have the same issue.
Would you avoid using third-party social login when creating a wallet?
#Keplr
Bitquery traced the theft of $6.01 million to Keplr wallets created using Google and Apple sign-in.
According to Crypto Briefing, the incident highlights the risks of crypto wallets relying on third-party social logins.
· Affected users were Keplr users whose wallets were generated by signing in with social accounts.
· The source only provides the tracing conclusion and does not explain the specific path of losses from hot wallets, so it cannot be inferred that all social login wallets have the same issue.
Would you avoid using third-party social login when creating a wallet?
#Keplr
According to Crypto Briefing, the incident highlights the risks of crypto wallets relying on third-party social logins.
· Affected users were Keplr users whose wallets were generated by signing in with social accounts.
· The source only provides the tracing conclusion and does not explain the specific path of losses from hot wallets, so it cannot be inferred that all social login wallets have the same issue.
Would you avoid using third-party social login when creating a wallet?
#Keplr
21
A real-life race is unfolding in the Cosmos scene tonight: hackers are stealing up front, white hats are scrambling after them, and your coins are stuck in the middle awaiting their verdict.
Keplr just came clean: a Web3Auth vulnerability exposed the private keys of users who logged in with Google/Apple, affecting more than 44,000 wallets. On-chain tracking has already identified $6.01 million in transfers, and about one in five social-login accounts may be affected. The official advice: everyone should quickly move their remaining funds to a wallet secured with a recovery phrase. Wait too long and your balance could drop to zero; staked funds will take time to unlock.
A snapshot of the crowd: Google-login users are moving out overnight, hands shaking so much they’re copying their recovery phrases onto the wrong lines; recovery-phrase and hardware-wallet users are calmly watching the drama unfold: “We told you not to take shortcuts.” Most confused are those who can’t tell white hats from black hats—they don’t even know who to thank when their wallet balance shrinks.
$ATOM 1.37 bucks, down 8.8% in 7 days; $INJ 8.2 bucks, still up 17.8% in 5 days. The same rescue list, two different trajectories.
Pick a side: A) Better to get out first; we’ll see who wins between the white hats and black hats / B) Panic selling creates bargains—buy if $ATOM drops below 1.3
#Keplr #Web3Auth #WalletSecurity
A real-life race is unfolding in the Cosmos scene tonight: hackers are stealing up front, white hats are scrambling after them, and your coins are stuck in the middle awaiting their verdict.
Keplr just came clean: a Web3Auth vulnerability exposed the private keys of users who logged in with Google/Apple, affecting more than 44,000 wallets. On-chain tracking has already identified $6.01 million in transfers, and about one in five social-login accounts may be affected. The official advice: everyone should quickly move their remaining funds to a wallet secured with a recovery phrase. Wait too long and your balance could drop to zero; staked funds will take time to unlock.
A snapshot of the crowd: Google-login users are moving out overnight, hands shaking so much they’re copying their recovery phrases onto the wrong lines; recovery-phrase and hardware-wallet users are calmly watching the drama unfold: “We told you not to take shortcuts.” Most confused are those who can’t tell white hats from black hats—they don’t even know who to thank when their wallet balance shrinks.
$ATOM 1.37 bucks, down 8.8% in 7 days; $INJ 8.2 bucks, still up 17.8% in 5 days. The same rescue list, two different trajectories.
Pick a side: A) Better to get out first; we’ll see who wins between the white hats and black hats / B) Panic selling creates bargains—buy if $ATOM drops below 1.3
#Keplr #Web3Auth #WalletSecurity
Keplr just came clean: a Web3Auth vulnerability exposed the private keys of users who logged in with Google/Apple, affecting more than 44,000 wallets. On-chain tracking has already identified $6.01 million in transfers, and about one in five social-login accounts may be affected. The official advice: everyone should quickly move their remaining funds to a wallet secured with a recovery phrase. Wait too long and your balance could drop to zero; staked funds will take time to unlock.
A snapshot of the crowd: Google-login users are moving out overnight, hands shaking so much they’re copying their recovery phrases onto the wrong lines; recovery-phrase and hardware-wallet users are calmly watching the drama unfold: “We told you not to take shortcuts.” Most confused are those who can’t tell white hats from black hats—they don’t even know who to thank when their wallet balance shrinks.
$ATOM 1.37 bucks, down 8.8% in 7 days; $INJ 8.2 bucks, still up 17.8% in 5 days. The same rescue list, two different trajectories.
Pick a side: A) Better to get out first; we’ll see who wins between the white hats and black hats / B) Panic selling creates bargains—buy if $ATOM drops below 1.3
#Keplr #Web3Auth #WalletSecurity

Keplr got drained this time, but don’t just focus on blaming Keplr.
The latest word on X: at least $6 million, involving more than 44,000 Cosmos wallets, all accounts created with Google/Apple sign-in. The source was Web3Auth. This login service was acquired by Consensys—the parent company of MetaMask—in June 2025. Web3Auth’s own statement says, “There is no evidence that MetaMask users were affected.”
That sounds very polished, but it dodges the real question: besides Keplr, how many wallets and apps use the same social login system? No one has provided a list so far. Even Keplr itself only came forward about 7.5 hours later to say it was one of them.
I did a rough calculation myself: divide $6 million among 44,000 wallets, and that’s only about $136 per wallet on average. The victims were mostly small accounts belonging to newbies who chose convenience and didn’t want to write down their seed phrases—the very people least able to investigate things on-chain for themselves.
And it gets even more ridiculous: right under CoinBureau’s warning post, an ICP shill account immediately showed up, in all caps, promoting “Internet Identity.” Someone’s wallet has just been drained, and he comes along to sell them the next login solution.
A so-called “non-custodial wallet you can log into with an email” essentially outsources the security of your private keys to an intermediary you’ve never even heard of. The convenience is real, but when something goes wrong, you really can’t find anyone to turn to.
#Keplr #WalletSecurity
Keplr got drained this time, but don’t just focus on blaming Keplr.
The latest word on X: at least $6 million, involving more than 44,000 Cosmos wallets, all accounts created with Google/Apple sign-in. The source was Web3Auth. This login service was acquired by Consensys—the parent company of MetaMask—in June 2025. Web3Auth’s own statement says, “There is no evidence that MetaMask users were affected.”
That sounds very polished, but it dodges the real question: besides Keplr, how many wallets and apps use the same social login system? No one has provided a list so far. Even Keplr itself only came forward about 7.5 hours later to say it was one of them.
I did a rough calculation myself: divide $6 million among 44,000 wallets, and that’s only about $136 per wallet on average. The victims were mostly small accounts belonging to newbies who chose convenience and didn’t want to write down their seed phrases—the very people least able to investigate things on-chain for themselves.
And it gets even more ridiculous: right under CoinBureau’s warning post, an ICP shill account immediately showed up, in all caps, promoting “Internet Identity.” Someone’s wallet has just been drained, and he comes along to sell them the next login solution.
A so-called “non-custodial wallet you can log into with an email” essentially outsources the security of your private keys to an intermediary you’ve never even heard of. The convenience is real, but when something goes wrong, you really can’t find anyone to turn to.
#Keplr #WalletSecurity
The latest word on X: at least $6 million, involving more than 44,000 Cosmos wallets, all accounts created with Google/Apple sign-in. The source was Web3Auth. This login service was acquired by Consensys—the parent company of MetaMask—in June 2025. Web3Auth’s own statement says, “There is no evidence that MetaMask users were affected.”
That sounds very polished, but it dodges the real question: besides Keplr, how many wallets and apps use the same social login system? No one has provided a list so far. Even Keplr itself only came forward about 7.5 hours later to say it was one of them.
I did a rough calculation myself: divide $6 million among 44,000 wallets, and that’s only about $136 per wallet on average. The victims were mostly small accounts belonging to newbies who chose convenience and didn’t want to write down their seed phrases—the very people least able to investigate things on-chain for themselves.
And it gets even more ridiculous: right under CoinBureau’s warning post, an ICP shill account immediately showed up, in all caps, promoting “Internet Identity.” Someone’s wallet has just been drained, and he comes along to sell them the next login solution.
A so-called “non-custodial wallet you can log into with an email” essentially outsources the security of your private keys to an intermediary you’ve never even heard of. The convenience is real, but when something goes wrong, you really can’t find anyone to turn to.
#Keplr #WalletSecurity
5
·
--
#Keplr建议社交登录用户转移资产
86% of wallets were drained only after the warning was issued
$AMZNB $TSMB
Keplr advises users who sign in with social accounts to move their assets. This is not a precautionary measure—it’s damage control after the fact.
On-chain data shows that attackers stole at least $6 million from more than 44,000 Keplr wallets accessed through Google/Apple sign-in, across 8 Cosmos chains. Keplr issued a warning on November 7 at 04:38 UTC, but the biggest wave of draining happened two hours after the warning—six times larger than the first wave. By wallet count, 86% of victims lost their funds only after seeing the warning.
The reason is simple: the private keys had already been compromised, and pausing the sign-in feature couldn’t stop those who already had the keys. “Pausing” protects accounts whose keys haven’t been compromised; it can’t protect those that have.
#Keplr #Web3安全 #Cosmos
{future}(BNBUSDT)
{web3_wallet_create}(560xc6bff31bbfa84d3c05ad61d8ec47be8b31517777)
#Keplr建议社交登录用户转移资产
86% of wallets were drained only after the warning was issued
$AMZNB $TSMB
Keplr advises users who sign in with social accounts to move their assets. This is not a precautionary measure—it’s damage control after the fact.
On-chain data shows that attackers stole at least $6 million from more than 44,000 Keplr wallets accessed through Google/Apple sign-in, across 8 Cosmos chains. Keplr issued a warning on November 7 at 04:38 UTC, but the biggest wave of draining happened two hours after the warning—six times larger than the first wave. By wallet count, 86% of victims lost their funds only after seeing the warning.
The reason is simple: the private keys had already been compromised, and pausing the sign-in feature couldn’t stop those who already had the keys. “Pausing” protects accounts whose keys haven’t been compromised; it can’t protect those that have.
#Keplr #Web3安全 #Cosmos
86% of wallets were drained only after the warning was issued
$AMZNB $TSMB
Keplr advises users who sign in with social accounts to move their assets. This is not a precautionary measure—it’s damage control after the fact.
On-chain data shows that attackers stole at least $6 million from more than 44,000 Keplr wallets accessed through Google/Apple sign-in, across 8 Cosmos chains. Keplr issued a warning on November 7 at 04:38 UTC, but the biggest wave of draining happened two hours after the warning—six times larger than the first wave. By wallet count, 86% of victims lost their funds only after seeing the warning.
The reason is simple: the private keys had already been compromised, and pausing the sign-in feature couldn’t stop those who already had the keys. “Pausing” protects accounts whose keys haven’t been compromised; it can’t protect those that have.
#Keplr #Web3安全 #Cosmos
173

·
--
【Market Alert】Keplr Private Key Leak: Social Login Users, Move Your Assets Now
Cosmos wallet Keplr confirmed that a vulnerability in the Web3Auth infrastructure exposed the private keys of some users who logged in with Google or Apple. Accounts created using a seed phrase or hardware wallet were not affected. Official reminder: Do not transfer new funds to the original account. Move any remaining transferable assets to an account created with a seed phrase or hardware wallet as soon as possible. Do you use social login or a seed phrase?
$ATOM $BTC $ETH
#Keplr #钱包安全 #Cosmos
(Source: Wu Says Blockchain)
⚠️Risk warning: The above is shared for informational purposes only and does not constitute investment advice. Investing involves risk; proceed with caution.
【Market Alert】Keplr Private Key Leak: Social Login Users, Move Your Assets Now
Cosmos wallet Keplr confirmed that a vulnerability in the Web3Auth infrastructure exposed the private keys of some users who logged in with Google or Apple. Accounts created using a seed phrase or hardware wallet were not affected. Official reminder: Do not transfer new funds to the original account. Move any remaining transferable assets to an account created with a seed phrase or hardware wallet as soon as possible. Do you use social login or a seed phrase?
$ATOM $BTC $ETH
#Keplr #钱包安全 #Cosmos
(Source: Wu Says Blockchain)
⚠️Risk warning: The above is shared for informational purposes only and does not constitute investment advice. Investing involves risk; proceed with caution.
Cosmos wallet Keplr confirmed that a vulnerability in the Web3Auth infrastructure exposed the private keys of some users who logged in with Google or Apple. Accounts created using a seed phrase or hardware wallet were not affected. Official reminder: Do not transfer new funds to the original account. Move any remaining transferable assets to an account created with a seed phrase or hardware wallet as soon as possible. Do you use social login or a seed phrase?
$ATOM $BTC $ETH
#Keplr #钱包安全 #Cosmos
(Source: Wu Says Blockchain)
⚠️Risk warning: The above is shared for informational purposes only and does not constitute investment advice. Investing involves risk; proceed with caution.
9

·
--
Keplr social-login wallet incident: Who actually holds your private keys?
If you created your Keplr wallet by clicking “Sign in with Google/Apple,” you should read this.
On November 7, Keplr said it had received reports of unauthorized transfers from some accounts created by signing in with Google or Apple. Web3Auth then confirmed that a security issue in its infrastructure had affected some embedded wallets used by Keplr. In a subsequent statement, Keplr explicitly described it as a “private key leak.”
A few things to distinguish:
1. Keplr wallets created with a seed phrase or hardware wallet are, according to the company, unaffected.
2. Sign-in with Google/Apple has been suspended. Web3Auth said it worked with partners to white-hat transfer funds from vulnerable wallets that had not yet been stolen, using the same route as the attackers. So if some accounts have lower or even zero balances, this may have been a rescue operation—not necessarily a theft. Staked and locked assets take longer to handle.
3. Neither party has yet disclosed the number of affected wallets or the amount of losses.
Official advice for users who may be affected: Don’t transfer any more funds into that account. Move any remaining liquid assets to an account secured with a seed phrase or hardware wallet. Trust only official Keplr and Web3Auth accounts, and treat any links in DMs offering to “help you recover” your funds as phishing.
“Seedless” login saves you the trouble of memorizing 12 words, not the risk—the key is simply stored somewhere else. Before using social login, ask: Who generates the private key, where is it stored, and who can access it if something goes wrong?
#Keplr #钱包安全 #Web3
Keplr social-login wallet incident: Who actually holds your private keys?
If you created your Keplr wallet by clicking “Sign in with Google/Apple,” you should read this.
On November 7, Keplr said it had received reports of unauthorized transfers from some accounts created by signing in with Google or Apple. Web3Auth then confirmed that a security issue in its infrastructure had affected some embedded wallets used by Keplr. In a subsequent statement, Keplr explicitly described it as a “private key leak.”
A few things to distinguish:
1. Keplr wallets created with a seed phrase or hardware wallet are, according to the company, unaffected.
2. Sign-in with Google/Apple has been suspended. Web3Auth said it worked with partners to white-hat transfer funds from vulnerable wallets that had not yet been stolen, using the same route as the attackers. So if some accounts have lower or even zero balances, this may have been a rescue operation—not necessarily a theft. Staked and locked assets take longer to handle.
3. Neither party has yet disclosed the number of affected wallets or the amount of losses.
Official advice for users who may be affected: Don’t transfer any more funds into that account. Move any remaining liquid assets to an account secured with a seed phrase or hardware wallet. Trust only official Keplr and Web3Auth accounts, and treat any links in DMs offering to “help you recover” your funds as phishing.
“Seedless” login saves you the trouble of memorizing 12 words, not the risk—the key is simply stored somewhere else. Before using social login, ask: Who generates the private key, where is it stored, and who can access it if something goes wrong?
#Keplr #钱包安全 #Web3
If you created your Keplr wallet by clicking “Sign in with Google/Apple,” you should read this.
On November 7, Keplr said it had received reports of unauthorized transfers from some accounts created by signing in with Google or Apple. Web3Auth then confirmed that a security issue in its infrastructure had affected some embedded wallets used by Keplr. In a subsequent statement, Keplr explicitly described it as a “private key leak.”
A few things to distinguish:
1. Keplr wallets created with a seed phrase or hardware wallet are, according to the company, unaffected.
2. Sign-in with Google/Apple has been suspended. Web3Auth said it worked with partners to white-hat transfer funds from vulnerable wallets that had not yet been stolen, using the same route as the attackers. So if some accounts have lower or even zero balances, this may have been a rescue operation—not necessarily a theft. Staked and locked assets take longer to handle.
3. Neither party has yet disclosed the number of affected wallets or the amount of losses.
Official advice for users who may be affected: Don’t transfer any more funds into that account. Move any remaining liquid assets to an account secured with a seed phrase or hardware wallet. Trust only official Keplr and Web3Auth accounts, and treat any links in DMs offering to “help you recover” your funds as phishing.
“Seedless” login saves you the trouble of memorizing 12 words, not the risk—the key is simply stored somewhere else. Before using social login, ask: Who generates the private key, where is it stored, and who can access it if something goes wrong?
#Keplr #钱包安全 #Web3
4
🚨 Keplr crypto wallet under threat: users report missing funds
The Keplr Wallet team reported unauthorized transactions in wallets created through Google and Apple accounts. Sign-in through these services has been temporarily disabled.
🔐 The issue is suspected to be related to the Web3Auth authentication provider, which also reported a security incident. According to a preliminary assessment, wallets with seed phrases and hardware devices were not affected.
⚠️ Keplr recommends not adding funds to potentially affected wallets or importing them into other apps.
The scale of the losses is still unknown. Users are being warned about scammers offering to help recover funds.
#Keplr #Cosmos #ATOM
🚨 Keplr crypto wallet under threat: users report missing funds
The Keplr Wallet team reported unauthorized transactions in wallets created through Google and Apple accounts. Sign-in through these services has been temporarily disabled.
🔐 The issue is suspected to be related to the Web3Auth authentication provider, which also reported a security incident. According to a preliminary assessment, wallets with seed phrases and hardware devices were not affected.
⚠️ Keplr recommends not adding funds to potentially affected wallets or importing them into other apps.
The scale of the losses is still unknown. Users are being warned about scammers offering to help recover funds.
#Keplr #Cosmos #ATOM
The Keplr Wallet team reported unauthorized transactions in wallets created through Google and Apple accounts. Sign-in through these services has been temporarily disabled.
🔐 The issue is suspected to be related to the Web3Auth authentication provider, which also reported a security incident. According to a preliminary assessment, wallets with seed phrases and hardware devices were not affected.
⚠️ Keplr recommends not adding funds to potentially affected wallets or importing them into other apps.
The scale of the losses is still unknown. Users are being warned about scammers offering to help recover funds.
#Keplr #Cosmos #ATOM
2
637
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BinanceReopensWithdrawalsForHYPE&APT
30,130 views
543 Discussing
2
#SouthKoreaDraftLawTargets15To20%ShareholderCap
34,290 views
374 Discussing
3
#TradFiForBeginners
141,689 views
1,500 Discussing
4
#KeplrAdvisesSocialLoginUsersToTransferAssets
22,612 views
367 Discussing
5
#TetherPlans€28.8MForJuventusCapitalIncrease
13,339 views
281 Discussing
6
#JobsReportRaisesHikeOdds
764,840 views
4,263 Discussing
7
#CPITestsDecemberRateOutlook
292,455 views
1,766 Discussing
8
#US Data Center Rules May Constrain AI Expansion
113,101 views
255 Discussing
9
#ARKPlans14ThematicETFsCoveringAIAndTokenizedMarkets
7,759 views
86 Discussing
10
#WillAnthropicListOnTime
245,596 views
1,819 Discussing