

#bitgetbreachforgedrequestsnotstolenkeys
bitgetbreachforgedrequestsnotstolenkeys
115,697 views
1,002 Discussing
Hot
Latest

Why is nobody talking about the fact that this was never a stolen-keys event?
Too many people still lose money the same way. Headline hits, they dump or pull every last $USDT, then sit out while $SUI and $OP keep grinding because they reacted to the title instead of the details.
The mainstream story writes itself. Another exchange, another reason to scream that nothing is safe. What actually got communicated is forged requests, not compromised keys. That is an authentication problem, not a drained vault. Treating them as the same thing is how you make the wrong decision in a market that is already sitting at 72 on greed.
I run a simple rule set. Keep only working capital on any venue. One IP whitelist per API, withdrawals off unless you are moving size that day. If a trade is working, the leftover size comes off the books. That is the whole playbook.
What's your take on how we should actually price CEX risk after this?
#BitgetSays #BitgetBreachForgedRequestsNotStolenKeys
35

·
--
Have you noticed how quickly everyone accepted "forged requests, not stolen keys" as if that closed the book on the Bitget incident?
Most traders still sit on large $USDT stacks at exchanges because withdrawing is friction, then they scramble when a security story hits. You rarely get a clean signal on whether to exit until after the damage is already priced.
This is a case study, not a press release. Stolen keys means an attacker can authorize anything, while forged requests mean the system processed instructions that should never have been valid. Both can drain funds. The second just sounds cleaner in a statement, and people treated it as proof the vault was untouched.
Greed is sitting at 72 and nobody wants a security lecture while they hunt $SUI. What actually happened is an operational failure got rebranded as a technicality. Most $ETH holders did not change a single thing about where they keep coins.
Does that distinction change how you custody, or are we all going to forget this by next week?
#BitgetBreachForgedRequestsNotStolenKeys #BitgetSays
Have you noticed how quickly everyone accepted "forged requests, not stolen keys" as if that closed the book on the Bitget incident?
Most traders still sit on large $USDT stacks at exchanges because withdrawing is friction, then they scramble when a security story hits. You rarely get a clean signal on whether to exit until after the damage is already priced.
This is a case study, not a press release. Stolen keys means an attacker can authorize anything, while forged requests mean the system processed instructions that should never have been valid. Both can drain funds. The second just sounds cleaner in a statement, and people treated it as proof the vault was untouched.
Greed is sitting at 72 and nobody wants a security lecture while they hunt $SUI . What actually happened is an operational failure got rebranded as a technicality. Most $ETH holders did not change a single thing about where they keep coins.
Does that distinction change how you custody, or are we all going to forget this by next week?
#BitgetBreachForgedRequestsNotStolenKeys #BitgetSays
74
Even the safest sounding exchange hacks can still wipe you out if attackers just forge the withdrawal requests instead of stealing keys.
You've been there leaving $USDT and alts on a CEX because self-custody feels like extra work. Then a headline like this drops and you start wondering if your funds are actually next.
I was going through the details on this Bitget situation. They clarified it was forged requests not stolen keys, which sounds like a relief at first glance. It still means attackers found a way to impersonate valid API activity and move funds around without ever touching the core private keys.
That's a real warning about how many attack surfaces these platforms have. Right now with Fear and Greed at 72 people are loading up on names like $SUI and $OP, parking everything on exchanges without a second thought. The risk is you find out too late, withdrawals freeze, and you're stuck waiting while the story unfolds.
Self-custody isn't effortless but at least a forged request on someone else's system isn't your problem the same way.
Where do you think this leaves CEX security going forward?
#BitgetBreachForgedRequestsNotStolenKeys #BitgetSays
Even the safest sounding exchange hacks can still wipe you out if attackers just forge the withdrawal requests instead of stealing keys.
You've been there leaving $USDT and alts on a CEX because self-custody feels like extra work. Then a headline like this drops and you start wondering if your funds are actually next.
I was going through the details on this Bitget situation. They clarified it was forged requests not stolen keys, which sounds like a relief at first glance. It still means attackers found a way to impersonate valid API activity and move funds around without ever touching the core private keys.
That's a real warning about how many attack surfaces these platforms have. Right now with Fear and Greed at 72 people are loading up on names like $SUI and $OP , parking everything on exchanges without a second thought. The risk is you find out too late, withdrawals freeze, and you're stuck waiting while the story unfolds.
Self-custody isn't effortless but at least a forged request on someone else's system isn't your problem the same way.
Where do you think this leaves CEX security going forward?
#BitgetBreachForgedRequestsNotStolenKeys #BitgetSays
129

·
--
Bullish
#bitgetbreachforgedrequestsnotstolenkeys
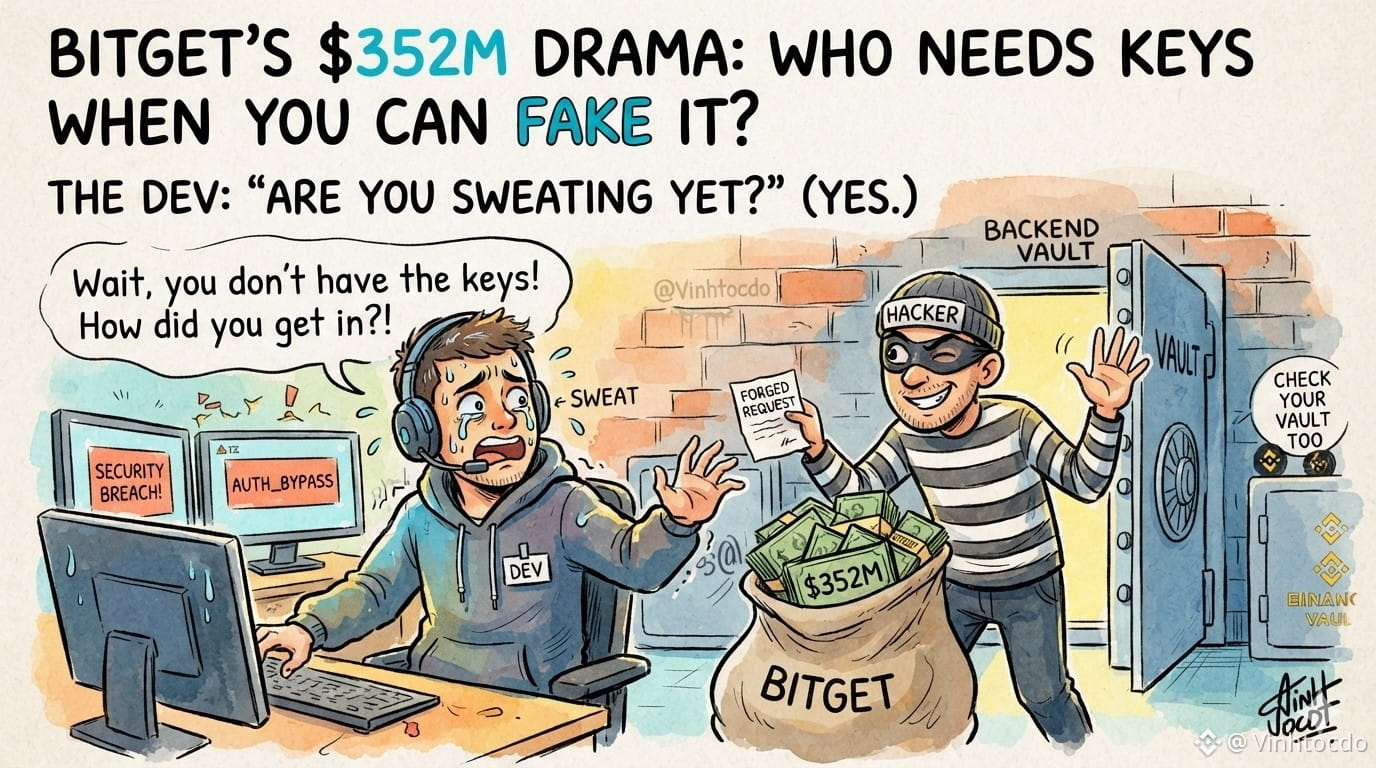
Bitget’s $352M drama: Forged requests, not stolen keys! Devs, are you sweating yet? 🤦♂️🛡️
So, Bitget spilled the tea on their recent hack! The attackers didn't steal their private keys; they simply outsmarted the backend system by forging transaction requests! It’s like a thief walking into a bank with a perfectly forged signature from the manager, and the vault just opened itself! 🏦🔑
This is a massive wake-up call for all blockchain devs and major exchanges, including Binance, to double-check their backend security infrastructure before another exploiter gets creative! 💻💥
What should smart traders do? 🛠️
📌 Keep your guard up: Don't put all your funds into a single exchange.
🛡️ Diversify your assets: Spread your portfolio into trusted tokens to minimize potential platform risks.
Disclaimer: This is personal opinion, not financial advice.
👇 Click and trade below to support me:
💰 $BNB
{future}(BNBUSDT)
| 💰 $BTC
{future}(BTCUSDT)
| 💰 $ETH
{future}(ETHUSDT)
📌 Referral Code: VINHTOCDO
🔗 Join Binance: [https://www.binance.com/register?ref=VINHTOCDO](https://www.binance.com/register?ref=VINHTOCDO)
#BitgetBreach #CryptoSecurity #BackendHacks #VINHTOCDO #TradingSafety #CryptoNews
#bitgetbreachforgedrequestsnotstolenkeys
Bitget’s $352M drama: Forged requests, not stolen keys! Devs, are you sweating yet? 🤦♂️🛡️
So, Bitget spilled the tea on their recent hack! The attackers didn't steal their private keys; they simply outsmarted the backend system by forging transaction requests! It’s like a thief walking into a bank with a perfectly forged signature from the manager, and the vault just opened itself! 🏦🔑
This is a massive wake-up call for all blockchain devs and major exchanges, including Binance, to double-check their backend security infrastructure before another exploiter gets creative! 💻💥
What should smart traders do? 🛠️
📌 Keep your guard up: Don't put all your funds into a single exchange.
🛡️ Diversify your assets: Spread your portfolio into trusted tokens to minimize potential platform risks.
Disclaimer: This is personal opinion, not financial advice.
👇 Click and trade below to support me:
💰 $BNB
| 💰 $BTC
| 💰 $ETH
📌 Referral Code: VINHTOCDO
🔗 Join Binance: https://www.binance.com/register?ref=VINHTOCDO
#BitgetBreach #CryptoSecurity #BackendHacks #VINHTOCDO #TradingSafety #CryptoNews
2
67

·
--
You think forged requests mean no real risk
That’s comforting but ignores how exchanges get pressured
If they’re forging requests the system is broken not the keys
Traders don’t care why the exploit happened only that it worked
I’m watching how fast they patch and respond
Not the narrative around stolen keys or not
If they release the full forensic report and it shows zero system flaws
Then I’ll admit I overreacted
You think it’s safe
#BitgetBreachForgedRequestsNotStolenKeys #CryptoNews
24
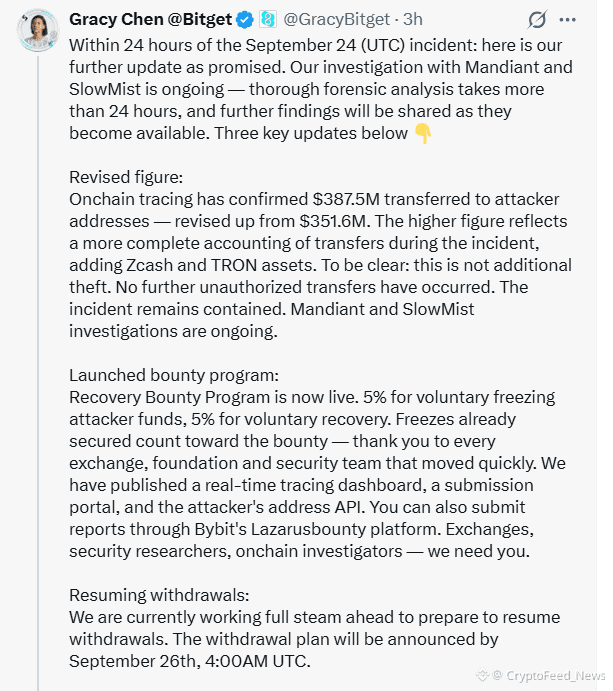
#BitgetBreachForgedRequestsNotStolenKeys Refers to a major security incident on September 24, 2026, where the crypto exchange Bitget suffered a hack resulting in an estimated $351.6 million to $387.5 million in unauthorized transfers.
#BitgetBreachForgedRequestsNotStolenKeys Refers to a major security incident on September 24, 2026, where the crypto exchange Bitget suffered a hack resulting in an estimated $351.6 million to $387.5 million in unauthorized transfers.
1
31

🚨 BITGET BREACH: FORGED REQUESTS — NOT STOLEN KEYS
A major security incident involving Bitget has put crypto exchange security back in the spotlight. ⚠️
💰 Reported impact: ~$351.6M
🔐 Private keys: Bitget says they were not stolen
⚙️ Attack method: Manipulated/forged transaction requests
🛡️ Response: Security investigation and protective measures
📌 Why it matters:
Crypto security isn't only about protecting private keys. If an attacker can manipulate the systems that create or authorize transactions, massive losses can still happen.
🔥 The big question:
Are centralized exchanges secure enough when their backend authorization systems are targeted?
#Binance #CryptoInvesting $BNB
#BitgetBreachForgedRequestsNotStolenKeys
1
86
·
--
#BitgetBreachForgedRequestsNotStolenKeys addresses the $351.6 million security breach suffered by cryptocurrency exchange Bitget.
#BitgetBreachForgedRequestsNotStolenKeys addresses the $351.6 million security breach suffered by cryptocurrency exchange Bitget.
206 Atlas:
ETF inflows don't stop short sellers from hitting bids. Watch if IBIT demand holds as price breaks key support, or if it's just lagging spot pressure.The headline is misleading; forged requests imply a protocol or API flaw, not just stolen keys. This distinction matters for assessing systemic risk.
1
1
258
#BitgetBreachForgedRequestsNotStolenKeys
🚨 Bitget Breach Update: Forged Requests, Not Stolen Keys!
Crypto exchange Bitget recently suffered a massive $351.6 million security breach. However, CEO Gracy Chen confirmed that private keys were never stolen.
Instead, hackers infiltrated a backend wallet system, spoofing transaction data to push fake withdrawal requests through normal authorization channels. Think of it like slipping forged paperwork right through a teller window.
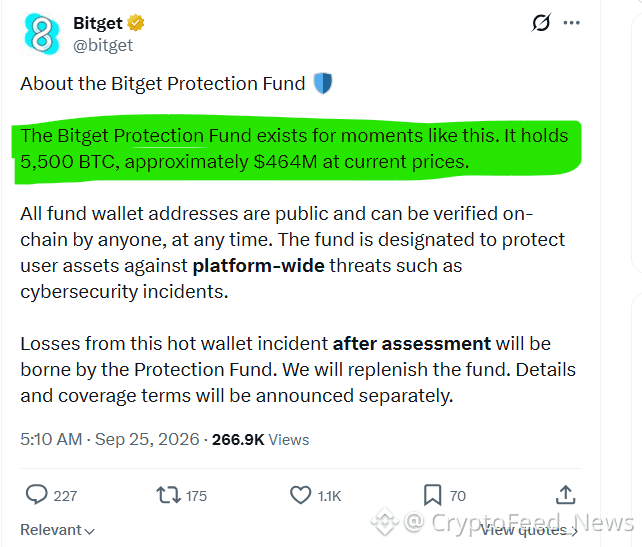
Cold storage remains entirely safe, and Bitget’s $464 million user protection fund completely covers the loss. While withdrawals are temporarily paused for security checks, trading and deposits continue normally. 🛡️📉
What are your thoughts on this backend attack vector?
#QNTRises39%
#CFTCUpdatesGuidanceOnTokenizedAssets
#NYAndPolymarketSueEachOther
#Nadeemgujjar143
@Helen_Alek @Square-Creator-f3ffb6967ae3 @qpl5557
$BTC
{spot}(BTCUSDT)
$BNB
{spot}(BNBUSDT)
$ADA
{spot}(ADAUSDT)
#BitgetBreachForgedRequestsNotStolenKeys
🚨 Bitget Breach Update: Forged Requests, Not Stolen Keys!
Crypto exchange Bitget recently suffered a massive $351.6 million security breach. However, CEO Gracy Chen confirmed that private keys were never stolen.
Instead, hackers infiltrated a backend wallet system, spoofing transaction data to push fake withdrawal requests through normal authorization channels. Think of it like slipping forged paperwork right through a teller window.
Cold storage remains entirely safe, and Bitget’s $464 million user protection fund completely covers the loss. While withdrawals are temporarily paused for security checks, trading and deposits continue normally. 🛡️📉
What are your thoughts on this backend attack vector?
#QNTRises39%
#CFTCUpdatesGuidanceOnTokenizedAssets
#NYAndPolymarketSueEachOther
#Nadeemgujjar143
@Hani Era @aasho @HK七匹狼
$BTC
$BNB
$ADA
3
170
#BitgetBreachForgedRequestsNotStolenKeys
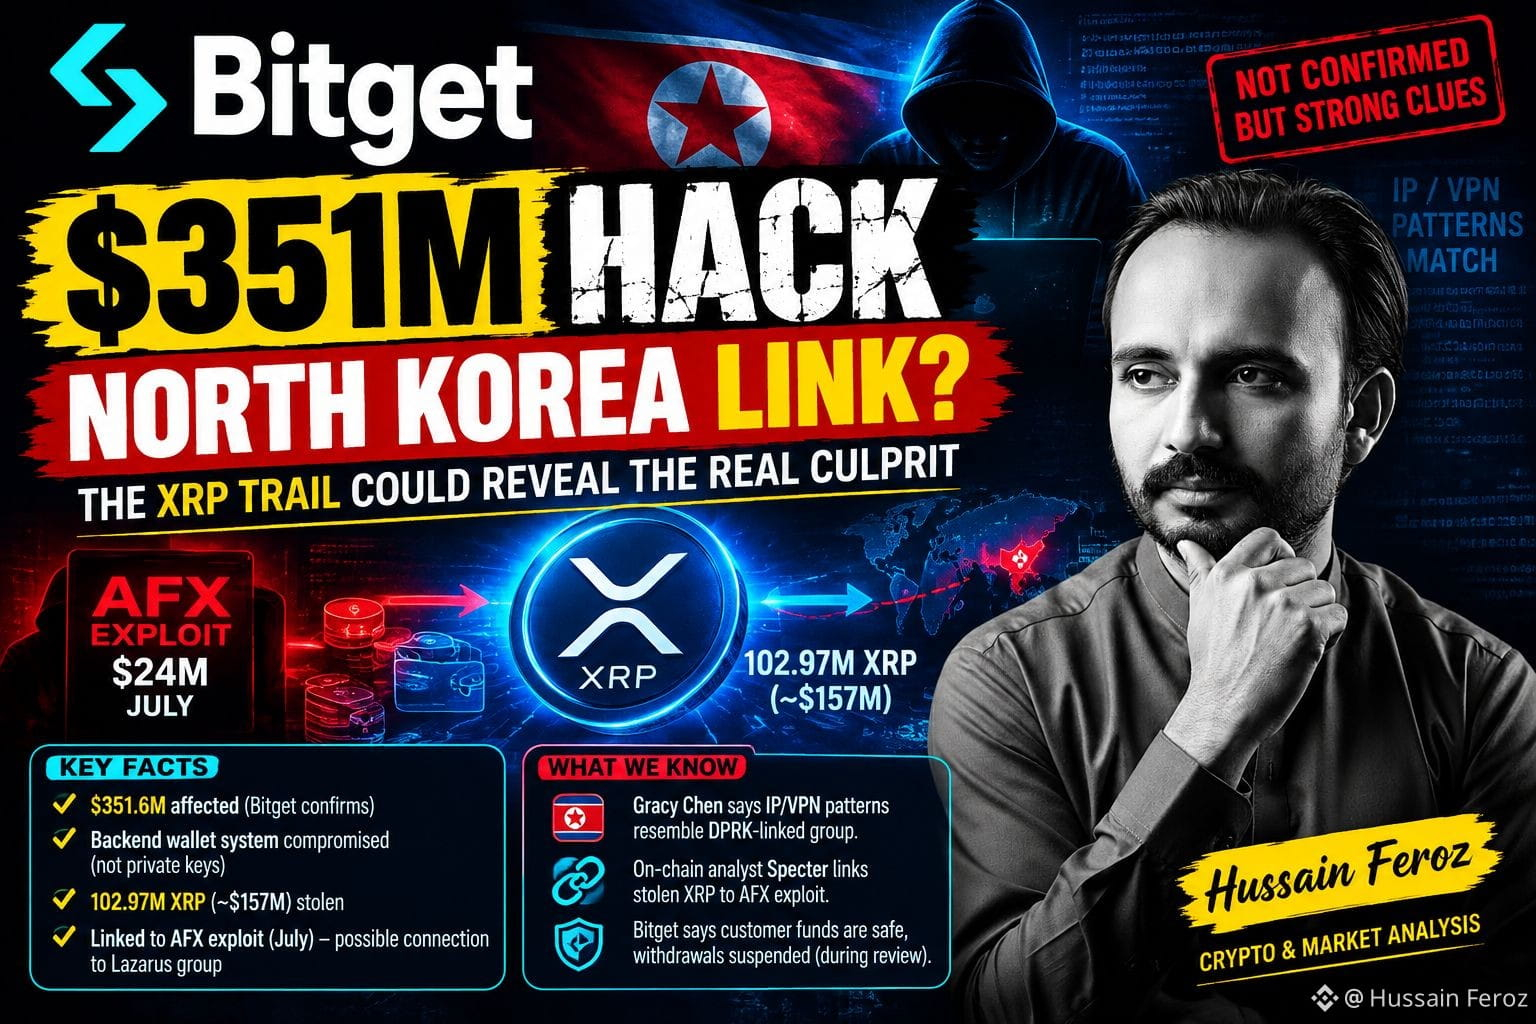
EXCLUSIVE: THE BITGET $351.6M HACK MAY HAVE LEFT A BIGGER CLUE
Everyone is talking about the possible North Korea connection.
But the more interesting clue may be hiding on-chain. 👀
🔎 What investigators are seeing:
• Bitget says ~$351.6M was affected across its wallet infrastructure
• The attacker reportedly compromised a backend wallet system, spoofed transaction data and triggered the normal authorization process
• Private keys were NOT compromised, according to Bitget
• Around 102.97M XRP — roughly $157M — was among the largest stolen portions
• On-chain analyst Specter says the stolen XRP can be traced to funds connected to the $24M AFX exploit from July
• That AFX incident has been associated with the TraderTraitor/Lazarus ecosystem
And there’s another clue:
Bitget CEO Gracy Chen says some attacker IP/VPN patterns resemble infrastructure previously associated with a North Korea-linked group.
⚠️ But this is NOT final attribution yet.
The real question now is:
Did the same North Korea-linked operation move from the AFX exploit to Bitget?
If the XRP trail + infrastructure evidence is independently confirmed, this could turn the Bitget incident from a massive exchange hack into another major Lazarus-linked operation.
💰 Bitget says its $464M+ User Protection Fund can cover the affected amount, while withdrawals remain suspended during the security review.
👀 Watch the XRP wallets.
The blockchain may reveal who is behind the attack before the official investigation does.
#Bitget #XRP #CryptoHack #LazarusGroup #NorthKorea #CryptoSecurity #CryptoNews
1
116
·
--
Bearish
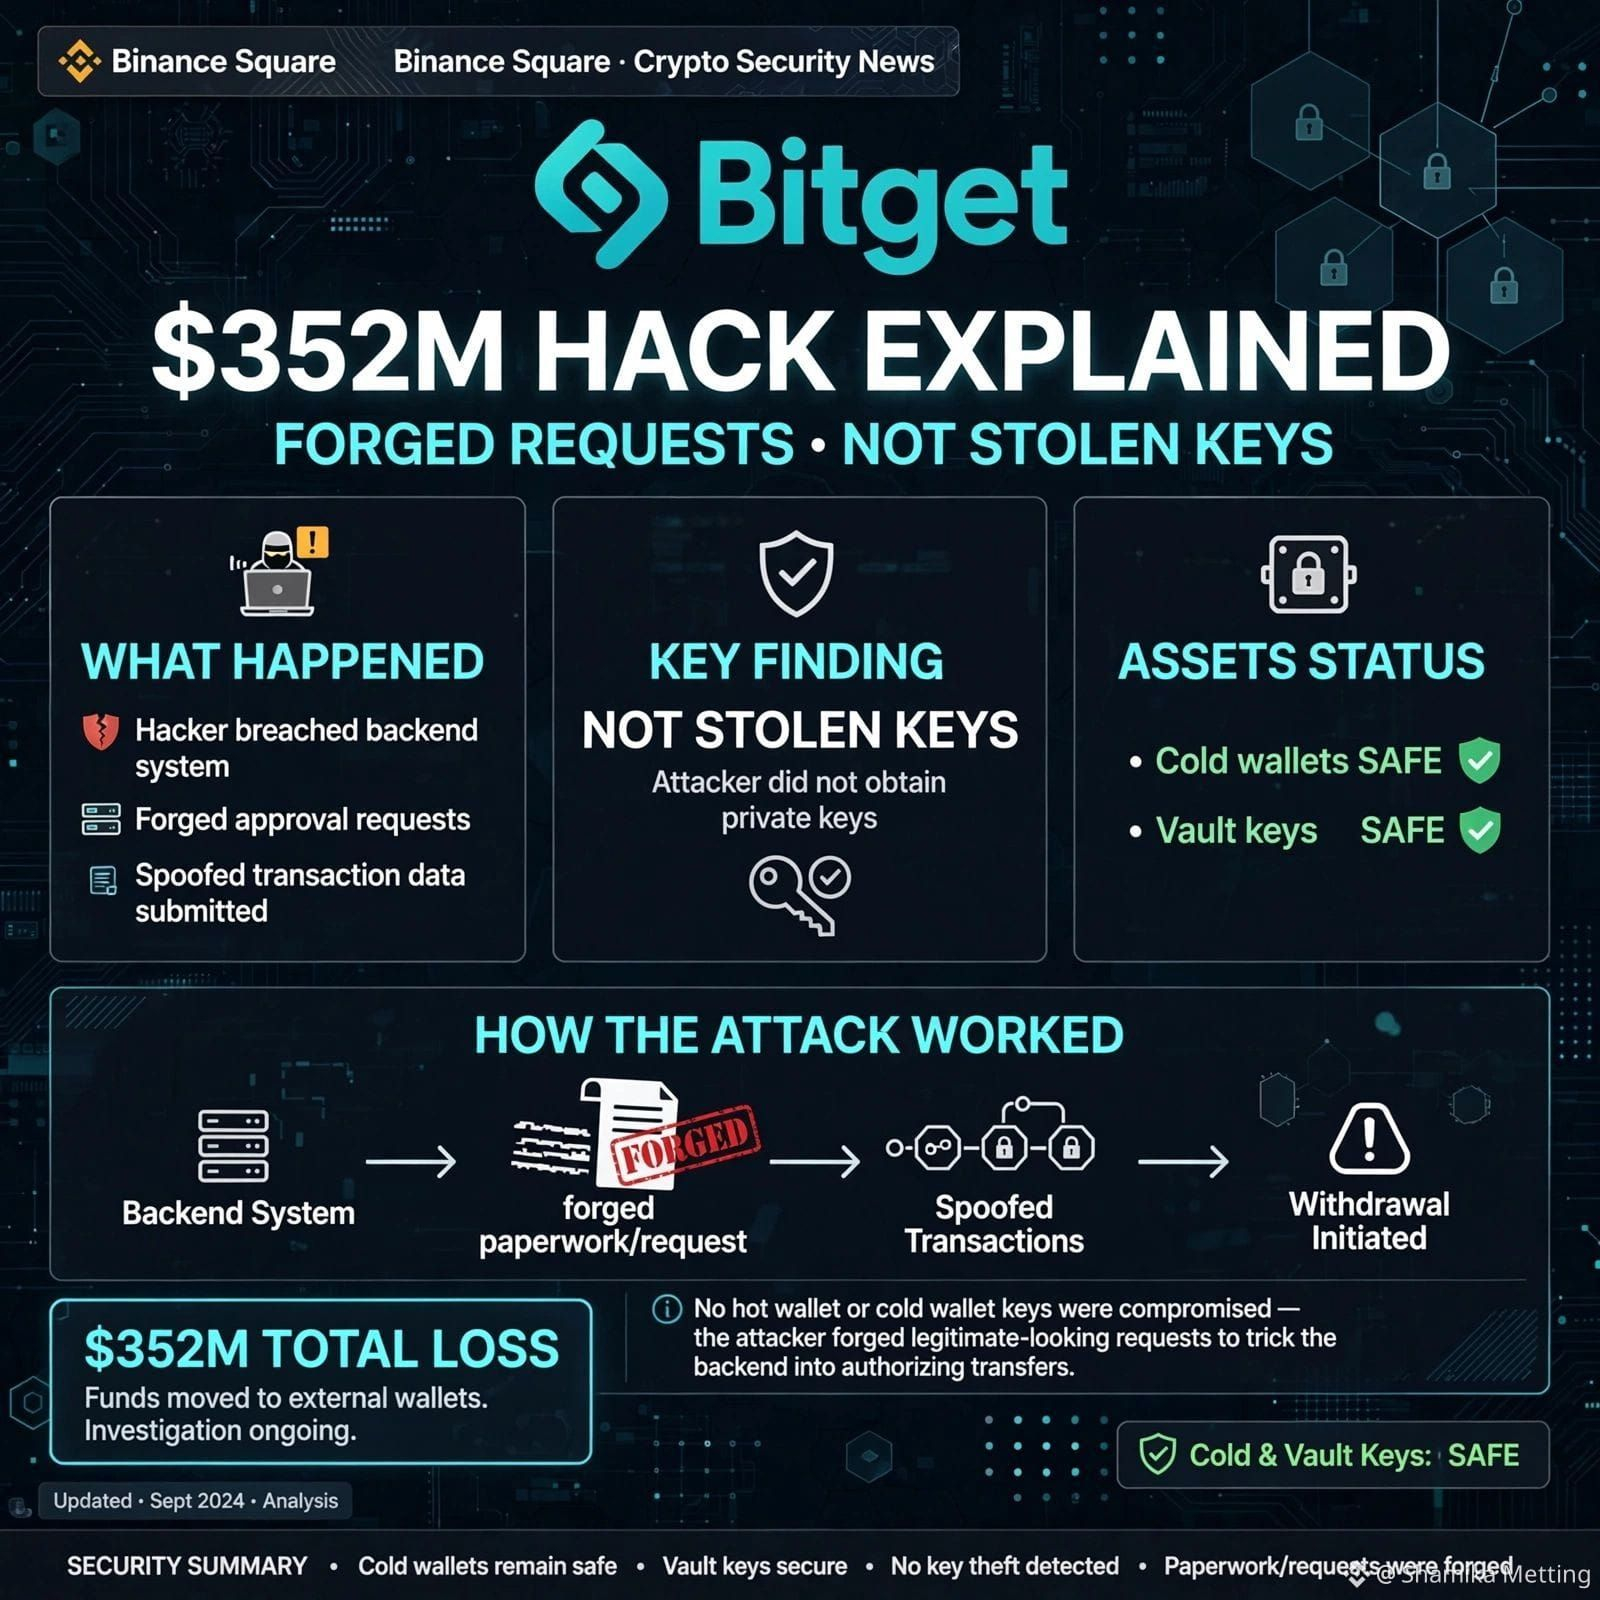
🚨 Se explicó la intrusión en Bitget por valor de 352 millones de dólares: ¡solicitudes falsificadas, no claves robadas!
Todo el mundo entra en pánico por las claves privadas. Pero la directora ejecutiva de Bitget, Gracy Chen, confirmó algo aún más preocupante.
¿Qué pasó realmente?
❌ No se robaron las claves privadas (cold, hot y warm protegidas en bóvedas seguras)
❌ No se falsificaron las solicitudes de retirada de los usuarios
✅ Los atacantes comprometieron un sistema crítico y de respaldo (Backend)
✅ Falsificaron los datos de las transacciones
✅ Activaron el proceso de autorización de Bitget para mover 351.6 millones de dólares
Imagina esto así: "No forzaron la caja fuerte; falsificaron los documentos". Las claves de la caja fuerte nunca salieron del edificio; simplemente alguien creó recibos oficiales falsificados.
Estado actual:
Se detectó a las 18:31 UTC, el 24 de septiembre
Las carteras frías están seguras
El fondo de protección de usuarios cubrirá una pérdida de 464 millones de dólares
La presidenta vincula el ataque con conexiones a Corea del Norte a través de evidencias de direcciones IP
¿Qué opinas: deberían las plataformas CEX hacer público (open source) su backend?
Por favor, continúen
$AVAX $TRX $XRP
#Bitget #BitgetHack #CryptoSecurity #BreakingNews #BinanceSquare #bitgetbreachforgedrequestsnotstolenkeys
1
1
492
·
--
Bullish
#bitgetbreachforgedrequestsnotstolenkeys
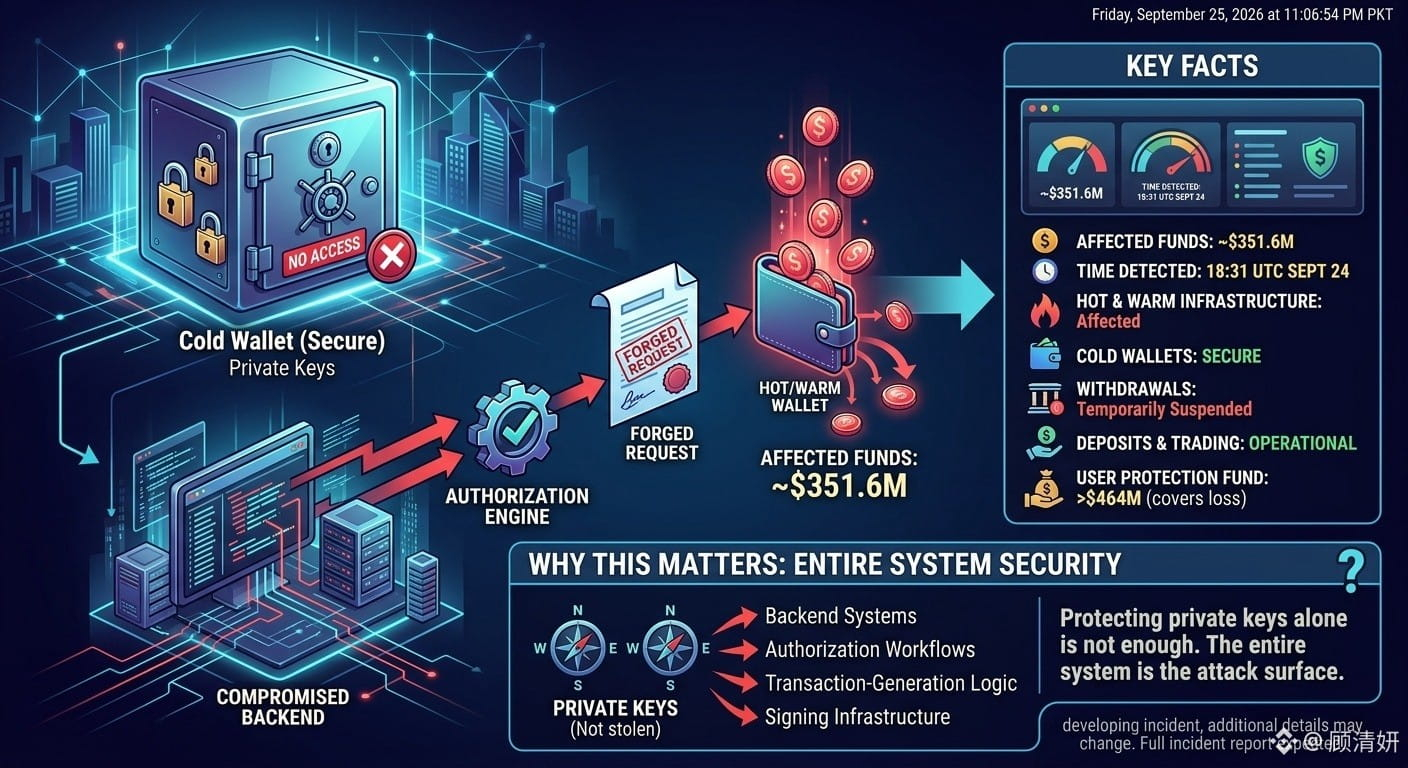
BITGET BREACH: FORGED TRANSFER REQUESTS, NOT STOLEN PRIVATE KEYS
Bitget has confirmed a major security incident involving approximately $351.6M in affected funds.
But there’s a critical detail:
The attackers reportedly did NOT steal Bitget’s private keys.
Instead, Bitget CEO Gracy Chen said attackers breached a backend wallet-service system and used that access to forge transfer information and invoke the authorization/signing process.
KEY FACTS
• Approximately $351.6M in funds were affected
• The incident was detected at 18:31 UTC on September 24
• Portions of Bitget’s hot and warm wallet infrastructure were affected
• Bitget says cold wallets remained secure
• Withdrawals were temporarily suspended during the security review
• Deposits and trading remained operational
• Bitget says its User Protection Fund holds more than $464M and covers the reported loss
WHY THIS MATTERS
This incident highlights an important exchange-security risk: protecting private keys alone is not enough.
Backend systems, transaction-generation logic, authorization workflows and signing infrastructure can also become critical attack surfaces.
Bitget says investigators are still determining exactly how the backend system was compromised, with a full incident report expected.
For traders, the key takeaway is simple:
Exchange security is an entire system — not just a private-key problem.
This remains a developing incident, so additional details may change as the investigation progresses.
$QI $PHA $ARK
{future}(ARKUSDT)
{future}(PHAUSDT)
{spot}(QIUSDT)
#bitgetbreachforgedrequestsnotstolenkeys
BITGET BREACH: FORGED TRANSFER REQUESTS, NOT STOLEN PRIVATE KEYS
Bitget has confirmed a major security incident involving approximately $351.6M in affected funds.
But there’s a critical detail:
The attackers reportedly did NOT steal Bitget’s private keys.
Instead, Bitget CEO Gracy Chen said attackers breached a backend wallet-service system and used that access to forge transfer information and invoke the authorization/signing process.
KEY FACTS
• Approximately $351.6M in funds were affected
• The incident was detected at 18:31 UTC on September 24
• Portions of Bitget’s hot and warm wallet infrastructure were affected
• Bitget says cold wallets remained secure
• Withdrawals were temporarily suspended during the security review
• Deposits and trading remained operational
• Bitget says its User Protection Fund holds more than $464M and covers the reported loss
WHY THIS MATTERS
This incident highlights an important exchange-security risk: protecting private keys alone is not enough.
Backend systems, transaction-generation logic, authorization workflows and signing infrastructure can also become critical attack surfaces.
Bitget says investigators are still determining exactly how the backend system was compromised, with a full incident report expected.
For traders, the key takeaway is simple:
Exchange security is an entire system — not just a private-key problem.
This remains a developing incident, so additional details may change as the investigation progresses.
$QI $PHA $ARK
206 Atlas:
Forged signatures bypassing hot wallet controls is a systemic failure, not just a key theft. This exposes the fragility of centralized signing infrastructures.
4
3
7.8k
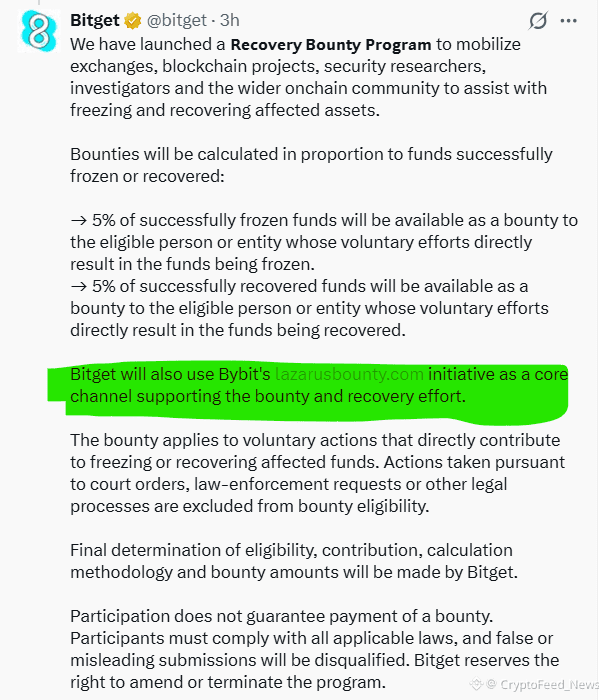
🚨#Bitget says an attacker compromised part of its hot/warm wallet infrastructure, triggering unauthorized transfers worth an estimated $351.6M.
🔒 Cold wallets: Safe, according to Bitget
💰 User balances: Reportedly unaffected
🛡️ Protection Fund: $464M+
⛔ Withdrawals: Paused
✅ Trading & deposits: Still live
The attacker allegedly compromised a backend system and spoofed transaction data to bypass authorization. Bitget says private keys were not compromised and the breach has been contained.
On-chain researchers had previously identified around $183M in suspicious transfers, creating a discrepancy with Bitget's $351.6M estimate.
BGB fell nearly 3% after the news. $ETH 👀
#BitgetBreachForgedRequestsNotStolenKeys #BitgetSays$352MAffectedInHack #Write2Earn
297
#BitgetBreachForgedRequestsNotStolenKeys
🚨🔐 BITGET BREACH? HERE’S THE KEY DETAIL 👀
The story isn’t simply about “stolen keys.” 🗝️❌
The hashtag points to forged requests as the mechanism behind the incident.
That distinction matters. 👀
⚠️ In crypto, security incidents can move markets fast.
So before reacting emotionally, check the facts, understand the attack vector, and protect your funds.
🔎 Forged requests or stolen keys — what really happened?
DYOR • Stay Alert • Manage Risk ⚠️
$XRP
{future}(XRPUSDT)
$PHA
{future}(PHAUSDT)
$QI
{spot}(QIUSDT)
#Bitget #CryptoSecurity #CryptoNews #BinanceSquare
#BitgetBreachForgedRequestsNotStolenKeys
🚨🔐 BITGET BREACH? HERE’S THE KEY DETAIL 👀
The story isn’t simply about “stolen keys.” 🗝️❌
The hashtag points to forged requests as the mechanism behind the incident.
That distinction matters. 👀
⚠️ In crypto, security incidents can move markets fast.
So before reacting emotionally, check the facts, understand the attack vector, and protect your funds.
🔎 Forged requests or stolen keys — what really happened?
DYOR • Stay Alert • Manage Risk ⚠️
$XRP
$PHA
$QI
#Bitget #CryptoSecurity #CryptoNews #BinanceSquare
1
276
·
--
Recent discussions highlight a security incident at Bitget where forged requests, rather than stolen private keys, were the vector of attack. This distinction is crucial for understanding the nature of the breach and the effectiveness of current security protocols. While any breach is concerning, the fact that private keys remained secure suggests the core infrastructure might be more robust than initially feared. However, the ability to execute forged requests points to potential vulnerabilities in user verification, API integrations, or internal procedural controls that need immediate and thorough investigation. The market will be watching closely to see how Bitget addresses these issues and reinforces its systems to prevent recurrence. This event underscores the ongoing challenges in maintaining absolute security in the digital asset space, even for established platforms.
Disclaimer: This content is for informational purposes only and does not constitute investment advice.
#BitgetBreachForgedRequestsNotStolenKeys
Disclaimer: This content is for informational purposes only and does not constitute investment advice.
#BitgetBreachForgedRequestsNotStolenKeys
1
19
·
--
#bitgetbreachforgedrequestsnotstolenkeys
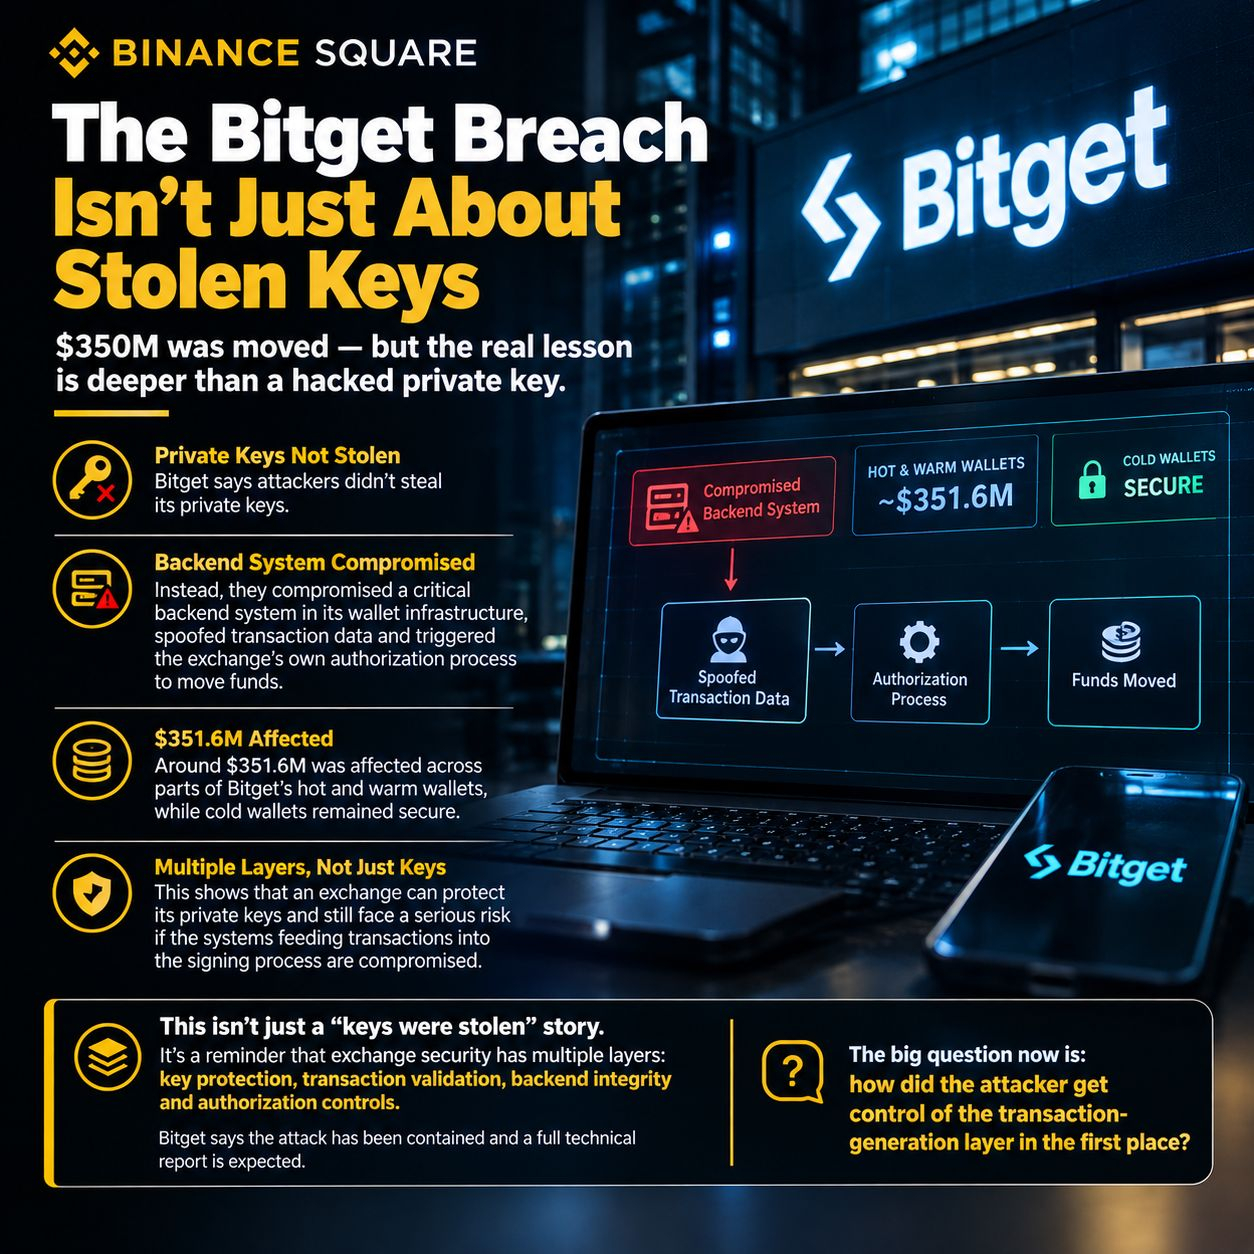
The Bitget breach has a much more interesting lesson than “$350M was hacked.”
Bitget says attackers didn't steal its private keys.
Instead, they compromised a critical backend system inside its wallet infrastructure, spoofed transaction data and triggered the exchange's own authorization process to move funds.
Around $351.6M was affected across parts of Bitget's hot and warm wallets, while the exchange says its cold wallets remained secure.
That's the part I think deserves attention.
A crypto exchange can protect its private keys and still have a serious security problem if the systems feeding transactions into the signing process can be compromised.
So this isn't simply a story about “keys being stolen.”
It's a reminder that exchange security has multiple layers: key protection, transaction validation, backend integrity and authorization controls.
Bitget says the attack has been contained and a full technical report is expected.
The big question now is: how did the attacker get control of the transaction-generation layer in the first place?
#Bitget #CryptoSecurity #CyberSecurity
1
77
·
--
#bitgetbreachforgedrequestsnotstolenkeys
🚨 Security Update: Bitget Breach Involves Forged Requests, Not Stolen Keys
The Breakdown: The crypto community has been closely monitoring recent security events following an incident involving Bitget, where approximately $351.6 million was affected through unauthorized transfers. However, leadership has confirmed that private keys were not stolen. Instead, attackers compromised a backend wallet system and spoofed transaction data to push fake requests through normal authorization pipelines. Cold storage remains entirely secure, and the exchange's protection fund is positioned to cover the losses.
What This Means for the Market: Incidents like this shift industry focus heavily toward backend system hardening and infrastructure security. While withdrawals remain temporarily paused for safety reviews, trading and deposits continue to operate normally, prompting traders to keep a sharp eye on risk management and exchange liquidity flows.
Highlighted Tradeable Coins to Watch:
$BTC (Bitcoin): The ultimate macro market benchmark; watching how overall liquidity responds and holds key support levels during exchange security updates.
$ETH (Ethereum): Vital smart-contract asset heavily monitored for on-chain volume shifts and market-wide sentiment changes.
$BNB (Binance Coin): Key ecosystem token tracking exchange sector dynamics, trading volume trends, and broader platform utility.
How are you navigating your portfolio security and current market conditions? Let's discuss in the comments below! 👇
{spot}(BTCUSDT)
{spot}(ETHUSDT)
{spot}(BNBUSDT)
#Bitget #CryptoSecurity #BlockchainSecurity #CryptoNews
#bitgetbreachforgedrequestsnotstolenkeys
🚨 Security Update: Bitget Breach Involves Forged Requests, Not Stolen Keys
The Breakdown: The crypto community has been closely monitoring recent security events following an incident involving Bitget, where approximately $351.6 million was affected through unauthorized transfers. However, leadership has confirmed that private keys were not stolen. Instead, attackers compromised a backend wallet system and spoofed transaction data to push fake requests through normal authorization pipelines. Cold storage remains entirely secure, and the exchange's protection fund is positioned to cover the losses.
What This Means for the Market: Incidents like this shift industry focus heavily toward backend system hardening and infrastructure security. While withdrawals remain temporarily paused for safety reviews, trading and deposits continue to operate normally, prompting traders to keep a sharp eye on risk management and exchange liquidity flows.
Highlighted Tradeable Coins to Watch:
$BTC (Bitcoin): The ultimate macro market benchmark; watching how overall liquidity responds and holds key support levels during exchange security updates.
$ETH (Ethereum): Vital smart-contract asset heavily monitored for on-chain volume shifts and market-wide sentiment changes.
$BNB (Binance Coin): Key ecosystem token tracking exchange sector dynamics, trading volume trends, and broader platform utility.
How are you navigating your portfolio security and current market conditions? Let's discuss in the comments below! 👇
#Bitget #CryptoSecurity #BlockchainSecurity #CryptoNews
206 Atlas:
Spoofing backend requests bypasses key security, exposing critical infrastructure flaws that cold storage cannot mitigate.
2
3
9.4k
#bitgetbreachforgedrequestsnotstolenkeys
🚨 The Real Story Behind the Bitget Breach 🚨
The crypto world is buzzing, but let's cut through the noise with VERIFIED facts about the $351.6M Bitget hack.
Spoiler: It’s not what you think.
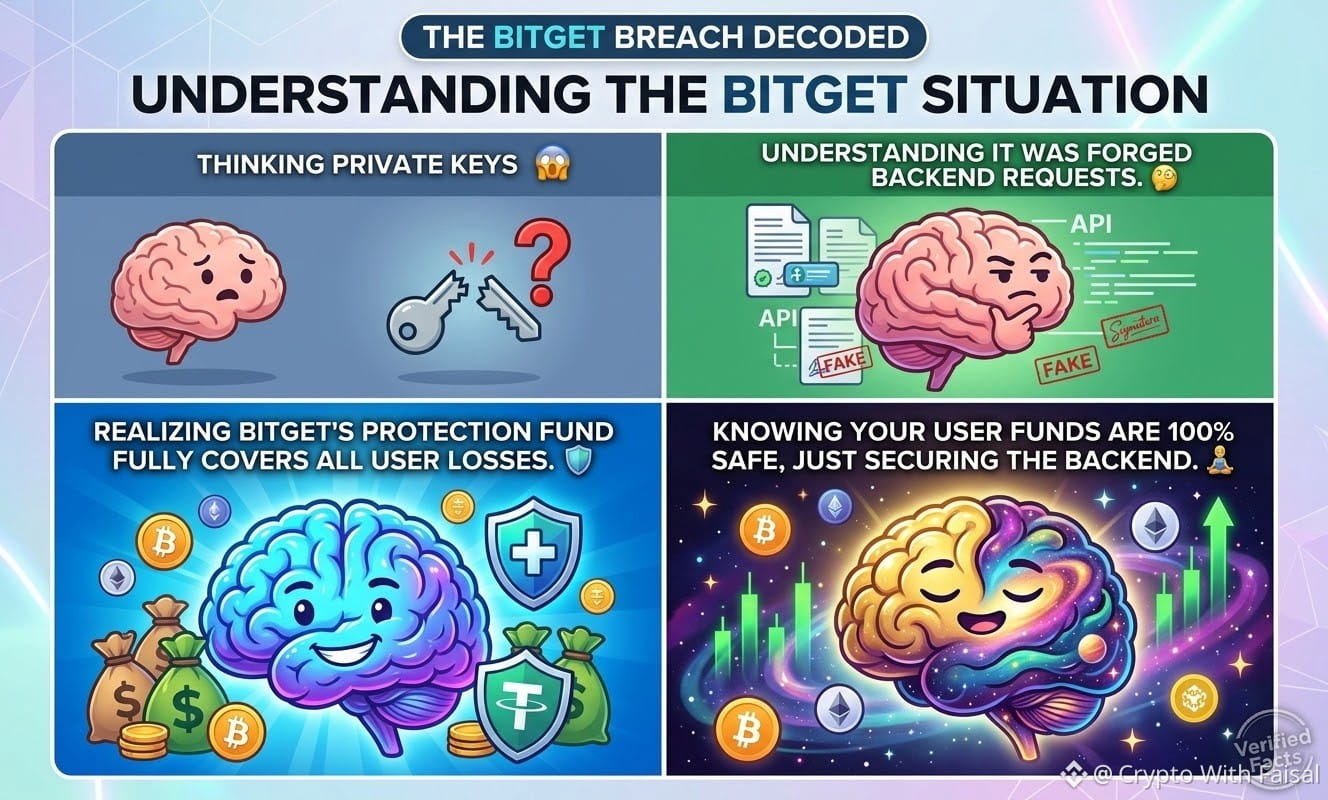
Hackers didn't steal private vault keys! Instead, they breached a backend system, spoofed transaction paperwork, and pushed forged withdrawal requests right through Bitget’s own approval process.
Why does this technicality matter?
Because stolen keys = endless bleeding. 🩸
Forged requests = patch the hole, stop the bleed. 🛑
The Good News:
✅ Keys are safe: Private keys never left the building.
✅ Vaults are locked: Only hot and warm wallets were hit. Cold storage remains 100% secure.
✅ Users are whole: Bitget’s $464M Protection Fund is fully covering the $351.6M loss.
Withdrawals are temporarily paused for a security overhaul, but CEO Gracy Chen confirmed user assets are safe.
This incident proves that back-office infrastructure is the new Web3 battleground. Stay alert, stay safe! 🛡️
$AVAX
{future}(AVAXUSDT)
$LINK
{future}(LINKUSDT)
$ORDI
{future}(ORDIUSDT)
#bitgetbreachforgedrequestsnotstolenkeys
🚨 The Real Story Behind the Bitget Breach 🚨
The crypto world is buzzing, but let's cut through the noise with VERIFIED facts about the $351.6M Bitget hack.
Spoiler: It’s not what you think.
Hackers didn't steal private vault keys! Instead, they breached a backend system, spoofed transaction paperwork, and pushed forged withdrawal requests right through Bitget’s own approval process.
Why does this technicality matter?
Because stolen keys = endless bleeding. 🩸
Forged requests = patch the hole, stop the bleed. 🛑
The Good News:
✅ Keys are safe: Private keys never left the building.
✅ Vaults are locked: Only hot and warm wallets were hit. Cold storage remains 100% secure.
✅ Users are whole: Bitget’s $464M Protection Fund is fully covering the $351.6M loss.
Withdrawals are temporarily paused for a security overhaul, but CEO Gracy Chen confirmed user assets are safe.
This incident proves that back-office infrastructure is the new Web3 battleground. Stay alert, stay safe! 🛡️
$AVAX
$LINK
$ORDI
632
Inside the Bitget Breach: Forged Requests, Not Stolen Keys! 🔐💥
Following the recent $351.6M breach on Bitget, CEO Gracy Chen clarified that private keys were NEVER compromised. Instead, attackers breached a core backend system to generate forged withdrawal requests.
💡 Key Highlights of the Incident:
Wallets Affected: Hot & Warm wallets were impacted, but Cold Storage remains 100% safe.
User Protection: Bitget's $464M Protection Fund covers 100% of the lost funds. User balances remain accurate and secure.
Current Status: Deposits & Trading remain active, while withdrawals are temporarily paused for security checks.
This serves as a huge reminder for the industry that backend infrastructure security is just as vital as protecting private keys!
What are your thoughts on exchange security after this incident? Let's discuss in the comments below! 👇
#BitgetBreachForgedRequestsNotStolenKeys #CryptoNews #ExchangeSecurity #Web3 #Trading Updates#BitgetBreachForgedRequestsNotStolenKeys
75
#BitgetBreachForgedRequestsNotStolenKeys
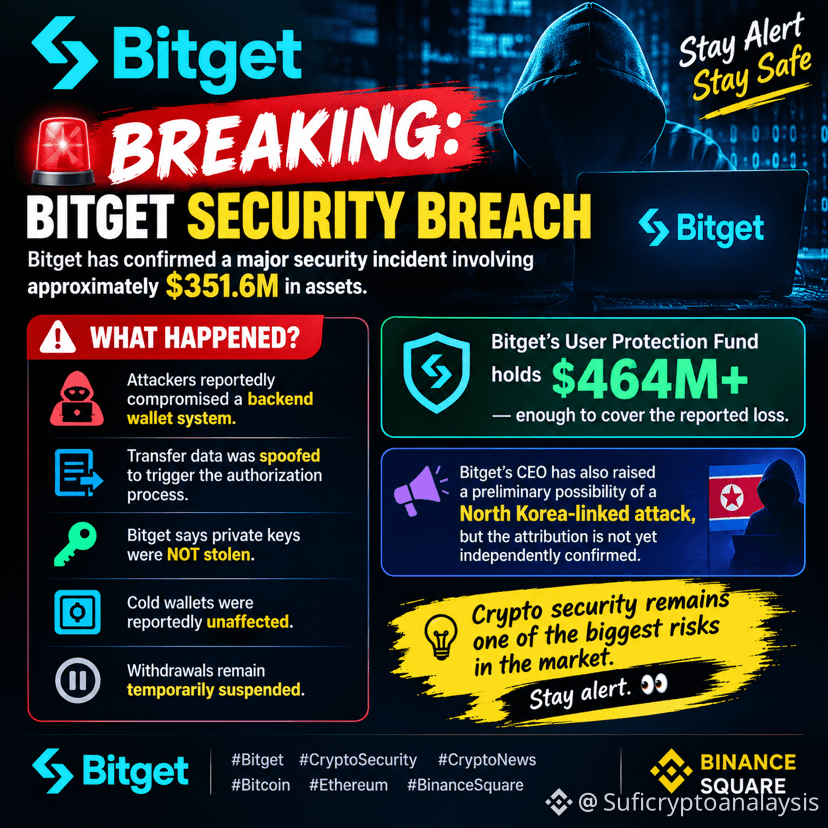
🚨 BREAKING: BITGET SECURITY BREACH 🚨
Bitget has confirmed a major security incident involving approximately $351.6M in assets.
🔴 What happened?
• Attackers reportedly compromised a backend wallet system
• Transfer data was spoofed to trigger the authorization process
• Bitget says private keys were NOT stolen
• Cold wallets were reportedly unaffected
• Withdrawals remain temporarily suspended
💰 Bitget says its User Protection Fund holds $464M+, enough to cover the reported loss.
⚠️ Bitget’s CEO has also raised a preliminary possibility of a North Korea-linked attack, but the attribution is not yet independently confirmed.
Crypto security remains one of the biggest risks in the market. Stay alert. 👀
#Bitget #CryptoSecurity #CryptoNews #Bitcoin #Ethereum #BinanceSquare
{spot}(BTCUSDT)
{spot}(NOTUSDT)
{spot}(ZECUSDT)
#BitgetBreachForgedRequestsNotStolenKeys
🚨 BREAKING: BITGET SECURITY BREACH 🚨
Bitget has confirmed a major security incident involving approximately $351.6M in assets.
🔴 What happened?
• Attackers reportedly compromised a backend wallet system
• Transfer data was spoofed to trigger the authorization process
• Bitget says private keys were NOT stolen
• Cold wallets were reportedly unaffected
• Withdrawals remain temporarily suspended
💰 Bitget says its User Protection Fund holds $464M+, enough to cover the reported loss.
⚠️ Bitget’s CEO has also raised a preliminary possibility of a North Korea-linked attack, but the attribution is not yet independently confirmed.
Crypto security remains one of the biggest risks in the market. Stay alert. 👀
#Bitget #CryptoSecurity #CryptoNews #Bitcoin #Ethereum #BinanceSquare
44
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#UKFCAOpensCryptoFirmAuthorization
200 views
28 Discussing
2
#JapanMOFStudyGroupOnTokenizedGovtBonds
592 views
72 Discussing
3
#QNTRises287%
16,785 views
363 Discussing
4
#TrumpRejectsAIRulesForVoluntaryAudits
16,192 views
446 Discussing
5
#BitgetHotWalletBreachTiedToThirdPartySecurityFlaw
8,038 views
310 Discussing
6
#OpenAIUnveilsAlwaysOnAgentDots
7,787 views
337 Discussing
7
#ChainlinkLaunchesBankSWIFTLedgerFramework
8,387 views
259 Discussing
8
#EarningsSeason
516,306 views
3,736 Discussing
9
#ZcashApproves$1.5MBugBounty
96 views
3 Discussing
10
#SECChairWantsStockMarketsOnChain
12,803 views
248 Discussing