

#securityalert
securityalert
521,699 vues
1,300 mentions
Populaire
Récents

·
--
🚨 $340K API EXPLOIT SWEEPS $ONE AS FORGED DOCUMENT ATTACK BYPASSES 2FA! 💣
A brutal $340,000 compromise just exposed a dangerous loophole in off-chain account security. 🔍 Attackers leveraged forged verification documents to override security settings, but the real structural failure happened when lingering API keys remained active after the account freeze was lifted.
The instant the 24-hour withdrawal lock expired, exploiters drained over 322k USDT alongside 9.1M $ONE directly through the compromised API without prompting 2FA confirmations. ⚡ This sharp incident highlights why active key audits are just as vital as cold storage discipline.
💡 Have you inspected your active API management permissions today to guarantee zero rogue access? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ONE #SecurityAlert #Crypto #RiskManagement
🛡️ ⚡
135
🔐 MY BINANCE ACCOUNT IS UNHACKABLE 🔐
Hackers are pulling, but my shield is STRONG! 🛡️
Here are my 5 Security Tips to keep your account SAFE:
1️⃣ Enable 2FA - Use Google Authenticator, not SMS.
2️⃣ Anti-Phishing Code - Set it in Binance Security settings.
3️⃣ Never Share - Binance will NEVER ask for your password.
4️⃣ Whitelist Address - Enable Withdrawal Whitelist.
5️⃣ Check URL - Always login at binance.com only.
Stay SAFU!
#SecurityAlert
2
37

🚨 ONGOING SECURITY BREACH SURFACES AS ATTACKER DRAINS ANOTHER $8M FROM $CRYPTO POOLS! ⚠️
The exploit saga deepens as smart contract vulnerabilities remain actively exploited. 🚨 The attacker just siphoned an additional $8M out of protocol reserves, proving that compromised access key channels are still wide open.
Smart money is pulling back liquidity rapidly while watching order flow for sudden dump spikes or laundering routes through mixing services. 📉 When contract integrity breaks, immediate risk preservation trumps every technical pattern on the chart.
Stay nimble and keep an eye on active treasury movements before deploying fresh capital. 🔍 Are you pulling your capital to safety, or waiting to bid the eventual capitulation wick? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #Crypto #SecurityAlert #DeFi #RiskManagement #MarketUpdate
🚨 🛡️
10

·
--
🚨 $CRYPTO PLATFORM BREACH EXPOSES $351M LIQUIDITY DRAIN IN ADVANCED EXPLOIT 🔍
Preliminary investigation into the recent $351.6M exploit on a top-tier exchange points toward state-sponsored cyber footprint patterns. 📊 System-level access allowed direct fund transfers without compromising hot or cold wallet private keys, ruling out insider manipulation at this stage.
💡 Institutional infrastructure risk remains a crucial variable when assessing market-wide liquidity stability. 🔍 As order flow normalizes, monitoring exchange proof-of-reserves and system integrity becomes essential for managing systemic tail risk. 💬 How is this systemic security event impacting your allocation strategy across central order books? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #CRYPTO #SecurityAlert #MarketStructure #RiskManagement
🛡️ 🔍
9
·
--
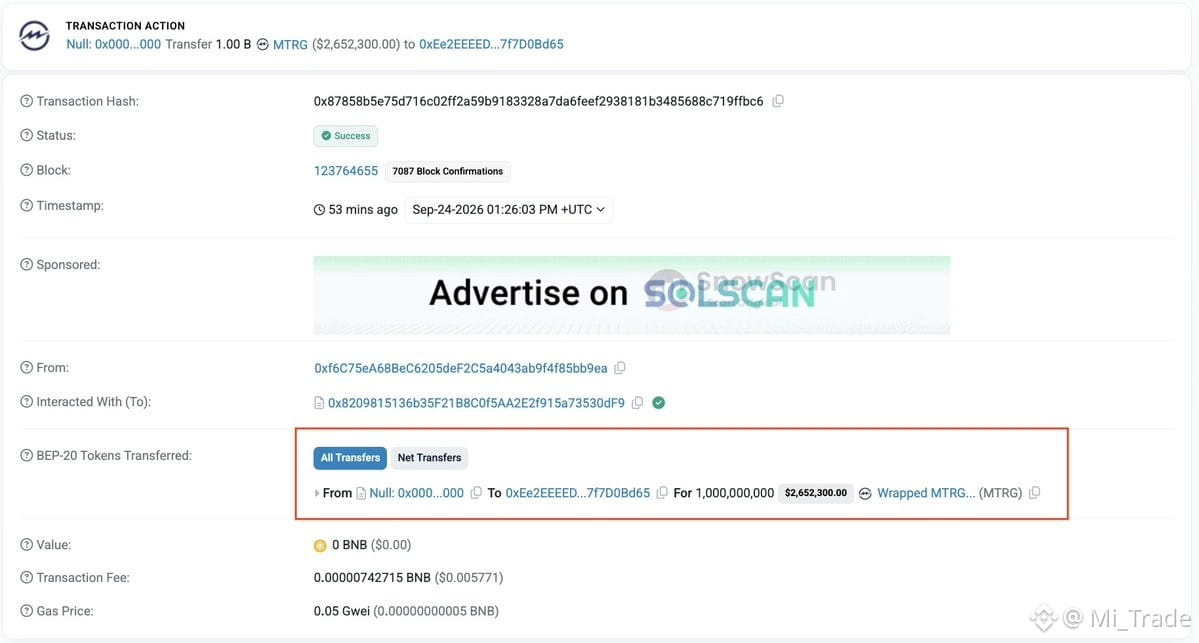
PeckShieldAlert vừa phát đi cảnh báo về sự cố bảo mật nghiêm trọng liên quan đến dự án Meter.io.
Cụ thể, hơn 1 tỷ token #MTRG đã được mint trái phép trên mạng lưới #BNBChain. Ngay sau thông tin này, giá của #MTRG đã ghi nhận mức sụt giảm mạnh -74%.
👀 Market Watch:
$MTRG
Nhà đầu tư cần thận trọng theo dõi các thông báo chính thức từ dự án để cập nhật tình hình.
#CryptoNews #SecurityAlert
Cụ thể, hơn 1 tỷ token #MTRG đã được mint trái phép trên mạng lưới #BNBChain. Ngay sau thông tin này, giá của #MTRG đã ghi nhận mức sụt giảm mạnh -74%.
👀 Market Watch:
$MTRG
Nhà đầu tư cần thận trọng theo dõi các thông báo chính thức từ dự án để cập nhật tình hình.
#CryptoNews #SecurityAlert
39

·
--
🚨 $1.8M DRAINED FROM PAYY NETWORK AS ATTACKER ROUTES STOLEN FUNDS TO $ETH 💣
🔍 On-chain monitors just caught a slick exploit trail where privacy stablecoin protocol Payy Network suffered a $1.8M USDC drain. The attacker primed their wallet via Railgun privacy protocol, converted the hijacked stablecoins directly into $ETH , and fractured the payload across three distinct destination addresses.
📊 Privacy protocols continue to grant bad actors a crucial head start to wash liquidity before re-entering major layer-1 assets. Order flow never lies, and watching where these ETH clusters attempt to cash out next is vital for anticipating sudden localized sell pressure. 💬 Do privacy rails make on-chain defense an uphill battle, or is this just brutal market punishment for weak smart contracts? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #USDC #SecurityAlert #DeFi #Crypto
👁️ 🛡️
11
·
--
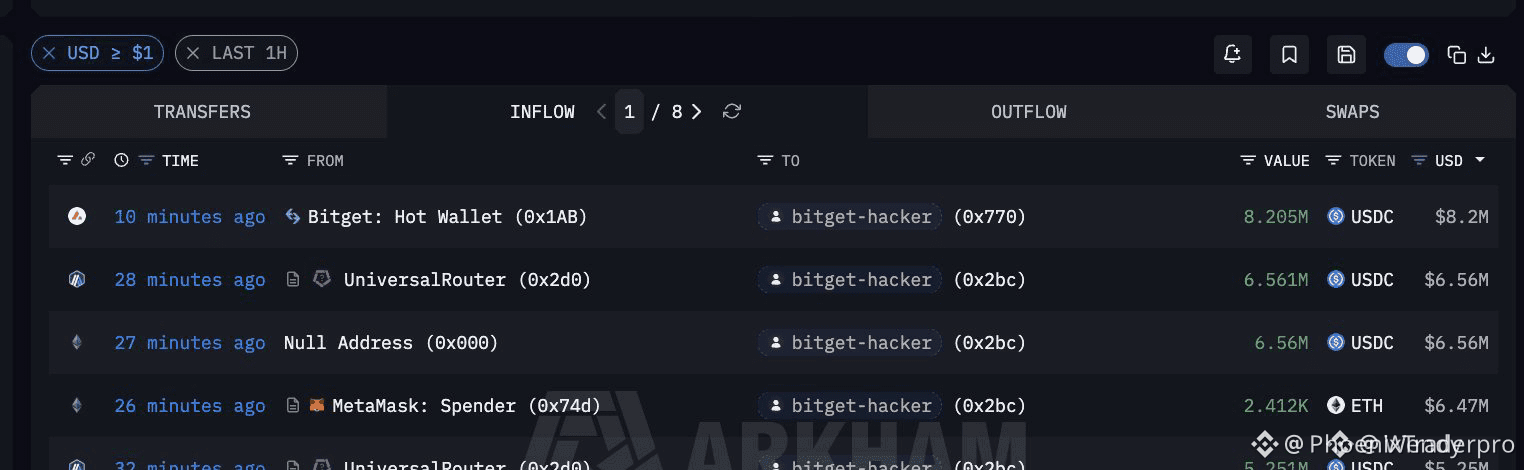
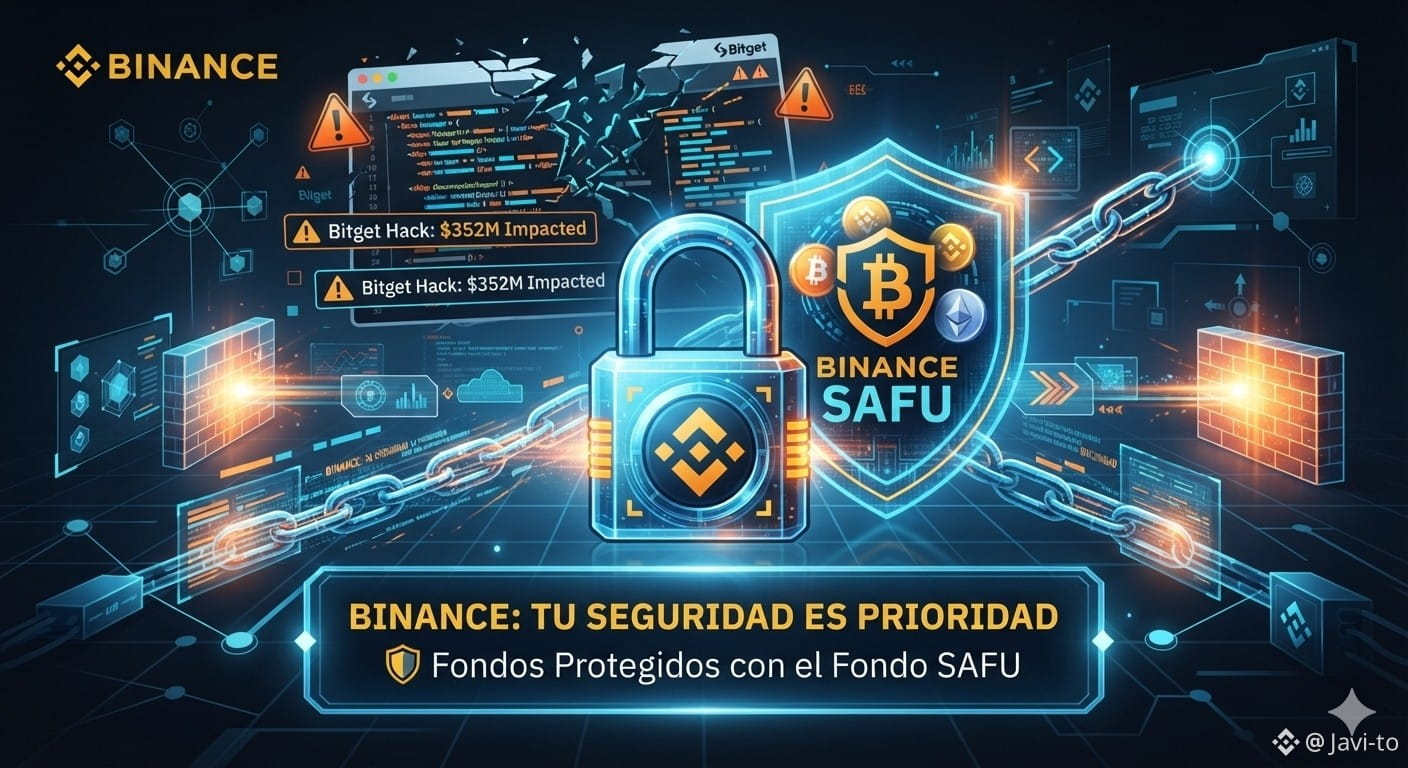
🚨 ¿Tus fondos están realmente seguros? El reciente hackeo millonario a Bitget por 352 millones de dólares encendió las alarmas en el mundo cripto. Aunque su CEO, Gracy Chen, aseguró que el capital de los usuarios está respaldado por su fondo de protección, este evento nos recuerda la importancia de elegir plataformas con la máxima infraestructura de seguridad. [1, 2, 3, 4]
En Binance, la protección no es una promesa, es un estándar activo. Con el fondo SAFU (Safe Asset Fund for Users), un estricto monitoreo de billeteras en tiempo real y pruebas de reservas (PoR) 1:1, tu tranquilidad es nuestra prioridad.
#SecurityAlert #SecurityTokenization
{spot}(DOGEUSDT)
{spot}(SOLUSDT)
{spot}(PEPEUSDT)
🔒 ¡Tu seguridad primero!
🚨 ¿Tus fondos están realmente seguros? El reciente hackeo millonario a Bitget por 352 millones de dólares encendió las alarmas en el mundo cripto. Aunque su CEO, Gracy Chen, aseguró que el capital de los usuarios está respaldado por su fondo de protección, este evento nos recuerda la importancia de elegir plataformas con la máxima infraestructura de seguridad. [1, 2, 3, 4]
En Binance, la protección no es una promesa, es un estándar activo. Con el fondo SAFU (Safe Asset Fund for Users), un estricto monitoreo de billeteras en tiempo real y pruebas de reservas (PoR) 1:1, tu tranquilidad es nuestra prioridad.
#SecurityAlert #SecurityTokenization
🔒 ¡Tu seguridad primero!
En Binance, la protección no es una promesa, es un estándar activo. Con el fondo SAFU (Safe Asset Fund for Users), un estricto monitoreo de billeteras en tiempo real y pruebas de reservas (PoR) 1:1, tu tranquilidad es nuestra prioridad.
#SecurityAlert #SecurityTokenization
🔒 ¡Tu seguridad primero!
2
385
·
--
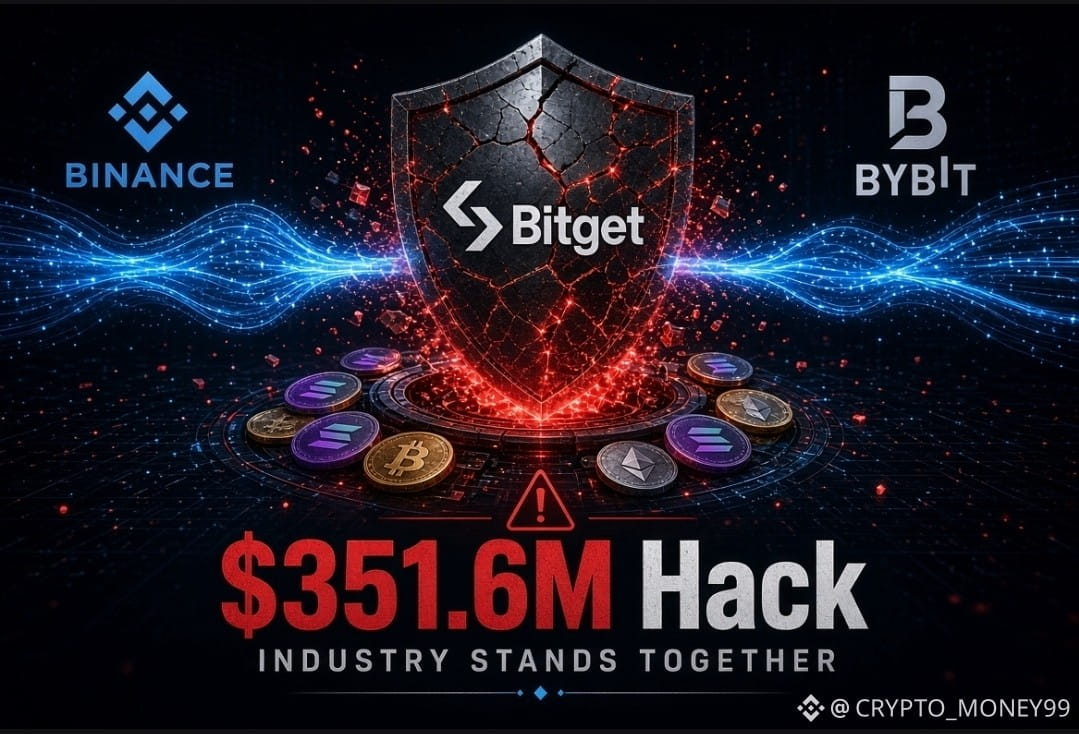
🚨 اختراق Bitget بـ 351.6 مليون دولار… والصناعة تتوحد
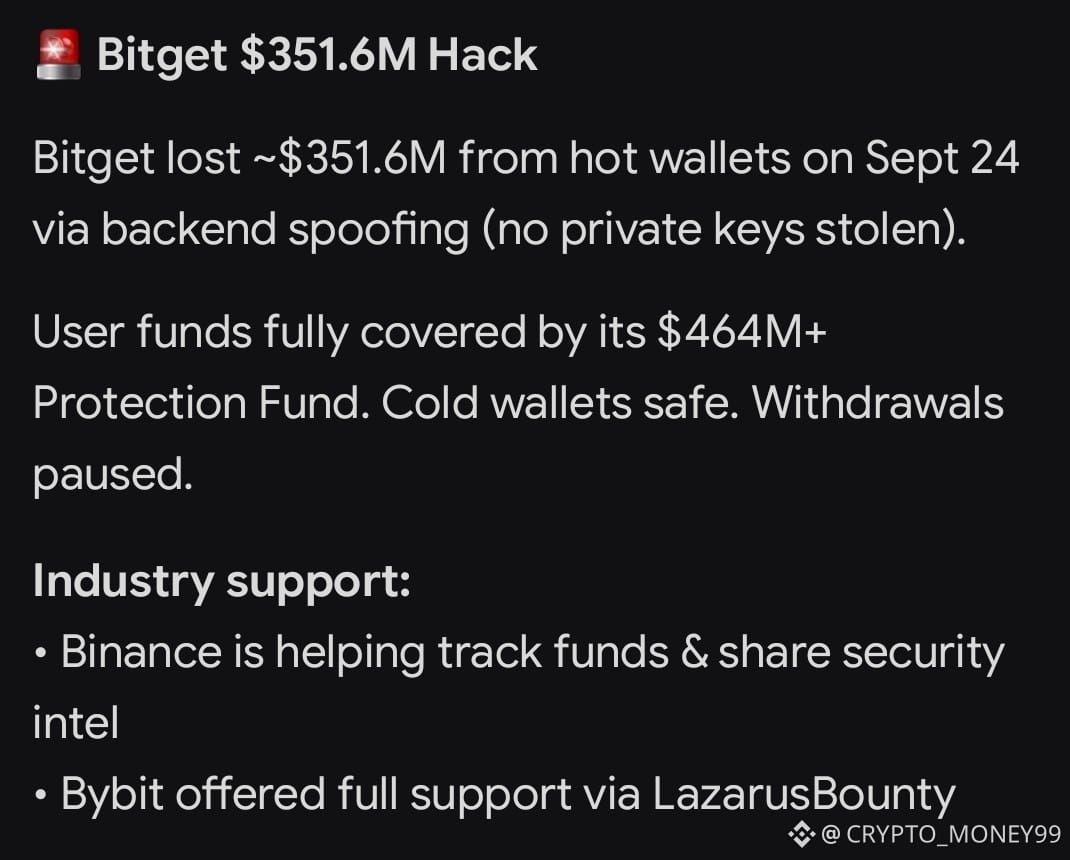
في 24 سبتمبر، تعرضت Bitget لاختراق في المحافظ الساخنة بقيمة تقارب 351.6 مليون دولار.
المفاتيح الخاصة لم تُسرق، والهجوم استهدف نظام الـ backend عبر تزوير بيانات المعاملات.
أهم النقاط:
• أموال المستخدمين آمنة ومغطاة بالكامل من صندوق الحماية (أكثر من 464 مليون دولار).
• المحافظ الباردة لم تتأثر.
• السحوبات متوقفة مؤقتاً، والتداول والإيداع مستمران.
واللافت في هذا الحادث هو موقف رواد الصناعة:
🔹 Binance (عبر الرئيس التنفيذي المشارك Richard Teng): أعلن أن فريق الأمن في بينانس يعمل بشكل وثيق مع Bitget منذ اللحظة الأولى، ويشارك المعلومات الأمنية ويتابع حركة الأموال المسروقة ويدعم جهود الاسترداد.
🔹 Bybit (عبر Ben Zhou): قدّم دعماً كاملاً وفعّل منصة LazarusBounty لتتبع الأموال، مؤكداً أن Bitget ساعدتهم سابقاً في حادثة مشابهة.
هذا التعاون يذكرنا بأن هجمات البورصات لم تعد شأناً فردياً… بل معركة جماعية بين الصناعة والمهاجمين.
ما رأيك؟ هل يكفي وجود صناديق الحماية، أم أن الاعتماد على المحافظ الساخنة ما زال نقطة ضعف كبيرة؟
#SecurityAlert #HackerNews #crypto #Binance #BTC
2
2.2k
·
--
🚨 CRITICAL SECURITY WARNING FOR ALL $BTC AND CRYPTO HOLDERS ON IOS! ⚠️
A malicious third-party app called FomoPeek is actively exploiting iOS vulnerabilities to target crypto users. ⚠️ Security intelligence confirms the app gains elevated root privileges, exposing private keys, seed phrases, and exchange credentials stored on the device. 🛡️
If you installed this application, act immediately. Delete FomoPeek, update your iOS system software, and sweep your $ETH assets to a brand-new wallet generated on a safe device before unauthorized actors access your vault. 🏦
Tight device security protects your capital just as much as disciplined risk management. 💬 Have you checked your installed mobile apps today to verify your self-custody setup is secure? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #ETH #SecurityAlert #CryptoSecurity #SelfCustody
🚨 🛡️
10

·
--
🚨 SECURITY ALERT: FOMOPEEK IOS EXPLOIT RISKS SELF-CUSTODY $BTC AND SEED PHRASES ⚠️
Institutional risk management extends beyond chart structure down to device security. 🚨 Critical security advisories flag FomoPeek versions 1.1–1.2 on iOS containing malicious vector code capable of escalating privileges to compromise global operational security across your device. 🔍
This is not an isolated wallet breach; elevated local permissions expose private keys, seed phrases, and credential stores across all installed applications. 🛡️ Immediate mitigation requires purging the application, updating iOS, and rotating self-custody funds into newly generated keys on an uncompromised environment. 💡
💬 Have you audited your active iOS devices for this compromised application footprint today? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #SecurityAlert #SelfCustody #CryptoSecurity
🛡️ 💡
30
·
--
🚨 CRITICAL SECURITY WARNING FOR ALL $BTC HOLDERS USING FOMOPEEK APP! 🚨
A devastating iOS kernel exploit embedded in FomoPeek versions 1.1 through 1.2 is actively breaching device sandboxes to decrypt native Keychain data. 🚨 SlowMist and a top-tier exchange security team confirmed the malicious code executes automated remote commands, granting attackers full access to private keys and seed phrases. 🛡️
If you have ever touched this application, generate a fresh wallet on a clean device immediately and migrate your funds before liquidity is drained. 🔍 Security hygiene is the ultimate edge in crypto, and protecting your capital comes before catching the next leg up. 💬 Have you audited your wallet permissions and app access lately? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #SecurityAlert #Crypto #WalletSecurity #RiskManagement
🚨 🛡️
19

·
--
🚨 $BTC ALERT: FAKE HARDWARE WALLET WARNINGS SPREAD VIA EMAIL BREACH 🦈
📊 The breach centers on email infrastructure, not the wallets themselves. Trezor confirmed a compromised mail service, while BitBox flagged a shared newsletter provider targeting multiple Bitcoin firms. 📌 This supply‑chain slip allows attackers to masquerade as trusted brands, leveraging brand credibility to push fraudulent security alerts.
🔍 Treat any unexpected wallet security email as unverified: pause, cross‑check through official channels, and never act on urgent links or requests. 💡 The hardware remains secure, but the communication layer is now a high‑risk vector.
💬 How are you reinforcing verification steps for critical alerts? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #SecurityAlert #CryptoSafety #Phishing
🔥 💎
51
·
--
🛡️ Comment sécuriser votre compte Binance à 100 % : Le guide ultime anti-piratage !La sécurité de vos fonds est la règle n°1 en crypto. Chaque jour, des pirates utilisent des méthodes de plus en plus sophistiquées (phishing, faux support client, malwares) pour s'emparer des identifiants des utilisateurs.
Heureusement, Binance met à votre disposition un arsenal d'outils de sécurité ultras puissants. Voici la checklist indispensable pour verrouiller votre compte comme un coffre-fort. 🔐
1. Activer l'Authentification à Deux Facteurs (2FA)
Ne vous contentez pas du simple mot de passe. Activez au moins deux méthodes de vérification :
Passkeys / Clés de sécurité physiques (YubiKey) : La méthode la plus sûre actuellement.
Binance Authenticator / Google Authenticator : Génère un code temporaire à 6 chiffres mis à jour toutes les 30 secondes.
SMS / Email : Indispensable, mais idéalement combiné avec une application d'authentification.
2. Configurer le Code Anti-Phishing ✉️
Le phishing consiste à vous envoyer de faux e-mails ressemblant à ceux de Binance pour voler vos identifiants.
Comment ça marche ? Dans vos paramètres de sécurité, définissez un Code Anti-Phishing (un mot ou une série de chiffres secrets).
L'avantage : Ce code apparaîtra dans le coin supérieur droit de tous les vrais e-mails envoyés par Binance. Si un e-mail ne contient pas ce code, supprimez-le immédiatement !
3. Gérer la Liste Blanche de Retrait (Whitelisting) 📝
Si un pirate réussit à accéder à votre compte, son premier réflexe sera de retirer vos crypto-monnaies vers son propre portefeuille.
Activer la liste blanche : Cette option bloque tout retrait vers une adresse crypto qui n'a pas été préalablement enregistrée et validée par vos soins.
Délai de verrouillage : Vous pouvez également activer un délai d'attente (par exemple 24h ou 48h) pour l'ajout de toute nouvelle adresse de retrait.
4. Utiliser des Mots de Passe Forts et Uniques 🔑
N'utilisez jamais le même mot de passe pour Binance et pour vos réseaux sociaux ou votre boîte e-mail.
Utilisez un gestionnaire de mots de passe pour générer un mot de passe complexe d'au moins 16 caractères (mélangeant majuscules, minuscules, chiffres et symboles).
5. Gérer les Appareils Autorisés 📱💻
Vérifiez régulièrement la section « Gestion des appareils » dans vos paramètres de sécurité Binance.
Supprimez immédiatement tout appareil ancien, inconnu ou que vous n'utilisez plus.
⚠️ 3 Règles d'or à ne JAMAIS oublier :
1. Binance ne vous demandera JAMAIS votre mot de passe ou vos codes 2FA par message, e-mail ou téléphone.
2. Ne cliquez jamais sur des liens suspects envoyés sur Telegram, WhatsApp ou X (Twitter) prétendant venir du « Support Binance ».
3. Accédez toujours au site officiel en vérifiant l'URL
💡 Et vous, quelles fonctionnalités de sécurité avez-vous déjà activées sur votre compte ? Dites-le moi en commentaire !
👇 Aimez, commentez et partagez cet article pour aider la communauté à garder ses fonds en sécurité !
#BinanceSquare
#SecurityAlert #CryptoSafety #Binance #2FA
🛡️ Comment sécuriser votre compte Binance à 100 % : Le guide ultime anti-piratage !
La sécurité de vos fonds est la règle n°1 en crypto. Chaque jour, des pirates utilisent des méthodes de plus en plus sophistiquées (phishing, faux support client, malwares) pour s'emparer des identifiants des utilisateurs.
Heureusement, Binance met à votre disposition un arsenal d'outils de sécurité ultras puissants. Voici la checklist indispensable pour verrouiller votre compte comme un coffre-fort. 🔐
1. Activer l'Authentification à Deux Facteurs (2FA)
Ne vous contentez pas du simple mot de passe. Activez au moins deux méthodes de vérification :
Passkeys / Clés de sécurité physiques (YubiKey) : La méthode la plus sûre actuellement.
Binance Authenticator / Google Authenticator : Génère un code temporaire à 6 chiffres mis à jour toutes les 30 secondes.
SMS / Email : Indispensable, mais idéalement combiné avec une application d'authentification.
2. Configurer le Code Anti-Phishing ✉️
Le phishing consiste à vous envoyer de faux e-mails ressemblant à ceux de Binance pour voler vos identifiants.
Comment ça marche ? Dans vos paramètres de sécurité, définissez un Code Anti-Phishing (un mot ou une série de chiffres secrets).
L'avantage : Ce code apparaîtra dans le coin supérieur droit de tous les vrais e-mails envoyés par Binance. Si un e-mail ne contient pas ce code, supprimez-le immédiatement !
3. Gérer la Liste Blanche de Retrait (Whitelisting) 📝
Si un pirate réussit à accéder à votre compte, son premier réflexe sera de retirer vos crypto-monnaies vers son propre portefeuille.
Activer la liste blanche : Cette option bloque tout retrait vers une adresse crypto qui n'a pas été préalablement enregistrée et validée par vos soins.
Délai de verrouillage : Vous pouvez également activer un délai d'attente (par exemple 24h ou 48h) pour l'ajout de toute nouvelle adresse de retrait.
4. Utiliser des Mots de Passe Forts et Uniques 🔑
N'utilisez jamais le même mot de passe pour Binance et pour vos réseaux sociaux ou votre boîte e-mail.
Utilisez un gestionnaire de mots de passe pour générer un mot de passe complexe d'au moins 16 caractères (mélangeant majuscules, minuscules, chiffres et symboles).
5. Gérer les Appareils Autorisés 📱💻
Vérifiez régulièrement la section « Gestion des appareils » dans vos paramètres de sécurité Binance.
Supprimez immédiatement tout appareil ancien, inconnu ou que vous n'utilisez plus.
⚠️ 3 Règles d'or à ne JAMAIS oublier :
1. Binance ne vous demandera JAMAIS votre mot de passe ou vos codes 2FA par message, e-mail ou téléphone.
2. Ne cliquez jamais sur des liens suspects envoyés sur Telegram, WhatsApp ou X (Twitter) prétendant venir du « Support Binance ».
3. Accédez toujours au site officiel en vérifiant l'URL
💡 Et vous, quelles fonctionnalités de sécurité avez-vous déjà activées sur votre compte ? Dites-le moi en commentaire !
👇 Aimez, commentez et partagez cet article pour aider la communauté à garder ses fonds en sécurité !
#BinanceSquare
#SecurityAlert #CryptoSafety #Binance #2FA
2
319

🚨 $BTC ALERT: FAKE HARDWARE WALLET EMAILS TARGETING USERS! 💥
🦈 Trezor confirmed its email service was breached, and BitBox flagged a shared newsletter provider that got hit. The attack rides on brand trust, not on the wallets themselves.
📊 The fake alerts can lure users into irreversible actions, so always double‑check through an independent channel before clicking any link. Verify the sender, scan the message for odd URLs, and treat any urgent request with skepticism. 🔍
💬 Are you double‑checking every security email before you act? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #SecurityAlert #HardwareWallet #CryptoSafety
🚀 🔥
24
·
--
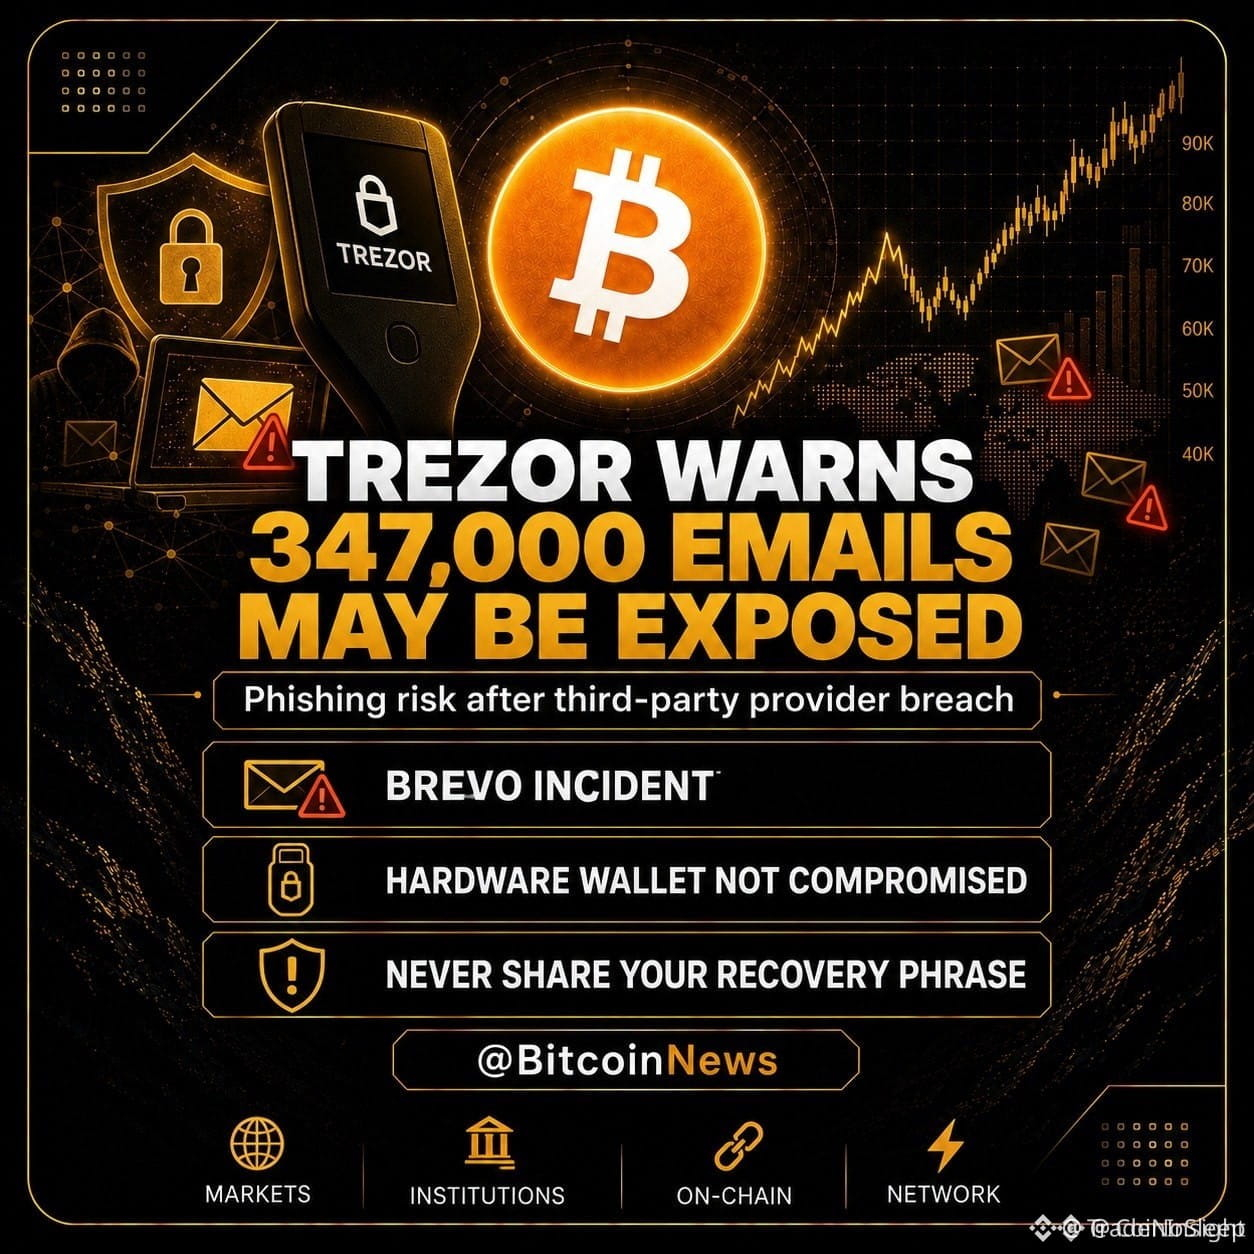
🚨 CRITICAL SECURITY NOTICE REGARDING $BTC HOLDINGS AND TREZOR PHISHING ATTACK ⚠️
A major third-party newsletter breach has exposed 347,000 email addresses, triggering a sophisticated phishing vector targeting $BTC cold storage users. 🔒 Attackers are broadcasting fake security alerts regarding a non-existent entropy vulnerability to trick holders into revealing recovery phrases. 🔍
Hardware devices remain completely uncompromised, proving that institutional security architecture holds firm while social engineering remains the primary attack surface. 🛡️ Smart market participants recognize that operational security is just as vital as managing technical chart structure. 💡
Never input recovery keys into any software interface or email link under any circumstance. 🤔 Are your cold storage protocols fully isolated from social engineering traps? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #SecurityAlert #CryptoSecurity #Web3
🛡️ 👁️
6
·
--
🚨 CRYPTO SECURITY ALERT: LIQUID NETWORK INCIDENT
The crypto security space is watching a major incident involving the Liquid Network, where roughly 4,000 BTC worth around $320 million at the time was reportedly moved during an exploit.
What makes the story unusual is that the parties involved reportedly described themselves as white-hat security researchers.
According to reports, approximately 85% of the Bitcoin was later returned, while questions remain around the funds that have not been recovered.
🔐 Why this matters
The incident is another reminder that even established blockchain infrastructure can face security risks.
For the wider crypto industry, the key questions now are:
• What caused the vulnerability?
• Who was responsible for the transactions?
• Will the remaining funds be recovered?
• What security measures will prevent a repeat?
👀 Crypto security remains one of the biggest issues the industry needs to solve.
$NVDAB $ASTER
#SecurityAlert #CryptoSecurity #BinanceSquareTalks

316

🚨 ATOMICQUEUE CONTRACT FLAW EXPOSED IN ETHER.FI ATTACK — CHECK YOUR $ETH PERMISSIONS! 🚨
A vulnerability inside the AtomicQueue contract just hit ether.fi, resulting in an exploit of roughly 15.45 $ETH . 🔍 The breach stems from a missing access control check on the solver parameter within the solve function, allowing bad actors to manipulate call flows.
By exploiting previously granted ERC-20 token allowances, the attacker forced victim addresses to execute unauthorized transfer calls without signature verification. ⚠️ Technical slip-ups like unchecked approvals leave capital wide open to malicious actors scanning for unmonitored order flows.
💬 Are you regularly revoking old token approvals across your active DeFi protocols, or do you leave your allowances wide open? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #DeFi #SecurityAlert #Crypto
🚨 🛡️
32
·
--
🔴 $VTHO ALERT: HACKERS SPREAD PHISHING EMAILS – SECURE YOUR WALLET NOW! 🚨
🦈 Smart money operators are already flagging a breach on Trezor’s email gateway; hackers are flooding inboxes with a “Critical Security Alert” lure. 📊 The phishing wave targets holders of $VTHO and $IOST , exploiting the recent soft‑sell sentiment to harvest assets in a single click.
💡 Immediate mitigation: abort any link or attachment from the alleged Trezor mail, revoke all unknown dApp connections, and rotate your device seed. 📌 A clean inbox is your first line of defense against the liquidity hunt that could otherwise turn your portfolio into a shark‑fed pool.
💬 Have you secured your hardware wallet and audited your dApp permissions? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #VTHO #SecurityAlert #Phishing #CryptoSafety
🛡️ 🔥
255

·
--
Article
Two-Factor Authentication Setup Guide (Part 1) 1. Why Two-Factor Authentication
Matters on Binance
If you hold crypto on Binance, your password is not
enough to keep your account safe. Data breaches,
phishing emails, and SIM-swap attacks happen every
day, and a password alone can be stolen, guessed, or
leaked. Two-factor authentication (2FA) adds a
second layer of verification, so even if someone gets
your password, they still can't log in or move your
funds without the second code.
Binance requires 2FA for withdrawals above certain
thresholds and strongly recommends it for every account. In this guide, you'll learn the different 2FA
methods Binance supports, how to set up each one,
and which option gives you the strongest protection.
2.Types of 2FA Available on Binance
Binance supports several authentication methods,
and you can enable more than one for layered
protection:
Google Authenticator (App-Based 2FA) —
generates a rotating 6-digit code every 30
seconds, considered one of the more secure and
widely used options
SMS Verification — sends a code to your
registered phone number
Email Verification — sends a code to your
registered email address
Passkey / Security Key (FIDO2) — hardware-based
authentication using a physical key or biometric
passkey
Binance/Google Authenticator combined with
anti-phishing codes — an added layer covered in a
separate guide
Security experts generally rank app-based or
hardware-based 2FA above SMS, since SMS can be
intercepted through SIM-swapping attacks. Where possible, use Google Authenticator or a passkey as
your primary method.
#SecurityAlert #Binance #TwoFactorAuthentication
Two-Factor Authentication Setup Guide (Part 1)
1. Why Two-Factor Authentication
Matters on Binance
If you hold crypto on Binance, your password is not
enough to keep your account safe. Data breaches,
phishing emails, and SIM-swap attacks happen every
day, and a password alone can be stolen, guessed, or
leaked. Two-factor authentication (2FA) adds a
second layer of verification, so even if someone gets
your password, they still can't log in or move your
funds without the second code.
Binance requires 2FA for withdrawals above certain
thresholds and strongly recommends it for every account. In this guide, you'll learn the different 2FA
methods Binance supports, how to set up each one,
and which option gives you the strongest protection.
2.Types of 2FA Available on Binance
Binance supports several authentication methods,
and you can enable more than one for layered
protection:
Google Authenticator (App-Based 2FA) —
generates a rotating 6-digit code every 30
seconds, considered one of the more secure and
widely used options
SMS Verification — sends a code to your
registered phone number
Email Verification — sends a code to your
registered email address
Passkey / Security Key (FIDO2) — hardware-based
authentication using a physical key or biometric
passkey
Binance/Google Authenticator combined with
anti-phishing codes — an added layer covered in a
separate guide
Security experts generally rank app-based or
hardware-based 2FA above SMS, since SMS can be
intercepted through SIM-swapping attacks. Where possible, use Google Authenticator or a passkey as
your primary method.
#SecurityAlert #Binance #TwoFactorAuthentication
116
·
--
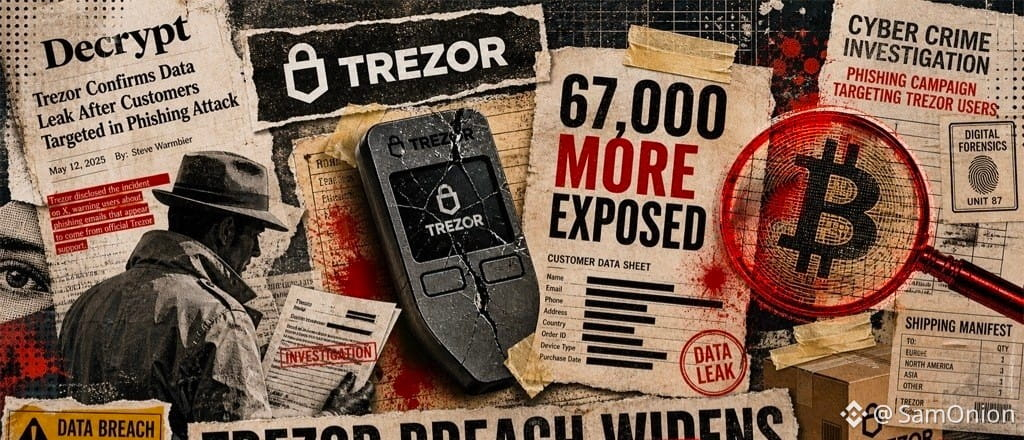
🚨 The disaster widens: Data for an additional 67,000 #Trezor customers exposed in a new deepening breach! 🔐 🚫 🔴
⚠️ Shipping and phone data in the dark web auction... and the company warns of an exceptional wave of phishing #scams ! ✅ 🔍 ⚖️ 😱
#BitcoinEthereumHitMultiMonthHighs
#SecurityAlert
$BTC
{spot}(BTCUSDT)
#zec
$ZEC
{spot}(ZECUSDT)
🚨 The disaster widens: Data for an additional 67,000 #Trezor customers exposed in a new deepening breach! 🔐 🚫 🔴
⚠️ Shipping and phone data in the dark web auction... and the company warns of an exceptional wave of phishing #scams ! ✅ 🔍 ⚖️ 😱
#BitcoinEthereumHitMultiMonthHighs
#SecurityAlert
$BTC
#zec
$ZEC
⚠️ Shipping and phone data in the dark web auction... and the company warns of an exceptional wave of phishing #scams ! ✅ 🔍 ⚖️ 😱
#BitcoinEthereumHitMultiMonthHighs
#SecurityAlert
$BTC
#zec
$ZEC

Good luck 🍀
De SamOnion
1
182
Connectez-vous pour découvrir plus de contenu
Rejoignez la communauté mondiale des adeptes de cryptomonnaies sur Binance Square
⚡️ Suviez les dernières informations importantes sur les cryptomonnaies.
💬 Jugé digne de confiance par la plus grande plateforme d’échange de cryptomonnaies au monde.
👍 Découvrez les connaissances que partagent les créateurs vérifiés.
Adresse e-mail/Nº de téléphone
Sujets d’actualité
1
#BTCFallsBelow$83000
1,353 vues
46 mentions
2
#FedProposesPaymentStablecoinRules
10,126 vues
252 mentions
3
#ChinaMayLetAlibabaByteDanceBuyNvidiaChips
12,737 vues
312 mentions
4
#USChinaRelease$30BTariffCutProductLists
2,150 vues
37 mentions
5
#SKoreaFSCConsidersVirtualAssetMarketMaker
10,050 vues
258 mentions
6
#ChinaIndustrialProfitGrowthSlowsFourthMonth
10,723 vues
264 mentions
7
#BitwiseFilesFinalNEARSpotETFProspectus
126,021 vues
1,830 mentions
8
#BitgetHackerMoves$83MStolenXRP
41,173 vues
178 mentions
9
#SOLSpotETFWeeklyInflow$188M
25,784 vues
141 mentions
10
#DogecoinETFsPostBiggestWeekSinceLaunch
71,376 vues
1,152 mentions