

Z O Y A
11.4k Posts
Z O Y A
Report
Block User
Crypto Enthusiast | Web3 & Markets | Sharing charts, trades & insights | Building in public 🚀
311 Following
24.0K+ Followers
37.5K+ Liked
Posts
All
Quotes
Live
PINNED
·
--
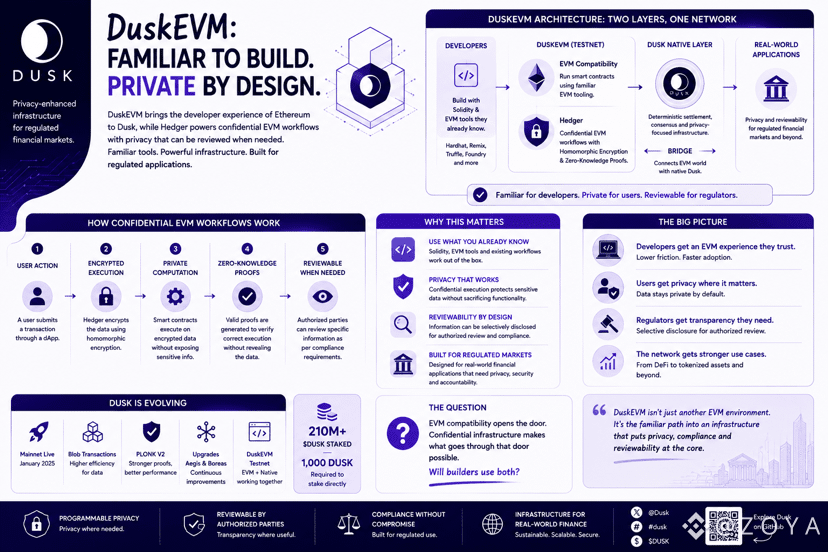
I was thinking about what actually makes an EVM environment useful on a network like Dusk. It’s easy to say “EVM compatible” and leave it there, but familiar tooling only gets you so far. The part I wanted to understand was what happens to the privacy side once developers start building normal EVM applications.
That’s where DuskEVM gets more interesting. It gives builders a familiar Solidity and EVM path into Dusk, while Hedger is designed for confidential EVM workflows using homomorphic encryption and zero-knowledge proofs. So developers don’t have to choose between an environment they already understand and privacy features designed for regulated applications. 🤯
That combination actually makes sense to me. A developer can work with familiar EVM concepts, while the underlying application can still deal with information that shouldn’t necessarily be public. And because Dusk is building for regulated financial markets, there’s also room for authorized review instead of treating privacy as complete invisibility.
I’m still more interested in what people actually build with it than the compatibility label itself 😂. EVM support is useful, but the real test is whether developers can use that familiarity while taking advantage of Dusk’s privacy infrastructure. If those two things work together properly, DuskEVM starts looking like more than just another EVM environment.
@Dusk_Foundation #dusk $DUSK
I was thinking about what actually makes an EVM environment useful on a network like Dusk. It’s easy to say “EVM compatible” and leave it there, but familiar tooling only gets you so far. The part I wanted to understand was what happens to the privacy side once developers start building normal EVM applications.
That’s where DuskEVM gets more interesting. It gives builders a familiar Solidity and EVM path into Dusk, while Hedger is designed for confidential EVM workflows using homomorphic encryption and zero-knowledge proofs. So developers don’t have to choose between an environment they already understand and privacy features designed for regulated applications. 🤯
That combination actually makes sense to me. A developer can work with familiar EVM concepts, while the underlying application can still deal with information that shouldn’t necessarily be public. And because Dusk is building for regulated financial markets, there’s also room for authorized review instead of treating privacy as complete invisibility.
I’m still more interested in what people actually build with it than the compatibility label itself 😂. EVM support is useful, but the real test is whether developers can use that familiarity while taking advantage of Dusk’s privacy infrastructure. If those two things work together properly, DuskEVM starts looking like more than just another EVM environment.
@Dusk #dusk $DUSK
1
3
681
PINNED
·
--
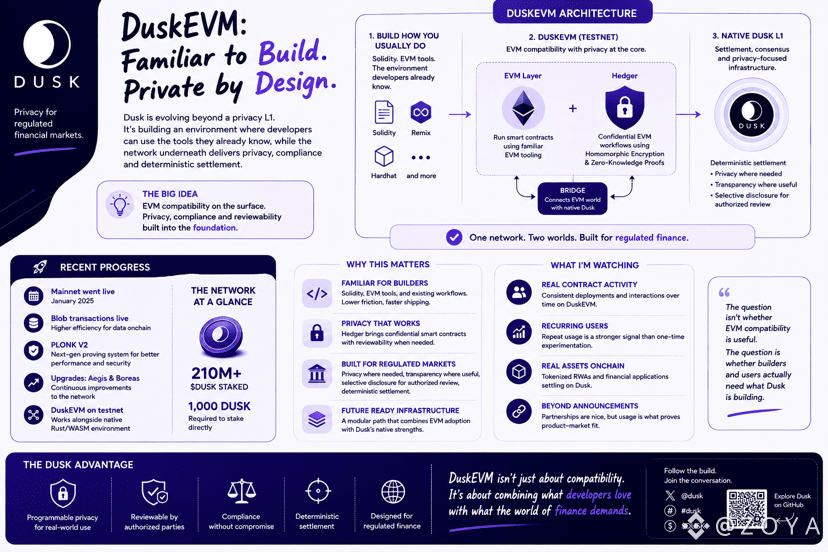
I used to think an EVM-compatible layer was mostly about making a chain easier for developers to use. Then I looked closer at DuskEVM and realized the interesting part is what it gets to sit on top of. You can keep working with familiar EVM tooling instead of having to relearn everything just to access another network.
DuskEVM gives builders a Solidity/EVM path into Dusk, while Hedger is designed to bring confidential EVM workflows into that environment. It uses homomorphic encryption and zero-knowledge proofs to support privacy that can still be reviewed when needed. So the EVM part isn’t really the whole story… it’s the familiar door into the infrastructure Dusk has been building underneath. 🤯
That made me think about how developers usually choose where to build. Familiar tooling matters because nobody wants to rebuild their entire workflow just to experiment with a new chain. But for regulated applications, the infrastructure underneath matters just as much. Being EVM-compatible is useful, but having privacy and reviewability built into the environment is what makes the combination more interesting.
I’m still curious what people will actually build with it 😂, because compatibility alone doesn’t guarantee anyone will use it. But I like the direction. DuskEVM doesn’t seem to be asking developers to choose between familiar EVM development and Dusk’s privacy-focused infrastructure. It’s trying to put the two together, and that’s the part I’ll be watching.
@Dusk_Foundation #dusk $DUSK
I used to think an EVM-compatible layer was mostly about making a chain easier for developers to use. Then I looked closer at DuskEVM and realized the interesting part is what it gets to sit on top of. You can keep working with familiar EVM tooling instead of having to relearn everything just to access another network.
DuskEVM gives builders a Solidity/EVM path into Dusk, while Hedger is designed to bring confidential EVM workflows into that environment. It uses homomorphic encryption and zero-knowledge proofs to support privacy that can still be reviewed when needed. So the EVM part isn’t really the whole story… it’s the familiar door into the infrastructure Dusk has been building underneath. 🤯
That made me think about how developers usually choose where to build. Familiar tooling matters because nobody wants to rebuild their entire workflow just to experiment with a new chain. But for regulated applications, the infrastructure underneath matters just as much. Being EVM-compatible is useful, but having privacy and reviewability built into the environment is what makes the combination more interesting.
I’m still curious what people will actually build with it 😂, because compatibility alone doesn’t guarantee anyone will use it. But I like the direction. DuskEVM doesn’t seem to be asking developers to choose between familiar EVM development and Dusk’s privacy-focused infrastructure. It’s trying to put the two together, and that’s the part I’ll be watching.
@Dusk #dusk $DUSK
3
5
434
·
--
Verified
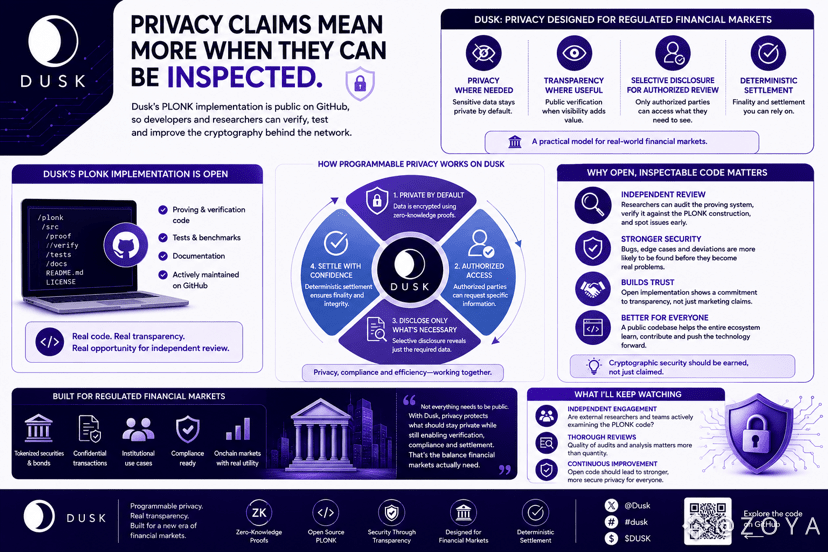
I went down a bit of a rabbit hole looking at Dusk’s PLONK code today, and it made me think about how we usually judge privacy projects. Seeing “zero-knowledge proofs” in a technical description is one thing. Being able to actually look at the implementation behind it is another.
Dusk’s PLONK implementation is publicly available on GitHub, so developers and researchers have something concrete to examine rather than only relying on a description in a whitepaper. That doesn’t automatically mean every part of the system is perfect, but I like that the cryptography isn’t being treated as a black box. 🤯
And this matters more when the goal is regulated finance. Dusk isn’t trying to make everything invisible. The bigger idea is privacy where sensitive information needs protection, while still leaving room for transparency and selective disclosure when an authorized party needs to verify something. That’s a much more practical model for financial markets than simply hiding everything.
I’m definitely not qualified to audit PLONK myself 😂, but I do like the principle here. If confidential financial activity is going onchain, I’d rather have the underlying privacy technology available for people to question and inspect than simply take a project’s word for it. That combination of privacy, verification and authorized disclosure is what makes Dusk interesting to me.
@Dusk_Foundation #dusk $DUSK
I went down a bit of a rabbit hole looking at Dusk’s PLONK code today, and it made me think about how we usually judge privacy projects. Seeing “zero-knowledge proofs” in a technical description is one thing. Being able to actually look at the implementation behind it is another.
Dusk’s PLONK implementation is publicly available on GitHub, so developers and researchers have something concrete to examine rather than only relying on a description in a whitepaper. That doesn’t automatically mean every part of the system is perfect, but I like that the cryptography isn’t being treated as a black box. 🤯
And this matters more when the goal is regulated finance. Dusk isn’t trying to make everything invisible. The bigger idea is privacy where sensitive information needs protection, while still leaving room for transparency and selective disclosure when an authorized party needs to verify something. That’s a much more practical model for financial markets than simply hiding everything.
I’m definitely not qualified to audit PLONK myself 😂, but I do like the principle here. If confidential financial activity is going onchain, I’d rather have the underlying privacy technology available for people to question and inspect than simply take a project’s word for it. That combination of privacy, verification and authorized disclosure is what makes Dusk interesting to me.
@Dusk #dusk $DUSK
17
32
3k
·
--
Verified
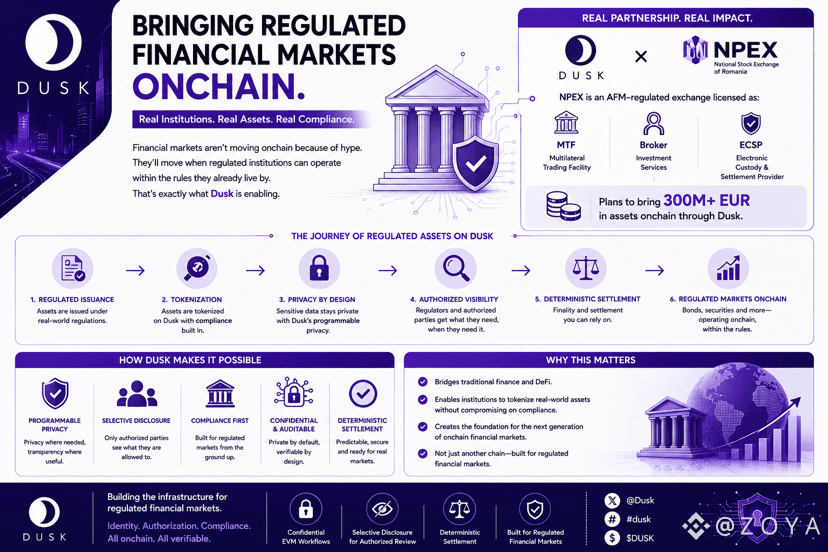
I used to think getting financial institutions onchain was mostly a technology problem… build the chain, make it secure, and eventually the institutions would come. Looking at Dusk made me realize there’s another part people don’t talk about enough: the institutions themselves have to be able to operate within the rules they already live by.
That’s why the NPEX connection caught my attention. NPEX is an AFM-regulated exchange, licensed as an MTF, Broker and ECSP, and it plans to bring 300M+ EUR in assets onchain through Dusk. I found that more interesting than another headline about “institutional adoption” because there’s an actual regulated market involved here. 🤯
Then I started thinking about what that means for the assets themselves. Bonds, securities and other financial products can’t just be dropped onto a public blockchain and expected to work like a meme coin. Ownership, compliance, privacy and settlement all have to fit together. That’s where Dusk’s approach starts to make more sense to me… the infrastructure is being designed around the requirements of regulated finance from the beginning.
I still want to see how much of this turns into actual market activity 😂, because partnerships and plans are one thing and real settlement is another. But if regulated venues can genuinely use Dusk to bring financial assets onchain, that feels like a much bigger test for blockchain than simply creating another token. That’s the part I’m watching.
@Dusk_Foundation #dusk $DUSK
I used to think getting financial institutions onchain was mostly a technology problem… build the chain, make it secure, and eventually the institutions would come. Looking at Dusk made me realize there’s another part people don’t talk about enough: the institutions themselves have to be able to operate within the rules they already live by.
That’s why the NPEX connection caught my attention. NPEX is an AFM-regulated exchange, licensed as an MTF, Broker and ECSP, and it plans to bring 300M+ EUR in assets onchain through Dusk. I found that more interesting than another headline about “institutional adoption” because there’s an actual regulated market involved here. 🤯
Then I started thinking about what that means for the assets themselves. Bonds, securities and other financial products can’t just be dropped onto a public blockchain and expected to work like a meme coin. Ownership, compliance, privacy and settlement all have to fit together. That’s where Dusk’s approach starts to make more sense to me… the infrastructure is being designed around the requirements of regulated finance from the beginning.
I still want to see how much of this turns into actual market activity 😂, because partnerships and plans are one thing and real settlement is another. But if regulated venues can genuinely use Dusk to bring financial assets onchain, that feels like a much bigger test for blockchain than simply creating another token. That’s the part I’m watching.
@Dusk #dusk $DUSK
14
16
1.7k
·
--
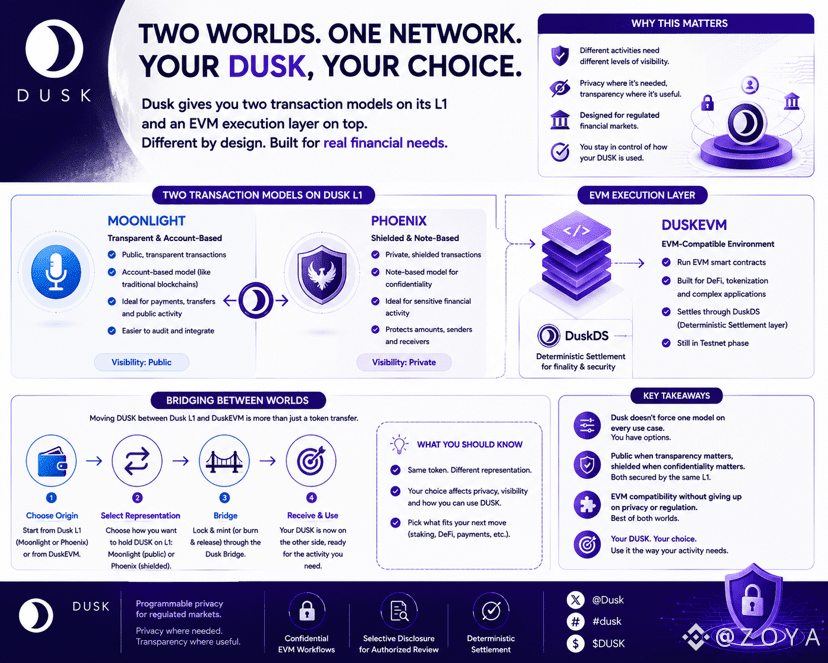
I was looking at Dusk’s transaction models today and something finally clicked for me… not every financial activity needs the same level of visibility. Moonlight keeps DUSK public and account-based, while Phoenix takes a shielded, note-based approach. Same network, same token, but a very different way of handling activity.
That distinction actually makes more sense when you think about what Dusk is trying to build. A payment that needs public visibility doesn’t necessarily need the same setup as a financial transaction where sensitive details should stay protected. Phoenix uses shielded transfers for that reason, while Moonlight keeps things transparent. 🤯
Then there’s DuskEVM, which adds an EVM-compatible environment on top of the network. What I like about this architecture is that privacy isn’t being treated as an all-or-nothing setting. Different applications can work with different levels of visibility instead of forcing every use case into the same model.
I’m still getting my head around all the ways these pieces will work together 😂, but the idea itself feels pretty practical. Public when transparency matters, shielded when confidentiality matters… and the network can support both without pretending financial activity always needs to look the same.
@Dusk_Foundation #dusk $DUSK
I was looking at Dusk’s transaction models today and something finally clicked for me… not every financial activity needs the same level of visibility. Moonlight keeps DUSK public and account-based, while Phoenix takes a shielded, note-based approach. Same network, same token, but a very different way of handling activity.
That distinction actually makes more sense when you think about what Dusk is trying to build. A payment that needs public visibility doesn’t necessarily need the same setup as a financial transaction where sensitive details should stay protected. Phoenix uses shielded transfers for that reason, while Moonlight keeps things transparent. 🤯
Then there’s DuskEVM, which adds an EVM-compatible environment on top of the network. What I like about this architecture is that privacy isn’t being treated as an all-or-nothing setting. Different applications can work with different levels of visibility instead of forcing every use case into the same model.
I’m still getting my head around all the ways these pieces will work together 😂, but the idea itself feels pretty practical. Public when transparency matters, shielded when confidentiality matters… and the network can support both without pretending financial activity always needs to look the same.
@Dusk #dusk $DUSK
12
10
590
·
--
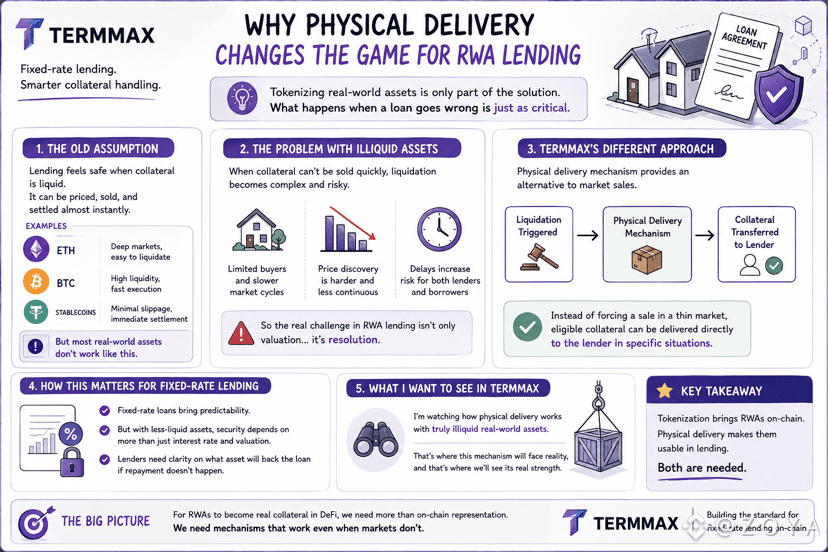
I spent some time looking at how TermMax handles collateral when the asset itself isnt easy to sell, and that changed how I think about RWA lending.
With highly liquid tokens, liquidation can usually rely on an active market to convert collateral into the required value. But that approach becomes much harder when the underlying asset has limited buyers or slower settlement.
TermMax’s physical delivery mechanism gives lenders another route…. instead of depending entirely on an immediate market sale, eligible collateral can be transferred to the lender when certain liquidation conditions occur.
So for me, the interesting part isnt simply using RWAs as collateral…. its designing the lending system around what happens when that collateral doesnt have deep liquidity in the first place.
@termmax #TermMax
I spent some time looking at how TermMax handles collateral when the asset itself isnt easy to sell, and that changed how I think about RWA lending.
With highly liquid tokens, liquidation can usually rely on an active market to convert collateral into the required value. But that approach becomes much harder when the underlying asset has limited buyers or slower settlement.
TermMax’s physical delivery mechanism gives lenders another route…. instead of depending entirely on an immediate market sale, eligible collateral can be transferred to the lender when certain liquidation conditions occur.
So for me, the interesting part isnt simply using RWAs as collateral…. its designing the lending system around what happens when that collateral doesnt have deep liquidity in the first place.
@TermMax #TermMax
7
6
248
·
--
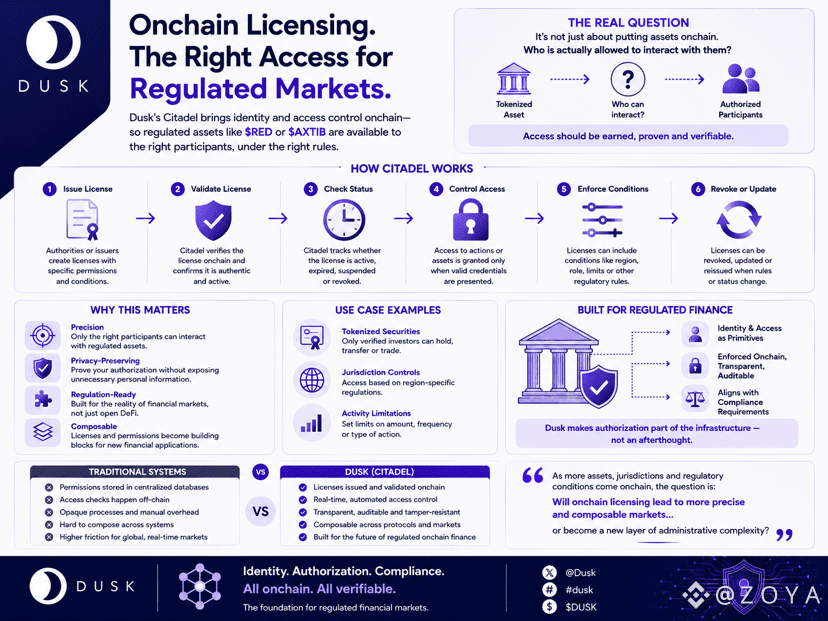
I’ve been thinking about something that feels pretty normal in traditional finance but gets overlooked onchain… permission. If a regulated asset is available onchain, that doesn’t automatically mean everyone should be able to interact with it. Looking into Dusk’s Citadel made me realize how much of finance actually depends on knowing who is allowed to do what.
Citadel is built around issuing and validating licenses, checking whether they’re still active, and controlling certain actions based on valid credentials. What I found interesting is that this turns authorization into something the blockchain can actually understand, instead of leaving it hidden in a database somewhere. A participant can prove they’re eligible without having to expose every detail about themselves. 🤯
Then I started thinking about how different that is from the usual crypto experience. Most of us are used to connecting a wallet and interacting with whatever contract we want, but regulated markets obviously can’t work that way. Tokenized securities need rules around who can hold them, trade them or access certain actions. Putting those permissions closer to the asset could make the whole system a lot more precise.
I still wonder how complicated these rules become once you have different assets, investors and jurisdictions involved 😂. But I like the direction Dusk is taking here. If regulated finance is going onchain, identity and authorization probably can’t stay as something happening quietly in the background. They need to be part of the infrastructure too.
@Dusk_Foundation #dusk $DUSK
I’ve been thinking about something that feels pretty normal in traditional finance but gets overlooked onchain… permission. If a regulated asset is available onchain, that doesn’t automatically mean everyone should be able to interact with it. Looking into Dusk’s Citadel made me realize how much of finance actually depends on knowing who is allowed to do what.
Citadel is built around issuing and validating licenses, checking whether they’re still active, and controlling certain actions based on valid credentials. What I found interesting is that this turns authorization into something the blockchain can actually understand, instead of leaving it hidden in a database somewhere. A participant can prove they’re eligible without having to expose every detail about themselves. 🤯
Then I started thinking about how different that is from the usual crypto experience. Most of us are used to connecting a wallet and interacting with whatever contract we want, but regulated markets obviously can’t work that way. Tokenized securities need rules around who can hold them, trade them or access certain actions. Putting those permissions closer to the asset could make the whole system a lot more precise.
I still wonder how complicated these rules become once you have different assets, investors and jurisdictions involved 😂. But I like the direction Dusk is taking here. If regulated finance is going onchain, identity and authorization probably can’t stay as something happening quietly in the background. They need to be part of the infrastructure too.
@Dusk #dusk $DUSK
15
13
277
·
--
What stands out about TermMax is the focus on making financing predictable while keeping the market customizable.
What stands out about TermMax is the focus on making financing predictable while keeping the market customizable.
70
·
--
TermMax gives you a better starting point for comparing opportunities when the important numbers are already defined upfront.
TermMax gives you a better starting point for comparing opportunities when the important numbers are already defined upfront.
60
·
--
I appreciate how TermMax combines familiar DeFi mechanics with a more structured approach to lending and borrowing.
I appreciate how TermMax combines familiar DeFi mechanics with a more structured approach to lending and borrowing.
40
·
--
TermMax is interesting because predictable rates can help separate a genuinely good opportunity from one that only looks good temporarily.
TermMax is interesting because predictable rates can help separate a genuinely good opportunity from one that only looks good temporarily.
30
·
--
The fixed-term model from TermMax could make planning longer strategies much easier when you already know the financing cost.
The fixed-term model from TermMax could make planning longer strategies much easier when you already know the financing cost.
47
·
--
I like how TermMax gives traders clearer numbers to work with instead of leaving everything dependent on floating rates.
I like how TermMax gives traders clearer numbers to work with instead of leaving everything dependent on floating rates.
32
·
--
TermMax makes fixed-rate borrowing feel more practical when you can actually calculate the cost before opening a position.
TermMax makes fixed-rate borrowing feel more practical when you can actually calculate the cost before opening a position.
47
·
--
The way Dusk combines programmable privacy with regulated finance gives the project a very clear direction.
The way Dusk combines programmable privacy with regulated finance gives the project a very clear direction.
130
·
--
I’m curious to see how Dusk’s confidential EVM capabilities translate into applications people actually use.
I’m curious to see how Dusk’s confidential EVM capabilities translate into applications people actually use.
42
·
--
Dusk could have a strong use case for tokenized assets where privacy requirements are more complex than people realize.
Dusk could have a strong use case for tokenized assets where privacy requirements are more complex than people realize.
42
·
--
Dusk is working on an important piece of infrastructure for institutions that need both confidentiality and accountability
Dusk is working on an important piece of infrastructure for institutions that need both confidentiality and accountability
1
2
71
·
--
The programmable privacy approach from Dusk feels especially useful for financial workflows with different access requirements.
The programmable privacy approach from Dusk feels especially useful for financial workflows with different access requirements.
21
·
--
I like how Dusk thinks about privacy around actual institutional requirements instead of treating it as a standalone feature.
I like how Dusk thinks about privacy around actual institutional requirements instead of treating it as a standalone feature.
44
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number