
#seguridadcrypto
seguridadcrypto
119,027 views
139 Discussing
Hot
Latest

·
--
🚨 $BTC BETRAYAL
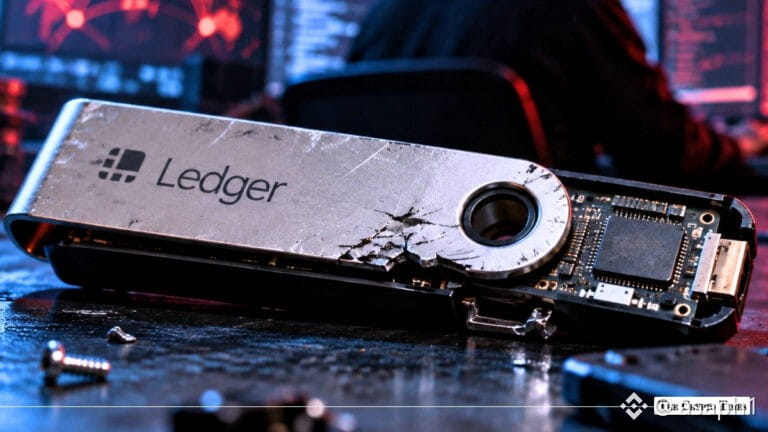
Ledger has just confirmed what nobody wanted to hear: tampered wallets are no longer a problem limited to Southeast Asia. Today, the company confirmed altered devices in Berlin and is investigating two more in Dubai. To me, this changes everything we thought we knew about self-custody: if the safe you bought in a store could come with a trap, what can we trust?
Take a look at the detail nobody is noticing:
→ Every confirmed device has the same physical modification, designed to steal your 24-word recovery phrase right when you first set up the wallet.
→ Investigators have already traced around $87 million drained from hundreds of wallets on Ethereum, Tron, and Bitcoin.
→ Ledger says there is no flaw in its chip or system, and that none of the cases originated from ledger.com, but it is asking anyone who bought a device in Berlin since January 2026 to contact support and move their funds to a new wallet.
Would you still keep your crypto in a hardware wallet bought in a store, or would you only buy directly from the official website? 👇
$BTC $ETH $SOL
#Ledger #SeguridadCrypto #SelfCustody
🚨 $BTC BETRAYAL
Ledger has just confirmed what nobody wanted to hear: tampered wallets are no longer a problem limited to Southeast Asia. Today, the company confirmed altered devices in Berlin and is investigating two more in Dubai. To me, this changes everything we thought we knew about self-custody: if the safe you bought in a store could come with a trap, what can we trust?
Take a look at the detail nobody is noticing:
→ Every confirmed device has the same physical modification, designed to steal your 24-word recovery phrase right when you first set up the wallet.
→ Investigators have already traced around $87 million drained from hundreds of wallets on Ethereum, Tron, and Bitcoin.
→ Ledger says there is no flaw in its chip or system, and that none of the cases originated from ledger.com, but it is asking anyone who bought a device in Berlin since January 2026 to contact support and move their funds to a new wallet.
Would you still keep your crypto in a hardware wallet bought in a store, or would you only buy directly from the official website? 👇
$BTC $ETH $SOL
#Ledger #SeguridadCrypto #SelfCustody
Ledger has just confirmed what nobody wanted to hear: tampered wallets are no longer a problem limited to Southeast Asia. Today, the company confirmed altered devices in Berlin and is investigating two more in Dubai. To me, this changes everything we thought we knew about self-custody: if the safe you bought in a store could come with a trap, what can we trust?
Take a look at the detail nobody is noticing:
→ Every confirmed device has the same physical modification, designed to steal your 24-word recovery phrase right when you first set up the wallet.
→ Investigators have already traced around $87 million drained from hundreds of wallets on Ethereum, Tron, and Bitcoin.
→ Ledger says there is no flaw in its chip or system, and that none of the cases originated from ledger.com, but it is asking anyone who bought a device in Berlin since January 2026 to contact support and move their funds to a new wallet.
Would you still keep your crypto in a hardware wallet bought in a store, or would you only buy directly from the official website? 👇
$BTC $ETH $SOL
#Ledger #SeguridadCrypto #SelfCustody
NORTEPAY:
ya no se sabe en qué confiar si hasta a las grandes empresas le roban
2
9
12.7k
·
--
🚨 $SOL SCAM AT THE AUTHORIZED STORE
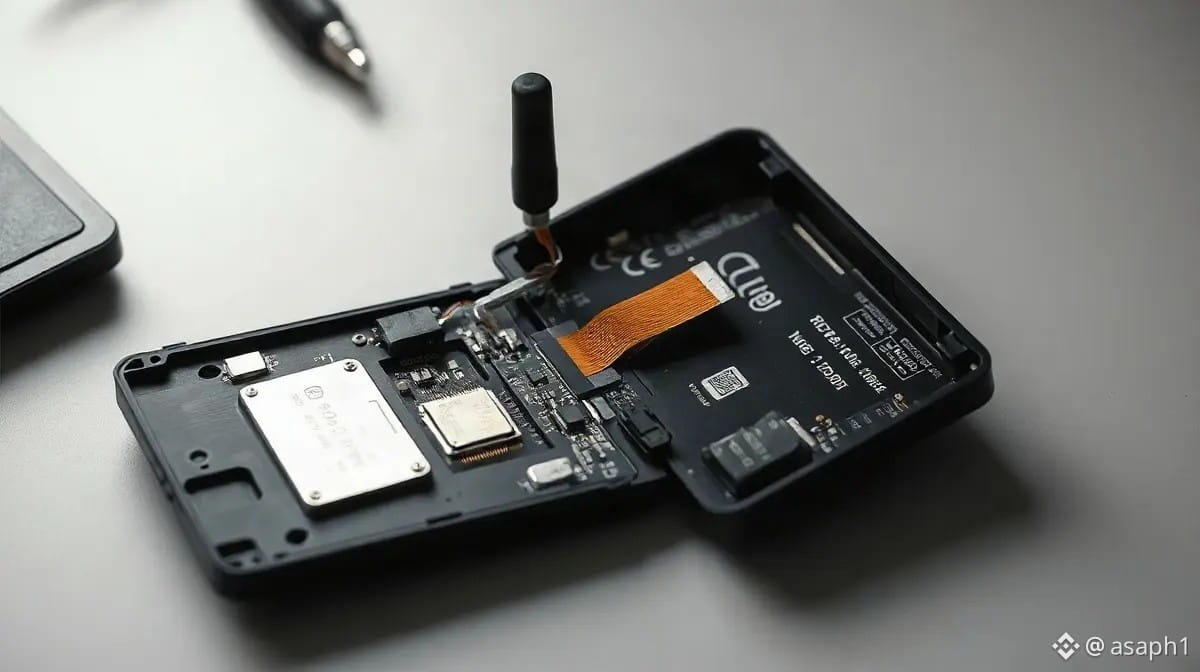
Two users in Dubai lost ~$604,000 in crypto from Ledger wallets bought new at Virgin Megastore, a Ledger-authorized store. To me, this breaks the golden rule we all kept repeating: buying from an official store no longer protects you from anything.
Look at the detail nobody is noticing:
→ The Ledger Flex lost ~1,300 SOL (~$97,000), and when it was opened, an extra board with a V1.3 antenna was found—the first implant of that version recorded by Mark Karpelès.
→ In the second case, a Ledger Stax lost 507,000 USDT on November 14, a month after it was bought new on October 11.
→ The tally now stands at 20 devices from 10 sellers in 10 countries, and Ledger’s Genuine Check does NOT detect these implants because the security chip remains intact.
Would you still store your crypto in a hardware wallet bought in a store? 👇
$SOL $USDT
#Ledger #Dubai #CryptoSecurity
🚨 $SOL SCAM AT THE AUTHORIZED STORE
Two users in Dubai lost ~$604,000 in crypto from Ledger wallets bought new at Virgin Megastore, a Ledger-authorized store. To me, this breaks the golden rule we all kept repeating: buying from an official store no longer protects you from anything.
Look at the detail nobody is noticing:
→ The Ledger Flex lost ~1,300 SOL (~$97,000), and when it was opened, an extra board with a V1.3 antenna was found—the first implant of that version recorded by Mark Karpelès.
→ In the second case, a Ledger Stax lost 507,000 USDT on November 14, a month after it was bought new on October 11.
→ The tally now stands at 20 devices from 10 sellers in 10 countries, and Ledger’s Genuine Check does NOT detect these implants because the security chip remains intact.
Would you still store your crypto in a hardware wallet bought in a store? 👇
$SOL $USDT
#Ledger #Dubai #CryptoSecurity
Two users in Dubai lost ~$604,000 in crypto from Ledger wallets bought new at Virgin Megastore, a Ledger-authorized store. To me, this breaks the golden rule we all kept repeating: buying from an official store no longer protects you from anything.
Look at the detail nobody is noticing:
→ The Ledger Flex lost ~1,300 SOL (~$97,000), and when it was opened, an extra board with a V1.3 antenna was found—the first implant of that version recorded by Mark Karpelès.
→ In the second case, a Ledger Stax lost 507,000 USDT on November 14, a month after it was bought new on October 11.
→ The tally now stands at 20 devices from 10 sellers in 10 countries, and Ledger’s Genuine Check does NOT detect these implants because the security chip remains intact.
Would you still store your crypto in a hardware wallet bought in a store? 👇
$SOL $USDT
#Ledger #Dubai #CryptoSecurity
AjedrezBlitz:
Terrible, ya no sé que pensar de Ledger y sus «carteras frías »
5
1
9
13.2k
·
--
🚨 $ETH BETRAYAL IN ETHERSCAN SUPPORT
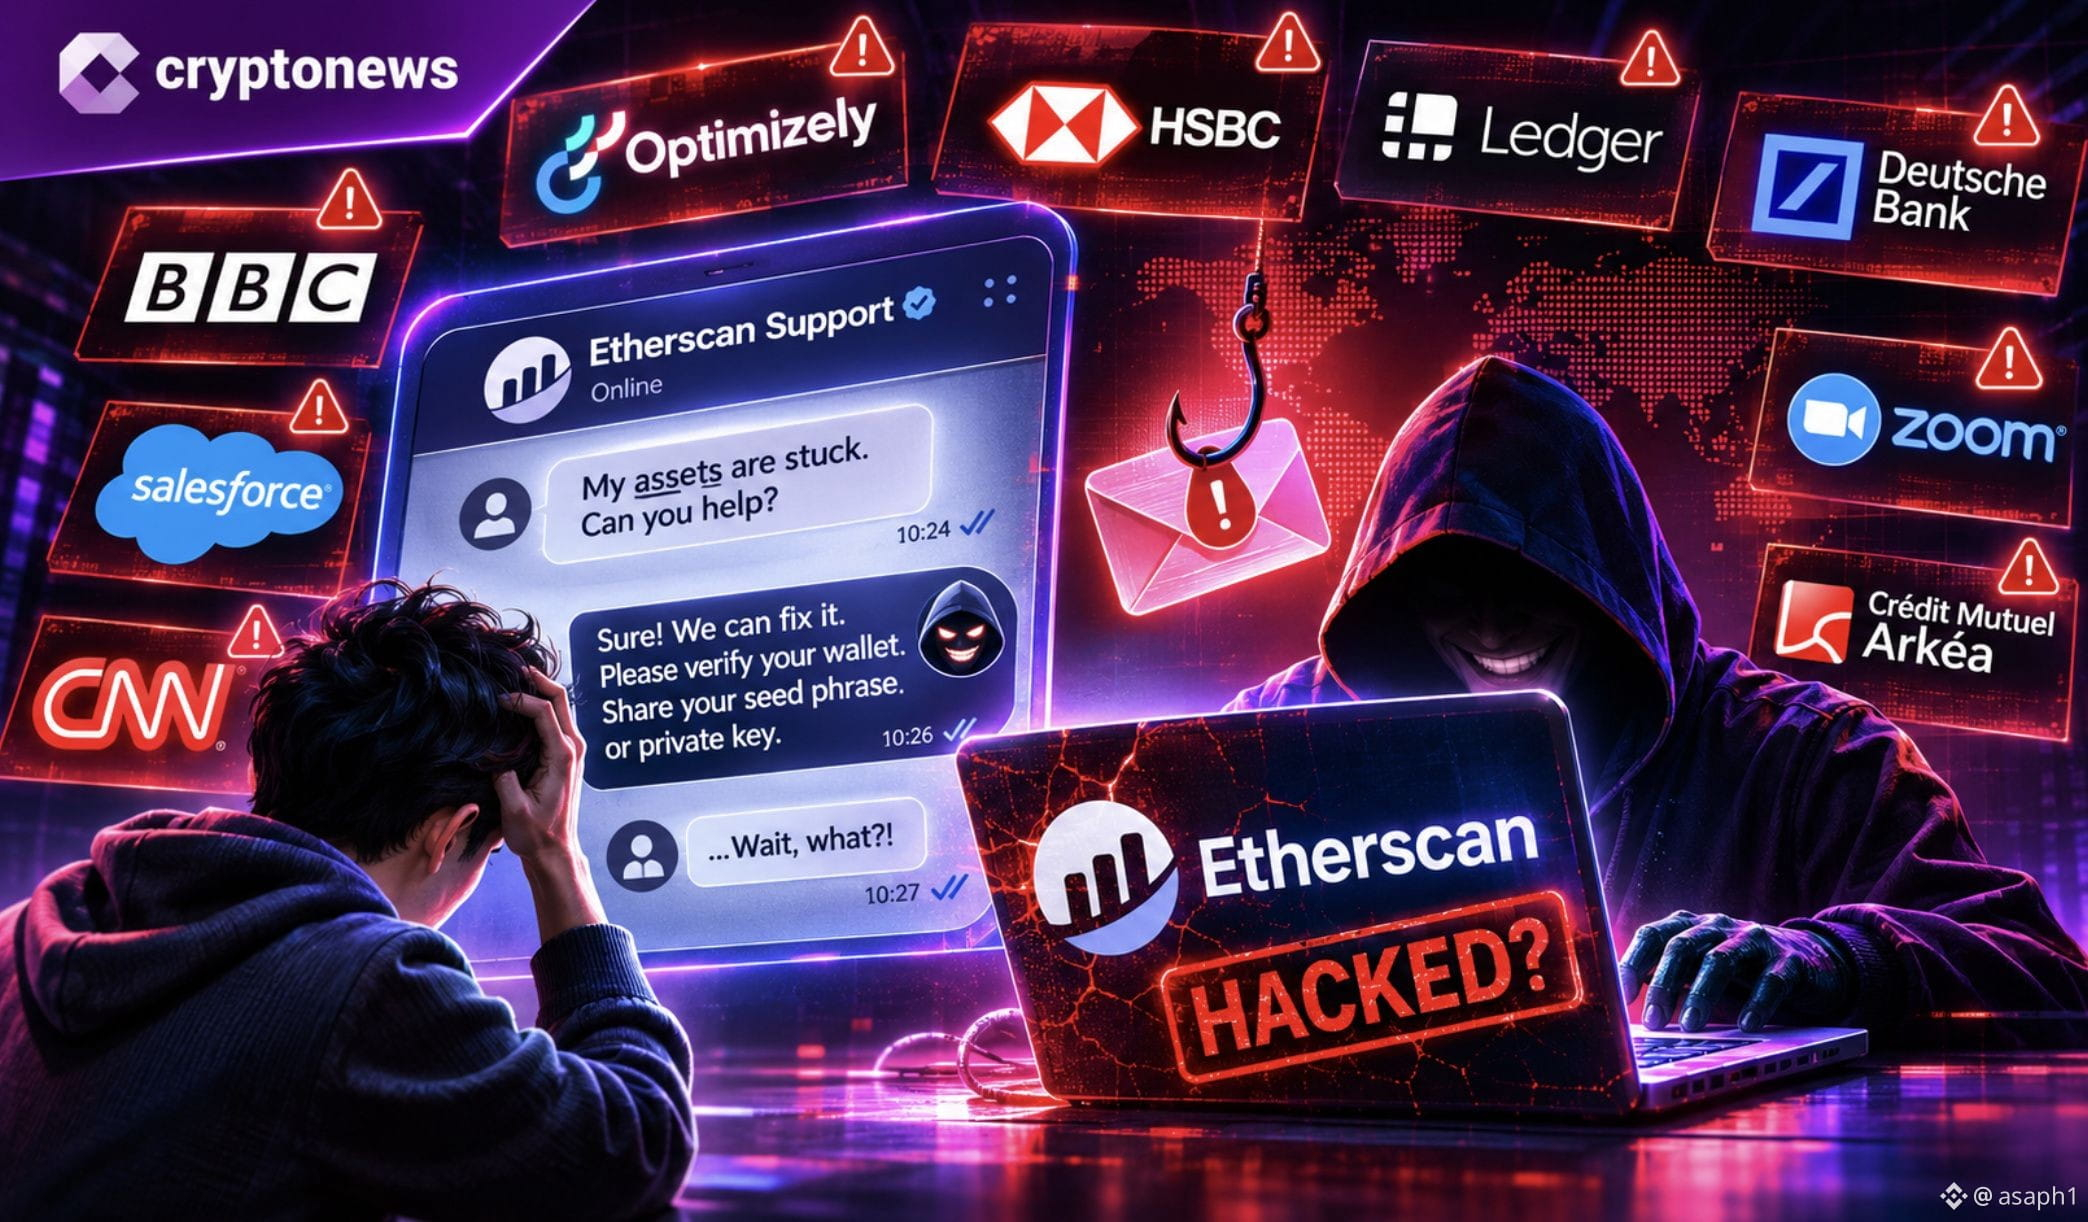
Etherscan, the explorer almost all of us use to verify every Ethereum transaction, announced today that it detected attempts to gain unauthorized access to its support and ticketing system (Freshworks). To me, this is the most dangerous thing this week: they don’t steal from the network—they steal your trust in the people who are supposed to “help” you.
Look at the detail nobody seems to be noticing:
→ Etherscan says there’s no evidence so far of a successful breach or stolen data, but the investigation is ongoing and preventive measures have already been taken.
→ The announcement came today at 09:20 UTC through its official account: support will NEVER ask for your private key, seed phrase, or password.
→ This isn’t an isolated case: 2 days ago, an Optimizely vulnerability injected malicious code into 178 websites (HSBC, BBC, Ledger, CNN, Salesforce, Zoom), and this week Lighter Perps lost $10.39M and a French bank lost around €100M.
Do you think twice before replying to “support” that messages you first? 👇
$ETH $BTC
#Etherscan #SeguridadCrypto #Phishing
🚨 $ETH BETRAYAL IN ETHERSCAN SUPPORT
Etherscan, the explorer almost all of us use to verify every Ethereum transaction, announced today that it detected attempts to gain unauthorized access to its support and ticketing system (Freshworks). To me, this is the most dangerous thing this week: they don’t steal from the network—they steal your trust in the people who are supposed to “help” you.
Look at the detail nobody seems to be noticing:
→ Etherscan says there’s no evidence so far of a successful breach or stolen data, but the investigation is ongoing and preventive measures have already been taken.
→ The announcement came today at 09:20 UTC through its official account: support will NEVER ask for your private key, seed phrase, or password.
→ This isn’t an isolated case: 2 days ago, an Optimizely vulnerability injected malicious code into 178 websites (HSBC, BBC, Ledger, CNN, Salesforce, Zoom), and this week Lighter Perps lost $10.39M and a French bank lost around €100M.
Do you think twice before replying to “support” that messages you first? 👇
$ETH $BTC
#Etherscan #SeguridadCrypto #Phishing
Etherscan, the explorer almost all of us use to verify every Ethereum transaction, announced today that it detected attempts to gain unauthorized access to its support and ticketing system (Freshworks). To me, this is the most dangerous thing this week: they don’t steal from the network—they steal your trust in the people who are supposed to “help” you.
Look at the detail nobody seems to be noticing:
→ Etherscan says there’s no evidence so far of a successful breach or stolen data, but the investigation is ongoing and preventive measures have already been taken.
→ The announcement came today at 09:20 UTC through its official account: support will NEVER ask for your private key, seed phrase, or password.
→ This isn’t an isolated case: 2 days ago, an Optimizely vulnerability injected malicious code into 178 websites (HSBC, BBC, Ledger, CNN, Salesforce, Zoom), and this week Lighter Perps lost $10.39M and a French bank lost around €100M.
Do you think twice before replying to “support” that messages you first? 👇
$ETH $BTC
#Etherscan #SeguridadCrypto #Phishing
152
·
--
🚨 $BTC BETRAYAL IN THE SAFEST WALLET
Trezor confirmed that Skladon, its shipping partner, was hacked, and data from around 27,000 orders was leaked: names, phone numbers, emails, and delivery addresses of people who bought a cold wallet. To me, this is the worst thing to happen today: the device you bought to protect your coins ended up exposing your home.
Look at the detail nobody is noticing:
→ The attack happened on November 7, and Skladon notified people 8 days later, on the 15th; the data covers orders from August 9 to November 7.
→ Affected customers are already receiving scam calls: with your name, your phone number, and proof that you own a Trezor, the scammer sounds convincing.
→ This is the third leak through a partner this year: ShipMonk exposed nearly 14,000 customers in August; Trezor is now cutting data retention from 90 to 45 days.
Would you still trust a cold wallet with your address after this? 👇
$BTC
#Trezor #SeguridadCrypto #Phishing
🚨 $BTC BETRAYAL IN THE SAFEST WALLET
Trezor confirmed that Skladon, its shipping partner, was hacked, and data from around 27,000 orders was leaked: names, phone numbers, emails, and delivery addresses of people who bought a cold wallet. To me, this is the worst thing to happen today: the device you bought to protect your coins ended up exposing your home.
Look at the detail nobody is noticing:
→ The attack happened on November 7, and Skladon notified people 8 days later, on the 15th; the data covers orders from August 9 to November 7.
→ Affected customers are already receiving scam calls: with your name, your phone number, and proof that you own a Trezor, the scammer sounds convincing.
→ This is the third leak through a partner this year: ShipMonk exposed nearly 14,000 customers in August; Trezor is now cutting data retention from 90 to 45 days.
Would you still trust a cold wallet with your address after this? 👇
$BTC
#Trezor #SeguridadCrypto #Phishing
Trezor confirmed that Skladon, its shipping partner, was hacked, and data from around 27,000 orders was leaked: names, phone numbers, emails, and delivery addresses of people who bought a cold wallet. To me, this is the worst thing to happen today: the device you bought to protect your coins ended up exposing your home.
Look at the detail nobody is noticing:
→ The attack happened on November 7, and Skladon notified people 8 days later, on the 15th; the data covers orders from August 9 to November 7.
→ Affected customers are already receiving scam calls: with your name, your phone number, and proof that you own a Trezor, the scammer sounds convincing.
→ This is the third leak through a partner this year: ShipMonk exposed nearly 14,000 customers in August; Trezor is now cutting data retention from 90 to 45 days.
Would you still trust a cold wallet with your address after this? 👇
$BTC
#Trezor #SeguridadCrypto #Phishing
2
3.9k
·
--
⚠️ ANOTHER TREZOR DATA BREACH: 27,000 CUSTOMERS EXPOSED
Did you see this? Trezor confirmed that an attacker accessed data from around 27,000 purchases through its shipping company, Skladon. Names, phone numbers, delivery addresses, and email addresses for orders placed between August 9 and November 7 were leaked.
This is the third data breach involving a Trezor partner so far this year. The company clarified that its own systems were not affected and that the wallets remain secure: no keys or recovery phrases were leaked. The problem is what comes next: scammers are already calling some customers.
I think the danger isn’t the wallet itself, but what comes afterward: with your name and address, they know you have crypto at home.
If you suddenly get a strange message claiming to be from Trezor, what do you do: ignore it or report it?
#CryptoSecurity
⚠️ ANOTHER TREZOR DATA BREACH: 27,000 CUSTOMERS EXPOSED
Did you see this? Trezor confirmed that an attacker accessed data from around 27,000 purchases through its shipping company, Skladon. Names, phone numbers, delivery addresses, and email addresses for orders placed between August 9 and November 7 were leaked.
This is the third data breach involving a Trezor partner so far this year. The company clarified that its own systems were not affected and that the wallets remain secure: no keys or recovery phrases were leaked. The problem is what comes next: scammers are already calling some customers.
I think the danger isn’t the wallet itself, but what comes afterward: with your name and address, they know you have crypto at home.
If you suddenly get a strange message claiming to be from Trezor, what do you do: ignore it or report it?
#CryptoSecurity
Did you see this? Trezor confirmed that an attacker accessed data from around 27,000 purchases through its shipping company, Skladon. Names, phone numbers, delivery addresses, and email addresses for orders placed between August 9 and November 7 were leaked.
This is the third data breach involving a Trezor partner so far this year. The company clarified that its own systems were not affected and that the wallets remain secure: no keys or recovery phrases were leaked. The problem is what comes next: scammers are already calling some customers.
I think the danger isn’t the wallet itself, but what comes afterward: with your name and address, they know you have crypto at home.
If you suddenly get a strange message claiming to be from Trezor, what do you do: ignore it or report it?
#CryptoSecurity
27
·
--
⚠️ AN EXCHANGE’S CUSTOMER SUPPORT WAS HACKED AND ITS CUSTOMERS’ DATA WAS LEAKED
Look what happened to Coinone, a South Korean exchange: the exchange itself wasn’t hacked; MetaM was, the company that handles customer support for them. And it had everything people had told customer support over chat or by phone: names, phone numbers, emails, dates of birth, bank accounts, passwords, ID numbers, home addresses, and even wallet addresses.
Coinone says only people who have contacted customer support at some point are at risk, though it doesn’t know how many there are, and that their accounts, trading, and wallets were not affected. But it warned that scammers can now use those details to impersonate the exchange, and urged affected users to change their passwords right away.
I think the danger isn’t just the exchange: it’s everything we tell customer support without thinking, believing it’ll be kept safe forever.
Have you ever given your password to customer support over chat or by phone?
#CryptoSecurity
⚠️ AN EXCHANGE’S CUSTOMER SUPPORT WAS HACKED AND ITS CUSTOMERS’ DATA WAS LEAKED
Look what happened to Coinone, a South Korean exchange: the exchange itself wasn’t hacked; MetaM was, the company that handles customer support for them. And it had everything people had told customer support over chat or by phone: names, phone numbers, emails, dates of birth, bank accounts, passwords, ID numbers, home addresses, and even wallet addresses.
Coinone says only people who have contacted customer support at some point are at risk, though it doesn’t know how many there are, and that their accounts, trading, and wallets were not affected. But it warned that scammers can now use those details to impersonate the exchange, and urged affected users to change their passwords right away.
I think the danger isn’t just the exchange: it’s everything we tell customer support without thinking, believing it’ll be kept safe forever.
Have you ever given your password to customer support over chat or by phone?
#CryptoSecurity
Look what happened to Coinone, a South Korean exchange: the exchange itself wasn’t hacked; MetaM was, the company that handles customer support for them. And it had everything people had told customer support over chat or by phone: names, phone numbers, emails, dates of birth, bank accounts, passwords, ID numbers, home addresses, and even wallet addresses.
Coinone says only people who have contacted customer support at some point are at risk, though it doesn’t know how many there are, and that their accounts, trading, and wallets were not affected. But it warned that scammers can now use those details to impersonate the exchange, and urged affected users to change their passwords right away.
I think the danger isn’t just the exchange: it’s everything we tell customer support without thinking, believing it’ll be kept safe forever.
Have you ever given your password to customer support over chat or by phone?
#CryptoSecurity
63
·
--
THEY SAID NOTHING WAS LOST… AND TODAY THEY ADMITTED $200,000 WAS STOLEN 🔓😤
Look what happened with Unocoin, an exchange in India: on November 6, they detected unusual activity and said nothing had been lost. Today, they admitted that about $200,000 was stolen from three hot wallets—the ones connected to the internet to move funds for day-to-day operations.
The most incredible part is how the attackers got in: using backup keys generated 8 years ago, printed on paper, and stored physically. The exchange says it will cover the loss with its own funds and that more than 90% of customers’ money is kept in cold storage.
I think that in crypto, trust is earned through transparency, and that’s exactly where they fell short.
Do you trust your exchange to tell you if it gets robbed?
#CryptoSecurity
THEY SAID NOTHING WAS LOST… AND TODAY THEY ADMITTED $200,000 WAS STOLEN 🔓😤
Look what happened with Unocoin, an exchange in India: on November 6, they detected unusual activity and said nothing had been lost. Today, they admitted that about $200,000 was stolen from three hot wallets—the ones connected to the internet to move funds for day-to-day operations.
The most incredible part is how the attackers got in: using backup keys generated 8 years ago, printed on paper, and stored physically. The exchange says it will cover the loss with its own funds and that more than 90% of customers’ money is kept in cold storage.
I think that in crypto, trust is earned through transparency, and that’s exactly where they fell short.
Do you trust your exchange to tell you if it gets robbed?
#CryptoSecurity
Look what happened with Unocoin, an exchange in India: on November 6, they detected unusual activity and said nothing had been lost. Today, they admitted that about $200,000 was stolen from three hot wallets—the ones connected to the internet to move funds for day-to-day operations.
The most incredible part is how the attackers got in: using backup keys generated 8 years ago, printed on paper, and stored physically. The exchange says it will cover the loss with its own funds and that more than 90% of customers’ money is kept in cold storage.
I think that in crypto, trust is earned through transparency, and that’s exactly where they fell short.
Do you trust your exchange to tell you if it gets robbed?
#CryptoSecurity
82
·
--
POLICE CAN NOW FREEZE STOLEN CRYPTO IN MINUTES 🚔🔒
Have you seen this? TRM Labs launched Beacon Concierge, a service that lets police in any country freeze stolen cryptocurrency in minutes by working directly with exchanges and stablecoin issuers.
Until now, when you got robbed, it took hours or days for the report to reach wherever the money was... and by then, it had already moved from wallet to wallet. This network now covers 80% of trading volume, and in 15 cases involving 14 agencies across 10 countries, more than $35 million in suspicious funds were frozen.
I think this changes the game for thieves: stealing crypto and disappearing won’t be as easy as it used to be.
Do you think this will put a stop to hacks, or will thieves always find a way around it?
#CryptoSecurity
POLICE CAN NOW FREEZE STOLEN CRYPTO IN MINUTES 🚔🔒
Have you seen this? TRM Labs launched Beacon Concierge, a service that lets police in any country freeze stolen cryptocurrency in minutes by working directly with exchanges and stablecoin issuers.
Until now, when you got robbed, it took hours or days for the report to reach wherever the money was... and by then, it had already moved from wallet to wallet. This network now covers 80% of trading volume, and in 15 cases involving 14 agencies across 10 countries, more than $35 million in suspicious funds were frozen.
I think this changes the game for thieves: stealing crypto and disappearing won’t be as easy as it used to be.
Do you think this will put a stop to hacks, or will thieves always find a way around it?
#CryptoSecurity
Have you seen this? TRM Labs launched Beacon Concierge, a service that lets police in any country freeze stolen cryptocurrency in minutes by working directly with exchanges and stablecoin issuers.
Until now, when you got robbed, it took hours or days for the report to reach wherever the money was... and by then, it had already moved from wallet to wallet. This network now covers 80% of trading volume, and in 15 cases involving 14 agencies across 10 countries, more than $35 million in suspicious funds were frozen.
I think this changes the game for thieves: stealing crypto and disappearing won’t be as easy as it used to be.
Do you think this will put a stop to hacks, or will thieves always find a way around it?
#CryptoSecurity
65
·
--
⚠️🚨 ATTACK ON LNBITS: USERS TOLD TO SHUT DOWN SERVERS
I just saw that LNbits, the free software many people use to set up their own wallet server on the $BTC Lightning Network, Bitcoin’s fast payment layer, is under attack, and its creators have asked users to shut down their servers immediately. One operator has already lost more than 2.2 million satoshis, Bitcoin’s smallest unit, due to a bug in an extension, and a patch is expected today.
Opinion: this shows how fragile even the most widely used free software can be when you don’t check in time which extensions are installed.
Would you check which extensions are installed in your wallets, or do you trust that this will never happen to you? #CryptoSecurity
⚠️🚨 ATTACK ON LNBITS: USERS TOLD TO SHUT DOWN SERVERS
I just saw that LNbits, the free software many people use to set up their own wallet server on the $BTC Lightning Network, Bitcoin’s fast payment layer, is under attack, and its creators have asked users to shut down their servers immediately. One operator has already lost more than 2.2 million satoshis, Bitcoin’s smallest unit, due to a bug in an extension, and a patch is expected today.
Opinion: this shows how fragile even the most widely used free software can be when you don’t check in time which extensions are installed.
Would you check which extensions are installed in your wallets, or do you trust that this will never happen to you? #CryptoSecurity
I just saw that LNbits, the free software many people use to set up their own wallet server on the $BTC Lightning Network, Bitcoin’s fast payment layer, is under attack, and its creators have asked users to shut down their servers immediately. One operator has already lost more than 2.2 million satoshis, Bitcoin’s smallest unit, due to a bug in an extension, and a patch is expected today.
Opinion: this shows how fragile even the most widely used free software can be when you don’t check in time which extensions are installed.
Would you check which extensions are installed in your wallets, or do you trust that this will never happen to you? #CryptoSecurity
28
·
--
🔒 CERTIK CALLS FOR LIMITS ON HOT WALLETS AFTER BINANCE HACK
Cybersecurity firm CertiK asked exchanges to set a dollar cap on the funds they hold in hot wallets, following the record $6.3 billion theft at Binance.
A hot wallet is connected to the internet and used for day-to-day withdrawals; a cold wallet is offline and much harder to rob.
Opinion: keeping almost everything in cold storage is no longer enough of a guarantee; what matters is how much remains exposed online.
Do you check whether your exchange keeps most of its funds offline? 🔐
#CryptoSecurity
🔒 CERTIK CALLS FOR LIMITS ON HOT WALLETS AFTER BINANCE HACK
Cybersecurity firm CertiK asked exchanges to set a dollar cap on the funds they hold in hot wallets, following the record $6.3 billion theft at Binance.
A hot wallet is connected to the internet and used for day-to-day withdrawals; a cold wallet is offline and much harder to rob.
Opinion: keeping almost everything in cold storage is no longer enough of a guarantee; what matters is how much remains exposed online.
Do you check whether your exchange keeps most of its funds offline? 🔐
#CryptoSecurity
Cybersecurity firm CertiK asked exchanges to set a dollar cap on the funds they hold in hot wallets, following the record $6.3 billion theft at Binance.
A hot wallet is connected to the internet and used for day-to-day withdrawals; a cold wallet is offline and much harder to rob.
Opinion: keeping almost everything in cold storage is no longer enough of a guarantee; what matters is how much remains exposed online.
Do you check whether your exchange keeps most of its funds offline? 🔐
#CryptoSecurity
1
788

$SOL Solana hardens its defenses after the $270M exploit at Drift.
Solana developers introduced the formal proposal SIMD-0723 to retire durable nonces, a feature that allowed signed transactions to remain valid for weeks, bypassing the usual 30-second expiration.
Why are they deciding to remove it?
- Security breach: This indefinite time window allowed attackers to drain more than $270 million from Drift in April after holding on to prior approvals.
- Network stability: In 2022, it caused a conflict that halted the network for 4.5 hours, and today just 555 accounts account for 97.5% of this volume in spam and bots.
📌 Exchanges and institutional entities rely on this leeway to sign transfers from devices isolated from the internet (air-gapped). To avoid operational friction, the removal will not take effect before May 5, 2027, giving time to audit alternatives such as Anza's Programmatic Signer or Blueshift's Vector.
Do you think removing non-expiring signatures is the definitive step to secure DeFi, or will it create unnecessary friction for large custodians?
#solana #SeguridadCrypto
{future}(SOLUSDT)
$SOL Solana hardens its defenses after the $270M exploit at Drift.
Solana developers introduced the formal proposal SIMD-0723 to retire durable nonces, a feature that allowed signed transactions to remain valid for weeks, bypassing the usual 30-second expiration.
Why are they deciding to remove it?
- Security breach: This indefinite time window allowed attackers to drain more than $270 million from Drift in April after holding on to prior approvals.
- Network stability: In 2022, it caused a conflict that halted the network for 4.5 hours, and today just 555 accounts account for 97.5% of this volume in spam and bots.
📌 Exchanges and institutional entities rely on this leeway to sign transfers from devices isolated from the internet (air-gapped). To avoid operational friction, the removal will not take effect before May 5, 2027, giving time to audit alternatives such as Anza's Programmatic Signer or Blueshift's Vector.
Do you think removing non-expiring signatures is the definitive step to secure DeFi, or will it create unnecessary friction for large custodians?
#solana #SeguridadCrypto
Solana developers introduced the formal proposal SIMD-0723 to retire durable nonces, a feature that allowed signed transactions to remain valid for weeks, bypassing the usual 30-second expiration.
Why are they deciding to remove it?
- Security breach: This indefinite time window allowed attackers to drain more than $270 million from Drift in April after holding on to prior approvals.
- Network stability: In 2022, it caused a conflict that halted the network for 4.5 hours, and today just 555 accounts account for 97.5% of this volume in spam and bots.
📌 Exchanges and institutional entities rely on this leeway to sign transfers from devices isolated from the internet (air-gapped). To avoid operational friction, the removal will not take effect before May 5, 2027, giving time to audit alternatives such as Anza's Programmatic Signer or Blueshift's Vector.
Do you think removing non-expiring signatures is the definitive step to secure DeFi, or will it create unnecessary friction for large custodians?
#solana #SeguridadCrypto
2
14
9.9k
🔒Security is key on your path to success.
Protect your capital and assets $BTC , $USDC $BNB ,
Enable two-factor authentication, set up an anti-phishing code, and review the devices with access to your account.
A good trade can lose its meaning if security is left until later.
Be wary of urgent messages, shortened links, and promises of guaranteed profits.
#SeguridadCrypto #BinanceSquareTalks #CryptoTips
{future}(BTCUSDT)
{spot}(USDCUSDT)
{spot}(BNBUSDT)
🔒Security is key on your path to success.
Protect your capital and assets $BTC , $USDC $BNB ,
Enable two-factor authentication, set up an anti-phishing code, and review the devices with access to your account.
A good trade can lose its meaning if security is left until later.
Be wary of urgent messages, shortened links, and promises of guaranteed profits.
#SeguridadCrypto #BinanceSquareTalks #CryptoTips
Protect your capital and assets $BTC , $USDC $BNB ,
Enable two-factor authentication, set up an anti-phishing code, and review the devices with access to your account.
A good trade can lose its meaning if security is left until later.
Be wary of urgent messages, shortened links, and promises of guaranteed profits.
#SeguridadCrypto #BinanceSquareTalks #CryptoTips
105

🚨 **BINANCE ANNOUNCES NEW MEASURES FOLLOWING SECURITY INCIDENT**
On October 30, 2026, Binance reported on the actions it is taking to respond to the security incident and restore its users’ trust.
**Key announcements:**
1️⃣ **Replenishment of funds:** Binance is buying the remaining 20% of the lost tokens to complete the replenishment of the affected assets.
2️⃣ **Proof of Reserves:** An initial snapshot of reserves will be taken within the next 12 hours, with results expected on Monday, November 2. This will make it possible to verify the platform’s reserves and ensure they back users’ balances.
3️⃣ **Recovery of stolen funds:** Binance is working with authorities, blockchain intelligence firms, token issuers, and other exchanges to track and recover the stolen funds.
4️⃣ **Technical report:** Binance will publish a detailed report explaining what happened, the causes of the incident, and the new security measures it will implement.
**MESSAGE FROM BINANCE’S CO-CEOS**
Yi and Richard say Binance takes responsibility for managing this incident, strengthening its security infrastructure, and protecting its users.
📌 **IMPORTANT POINT:** The platform promises greater transparency through verifiable Proof of Reserves and the publication of a technical report.
Source: Binance announcement – 30/10/2026.
#Binance #Bitcoin #Crypto #ProofOfReserves #Cryptocurrencies #SeguridadCrypto
🚨 **BINANCE ANNOUNCES NEW MEASURES FOLLOWING SECURITY INCIDENT**
On October 30, 2026, Binance reported on the actions it is taking to respond to the security incident and restore its users’ trust.
**Key announcements:**
1️⃣ **Replenishment of funds:** Binance is buying the remaining 20% of the lost tokens to complete the replenishment of the affected assets.
2️⃣ **Proof of Reserves:** An initial snapshot of reserves will be taken within the next 12 hours, with results expected on Monday, November 2. This will make it possible to verify the platform’s reserves and ensure they back users’ balances.
3️⃣ **Recovery of stolen funds:** Binance is working with authorities, blockchain intelligence firms, token issuers, and other exchanges to track and recover the stolen funds.
4️⃣ **Technical report:** Binance will publish a detailed report explaining what happened, the causes of the incident, and the new security measures it will implement.
**MESSAGE FROM BINANCE’S CO-CEOS**
Yi and Richard say Binance takes responsibility for managing this incident, strengthening its security infrastructure, and protecting its users.
📌 **IMPORTANT POINT:** The platform promises greater transparency through verifiable Proof of Reserves and the publication of a technical report.
Source: Binance announcement – 30/10/2026.
#Binance #Bitcoin #Crypto #ProofOfReserves #Cryptocurrencies #SeguridadCrypto
On October 30, 2026, Binance reported on the actions it is taking to respond to the security incident and restore its users’ trust.
**Key announcements:**
1️⃣ **Replenishment of funds:** Binance is buying the remaining 20% of the lost tokens to complete the replenishment of the affected assets.
2️⃣ **Proof of Reserves:** An initial snapshot of reserves will be taken within the next 12 hours, with results expected on Monday, November 2. This will make it possible to verify the platform’s reserves and ensure they back users’ balances.
3️⃣ **Recovery of stolen funds:** Binance is working with authorities, blockchain intelligence firms, token issuers, and other exchanges to track and recover the stolen funds.
4️⃣ **Technical report:** Binance will publish a detailed report explaining what happened, the causes of the incident, and the new security measures it will implement.
**MESSAGE FROM BINANCE’S CO-CEOS**
Yi and Richard say Binance takes responsibility for managing this incident, strengthening its security infrastructure, and protecting its users.
📌 **IMPORTANT POINT:** The platform promises greater transparency through verifiable Proof of Reserves and the publication of a technical report.
Source: Binance announcement – 30/10/2026.
#Binance #Bitcoin #Crypto #ProofOfReserves #Cryptocurrencies #SeguridadCrypto
2
237
·
--
Article
🚨 WHAT HAPPENED WITH BINANCE? Everything you need to know about the historic hack 🚨🚨 WHAT HAPPENED WITH BINANCE? Everything you need to know about the historic hack 🚨
The crypto market was shaken after a security incident at Binance involving approximately $6.3 billion in assets was confirmed. If you have funds on the platform or use it, here’s what you need to know, clearly and directly:
1️⃣ What happened?
Unauthorized access—apparently through a compromised platform developer’s device—enabled the mass movement of funds across 10 blockchains in a matter of minutes.
🚨 WHAT HAPPENED WITH BINANCE? Everything you need to know about the historic hack 🚨
🚨 WHAT HAPPENED WITH BINANCE? Everything you need to know about the historic hack 🚨
The crypto market was shaken after a security incident at Binance involving approximately $6.3 billion in assets was confirmed. If you have funds on the platform or use it, here’s what you need to know, clearly and directly:
1️⃣ What happened?
Unauthorized access—apparently through a compromised platform developer’s device—enabled the mass movement of funds across 10 blockchains in a matter of minutes.
The crypto market was shaken after a security incident at Binance involving approximately $6.3 billion in assets was confirmed. If you have funds on the platform or use it, here’s what you need to know, clearly and directly:
1️⃣ What happened?
Unauthorized access—apparently through a compromised platform developer’s device—enabled the mass movement of funds across 10 blockchains in a matter of minutes.
98

·
--
The problem at Binance may not be a traditional theft.
Ido Ben-Natan, CEO of Blockaid, points to a possible misuse of private keys.
The theory is that the attackers manipulated the infrastructure responsible for signing transactions.
It’s a method similar to what happened recently with Bybit.
This isn’t a conventional hack, but rather a failure in the internal process.
What do you think about this kind of security failure?
$BNB $BTC
#Binance #CryptoSecurity
The problem at Binance may not be a traditional theft.
Ido Ben-Natan, CEO of Blockaid, points to a possible misuse of private keys.
The theory is that the attackers manipulated the infrastructure responsible for signing transactions.
It’s a method similar to what happened recently with Bybit.
This isn’t a conventional hack, but rather a failure in the internal process.
What do you think about this kind of security failure?
$BNB $BTC
#Binance #CryptoSecurity
Ido Ben-Natan, CEO of Blockaid, points to a possible misuse of private keys.
The theory is that the attackers manipulated the infrastructure responsible for signing transactions.
It’s a method similar to what happened recently with Bybit.
This isn’t a conventional hack, but rather a failure in the internal process.
What do you think about this kind of security failure?
$BNB $BTC
#Binance #CryptoSecurity
95
·
--
Someone just exploited a vulnerability in the Cysic bridge.
The attacker managed to mint 10 million tokens on the BNB Smart Chain.
They then moved $744,000 in $ETH and $BNB directly to Tornado Cash.
The company has already offered a 10% bounty to recover the funds.
It’s impressive how quickly these assets disappear into mixers.
What do you think about this kind of bounty?
#Cysic #CryptoSecurity
Someone just exploited a vulnerability in the Cysic bridge.
The attacker managed to mint 10 million tokens on the BNB Smart Chain.
They then moved $744,000 in $ETH and $BNB directly to Tornado Cash.
The company has already offered a 10% bounty to recover the funds.
It’s impressive how quickly these assets disappear into mixers.
What do you think about this kind of bounty?
#Cysic #CryptoSecurity
The attacker managed to mint 10 million tokens on the BNB Smart Chain.
They then moved $744,000 in $ETH and $BNB directly to Tornado Cash.
The company has already offered a 10% bounty to recover the funds.
It’s impressive how quickly these assets disappear into mixers.
What do you think about this kind of bounty?
#Cysic #CryptoSecurity
161

·
--
Did you receive the SMS but don’t see the bolívares in your account? Stop right there!
With 257 active offers on Binance P2P and the selling rate around 927.27 Bs, things are moving fast today. But watch out, my people: the rush is the fraudster’s best friend.
If you’re selling USDT, there’s no negotiating with the rule:
1. Go straight into your bank’s app.
2. Confirm the EXACT AVAILABLE balance (not deferred).
3. Make sure the account holder’s name matches 100% with the name on Binance.
No screenshots over chat, no receipts by email. Your bank calls the shots.
Have you checked your account today before releasing funds? Operate safely.
#BinanceP2P #SeguridadCrypto #VenezuelaCrypto #BinanceSquare
Did you receive the SMS but don’t see the bolívares in your account? Stop right there!
With 257 active offers on Binance P2P and the selling rate around 927.27 Bs, things are moving fast today. But watch out, my people: the rush is the fraudster’s best friend.
If you’re selling USDT, there’s no negotiating with the rule:
1. Go straight into your bank’s app.
2. Confirm the EXACT AVAILABLE balance (not deferred).
3. Make sure the account holder’s name matches 100% with the name on Binance.
No screenshots over chat, no receipts by email. Your bank calls the shots.
Have you checked your account today before releasing funds? Operate safely.
#BinanceP2P #SeguridadCrypto #VenezuelaCrypto #BinanceSquare
With 257 active offers on Binance P2P and the selling rate around 927.27 Bs, things are moving fast today. But watch out, my people: the rush is the fraudster’s best friend.
If you’re selling USDT, there’s no negotiating with the rule:
1. Go straight into your bank’s app.
2. Confirm the EXACT AVAILABLE balance (not deferred).
3. Make sure the account holder’s name matches 100% with the name on Binance.
No screenshots over chat, no receipts by email. Your bank calls the shots.
Have you checked your account today before releasing funds? Operate safely.
#BinanceP2P #SeguridadCrypto #VenezuelaCrypto #BinanceSquare
36
Sandbox Deactivates Connection Points on Affected Networks After Exploits
The web gaming platform Sandbox disabled the connection points on the affected networks to isolate the tokens and warned users not to trade SAND on Base and BNB, citing an impact of 0.01% of the supply.
$SAND $BNB
#CryptoSecurity
⚠️ This content is for informational and educational purposes only. It does not constitute financial advice. Do your own research before making any investment decisions. #DYOR
Sandbox Deactivates Connection Points on Affected Networks After Exploits
The web gaming platform Sandbox disabled the connection points on the affected networks to isolate the tokens and warned users not to trade SAND on Base and BNB, citing an impact of 0.01% of the supply.
$SAND $BNB
#CryptoSecurity
⚠️ This content is for informational and educational purposes only. It does not constitute financial advice. Do your own research before making any investment decisions. #DYOR
The web gaming platform Sandbox disabled the connection points on the affected networks to isolate the tokens and warned users not to trade SAND on Base and BNB, citing an impact of 0.01% of the supply.
$SAND $BNB
#CryptoSecurity
⚠️ This content is for informational and educational purposes only. It does not constitute financial advice. Do your own research before making any investment decisions. #DYOR
1
129
Attention to all new users in P2P trading! 🔒 A golden rule you must never forget: Never release your crypto just based on a screenshot the buyer sends you. Always open your banking app and confirm that the real money is already available. Safety first! 🛡️ #BinanceP2P #SeguridadCrypto
Attention to all new users in P2P trading! 🔒 A golden rule you must never forget: Never release your crypto just based on a screenshot the buyer sends you. Always open your banking app and confirm that the real money is already available. Safety first! 🛡️ #BinanceP2P #SeguridadCrypto
118
·
--
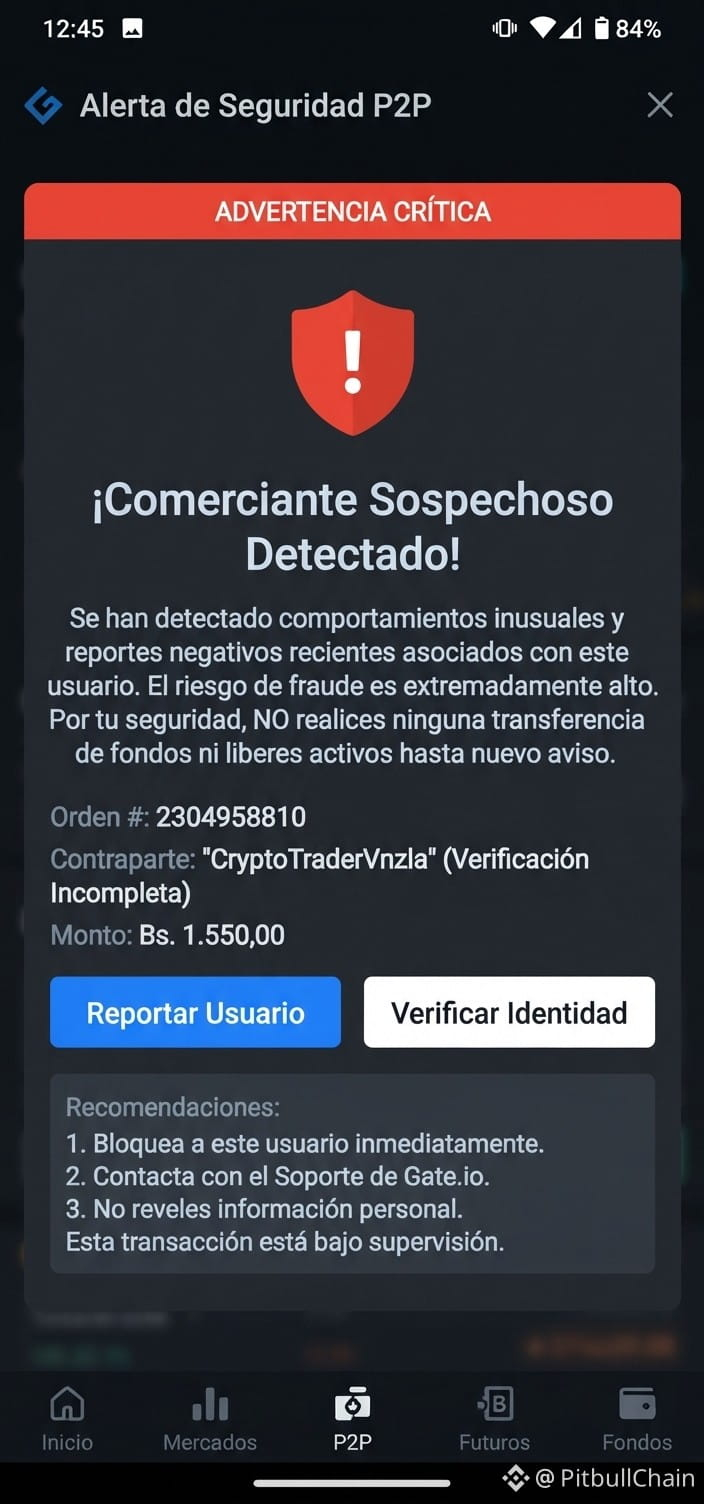
Do you check your bank account before releasing $USDT, or do you just rely on the screenshot? ⚠️
With more than 250 active orders and the market moving on Binance P2P, fraud attempts using third-party payments and edited receipts are still lurking.
Golden security rule:
1. Check your bank directly in the official app.
2. Account holder = Name verified on Binance.
Never release out of urgency or pressure from the chat!
📊 Live fees and analysis at pitbullchain.com
$USDT #BinanceP2P #SeguridadCrypto #VenezuelaCrypto #USDT
Do you check your bank account before releasing $USDT, or do you just rely on the screenshot? ⚠️
With more than 250 active orders and the market moving on Binance P2P, fraud attempts using third-party payments and edited receipts are still lurking.
Golden security rule:
1. Check your bank directly in the official app.
2. Account holder = Name verified on Binance.
Never release out of urgency or pressure from the chat!
📊 Live fees and analysis at pitbullchain.com
$USDT #BinanceP2P #SeguridadCrypto #VenezuelaCrypto #USDT
With more than 250 active orders and the market moving on Binance P2P, fraud attempts using third-party payments and edited receipts are still lurking.
Golden security rule:
1. Check your bank directly in the official app.
2. Account holder = Name verified on Binance.
Never release out of urgency or pressure from the chat!
📊 Live fees and analysis at pitbullchain.com
$USDT #BinanceP2P #SeguridadCrypto #VenezuelaCrypto #USDT
77
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#CanBTCReboundAfterFallingBelow60K?
360,624 views
1,510 Discussing
2
#GlobalStocksFaceLongestLosingStreakSince2023
119,016 views
1,071 Discussing
3
#BlackRockIBITPostsRecord$541MSingleDayOutflow
613 views
15 Discussing
4
#AnthropicPlungesTowardIPOPriceonDay2
57,449 views
581 Discussing
5
#TwentyOneCapitalAdds172.25BTC
10,155 views
153 Discussing
6
#HKBillWouldExcludeTokenizedDepositsFromVirtualAssets
861 views
14 Discussing
7
#BNBDropsBelow540USDTWith8.46%DailyDecline
30,925 views
263 Discussing
8
#HKBillProposesHK$100KFineForUnauthorizedCryptoTitles
1,009 views
14 Discussing
9
#BitMineFaces$10.1BUnrealizedETHLoss
1,967 views
18 Discussing
10
#StrategyReports$35BNetReserves
1,834 views
17 Discussing